
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended
 keycloak/keycloak
 artemy-ccrsky/cve-2024-41276
PIN-based Authentication Bypass vulnerability in Kaiten
 abraxas/hyperswitch-payout-confirm-secret
Proof-of-concept and lab for a Hyperswitch payout confirm flaw: a dummy client_secret plus amount in POST /payouts/{id}/confirm raises the stored…
 ricardojoserf/cve-2019-19033
CVE-2019-19033 description and scripts to check the vulnerability in Jalios JCMS 10 (Authentication Bypass)
 abraxas/superset-g3-v0-import-sql-plant
Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…
 0xblackash/cve-2025-31161
CVE-2025-31161
 peach-research-lab/authorizationbench
[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 motikan2010/cve-2021-34646
CVE-2021-34646 PoC
 bridgeralderson/cve-2026-58424
A flaw in Gitea Open Source Git Server’s approval‑gate logic allows a pull request that originates from a permanent fork to merge without satisfying…
 strikoder-premium/cve-2026-29000-pac4j-jwt
CVE-2026-29000 PoC: pac4j-jwt PlainJWT-in-JWE authentication bypass.
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…
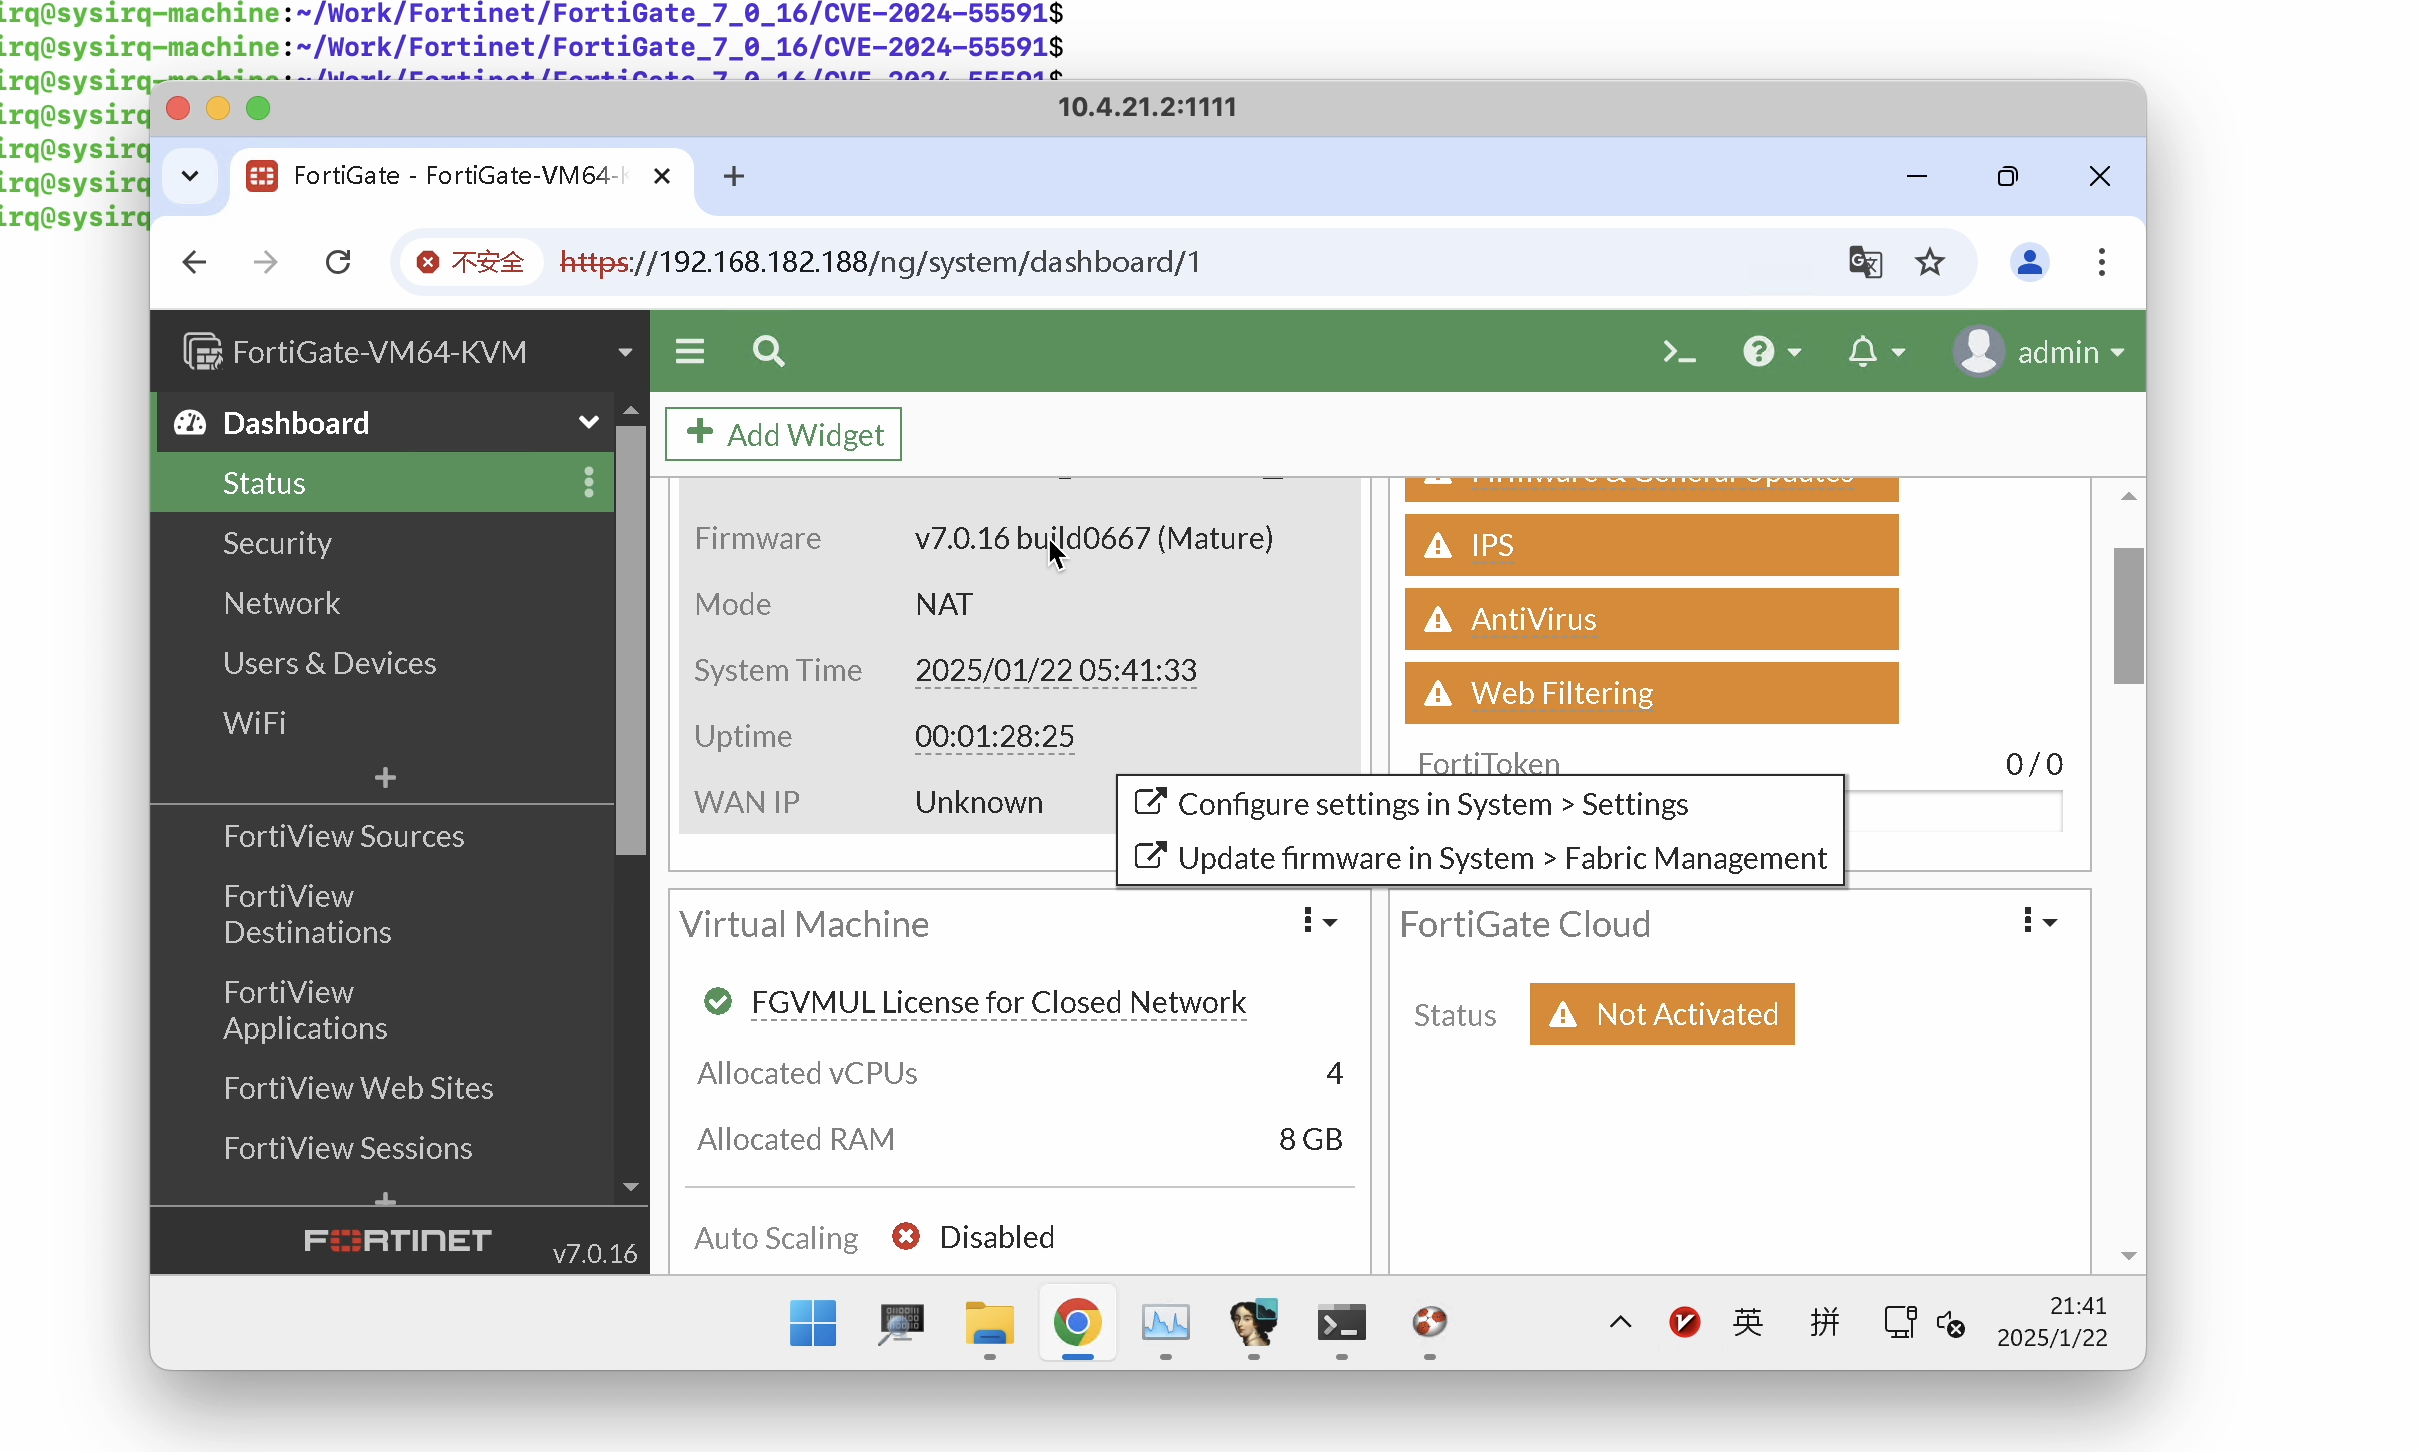 sysirq/fortios-auth-bypass-exploit-cve-2024-55591
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.
 baph00met/cve-2024-47533
CVE-2024-47533: Cobbler Authentication Bypass & Code Execution
 0xterror/cve-2026-82329-jfrog-artifactory-
Exploit PoC for CVE-2026-82329, an authentication bypass in JFrog Artifactory. Demonstrates forging JWT tokens to gain admin access and create a…
 ainrm/jrohy-trojan-unauth-poc
CVE-2024-55215
 0xgh057r3c0n/cve-2025-31161
🛡️ CVE-2025-31161 - CrushFTP User Creation Authentication Bypass Exploit








