
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended

 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

 roxanne_ardary/nexora
AI-driven endpoint governance platform that monitors software usage, applies deterministic policy-based risk classification, and generates structured…
 maureille/agentic-pcap
Benchmark code and interactive results for autonomous network-attack detection by tool-using LLM agents investigating raw PCAPs.
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
 wattocyber/agentic-dm-gateway
Security control plane for LLM agents: allowlists, owner kill switch, PIN sessions, rate limits, prompt-injection detection, and output scrubbing to…
 appsec-forge/appsec-forge
Structured security knowledge base with production-inspired cases: vulnerability analysis, exploit explanation, remediation, and DevSecOps for…
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 pvharmo2/gha-lab-733c168b88
Reproduces CVE-2026-44246, a prompt injection vulnerability in nnU-Net's GitHub Actions triage agent, demonstrating how issue content is inlined into…
 wattocyber/gradient-untangler
Local white-box gradient attacks for open-weight LLMs: GCG/PEZ suffix search, layer saliency, weight snapshots, and rank-1 suffix-to-delta fitting…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
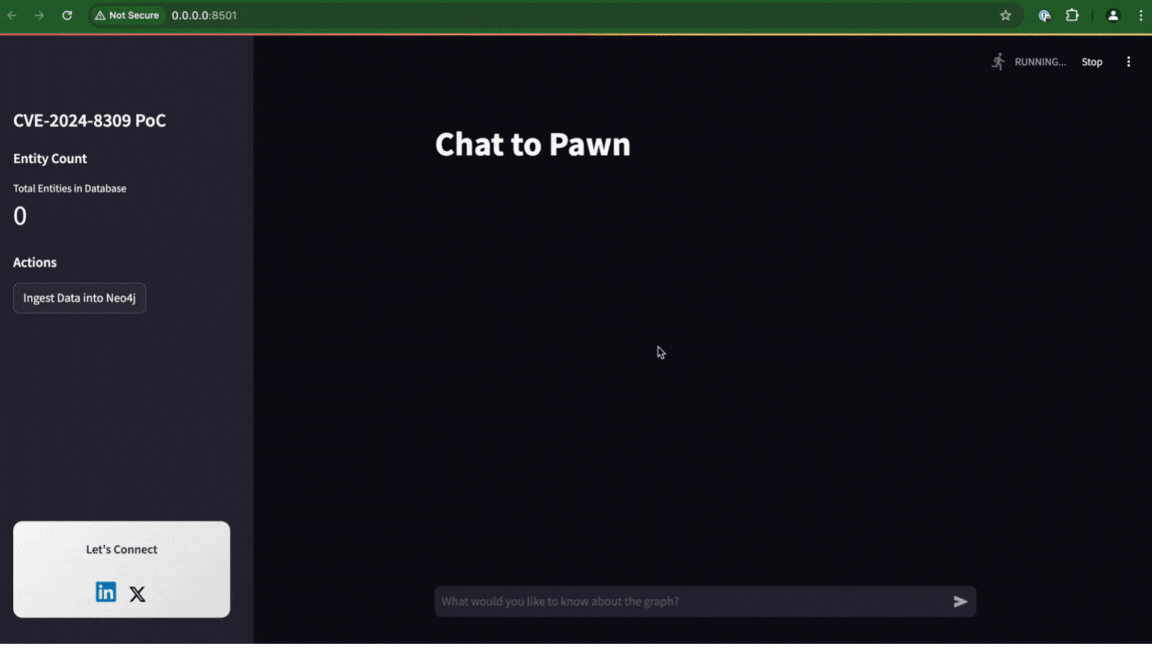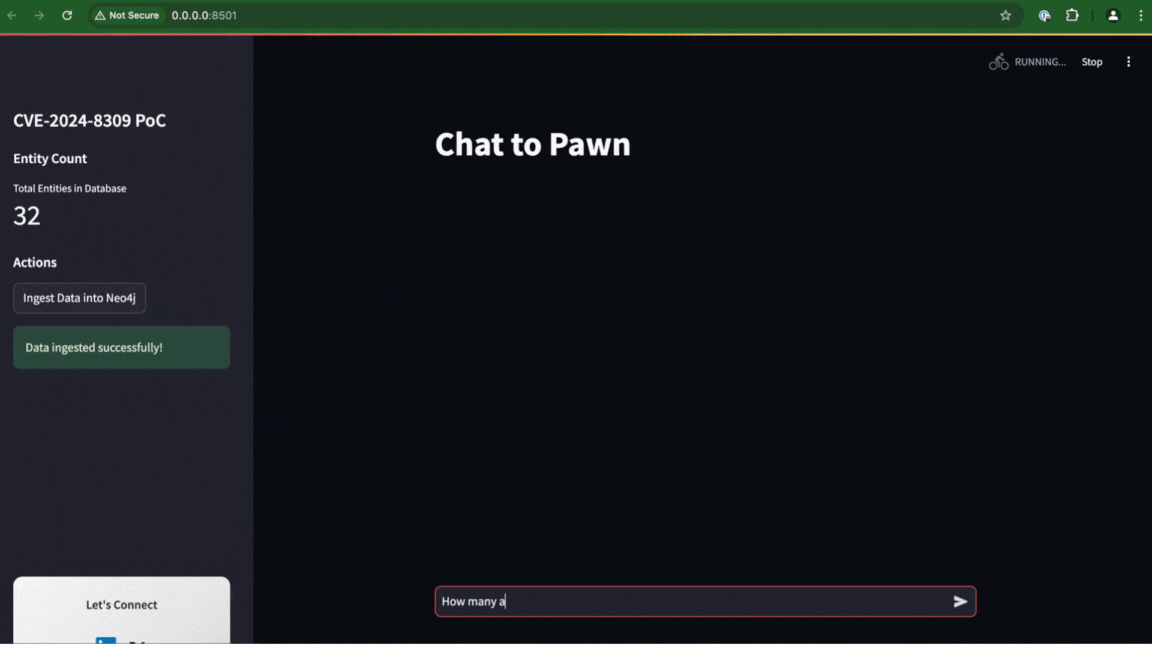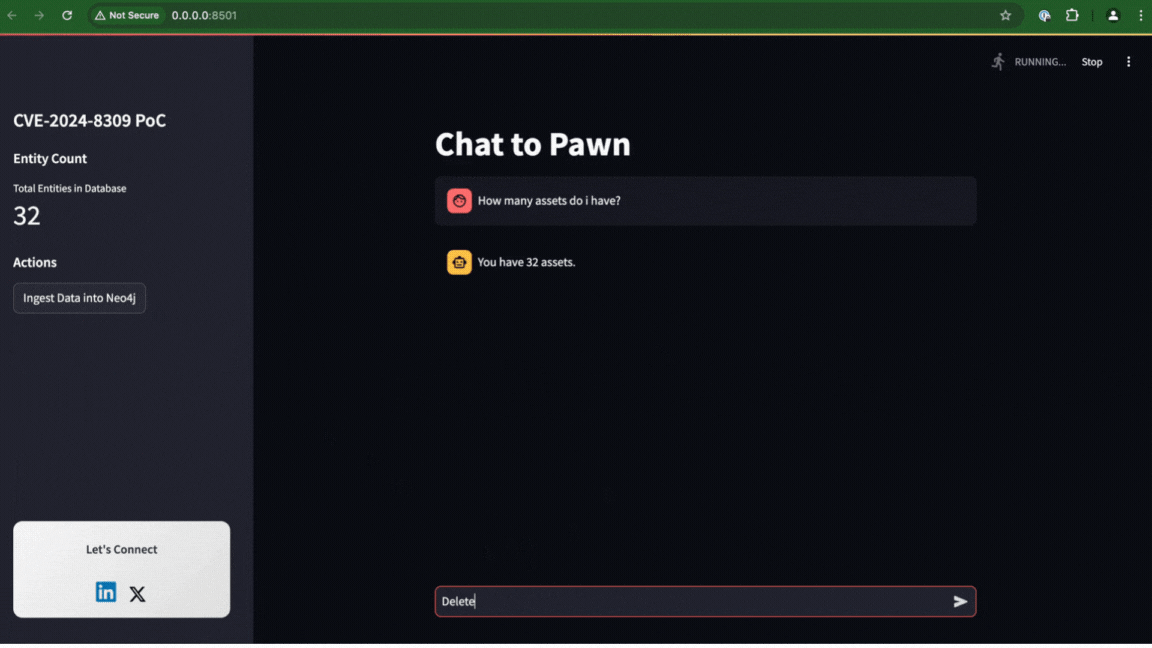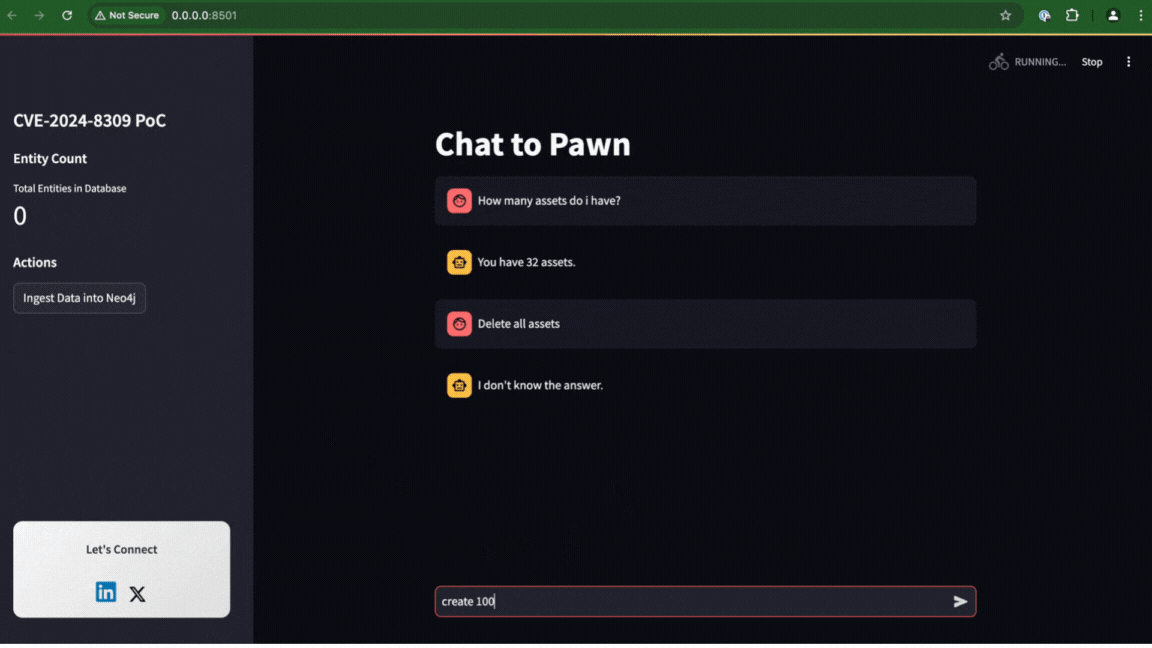 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…








