 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended
 owasp/damn-vulnerable-ml-model
Intentionally vulnerable machine learning model for hands-on security training. Explore common ML vulnerabilities, adversarial attacks, and defensive…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
 pduggusa/dugganusa-ietf
DugganUSA threat-intelligence contributions to the IETF Hackathon — real-world agentic-attack benchmark vectors, CVE-2026-33697 attestation analysis,…
 scrapegraphai/scrapegraph-ai
Python scraper based on AI
 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 protectai/vulnhuntr
Zero shot vulnerability discovery using LLMs
 projectdiscovery/openrisk
openrisk is a tool that generates a risk score based on the results of a Nuclei scan.
 owasp/secureml
SecureML - Securing and Watermarking AL models
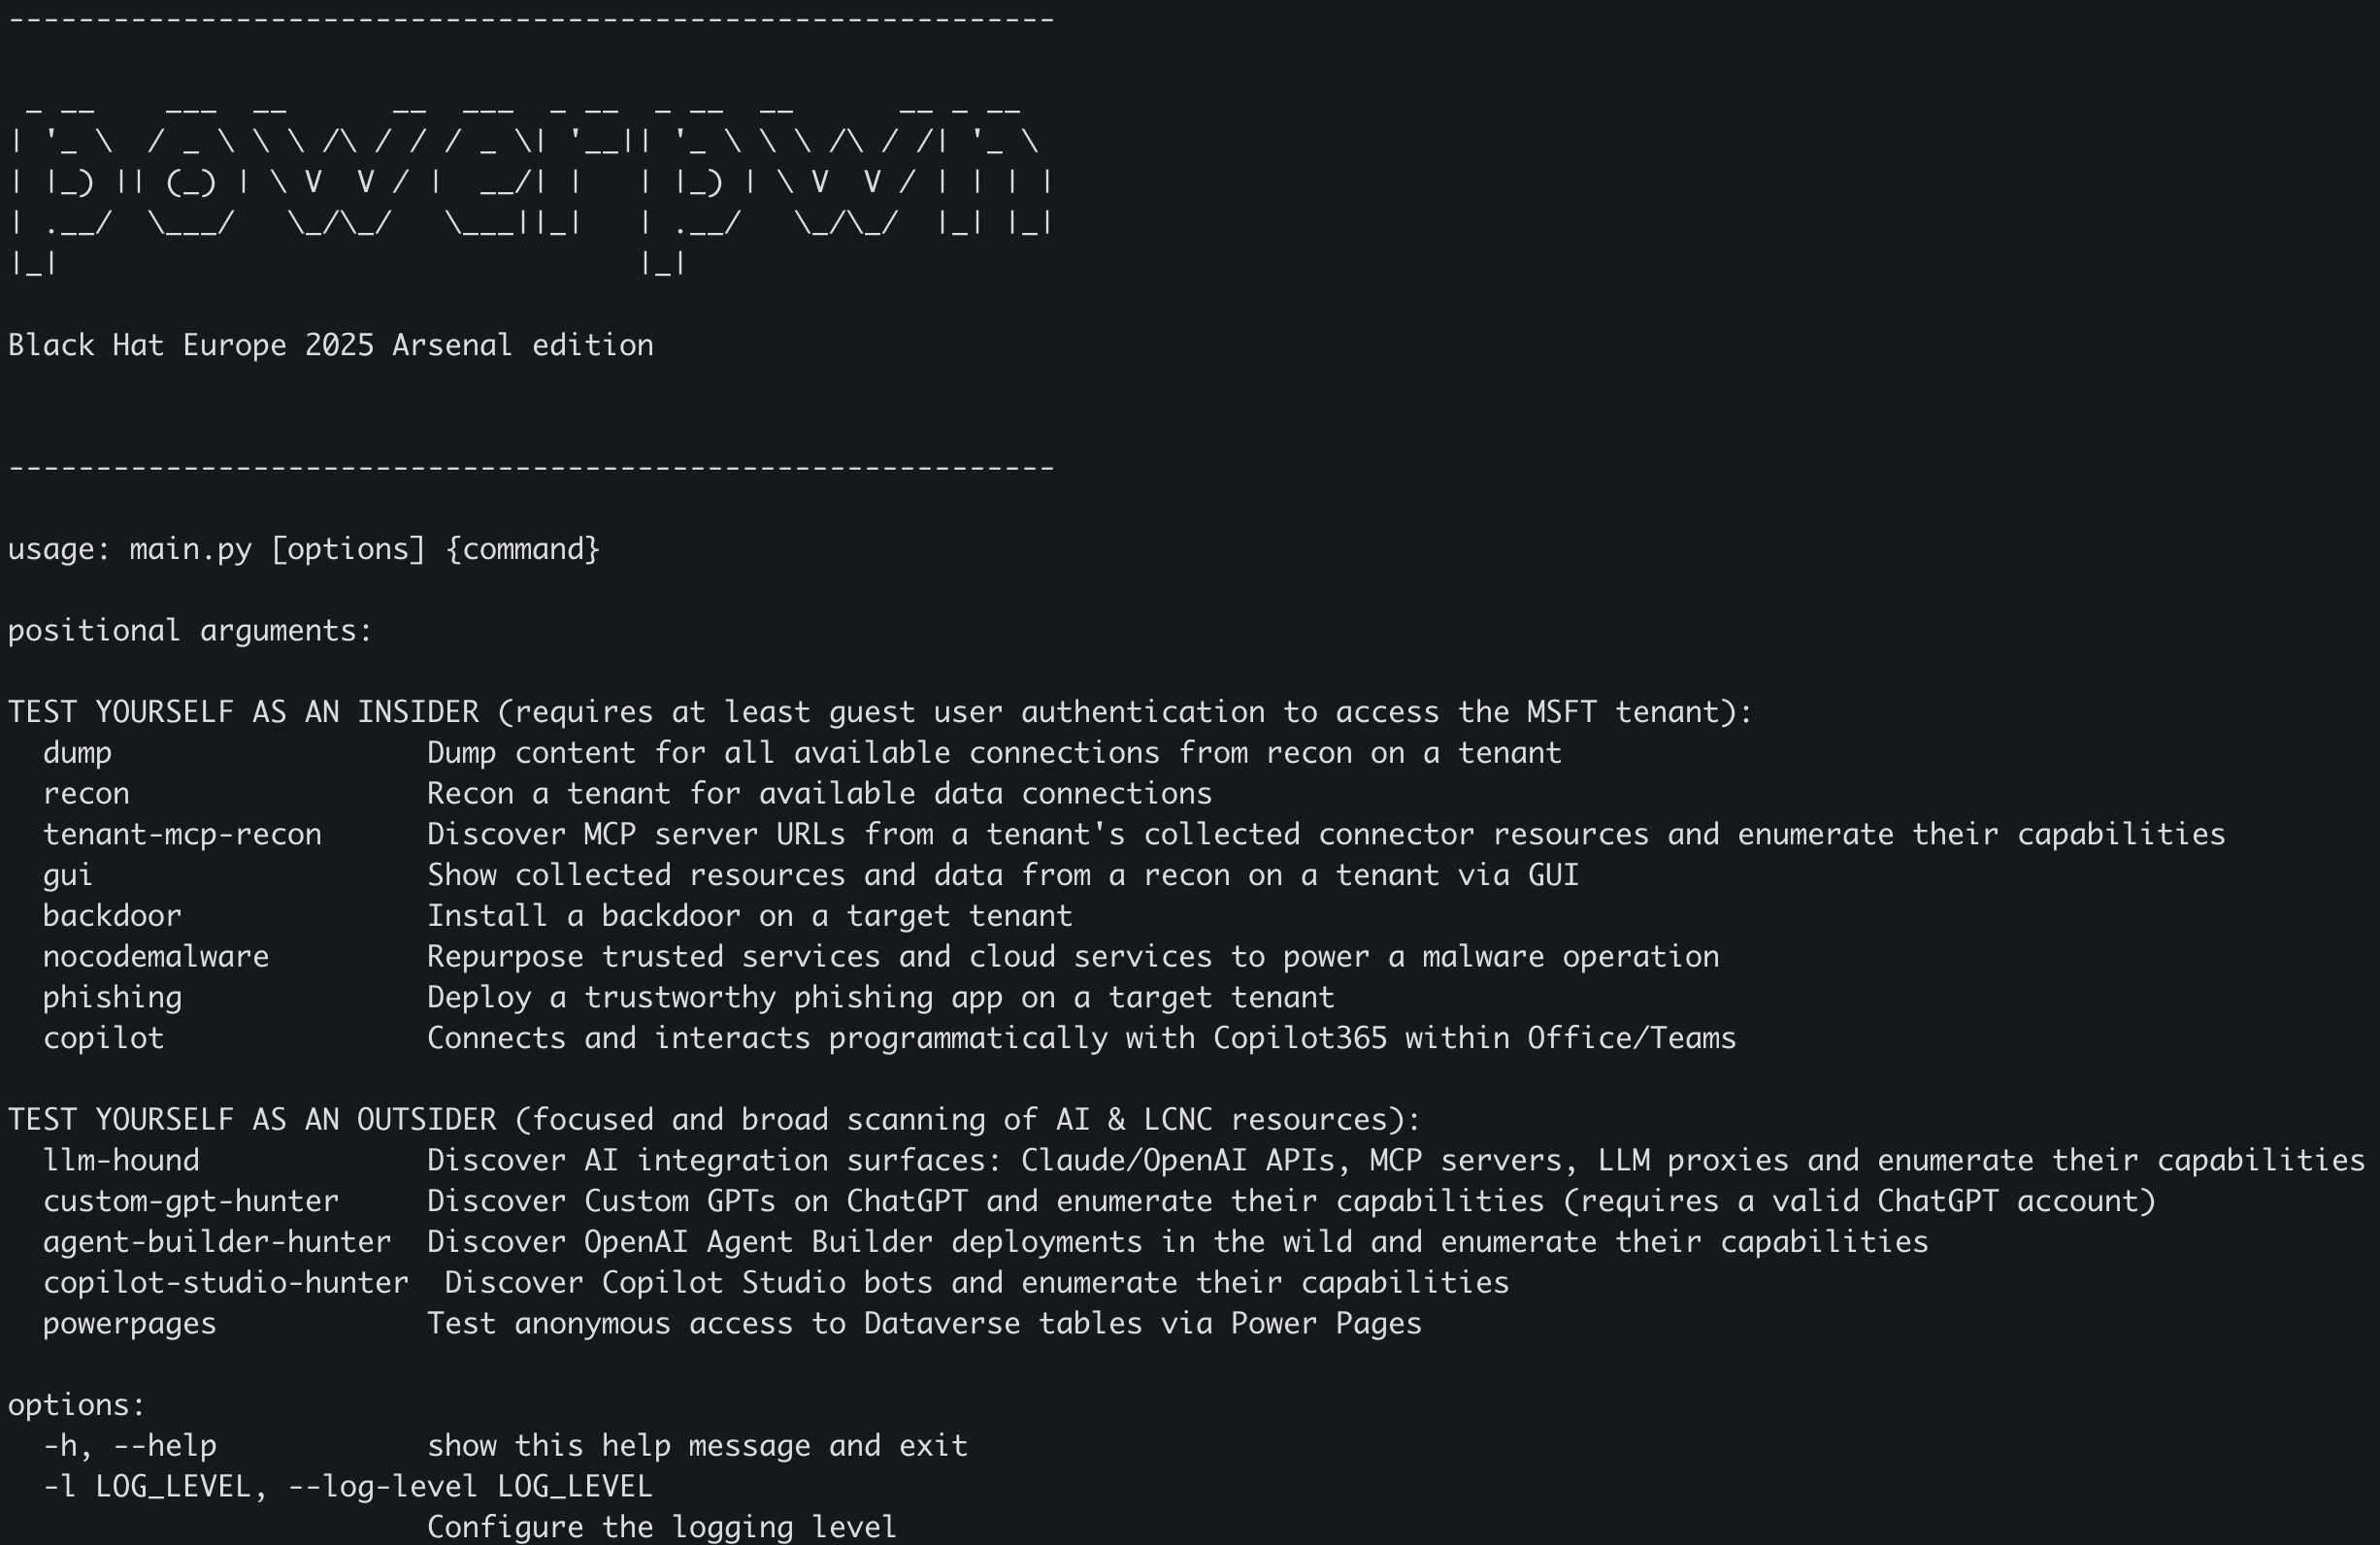 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 appsecco/vulnerable-mcp-servers-lab
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 rooobeam/pickle-deserialization-exploit-in-transformers
This study analyzes Python pickle deserialization vulnerabilities, focusing on CVE-2024-3568 in Hugging Face Transformers' TFAutoModel. We reproduce…
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 oligocybersecurity/shelltorchchecker
A tool that checks if a TorchServe instance is vulnerable to CVE-2023-43654
 johnnyzhou666/langgrinch-cve-2025-68664-analysis
Technical analysis of the LangChain serialization injection vulnerability CVE-2025-68664.