
 #1
Adversarial ML attack frameworks, evasion techniques, and model robustness evaluation tools.
Kitploit recommended
 darkspacesecurity/runas-stealer
RunAs Utility Credential Stealer implementing 3 techniques : Hooking CreateProcessWithLogonW, Smart Keylogging, Remote Debugging
 ioactive/i-know-where-your-page-lives
I Know Where Your Page Lives: Derandomizing the latest Windows 10 Kernel - ZeroNights 2016
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
 santanderai/autoguardrails
Alignment-research scaffold (autoresearch-style) for LLM guardrails: search over a single policy.md surface
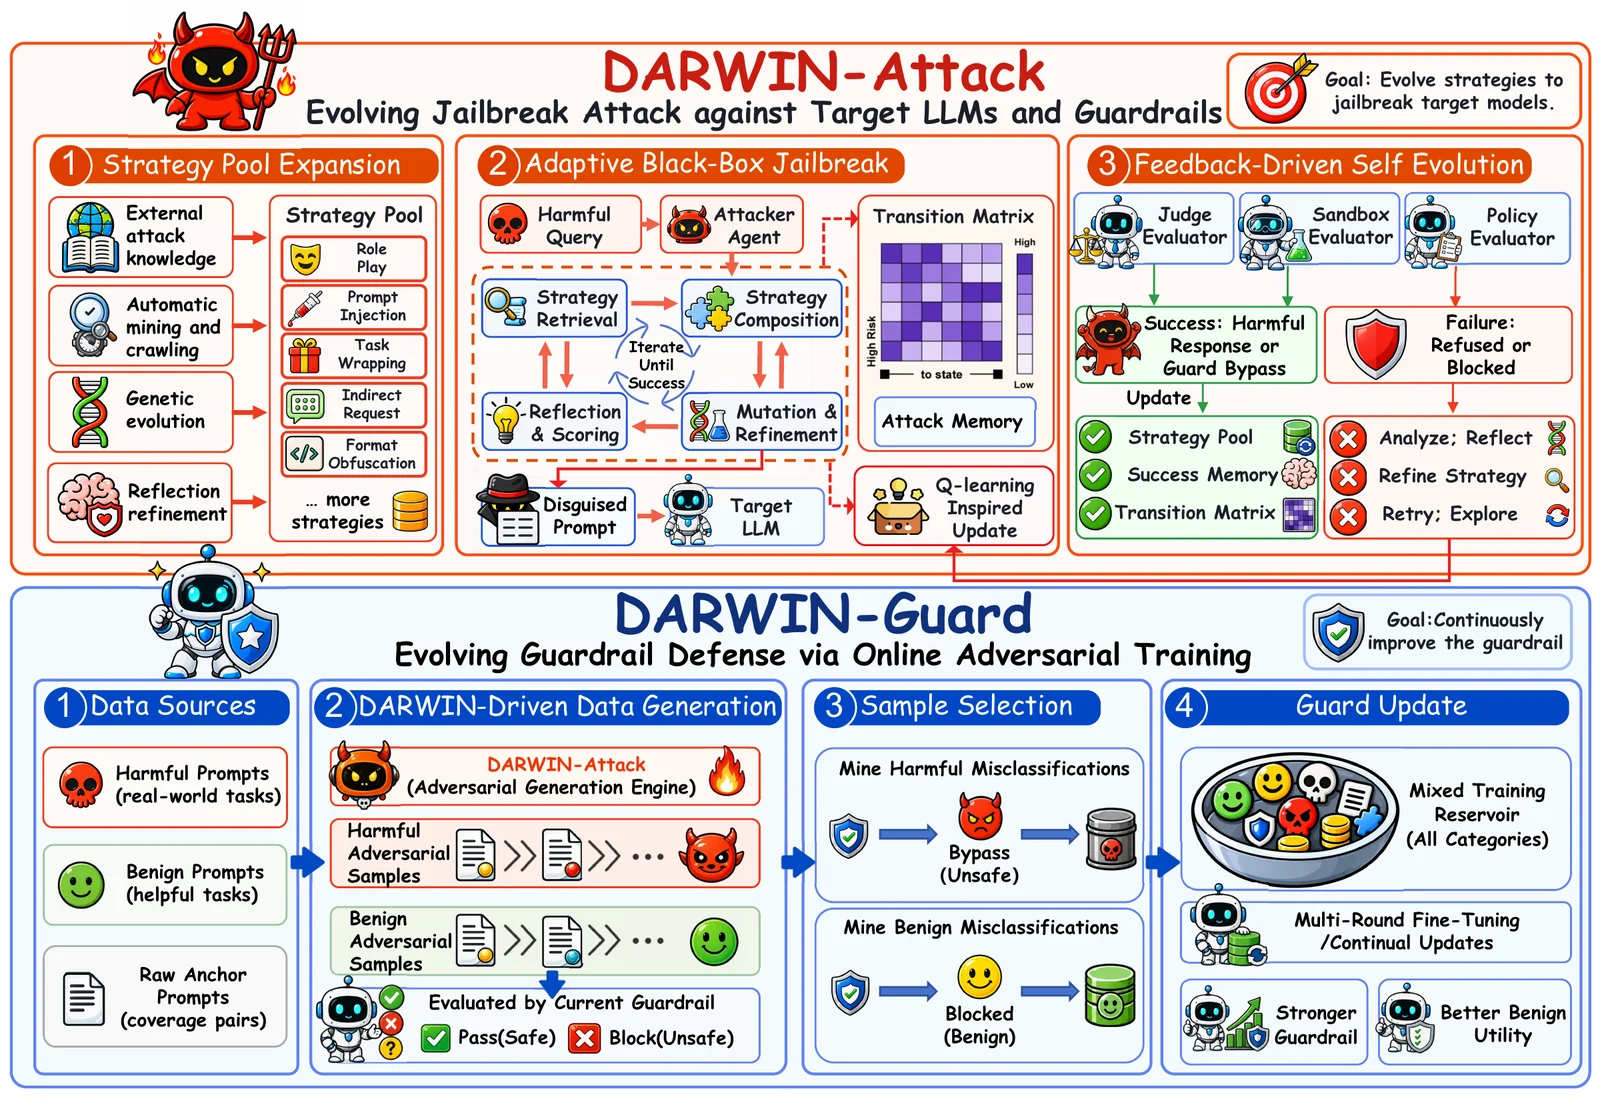 zju-llm-safety/darwin
Evolutionary LLM jailbreak and guardrail framework that grows a reusable strategy pool via genetic mutation, Markov selection, and online adversarial…
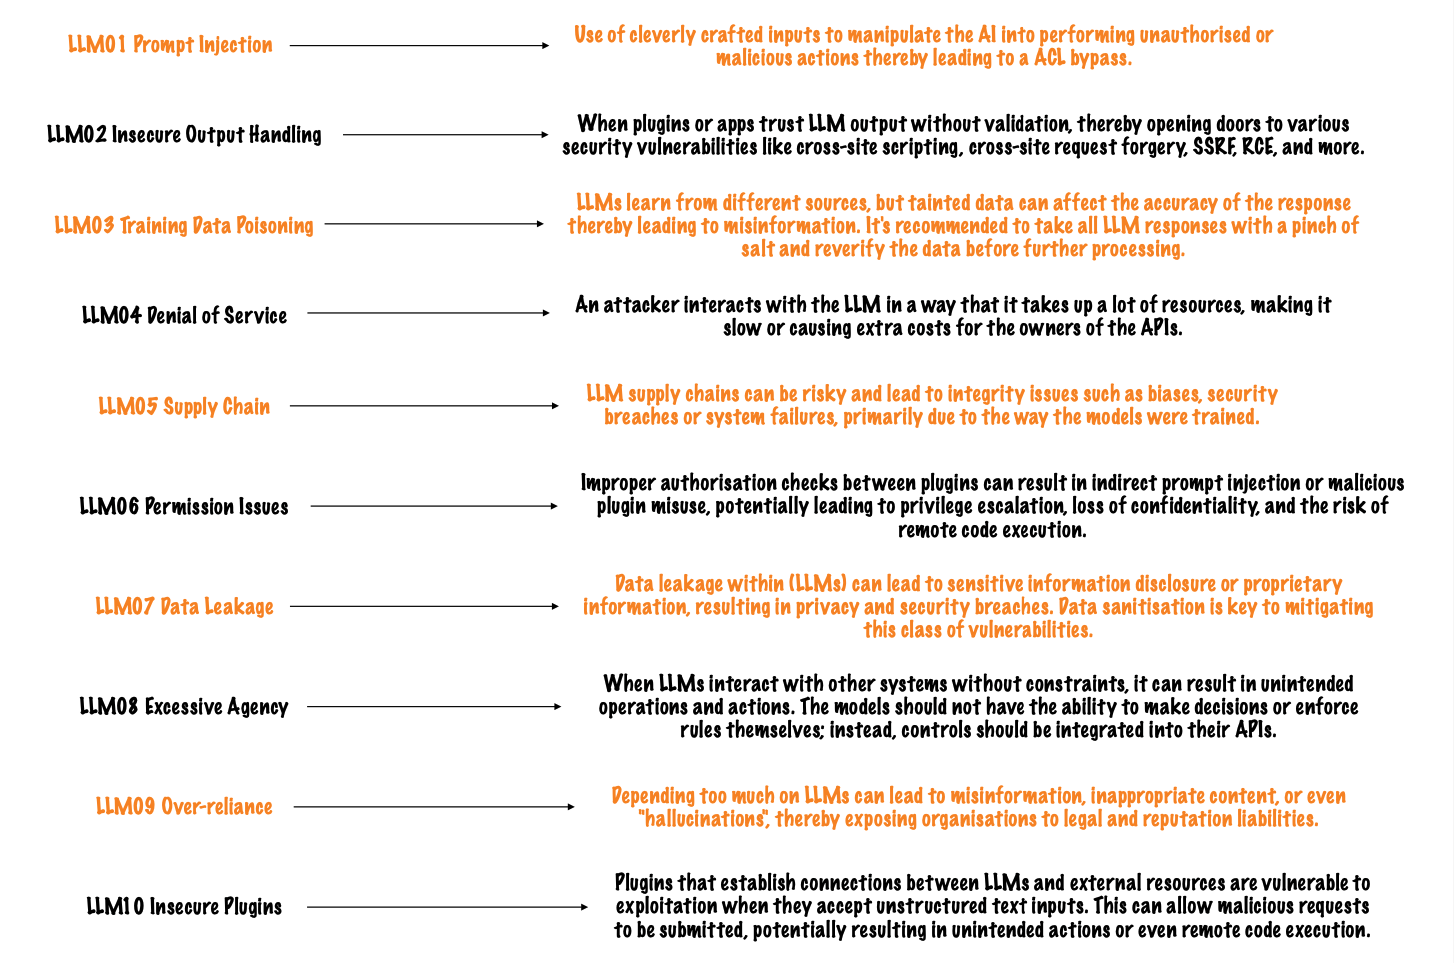 seezo-io/llm-security-101
Delving into the Realm of LLM Security: An Exploration of Offensive and Defensive Tools, Unveiling Their Present Capabilities.
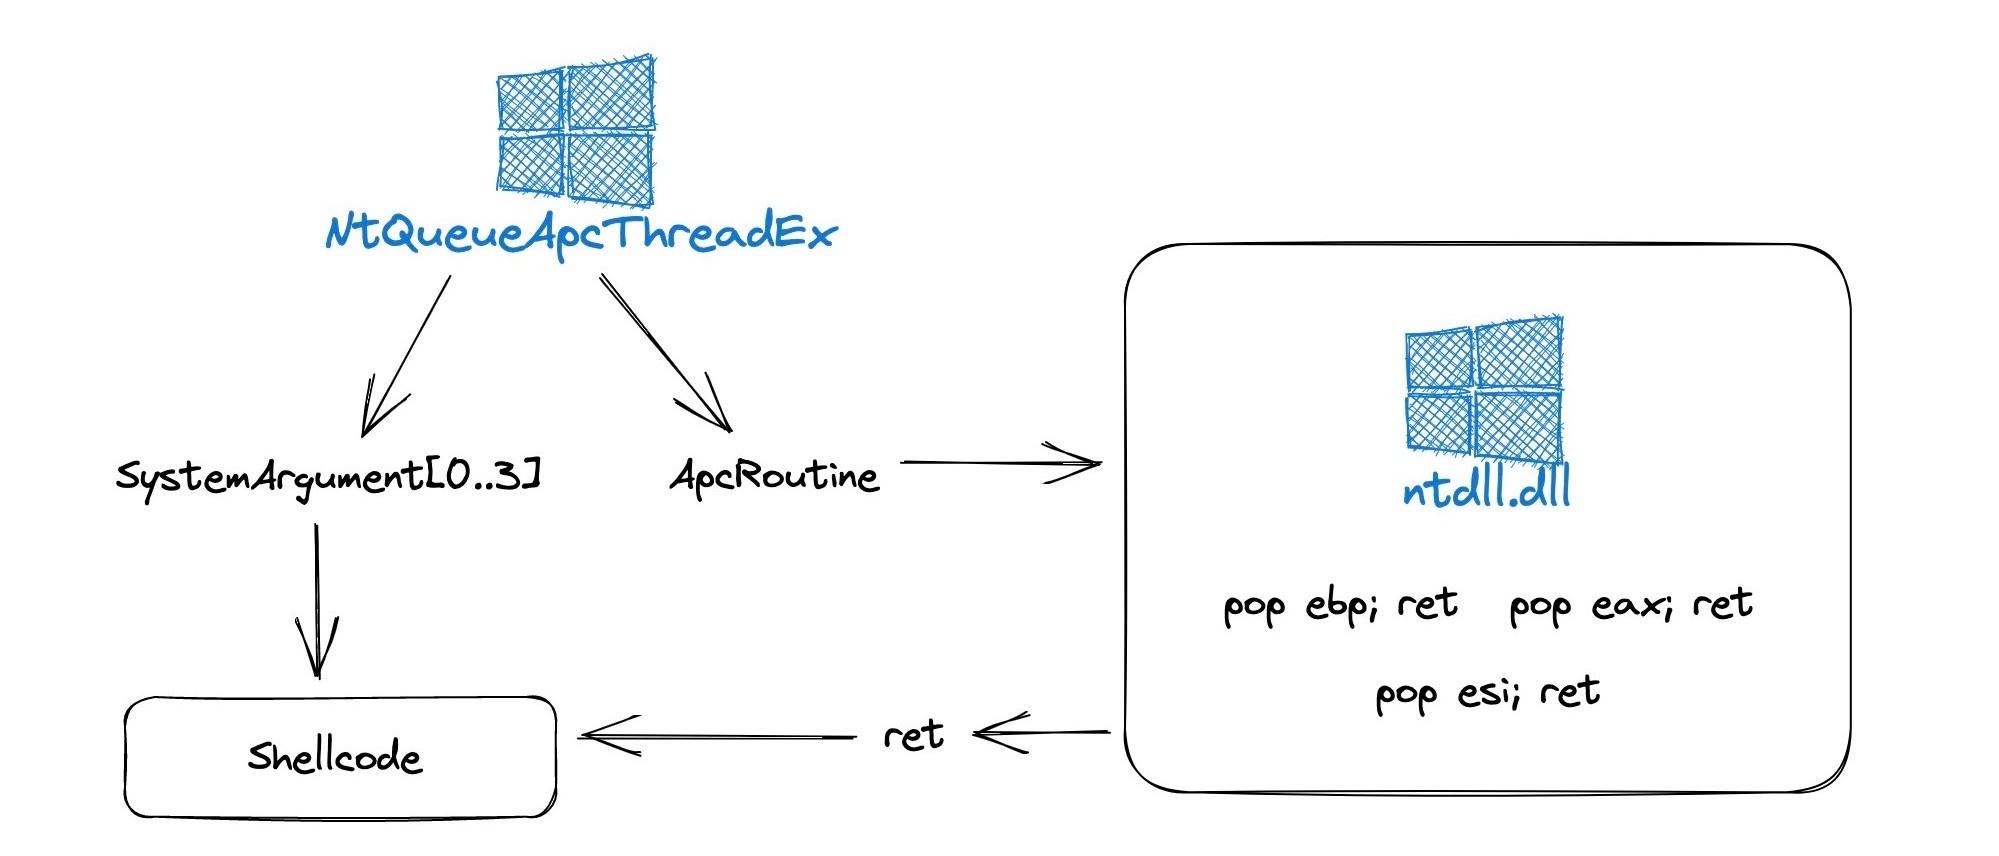 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
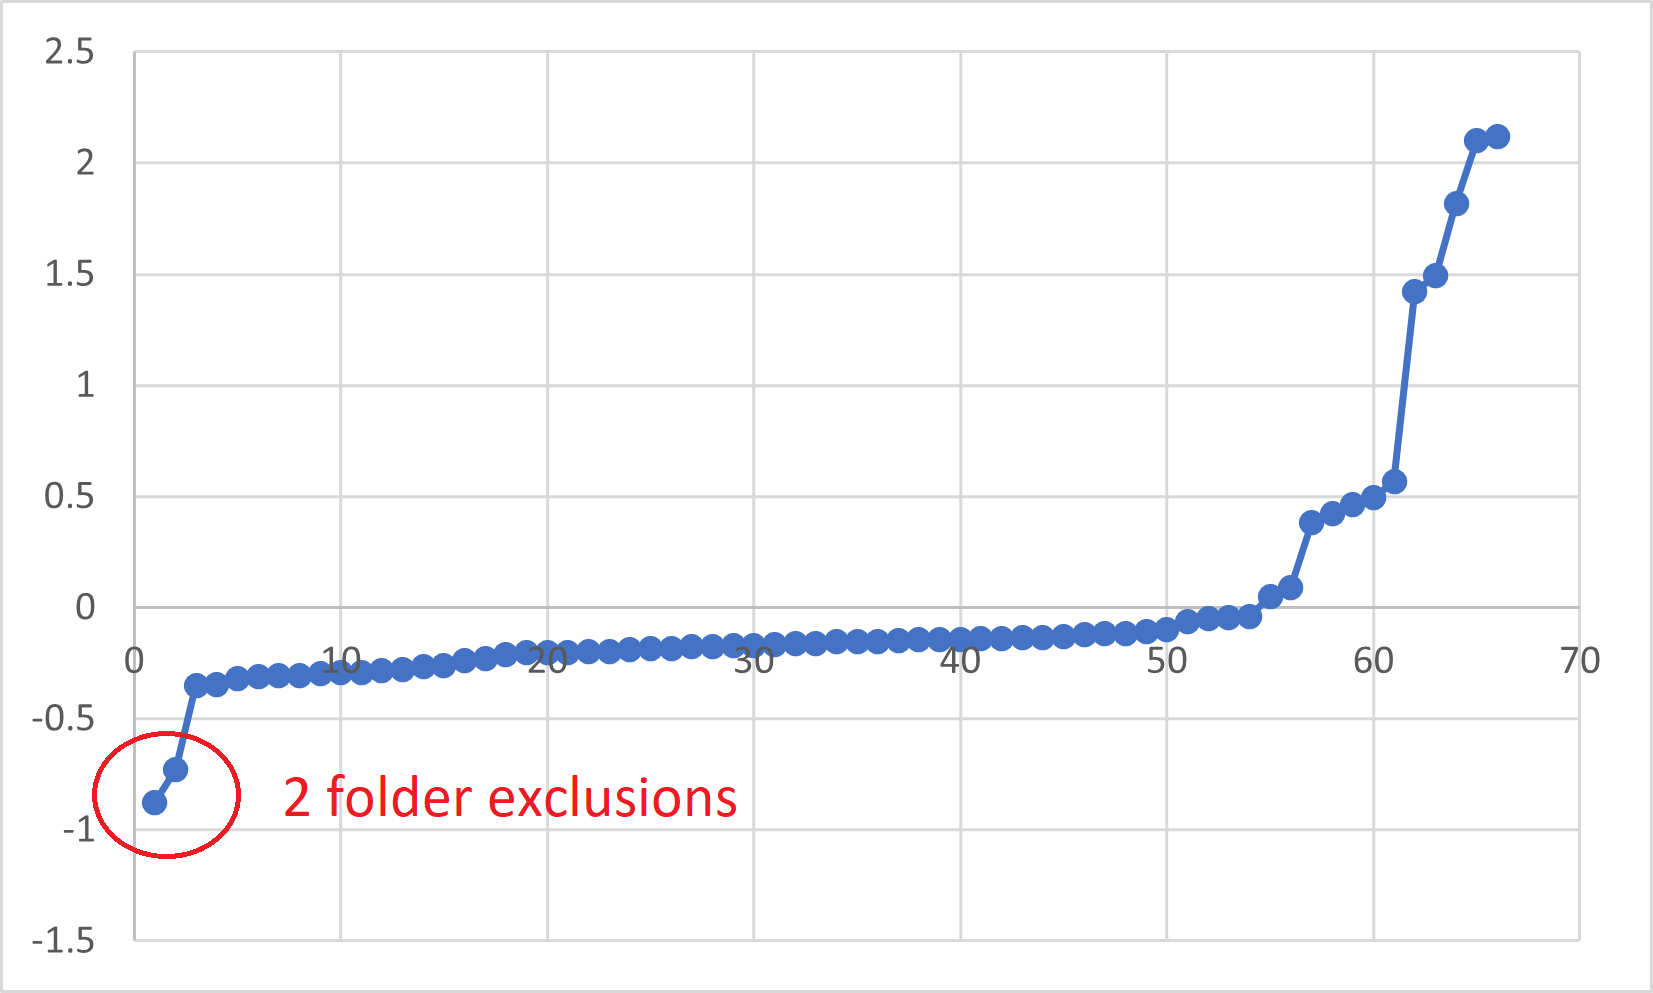 bananabr/timeexception
A tool to find folders excluded from AV real-time scanning using a time oracle
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 bishopfox/brokenhill
A productionized greedy coordinate gradient (GCG) attack tool for large language models (LLMs)
 idov31/jormungandr
Jormungandr is a kernel implementation of a COFF loader, allowing kernel developers to load and execute their COFFs in the kernel.
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog








