

Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Einreichen
ToolsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/s3n4t0r-0x0/apts-adversary-simulation
Privilege EscalationReconnaissancePersistence MechanismsExploitationLateral MovementPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingPayload DevelopmentAdversarial Attack
1.1k19049vor 7 TagenVon Kitploit geprüft

Über

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks .

Teilen
GitHubs3n4t0r-0x0/apts-adversary-simulation

APTs-Adversary-Simulation

Repository anzeigen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

APTs Adversary Simulation


Comprehensive collection of simulated APT attacks based on real world TTPs used by state sponsored APT Groups from Russia, China, Iran, and North Korea
hollywood-Comp-02

[!CAUTION] Important Notice: This project is strictly for educational, research, and defensive security purposes only. Unauthorized use of these techniques may violate laws and result in serious legal consequences.

🧠 Overview

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, command and control (C2) servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks. The simulations are based on extensive research from leading cybersecurity firms, including PaloAlto Unit42, Kaspersky, Microsoft, Cisco, Trellix, CrowdStrike, and WithSecure.

Learn More About the Importance and Outcomes of the Experience:

  • Why Adversary Simulation? - Understanding the strategic value of simulating advanced threats
  • Adversary Simulation VS Adversary Emulation - Key differences and when to use each approach
  • How do I simulate an APT - Adversary Simulation Is Not a Methodology It's the Outcome of Experience

🎯 Simulated APT Groups

Note: APT group names in this repository follow the naming conventions used by different security vendors. The same APT group may have different names depending on the vendor (e.g., Mandiant, CrowdStrike, Microsoft, Kaspersky, etc.).
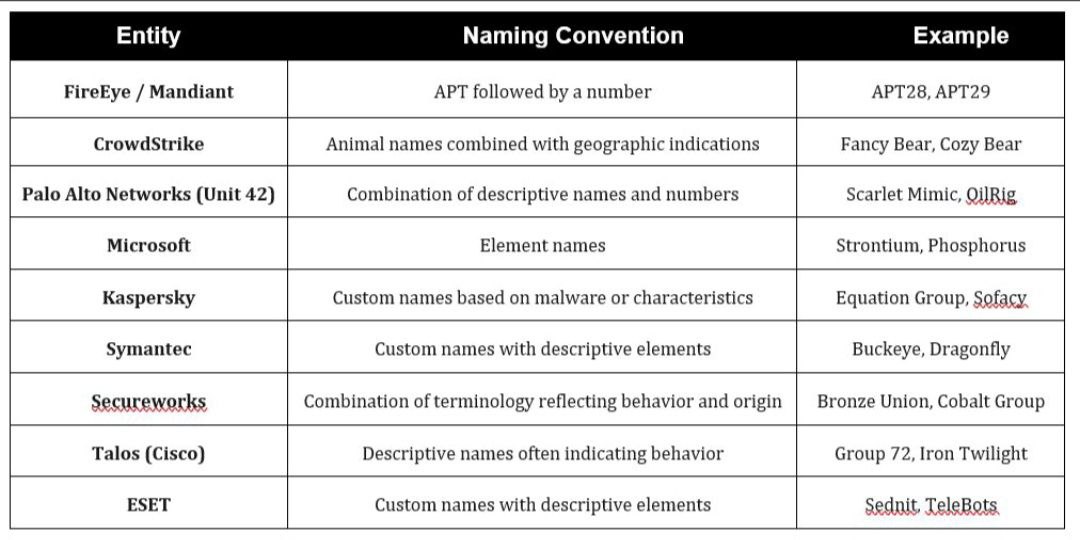
photo_2025-11-09_04-26-38

Below is the complete list of simulated APT Groups:

Country
of Origin
Russia 🇷🇺 China 🇨🇳 North Korea 🇰🇵 Iran 🇮🇷
APT Groups

Cozy Bear
Voodoo Bear
Fancy Bear
Energetic Bear
Berserk Bear
Gossamer Bear
Primitive Bear
Ember Bear
Venomous Bear

Mustang Panda
Wicked Panda
Goblin Panda
Deep Panda
Glacial Panda
Anchor Panda
Samurai Panda
Phantom Panda
Sunrise Panda
Ethereal Panda

Lazarus
Labyrinth Chollima
Velvet Chollima
Famous Chollima
Ricochet Chollima
Silent Chollima

Helix Kitten
Charming Kitten
Static Kitten
Muddy Water
Tracer Kitten
Pioneer Kitten
Nemesis Kitten
Clever Kitten
Pulsar Kitten
Remix Kitten
Haywire Kitten

🛠️ Adversary Framework

All adversary simulations are powered by BEAR-C2 a custom command and control framework designed for realistic threat simulation.
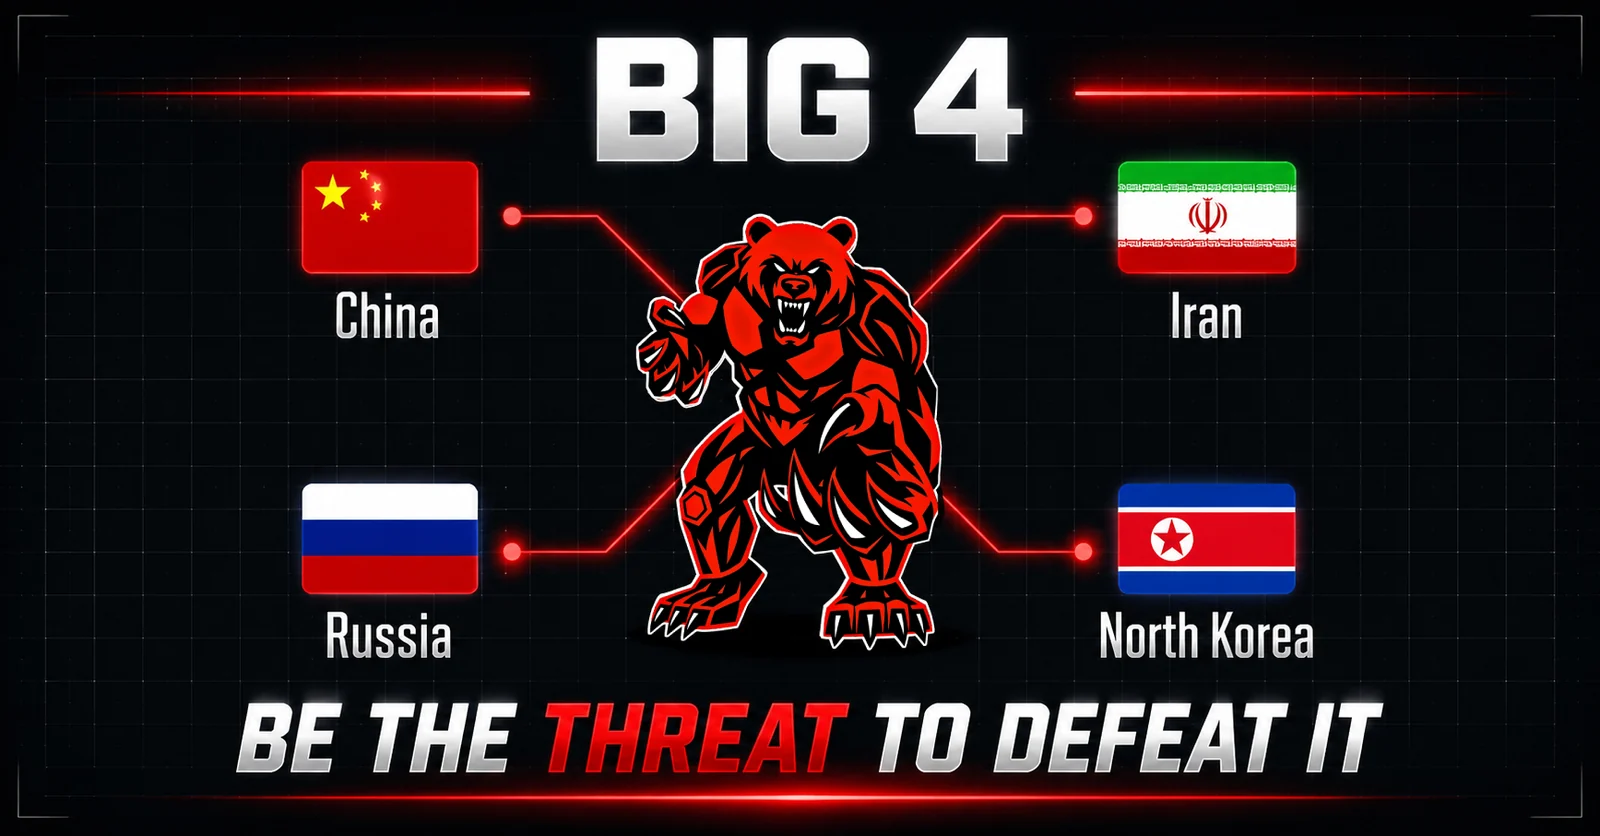
image psd(1)

📫 Contact

Telegram Twitter/X LinkedIn Reddit
Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

Noch keine Beliebtheitsdaten.

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →