prismorsec/prismor
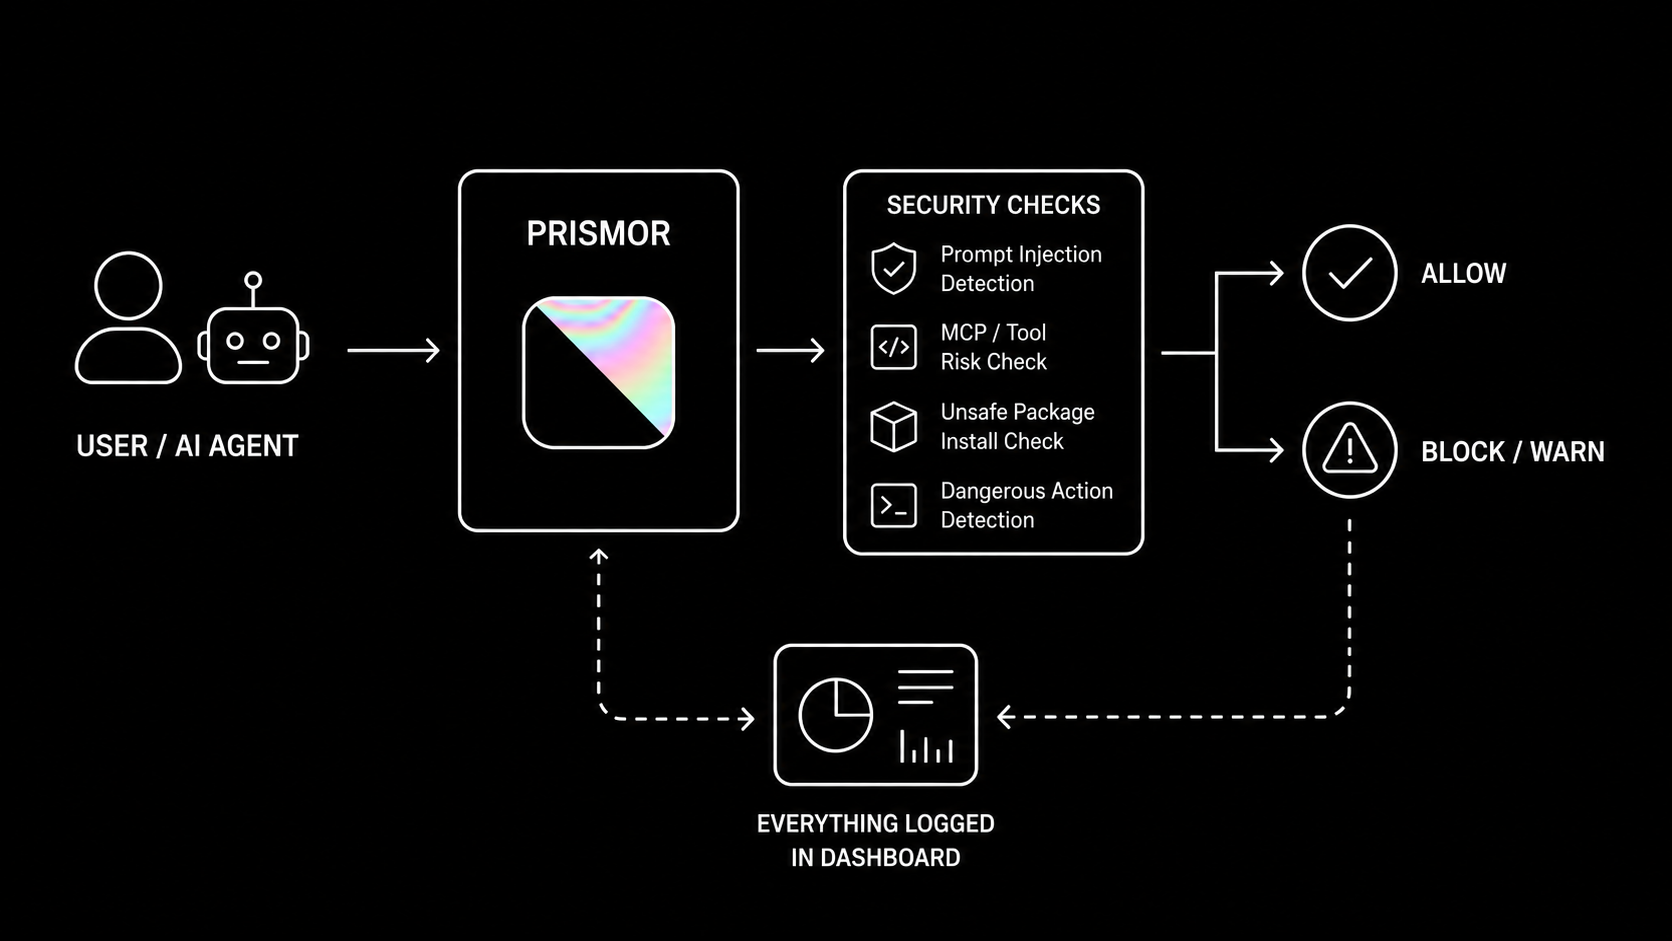
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)




Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.
This creates risks that traditional security tooling isn't designed for:
.env or credential files as part of a debugging task and sends the content outboundStandard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable
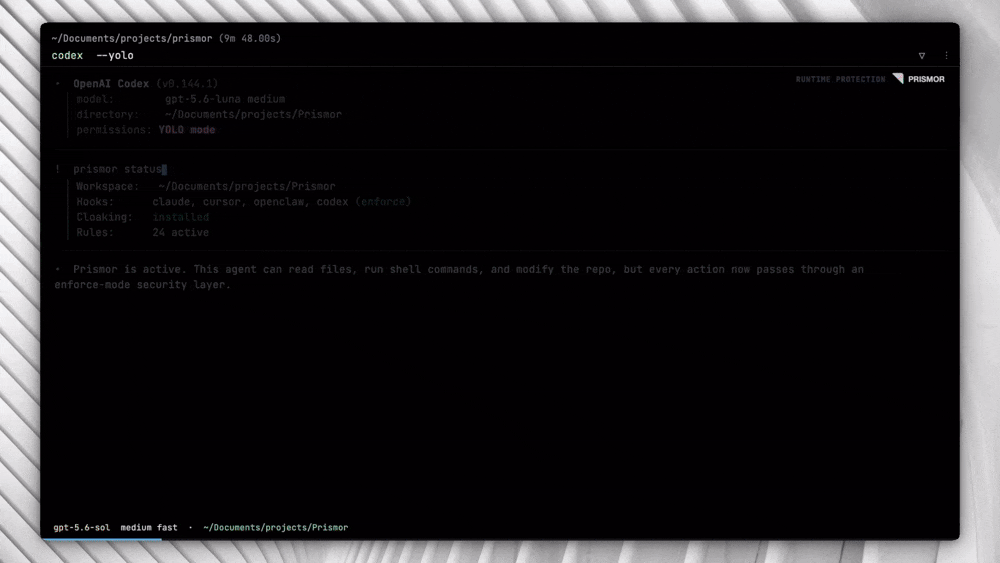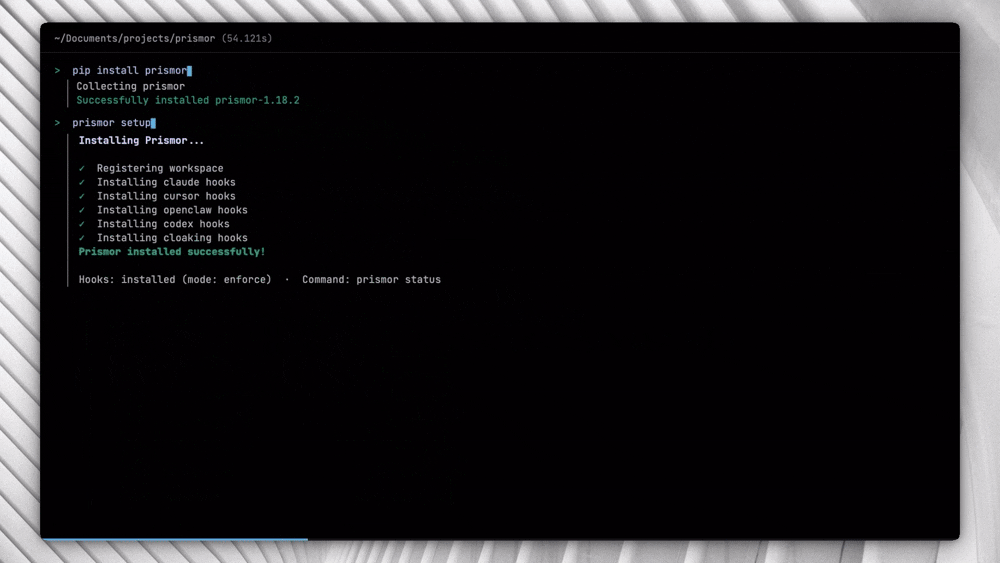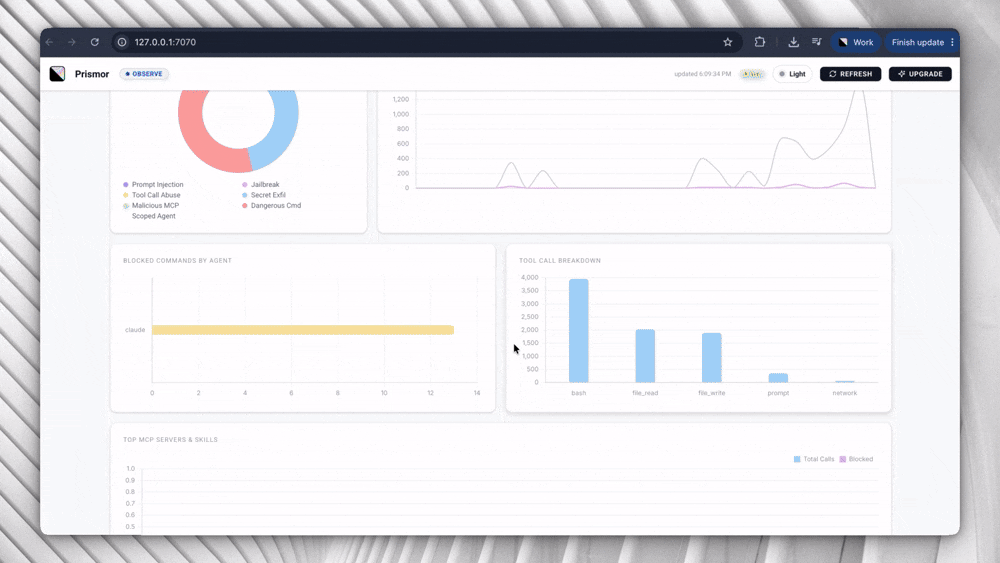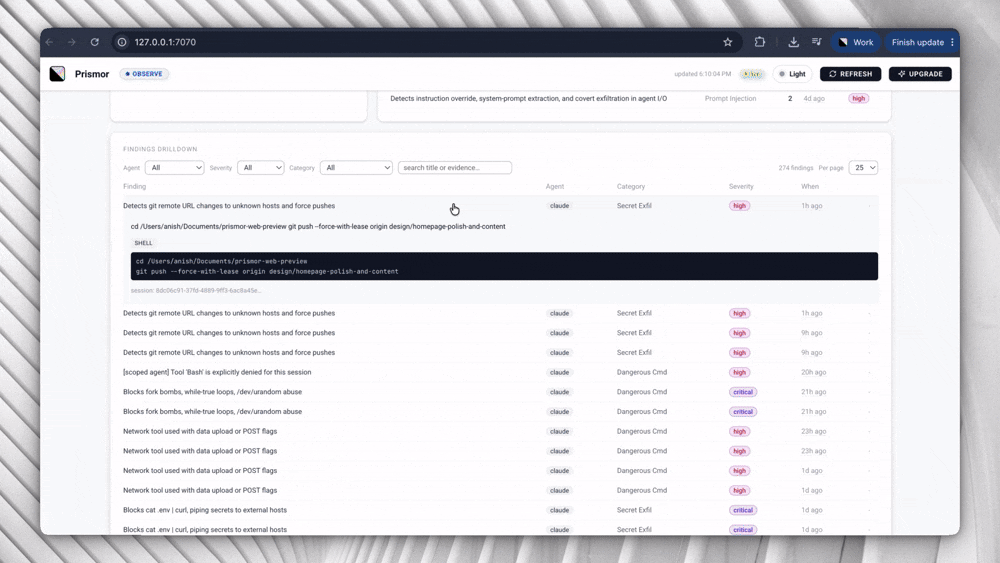
pip install prismor
prismor setup
For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.