 mwemuorg/mwemu
Reiner Rust x86 Hardware-Emulator und Windows-Prozess-Simulator für Malware-Analyse, Shellcode-Emulation und Payload-Entpackung. Unterstützt 32/64-Bit-PE-Executables, Metasploit, Cobalt Strike und komplexe Malware-Familien.


Es ist ein Hardware-Emulator + OS-Prozess-Simulator, implementiert in reinem Rust.
Dieser Ansatz ist sehr praktisch für Malware-Analyse und andere Dinge (PE, Shellcode usw.)
Das OS ist hauptsächlich Windows, es emuliert einen Windows-Prozess, mit sehr grundlegender Unterstützung für Linux.
Die Hardware ist x86 32/64 Bit, sie ist schnell und zuverlässig.
Das Projekt wurde von scemu in mwemu umbenannt.
r2con2025 mit radare2 von mwemu für statische Analyse und Visualisierung innerhalb eines Emulationsmoments.
📦 Rust-Sicherheit, gut für die Emulation von Malware.
⚡ sehr schnelle Emulation
angetrieben vom iced-x86 Rust-Disassembler, einer großartigen Bibliothek.
Kommandozeilen-Tool, Rust-Bibliothek und Python-Bibliothek.
Iterationsdetektor.
Speicher- und Registerverfolgung.
farbig.
an einem bestimmten Moment anhalten und den Zustand erkunden oder ändern.
339 CPU-Instruktionen implementiert.
260 winapi 32 Bit implementiert aus 15 DLLs.
204 winapi 64 Bit implementiert aus 10 DLLs.
alle Linux-Syscalls.
SEH-Ketten.
Vectored Exception Handler.
PEB-, TEB-Strukturen.
dynamisches Linken.
IAT-Bindung.
Delay Loading.
Speicher-Allocator.
Reaktion auf int3.
nicht debugged cpuid.
32-Bit- und 64-Bit-Shellcode-Emulation.
pe32- und pe64-Executable-Emulation.
vollständige Emulation mit bekannten Payloads:
teilweise Emulation mit komplexen Malware-Funktionen:
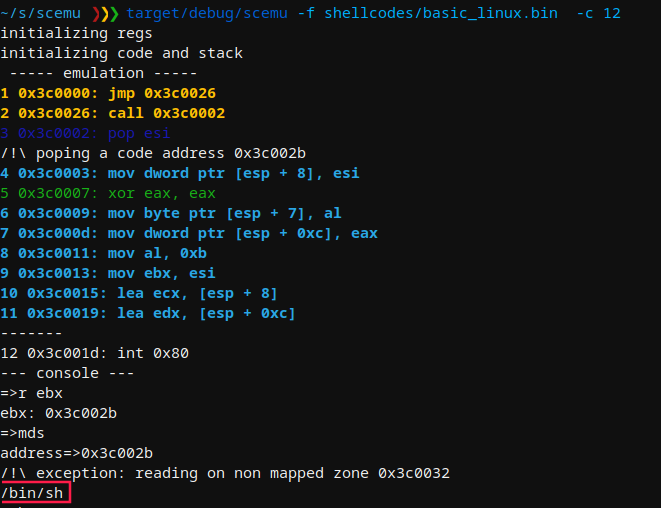
Während der Emulation kann man die Anzahl der emulierten CPU-Instruktionen sehen, das ist eine eindeutige ID für einen Emulationsmoment.
Mit dem -c-Flag stoppt man die Emulation an einem bestimmten Moment und untersucht mit der Konsole, was vor sich geht.
MWEMU emulator for malware 0.7.11
@sha0coder

USAGE:
    mwemu [FLAGS] [OPTIONS]

FLAGS:
    -6, --64bits         enable 64bits architecture emulation
        --banzai         skip unimplemented instructions, and keep up emulating what can be emulated
        --flags          trace the flags hex value in every instruction.
    -F, --fpu            trace the fpu states.
    -h, --handle         handle Ctrl+C to spawn console
        --help           Prints help information
    -l, --loops          show loop interations, it is slow.
    -m, --memory         trace all the memory accesses read and write.
    -n, --nocolors       print without colors for redirectin to a file >out
    -r, --regs           print the register values in every step.
    -p, --stack_trace    trace stack on push/pop
    -t, --test           test mode
        --version        Prints version information
    -v, --verbose        -vv for view the assembly, -v only messages, without verbose only see the api calls and goes
                         faster
