Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
kingfisher — Geheimnisse erkennen. Live validieren. Auswirkungsradius abbilden. Schnell widerrufen. Die CLI ausführen oder in Rust, Python oder Node.js einbetten. | Kitploit
Tools/GitHubGitHub/mongodb/kingfisher
Statische AnalyseSchwachstellenscannerContainer-SicherheitDynamische Code-Analyse (DAST)InformationsbeschaffungCloud-SicherheitDevSecOpsDienstprogramme & FrameworksSecret-ErkennungLieferkettensicherheit
GitHub
1.3k126178vor 2 TagenVon Kitploit geprüft
mongodb/kingfisher

kingfisher

Geheimnisse erkennen. Live validieren. Auswirkungsradius abbilden. Schnell widerrufen. Die CLI ausführen oder in Rust, Python oder Node.js einbetten.
Repository anzeigenWebseite
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

Detect and Validate Secrets Anywhere. Map Access. Revoke Fast.

Kingfisher Logo
Apache 2.0 License Container downloads
GitHub downloads PyPI downloads

Find leaked secrets. Validate what’s live. Map the blast radius. Revoke fast.

Kingfisher is a fast, free, open-source secret scanner and credential response tool built in Rust. It detects leaked secrets with hundreds of built-in rules, validates which credentials are active, maps access for supported credential types, and revokes supported secrets—all in one Apache-2.0-licensed release:

Detect → Validate → Map → Triage → Revoke

  • scan source code, Git history, cloud storage, container images, archives, and developer platforms
  • validate which credentials are active
  • map a leaked secret's identity, permissions, and reachable resources
  • triage findings in a browser, or output as SARIF, JSON, TOON
  • send real-time alerts to Slack, Microsoft Teams, Discord, Mattermost, Google Chat, or any JSON webhook
  • revoke supported secrets

Defender workflow: Follow the end-to-end defender workflow for secret detection, validation, notifications, blast-radius mapping, and revocation.

Embed Kingfisher in Python, Node.js, or Rust

Add native secret detection, live credential validation, and explicit revocation to your Python, JavaScript/TypeScript (Node.js), or Rust application. The same Rust engine and rule catalog run in-process, with no CLI subprocess required. Kingfisher is an embeddable secret scanner that also runs as a standalone CLI.
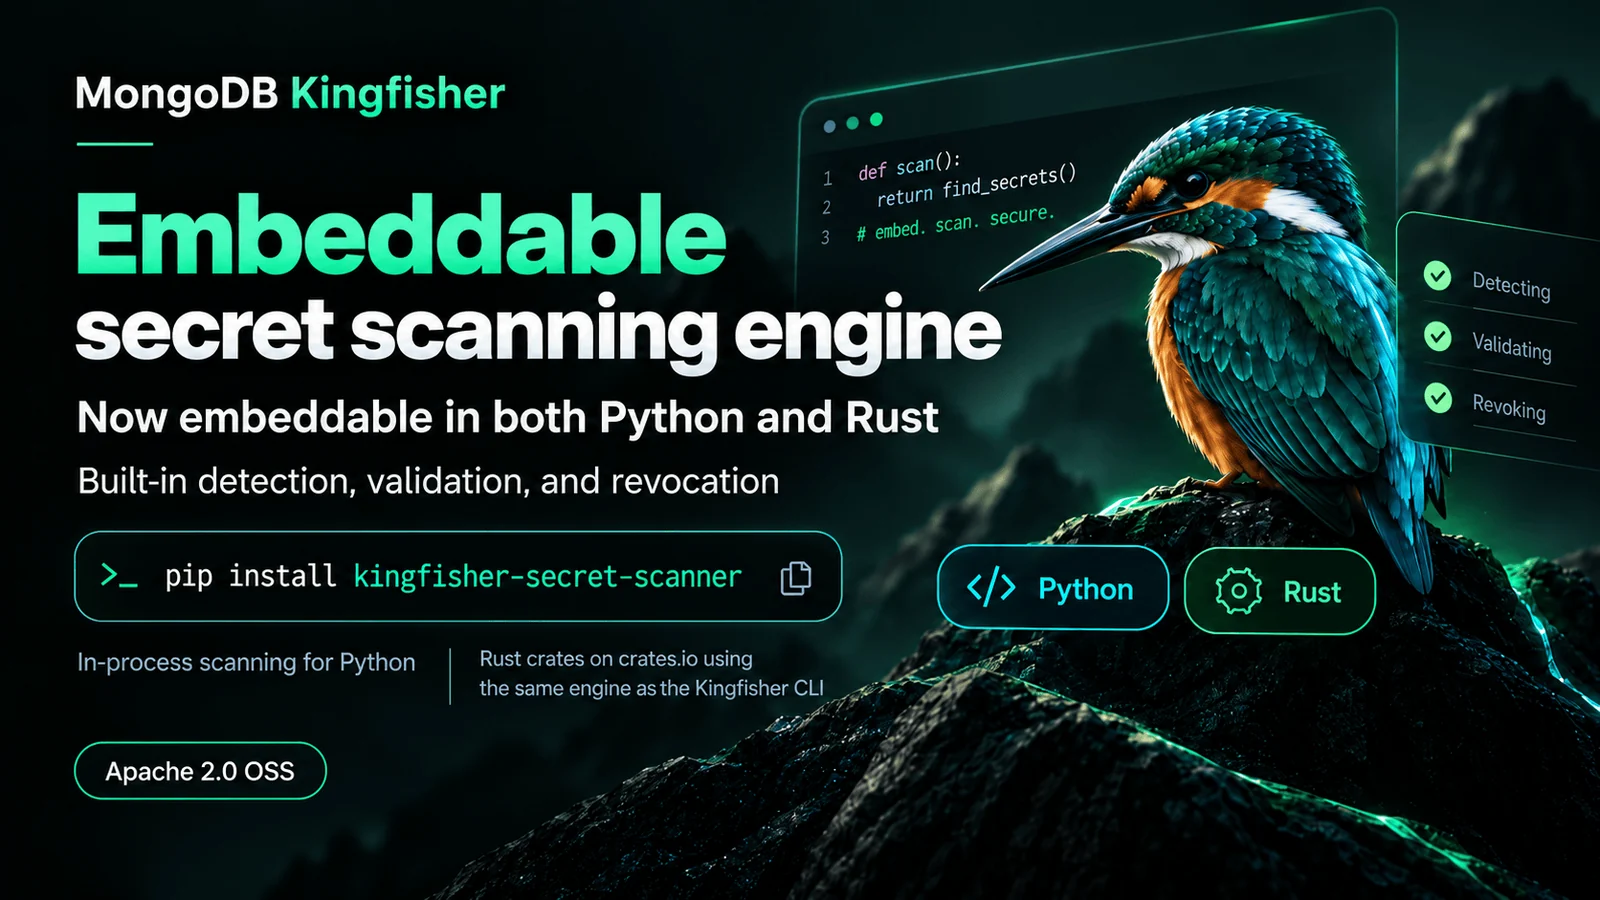
Kingfisher embeddable secret scanner: Detect Secrets → Validate → Map Blast Radius → Revoke. Native Python, Node.js/TypeScript and Rust SDK installs, plus CLI installation and HTML report commands.

Choose your language and add the SDK to your existing application:

  • Python:

    uv add kingfisher-secret-scanner
    

    Import kingfisher_sdk. See the Python SDK guide and runnable examples for scanning, validation, rule inspection, and explicit revocation.

  • Node.js / TypeScript:

    npm install kingfisher-secret-scanner
    

    The stable npm SDK 1.0.0 wraps the same Rust crates with napi-rs. See the Node SDK guide and source/examples. It targets Node.js, including VS Code workspace extensions, rather than browser/WASM runtimes. Explore Kingfisher Workbench, a commented showcase with live progress, Git-history scanning and a redacted HTML report, or start with the runnable recipe walkthrough; maintainers can follow the npm trusted-publishing setup.

  • Rust:

    cargo add kingfisher-scanner --features validation
    

    The validation feature enables live validation and revocation; omit --features validation for detection only. See the library guide, runnable examples, and revocation guide.

Or install the CLI, scan a codebase, and open the interactive HTML report:

uv tool install kingfisher-bin
kingfisher scan /path/to/code --view-report

Replace /path/to/code with your source directory. Scans validate credentials by default; add --no-validate for detection only. Add --blast-radius to map supported credentials' access when authorized. Revocation remains a separate, explicit action. See the CLI installation guide and usage guide for more options.

Scan Targets

Kingfisher handles local files and directories, Git repositories and history, compressed and office-document archives, SQLite databases, Python bytecode, Docker images, source-hosting organizations, cloud object storage, collaboration tools, and API-development platforms.

Files / DirsLocal GitGitHubGitLabAzure ReposBitbucketGiteaHugging Face
Files / Dirs
Files / Dirs
Local Git
Local Git
GitHub
GitHub
GitLab
GitLab
Azure Repos
Azure Repos
Bitbucket
Bitbucket
Gitea
Gitea
Hugging Face
Hugging Face
Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Das System der Handlung für KI-native Cybersicherheit – wo Absicht zu gesteuerter Ausführung wird, Beweise zu operativem Gedächtnis werden und jeder Einsatz den nächsten verbessert.

    264

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →