 fortra/no-consolation
Ein BOF, der nicht verwaltete PEs inline ausführt

Dies ist eine Beacon Object File (BOF), die nicht verwaltete PEs inline ausführt und deren Ausgabe abruft, ohne eine Konsole zuzuweisen (d. h. ohne conhost.exe zu starten).
Summary: Run an unmanaged EXE/DLL inside Beacon's memory.

Usage: noconsolation [--local] [--inthread] [--link-to-peb] [--dont-unload] [--timeout 60] [-k] [--method funcname] [-w] [--no-output] [--alloc-console] [--close-handles] [--free-libraries wininet.dll,winhttp.dll] [--dont-save] [--list-pes] [--unload-pe pename] [--load-all-dependencies] [--load-all-dependencies-but advapi32.dll] [--load-dependencies wininet.dll] [--search-paths C:\Windows\Temp\] /path/to/binary.exe arg1 arg2
    --local, -l                                    Optional. The binary should be loaded from the target Windows machine
    --inthread, -it                                Optional. Run the PE with the main thread. This might hang your beacon depending on the PE and its arguments.
    --link-to-peb, -ltp                            Optional. Load the PE into the PEB
    --dont-unload, -du                             Optional. If set, the DLL won't be unloaded.
    --timeout NUM_SECONDS, -t NUM_SECONDS          Optional. The number of seconds you wish to wait for the PE to complete running. Default 60 seconds. Set to 0 to disable
    -k                                             Optional. Overwrite the PE headers
    --method EXPORT_NAME, -m EXPORT_NAME           Optional. Method or function name to execute in case of DLL. If not provided, DllMain will be executed
    -w                                             Optional. Command line is passed to unmanaged DLL function in UNICODE format. (default is ANSI)
    --no-output, -no                               Optional. Do not try to obtain the output
    --alloc-console, -ac                           Optional. Allocate a console. This will spawn a new process
    --close-handles, -ch                           Optional. Close Pipe handles once finished. If PowerShell was already ran, this will break the output for PowerShell in the future
    --free-libraries, -fl DLL_A,DLL_B              Optional. List of DLLs (previously loaded with --dont-unload) to be offloaded
    --dont-save, -ds                               Optional. Do not save this binary in memory
    --list-pes, -lpe                               Optional. List all PEs that have been loaded in memory
    --unload-pe PE_NAME, -upe PE_NAME              Optional. Unload from memory a PE
    --load-all-dependencies, -lad                  Optional. Custom load all the PE's dependencies
    --load-all-dependencies-but, -ladb DLL_A,DLL_B Optional. Custom load all the PE's dependencies except these
    --load-dependencies, -ld DLL_A,DLL_B           Optional. Custom load these PE's dependencies
    --search-paths, -sp PATH_A,PATH_B              Optional. Look for DLLs on these paths (system32 is the default)

    /path/to/binary.exe                   Required. Full path to the windows EXE/DLL you wish you run inside Beacon. If already loaded, you can simply specify the binary name.
    ARG1 ARG2                             Optional. Parameters for the PE. Must be provided after the path

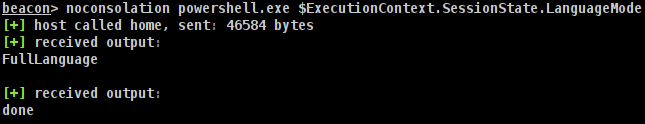
    Example: noconsolation --local C:\windows\system32\windowspowershell\v1.0\powershell.exe $ExecutionContext.SessionState.LanguageMode
    Example: noconsolation /tmp/mimikatz.exe privilege::debug token::elevate exit
    Example: noconsolation --local C:\windows\system32\cmd.exe /c ipconfig
    Example: noconsolation --list-pes
    Example: noconsolation LoadedBinary.exe args
Binaries werden nach ihrer ersten Ausführung automatisch verschlüsselt und im Speicher abgelegt. Das bedeutet, dass Sie das Binary nicht ständig über das Netzwerk senden müssen.
Um ein Binary auszuführen, das bereits im Speicher gespeichert wurde, geben Sie einfach seinen Namen anstelle des vollständigen Pfads an. Anstatt also Folgendes auszuführen:
beacon> noconsolation --local C:\windows\system32\cmd.exe /c ipconfig
Stattdessen führen Sie Folgendes aus:
beacon> noconsolation cmd.exe /c ipconfig
Um alle im Speicher geladenen Binaries aufzulisten, führen Sie --list-pes aus.
Wenn Sie mit einem Binary fertig sind und es entladen möchten, führen Sie --unload-pe mimikatz.exe aus.
Wenn Sie schließlich ein Binary ausführen möchten, ohne dass es automatisch in den Speicher geladen wird, führen Sie es mit --dont-save aus.
Sie können alle Image-Load-Ereignisse vermeiden, indem Sie alle Abhängigkeiten der PE benutzerdefiniert laden:
beacon> noconsolation --load-dependencies --link-to-peb /tmp/malware.exe
Nach Abschluss der Ausführung werden die PE und ihre Abhängigkeiten automatisch entladen.
DLLs, die Thread Local Storage verwenden, werden nicht unterstützt.
