Tool-Verzeichnis
Kategorien
Tools / GitHub / ch4120n / ch4120n-cve-pulse
Entdecken Sie die meistgenutzten Tools unserer Community.
Letzte 7 Tage Letzte 30 Tage
ch4120n/ch4120n-cve-pulse
Ch4120N-CVE-Pulse Live-CVE-PoC-Aggregator (Proof-of-Concepts) mit intelligenter Suche & Threat Intelligence
CVE Pulse
CVE-Proof‑of‑Concepts
EPSS-Scores
CISA-KEV
Snapshots & Diffs
statische Website
📋 Inhaltsverzeichnis
👨💻 Projektersteller
🎯 Was es macht
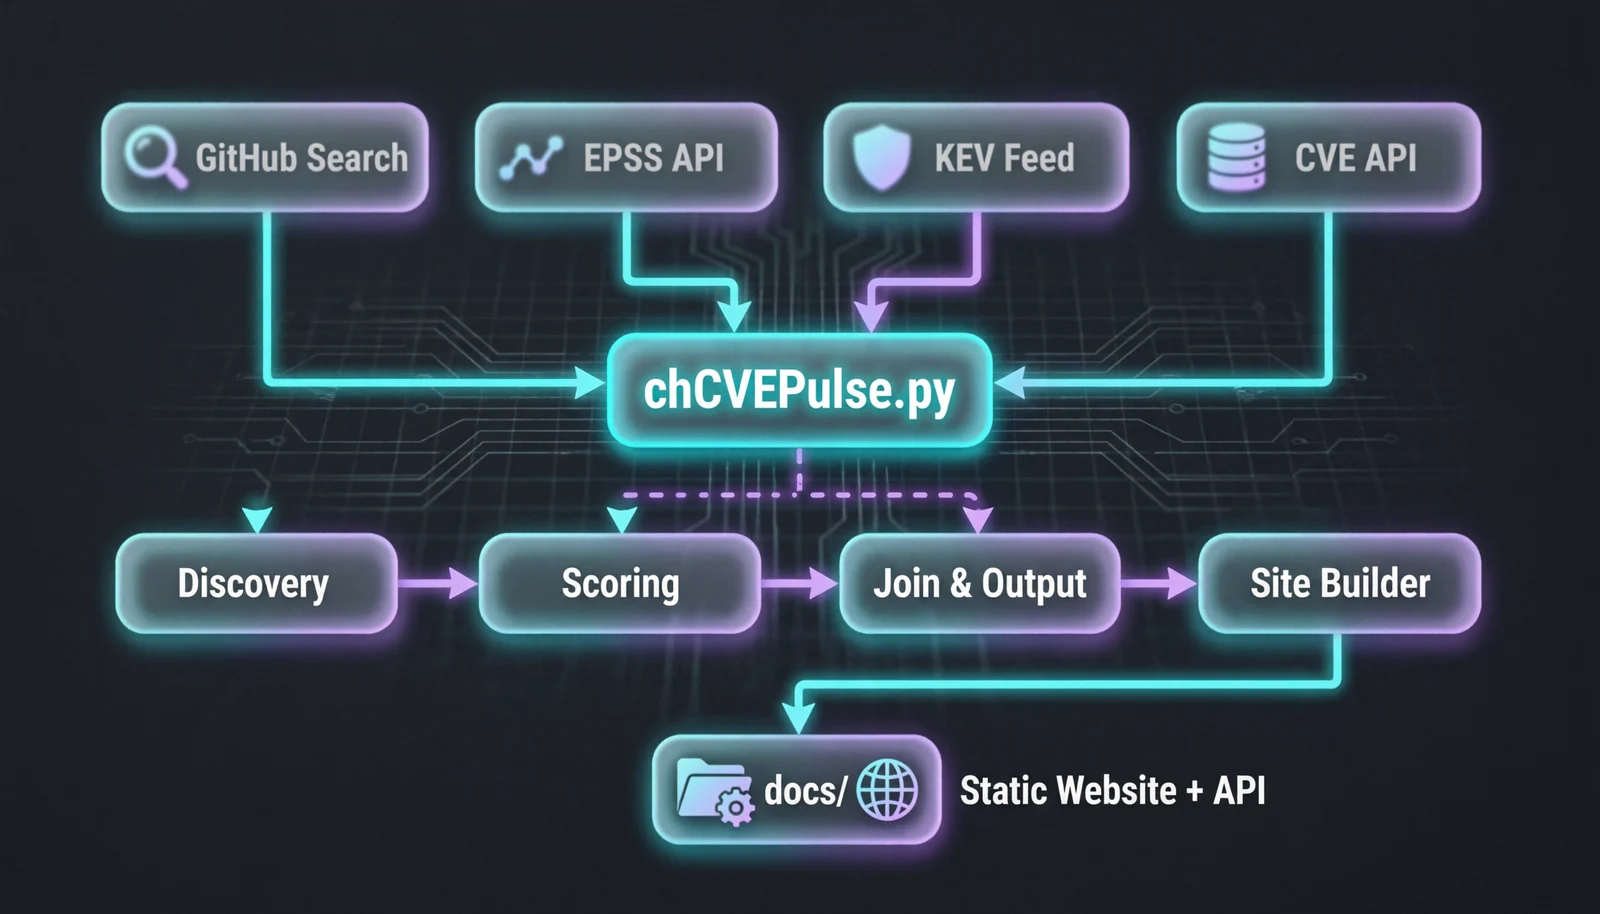
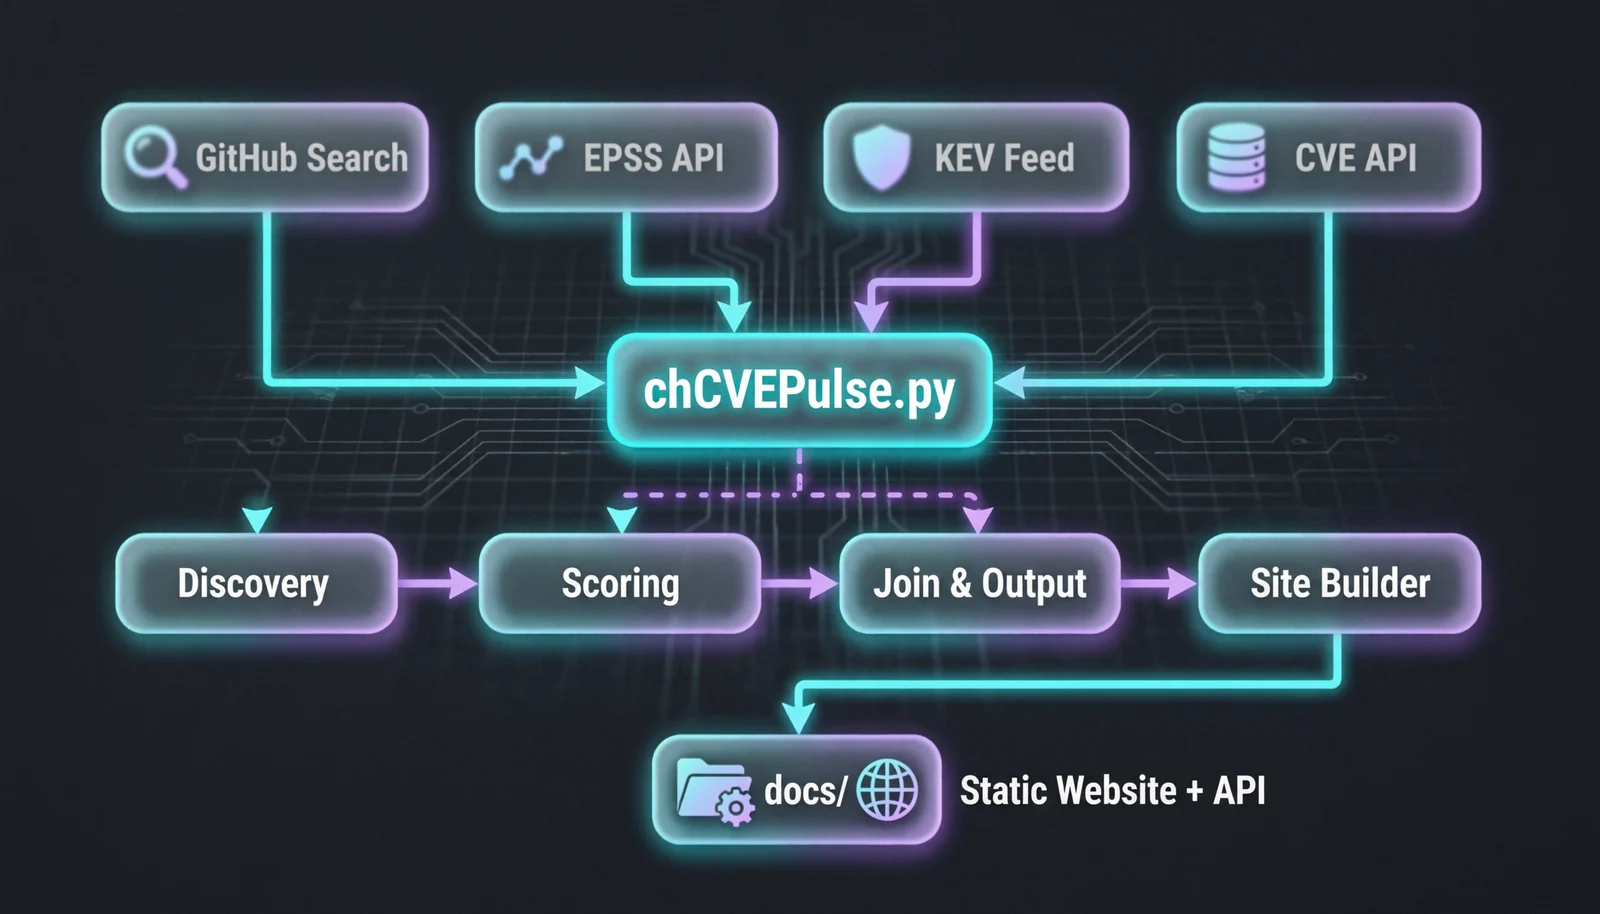
Ruft die neuesten EPSS-Scores und den CISA-Katalog der bekannten ausgenutzten Schwachstellen (KEV) ab.Durchsucht GitHub nach Repositories, die Exploit-PoCs für CVEs enthalten (mittels Suche + GraphQL-Metadaten).Bewertet jeden Kandidaten mit einem Konfidenzmodell (Stars, Aktualität, Keyword-Übereinstimmungen, Blacklist usw.).Verknüpft die PoC-Daten mit EPSS und KEV und erstellt dann eine vollständige JSON-API.Generiert eine statische Website mit einer leistungsstarken clientseitigen Suchmaschine.Erstellt tägliche Snapshots und Diffs , damit du neue PoCs mit hoher Konfidenz verfolgen kannst.
✨ Hauptfunktionen
🔍 Automatisierte PoC-Entdeckung – GitHub-Code-/Repository-Suche über mehrere Zeitfenster
🧠 Intelligente Bewertung – Code- vs. Dokumentations-Übereinstimmungen, Star-Anzahl, Aktualität, Blacklist und Heuristiken
📈 EPSS- & KEV-Integration – CISAs KEV-Liste und FIRSTs EPSS-Scores werden mit PoC-Daten zusammengeführt
📊 Tägliche Snapshots & Diffs – sieh, was neu ist, was zu „hoher Konfidenz" hochgestuft und was entfernt wurde
🌐 Durchsuchbare Website – Fuzzy-Suche nach CVE-ID, Hersteller, Produkt, Keyword, mit negativen Filtern (-windows)
🚀 Vollständig automatisiert – GitHub-Actions-Pipelines aktualisieren alles nach Zeitplan
💾 Keine Serverkosten – alle Daten sind statisches JSON/HTML, gehostet auf GitHub Pages
🛡️ Blacklist-Unterstützung – ignorieren Sie rauschige oder irrelevante Repositories
🧱 Architektur
⚙️ Wie es funktioniert
fetch-epssfetch-kevsync-cvesdata/github.txt und ruft CVE-Metadaten von der MITRE-API ab, dann werden Markdown-Dateien für jede CVE erstellt/aktualisiert.pipelinebuild-*-Befehle):
Erstellt einen Scope von CVEs zum Scannen (aus github.txt oder zuvor niedrig-konfidenten).
Verwendet die GitHub-Such-API, um Repositories zu finden, die die CVE-ID erwähnen.
Reichert Kandidaten mit Repository-Metadaten (Stars, Sprache, Themen) über GraphQL an.
Bewertet jedes Repository und weist eine Konfidenzstufe zu (hoch , mittel , niedrig ).
Schreibt JSON-Dateien pro CVE, einen Index und eine Top-100-Liste.
Erstellt einen Snapshot des aktuellen Zustands und ein Diff gegenüber dem Vortag.
build-siteCVE_list.json, trending_poc.json und die statische HTML-Seite.Die Website (docs/) wird auf GitHub Pages bereitgestellt.
🚀 Schnellstart```bash
Clone the repository
Install dependencies pip install -r requirements.txt
Download base data python chCVEPulse.py fetch-epss
python chCVEPulse.py fetch-kev
Sync your initial CVE list (from data/github.txt) python chCVEPulse.py sync-cves
Run the full discovery pipeline (needs GITHUB_TOKEN for higher rate limits) export GITHUB_TOKEN=your_token_here
python chCVEPulse.py pipeline --days 7
Generate the static website python chCVEPulse.py build-site
Open docs/index.html in your browser ---
## 📦 Installation
**Voraussetzungen:**
- Python 3.9+
- `pip`
Installiere die Pakete:```bash
pip install -r requirements.txt
(requirements.txt enthält requests, jinja2 und weitere Abhängigkeiten.)
💻 Verwendung Alle Vorgänge laufen über das einzelne Skript chCVEPulse.py.
Unterbefehle Befehl Beschreibung fetch-epssEPSS-Daten herunterladen fetch-kevKEV-Katalog herunterladen sync-cvesCVE-Markdowns aus data/github.txt aktualisieren build-siteDie statische Website generieren (CVE-Liste + HTML) build-diffsTäglichen Diff aus den letzten beiden Snapshots erstellen build-joinedZusammengeführte KEV+EPSS+PoC-JSON-Endpunkte erstellen pipelineDie vollständige Pipeline ausführen (discover → output → diff → site)
Fetch new data python chCVEPulse.py fetch-epss --limit 2000
python chCVEPulse.py fetch-kev
Update a specific CVE python chCVEPulse.py sync-cves --cve CVE-2025-12345
Full pipeline (daily mode) python chCVEPulse.py pipeline --days 7 --mode daily --limit 50
Regenerate website only python chCVEPulse.py build-site --html-mode summary
### Vollständige Pipeline

Der `pipeline`-Unterbefehl kann fein abgestimmt werden:

- `--days` : wie viele Tage zurück GitHub durchsucht werden soll (Standard: 7)
- `--mode` : `daily` (aktuelle CVEs, schneller) oder `weekly` (breiterer Scan)
- `--limit` : maximale Anzahl zu scannender CVEs (Standard: 50)
- `--cve` : eine oder mehrere CVE-IDs zum Scannen angeben
- `--skip-discovery` : nur Ausgaben aus vorhandenen Daten neu generieren
- `--check-links` : überprüfen, ob Repository-URLs noch erreichbar sind

---

## 📊 Ausgabe & Website

Nach einem erfolgreichen Pipeline-Lauf enthält `docs/`:

- **`index.html`** – die Hauptsuchseite (unterstützt von `logic.js` und `style.css`)
- **`CVE_list.json`** – alle CVEs mit Beschreibungen und PoC-Links
- **`trending_poc.json`** – kürzlich aktualisierte PoCs (aus der automatisch aktualisierten README)
- **`api/v1/`** – vollständige REST-ähnliche JSON-Endpunkte:
  - `joined_top.json` – CVEs mit hoher Priorität mit PoCs, EPSS und KEV-Status
  - `kev.json` – angereicherte KEV-Liste
  - `epss_top.json` – Top-EPSS-CVEs mit PoCs
  - `cve/{CVE-ID}.json` – detaillierte PoC-Informationen pro CVE
  - `snapshots/` – tägliche Status-Snapshots
  - `diffs/` – tägliche Änderungen

Die Suche unterstützt **Fuzzy-Matching**, Hersteller-/Produktfilter und negative Begriffe (z. B. `-windows`).

---

## 🗂️ Projektstruktur```
Ch4120N-CVE-Pulse/
├── chCVEPulse.py
├── scripts/
│   ├── config.py
│   ├── helpers.py
│   ├── github_api.py
│   ├── scoring.py
│   ├── discovery.py
│   ├── outputs.py
│   ├── diff.py
│   ├── joined.py
│   ├── site.py
│   ├── sync.py
│   ├── fetch_epss.py
│   ├── fetch_kev.py
│   └── pipeline.py
├── templates/
│   └── index.html# Jinja2 template for the website
├── data/
│   ├── github.txt# CVE -> PoC URL list (edit this)
│   ├── blacklist.txt
│   ├── cache/
│   └── evidence/
├── docs/
│   ├── api/v1/
│   └── index.html, style.css, logic.js
├── requirements.txt
└── README.md
🔧 Konfiguration Fast alle Einstellungen befinden sich in scripts/config.py:
GITHUB_SOURCES – Pfad zu deiner data/github.txtEPSS_API_URL, KEV_URL, CVE_API_TEMPLATE – externe API-EndpunkteHIGH_EPSS_THRESHOLD – minimaler EPSS-Wert für „hohe“ WarnungenTOP_KEV_COUNT – wie viele KEV-Einträge behalten werdenSNAPSHOT_RETENTION_DAYS – wie lange alte Snapshots aufbewahrt werden
📡 Datenquellen Quelle Beschreibung GitHub Search API Entdeckt Repositories, die CVE-IDs erwähnen GitHub GraphQL Ruft Star-Anzahl, Sprache, Themen, Fork-/Archiv-Status ab FIRST EPSS Exploit Prediction Scoring System CISA KEV Katalog bekannter ausgenutzter Schwachstellen MITRE CVE API Offizielle CVE-Beschreibungen, Referenzen, Produkte
Ein GitHub-Token wird empfohlen, um die API-Ratenlimits zu erhöhen (als Umgebungsvariable GITHUB_TOKEN festlegen).
📅 Automatisierung (CI/CD) Drei GitHub-Actions-Workflows halten alles aktuell:
sync_cve_pocs.ymldata/github.txt, ruft frische CVE-Metadaten ab und aktualisiert Markdown-Dateien.hot_cves.ymlTrending PoCs in dieser README.site.yml Alle Workflows befinden sich in .github/workflows/.
📈 Trending PoCs
Die untenstehende Tabelle Trending PoCs wird automatisch aktualisiert – alle 6 Stunden durch die CI-Pipeline.
2026 (latest 20 of 584 repos)
2025 (latest 20 of 594 repos)
2024 (latest 20 of 636 repos) Stars Updated Repository Description 2456⭐ 2 days ago CVE-2024-1086 Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including Debian, Ubuntu, and KernelCTF. The success rate is 99.4% in KernelCTF images. 689⭐ 1 day ago CVE-2024-38063 poc for CVE-2024-38063 (RCE in tcpip.sys) 497⭐ 20 days ago cve-2024-6387-poc a signal handler race condition in OpenSSH's server (sshd) 517⭐ 1 day ago CVE-2024-49113 LdapNightmare is a PoC tool that tests a vulnerable Windows Server against CVE-2024-49113 526⭐ 2 days ago CVE-2024-6387_Check CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH 224⭐ 31 days ago CVE-2024-38077 RDL的堆溢出导致的RCE 378⭐ 23 days ago cve-2024-6387-poc 32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc 333⭐ 8 days ago CVE-2024-21338 Local Privilege Escalation from Admin to Kernel vulnerability on Windows 10 and Windows 11 operating systems with HVCI enabled. 331⭐ 5 days ago CVE-2024-0044 CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13 320⭐ 2 days ago CVE-2024-4577 PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC 285⭐ 2 days ago
2023 (latest 20 of 531 repos)
2022 (latest 20 of 560 repos)
⚠️ Haftungsausschluss Dieses Projekt ist für Threat Intelligence, Schwachstellenmanagement und defensive Sicherheitsforschung gedacht.
📄 Lizenz GPLv3 -Lizenz – den vollständigen Text findest du in der Datei LICENSE .
"Stay ahead of threats – track every CVE PoC in real time."
⭐ Wenn dir dieses Projekt hilft, ziehe bitte einen Stern in Betracht!
Made with ❤️ by Ch4120N
CVE-2026-75604 Next.js Windows RCE poc
102⭐ 23 hours ago CVE-2026-43499-Poc-Analysis Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only.
18⭐ 6 days ago CVE-2026-43499-Poc-Analysis Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only.
63⭐ 29 days ago CVE-2026-45504 CVE-2026-45504 Microsoft Exchange File Read
109⭐ 6 days ago Copy-Fail-Exploit-CVE-2026-31431 Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python script (or .c elf) roots every Linux distribution shipped since 2017.
432⭐ 2 days ago Next.js-RSC-RCE-Scanner-CVE-2025-66478 A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.
197⭐ 1 day ago POC-CVE-2025-24813 his repository contains an automated Proof of Concept (PoC) script for exploiting CVE-2025-24813 , a Remote Code Execution (RCE) vulnerability in Apache Tomcat. The vulnerability allows an attacker to upload a malicious serialized payload to the server, leading to arbitrary code execution via deserialization when specific conditions are met.
160⭐ 8 days ago CVE-2025-21756 Exploit for CVE-2025-21756 for Linux kernel 6.6.75. My first linux kernel exploit!
195⭐ 27 days ago CVE-2025-32756-POC Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products.
CVE-2024-21413 PoC for THM Lab
195⭐ 2 days ago CVE-2024-6387 Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387)
181⭐ 6 days ago CVE-2024-25600 Unauthenticated Remote Code Execution – Bricks <= 1.9.6
87⭐ 40 days ago CVE-2024-40725-CVE-2024-40898 CVE-2024-40725 and CVE-2024-40898, affecting Apache HTTP Server versions 2.4.0 through 2.4.61. These flaws pose significant risks to web servers worldwide, potentially leading to source code disclosure and server-side request forgery (SSRF) attacks.
113⭐ 14 days ago CVE-2024-6387 PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
156⭐ 16 days ago CVE-2024-21413 Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
VMWare vRealize Network Insight Pre-Authenticated RCE (CVE-2023-20887)
236⭐ 2 days ago CVE-2023-29357 Microsoft SharePoint Server Elevation of Privilege Vulnerability
166⭐ 8 days ago CVE-2023-25157 CVE-2023-25157 - GeoServer SQL Injection - PoC
281⭐ 10 days ago CVE-2022-0847 CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847 的漏洞原理类似于 CVE-2016-5195 脏牛漏洞(Dirty Cow),但它更容易被利用。漏洞作者将此漏洞命名为“Dirty Pipe”
354⭐ 18 hours ago CVE-2022-21894 baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
238⭐ 31 days ago CVE-2022-20699 Cisco Anyconnect VPN unauth RCE (rwx stack)
236⭐ 9 days ago CVE-2022-30075 Tp-Link Archer AX50 Authenticated RCE (CVE-2022-30075)
218⭐ 10 days ago CVE-2022-34918 CVE-2022-34918 netfilter nf_tables 本地提权 POC

 ch4120n/ch4120n-cve-pulse