
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Einreichen
ToolsExploitsBlog
Einreichen

Hacking-, PenTest- und Cybersicherheits-Tools für Ihr Sicherheitsarsenal!

Kitploit ist ein Verzeichnis von Hacking-, Cybersicherheits- und Pentesting-Tools. Entdecken Sie die neuesten Projekt-Updates, um Schwachstellen zu finden, Systeme zu analysieren, Tests zu automatisieren und Ihre Sicherheit zu stärken.

FeedsKontaktDatenschutz© 2026 Kitploit

Tool-Verzeichnis

Kategorien

Alle Kategorien anzeigen
Loading categories
CVE-2026-11645 — Advisory repository documenting CVE-2026-11645, a Chrome V8 out-of-bounds memory corruption zero-day enabling RCE, with affected versions, detection indicators, and patch guidance. | Kitploit
Tools/GitHubGitHub/ashrafzaryouh/cve-2026-11645
Vulnerability AnalysisWeb SecurityThreat IntelligenceLearning & Education
GitHubashrafzaryouh/cve-2026-11645

CVE-2026-11645

Advisory repository documenting CVE-2026-11645, a Chrome V8 out-of-bounds memory corruption zero-day enabling RCE, with affected versions, detection indicators, and patch guidance.

Repository anzeigen
1vor 5 MonatenNoch nicht geprüft

Beliebteste

Alle anzeigen →

Entdecken Sie die meistgenutzten Tools unserer Community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 Das ultimative OSINT-Toolkit: Untersuchungsgraph, Konfidenzbewertung, Alias-Familien, Karte, Zeitleiste und Berichte. 49 Module, 400+ Websites, keine API-Schlüssel erforderlich.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    618
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT-Plattform, die Shadowserver-Berichte in MongoDB einliest und sie als interaktive Karten, Analysen, Findings, Advisories und Executive-Dashboards wiedergibt.

    411
  • 4

    ARTEX

    baarai/artex

    LLM-basierte Multi-Agenten-Plattform für autonome Penetrationstests mit Planer-/Worker-Agenten, Asset- und Explorationsgraphen, MITM-Verkehrsaufzeichnung und Schwachstellen-Retesting.

    328
  • 5

    jumpserver

    jumpserver/jumpserver

    JumpServer ist eine Open-Source-Plattform für Privileged Access Management (PAM), die DevOps- und IT-Teams bedarfsgesteuerten und sicheren Zugriff auf SSH-, RDP-, Kubernetes-, Datenbank- und RemoteApp-Endpunkte über einen Webbrowser bietet.

    314
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    KI-gestützte OSINT-Engine zur Entdeckung und Kartierung von über 7.700 Social-Media-Identitäten im gesamten Web

    275

Alle Tools erkunden

Durchsuchen Sie unsere Tool-Sammlung

Alle Tools anzeigen →
Teilen
Inhalt in der angeforderten Sprache nicht verfügbar. Englische Version wird angezeigt.

🚨 CVE-2026-11645 🚨

🌐 Google Chrome V8 Zero-Day Memory Corruption Vulnerability

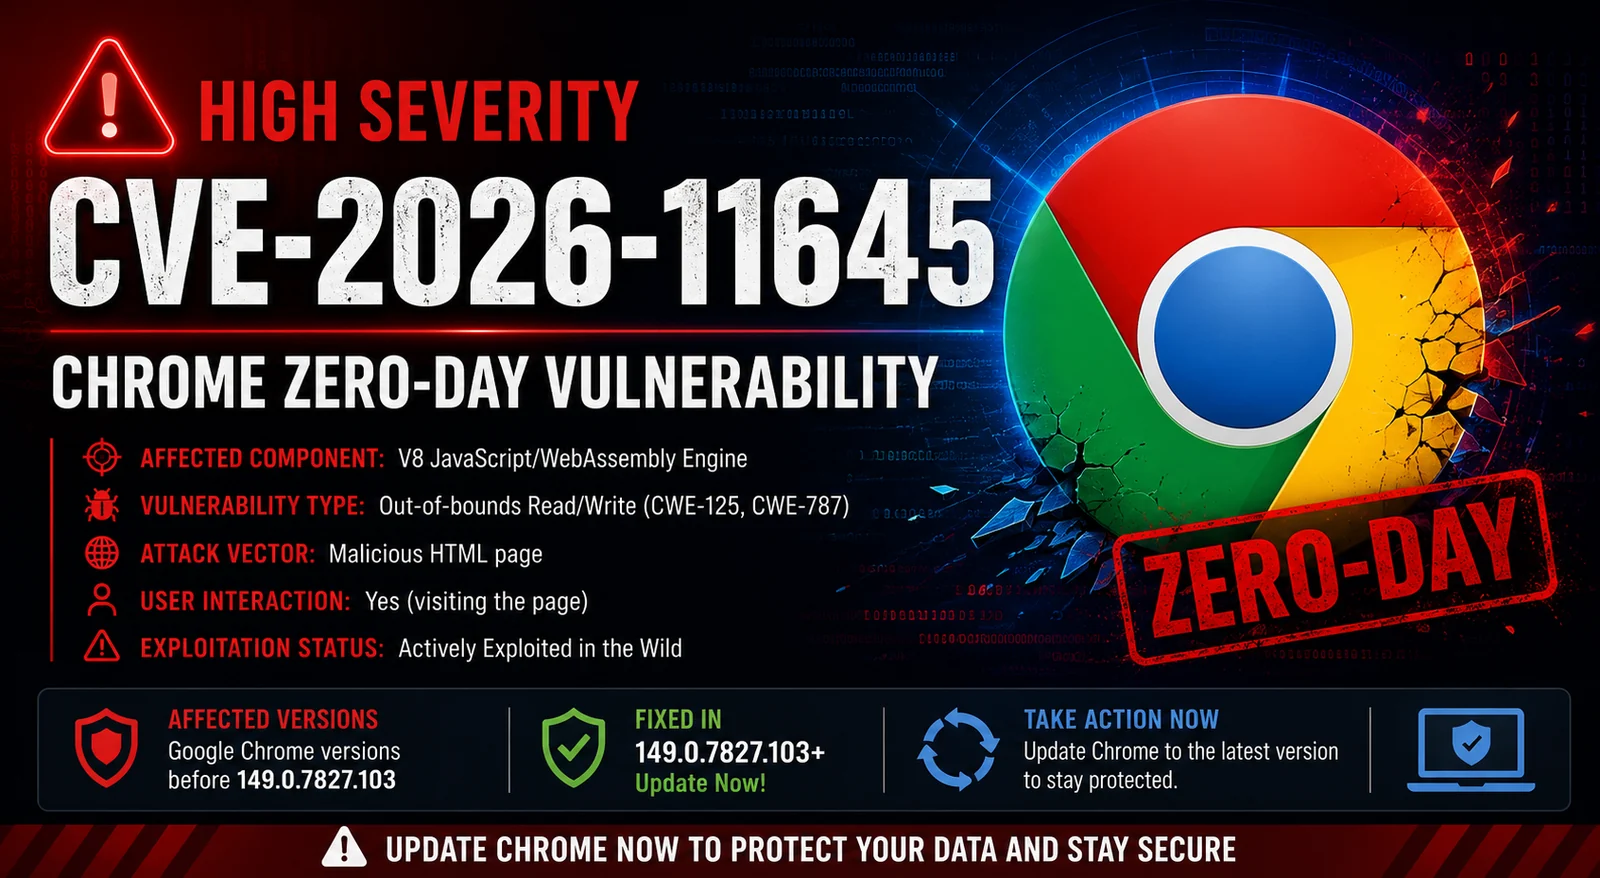
ChatGPT Image Jun 11, 2026, 04_25_47 PM

Severity CVSS Status Chrome

🔥 Actively Exploited Zero-Day

⚡ V8 Engine Memory Corruption

🛡️ Patch Immediately


📖 Overview

⚠️ CVE-2026-11645 is a high-severity zero-day vulnerability affecting the Google Chrome V8 JavaScript engine. The flaw allows attackers to trigger an Out-of-Bounds Read/Write condition that may lead to Remote Code Execution (RCE).


🎯 Vulnerability Information

🏷️ Field📋 Value
CVECVE-2026-11645
🔥 SeverityHigh
📊 CVSS8.8
🏢 VendorGoogle
🌐 ProductChrome
🧩 ComponentV8 Engine
💥 TypeOut-of-Bounds Read/Write
⚠️ ExploitedYes
🎯 ImpactRemote Code Execution

🧠 Technical Summary

The vulnerability exists within Chrome's V8 JavaScript engine.

An attacker can craft a malicious webpage that:

  • 🎯 Triggers memory corruption
  • 📖 Reads unintended memory regions
  • ✍️ Writes outside allocated boundaries
  • 💻 Executes arbitrary code
  • 🔓 Assists exploitation chains
  • 🚨 Causes browser crashes

⚔️ Attack Chain

🌐 Victim Opens Malicious Website
                │
                ▼
📜 Crafted JavaScript Payload
                │
                ▼
🧩 V8 Engine Vulnerability Triggered
                │
                ▼
💥 Out-of-Bounds Memory Access
                │
                ▼
⚡ Remote Code Execution
                │
                ▼
🚨 Browser Compromise

🎯 Affected Versions

❌ Vulnerable

Chrome < 149.0.7827.103
CVE-2026-11645

✅ Fixed

🪟 Windows : 149.0.7827.102+
🍎 macOS   : 149.0.7827.103+
🐧 Linux   : 149.0.7827.102+

💥 Potential Impact

ImpactRisk
⚡ Remote Code Execution🔴 High
🔍 Information Disclosure🔴 High
💣 Browser Crash🟠 Medium
🔗 Exploit Chaining🟠 Medium
🏢 Enterprise Risk🔴 High

🔎 Detection Opportunities

Monitor for:

🚨 Indicators:
  - Unexpected browser crashes
  - Suspicious JavaScript activity
  - Exploit-kit traffic
  - Malicious domain visits
  - Unusual Chrome child processes
  - Browser memory anomalies

🛡️ Mitigation

🚀 Immediate Actions

chrome://settings/help

✅ Recommendations

  • 🔄 Update Chrome immediately
  • 🛡️ Enable automatic updates
  • 🔒 Restrict untrusted extensions
  • 📡 Monitor browser telemetry
  • 🚨 Review EDR alerts
  • 📊 Track threat intelligence feeds

📈 Risk Assessment

Likelihood  : ██████████  HIGH
Impact      : ██████████  HIGH
Overall     : 🚨 CRITICAL 🚨

📚 References

  • 🌐 Google Chrome Security Advisory
  • 🏛️ NIST National Vulnerability Database
  • 🔬 Chromium Security Updates

⚠️ Disclaimer

This repository is provided for:

  • 🎓 Security Education
  • 🔍 Vulnerability Research
  • 🛡️ Defensive Security
  • 📊 Patch Management

❌ No exploit code is included.


⭐ Stay Updated • Patch Early • Hunt Smart ⭐

🚀 Cyber Threat Intelligence Repository 🚀

Tool herunterladen