

opencti v7.260907.0
Offene Plattform für Cyber-Bedrohungsinformationen




The open source threat intelligence platform at the heart of Continuous Threat Exposure Management.
OpenCTI turns cyber threat intelligence into a living knowledge graph: who targets you, how they operate, which vulnerabilities and tools they rely on, and what your defenses already cover. It is the threat intelligence foundation of CTEM in the XTM Platform: know the adversary in OpenCTI, validate your exposure to it with OpenAEV, quantify the risk with OpenCRQ, and drive the whole loop with XTM One.
If OpenCTI helps your security program, give it a star: it is how the project grows.
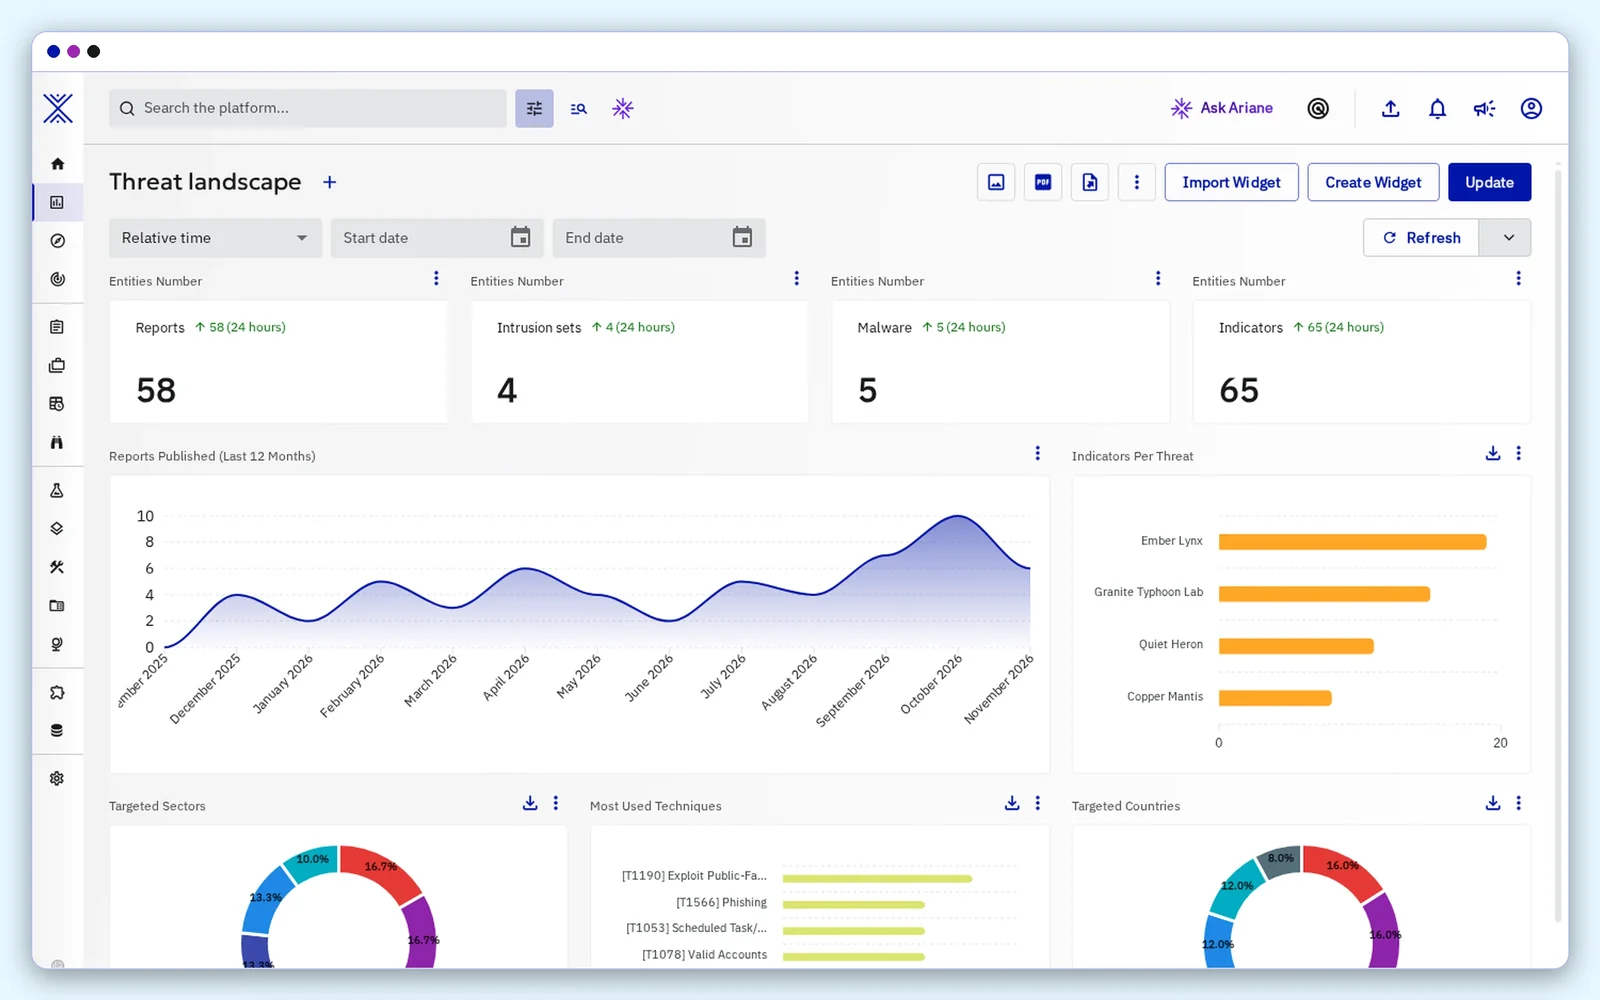
Table of contents
- Why OpenCTI
- Capabilities
- Gallery
- How it works
- Part of the XTM Platform
- Use cases by security role
- Quick start
- Editions
- Integrations and ecosystem
- Community
- Contributing
- Security
- License
- About Filigran
Why OpenCTI
Exposure management starts with the threat. Before you can decide which exposure to fix first, you need to know which adversaries matter to your sector and region, which techniques they use and which vulnerabilities they exploit in the wild.
- Structured, not scattered. Every report, feed and analyst note lands in one STIX 2.1 knowledge graph, each fact linked to its source, its confidence and its first and last seen dates.
- Actionable for CTEM. Attack patterns, vulnerabilities and indicators carry straight into validation (OpenAEV), risk quantification (OpenCRQ), detection and the agents of XTM One.
- Open by design. An Apache 2.0 core, a GraphQL API, a Python client and a large catalog of connectors to the tools you already run.
Capabilities
| CTEM stage | What OpenCTI gives your team |
|---|---|
| Scoping | Priority intelligence requirements, sectors, regions and the threats that target them, scored and surfaced so the program starts from the adversaries that matter. |
| Discovery | Threat actors, campaigns, malware, tools, techniques, vulnerabilities and indicators in one STIX 2.1 graph, fed by TAXII, RSS, CSV, JSON and hundreds of connectors. |
| Prioritization | Vulnerabilities ranked by the adversaries that exploit them, inference rules that derive targeting and attribution, decay rules that age indicators out. |
| Validation | The ATT&CK matrix of any threat and its security coverage, with the OpenAEV counterpart of every shared object and its simulation results written back. |
| Mobilization | Cases, playbooks, dashboards, STIX, CSV and PDF exports, live streams and TAXII collections that put the knowledge into the hands of every team. |