
 #1
Tools für Angreifersimulation, Red-Team-Infrastruktur, C2-Frameworks und operative Sicherheit.
Kitploit empfohlen

 mrwadams/attackgen
AttackGen ist ein Cybersicherheits-Tool für Incident-Response-Tests, das die Leistungsfähigkeit großer Sprachmodelle und des umfassenden MITRE…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 vulnsvnc/cve-2026-125399
Write-up und Proof-of-Concept für CVE-2026-125399, eine zero-click-OS-Command-Injection ohne Authentifizierung in Fluxion über eval() auf eine vom…
 absllk/hexestra
KI-native Penetrationstest-IDE, in der Operatoren und ein KI-Agent Browser, Terminals, Traffic-Capture, Shells, Asset-Graph, Aufgaben und Beweise in…
 nccgroup/steppingstones
Webbasiertes Red-Team-Tool für Aktivitätsprotokollierung, Berichterstattung und Lagebewusstsein mit Cobalt Strike- und BloodHound-Integration.
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 martian56/redcell
KI-Red-Team-Plattform. Autonome LLM-Agenten führen einen Penetrationstest Ende-zu-Ende in einem Kali-Container durch und verfassen den Bericht.…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 tenderacer-lgtm/cve-2026-14900-poc
CVE-2026-14900: Nicht authentifizierte RCE in Cost Calculator Builder Pro (<= 4.0.3) über XOR-Gadget
 esrrhs/pingtunnel
Pingtunnel ist ein Tool, das TCP/UDP-Verkehr über ICMP sendet
 xalgorix/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…
 lolbas-project/lolbas
Von der Landschaft lebende Binärdateien und Skripte - (LOLBins und LOLScripts)
 pennyw0rth/netexec
Post-Exploitation-Framework für automatisierte Netzwerk-Authentifizierungstests, Credential-Harvesting und laterale Bewegung in Windows/AD-Umgebungen…
 benthecyberone/copperhound
Rust attack-path analysis for AD, ADCS and Entra ID
 firefart/stunner
Testen und Ausnutzen von STUN/TURN-Servern auf Fehlkonfigurationen, die das Pivoting im internen Netzwerk über SOCKS-Proxy, Memory-Leak-Angriffe und…
 ghostvectoracademy/dllhijackhunter
Automatisierte Entdeckung, Validierung und Bestätigung von DLL-Hijacking. Lokale Fehlkonfigurationen in bewaffnete, bestätigte Angriffspfade…
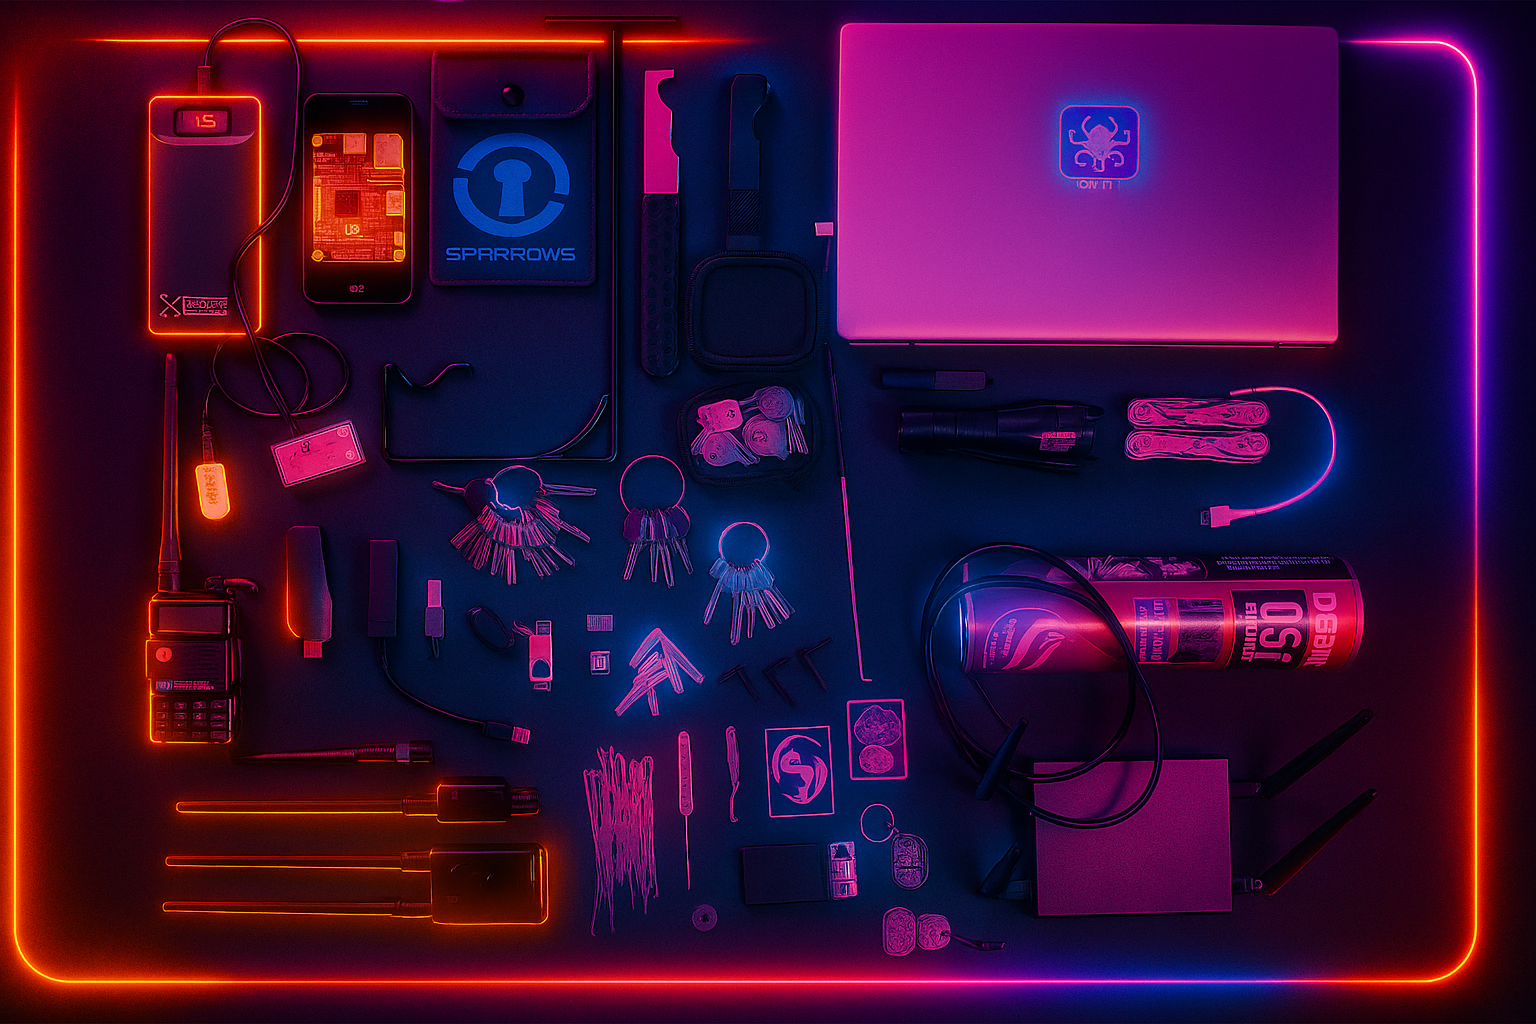 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.







