
 #1
Tools zum Scannen, Sichern und Härten von Docker, Kubernetes und containerisierten Umgebungen.
Kitploit empfohlen
 sdodson/cve-2026-46595-proof
Go-Proof-of-Concept zur Demonstration von CVE-2026-46595 in golang.org/x/crypto/ssh, unter Verwendung von Symbolinspektion gestrippter Binärdateien…
 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 pwnvader/cve-2026-88877-poc-pwnvader
Proof-of-Concept und reproduzierbares Lab für CVE-2026-88877, eine Authentifizierungsumgehung in Traefik ingress-nginx über from-to-www-redirect, mit…
 mondoohq/cnspec
Eine quelloffene, cloud-native Sicherheitslösung zum Schutz von allem vom Build bis zur Laufzeit
 joaovicdev/exploit-cve-2026-33634
Bewusst verwundbares Docker-Lab zur Reproduktion von CVE-2026-33634: LiteLLM-Gateway-SSRF über api_base plus eine trojanisierte Abhängigkeit, mit…
 joaovicdev/exploit-cve-2026-87902
Vulnerables Lab (Docker) + Python-PoC für CVE-2026-87902 — nicht authentifizierter Path Traversal im WordPress Core (page-template -> LFI -> bedingte…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 owasp/owasp-ctf-in-a-box
Selbst gehostetes OWASP-CTF-Kit: eine Box, eine kostenlose GitHub-Organisation, keine Cloud-Abhängigkeiten
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker-Image, das einen Proof-of-Concept-Exploit für CVE-2022-0847 (Dirty Pipe) paketiert, eine Privilegieneskalations-Schwachstelle im Linux-Kernel.
 abhaybansal16/cve-2025-55182-lab
Docker-basiertes Lab zur Reproduktion von CVE-2025-55182 (React2Shell), einer nicht authentifizierten RCE im React Server Components Flight Protocol,…
 amulyakaushik/cve-2023-27163-lab
Docker-basiertes Lab zur Reproduktion von CVE-2023-27163 SSRF in Request-Baskets, mit Exploit-Verifikation, Erkennungsskript und…
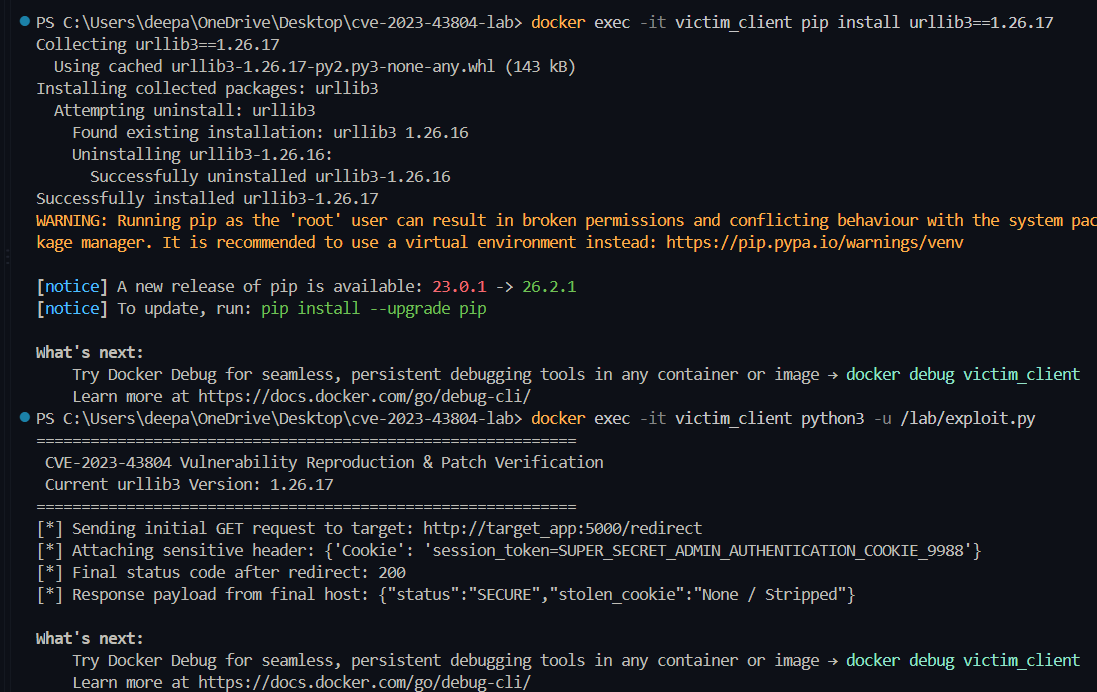 deepanshu-khurana/cve-2023-43804
Containerisiertes dreistufiges Lab, das CVE-2023-43804 urllib3-Cookie-Leak über Cross-Origin-Redirects reproduziert, mit Exploit-Skript und…
 shambhavim18/cve-2019-15107-lab
Docker-basiertes Lab zur Demonstration von CVE-2019-15107, der nicht authentifizierten RCE in Webmin, inklusive Deployment, Ausnutzung, Erkennung und…
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana Unauthenticated Path Traversal - Security Lab | Shivam Gupta | 23104003
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.








