


مساعد أمني مدعوم بالذكاء الاصطناعي يكتشف الثغرات أثناء كتابتك للكود. فحص أمني في الوقت الفعلي، وشروحات تعليمية، وإصلاحات تلقائية للمطورين.


حارسك الأمني المدعوم بالذكاء الاصطناعي — متصل الآن بذكاء المهاجمين المباشر
الميزات • البنية المعمارية • تكامل Raven • التثبيت • خارطة الطريق • المساهمة
يكتشف CodeGuard Copilot الثغرات الأمنية أثناء كتابتك للكود، وليس بعد إجراء الـ commit. فهو يجمع بين الكشف الحتمي عبر أنماط regex والتحليل العميق المدعوم بالذكاء الاصطناعي وذكاء المهاجمين المباشر من نظام Raven/WraithWall البيئي ليمنحك سياقاً لا تستطيع أي إضافة أمنية أخرى لـ VS Code تقديمه.
ما الذي يميزه:
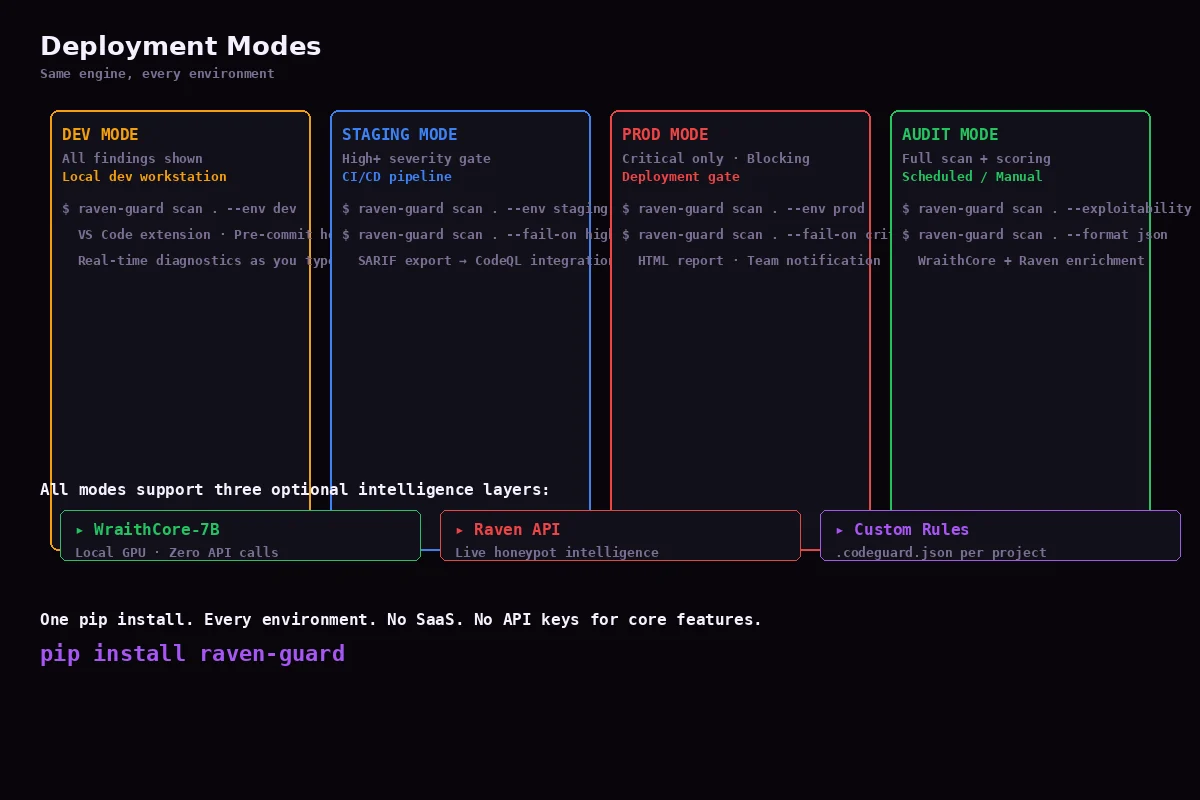
.codeguard.json — regex، الخطورة، CWE، لكل ملف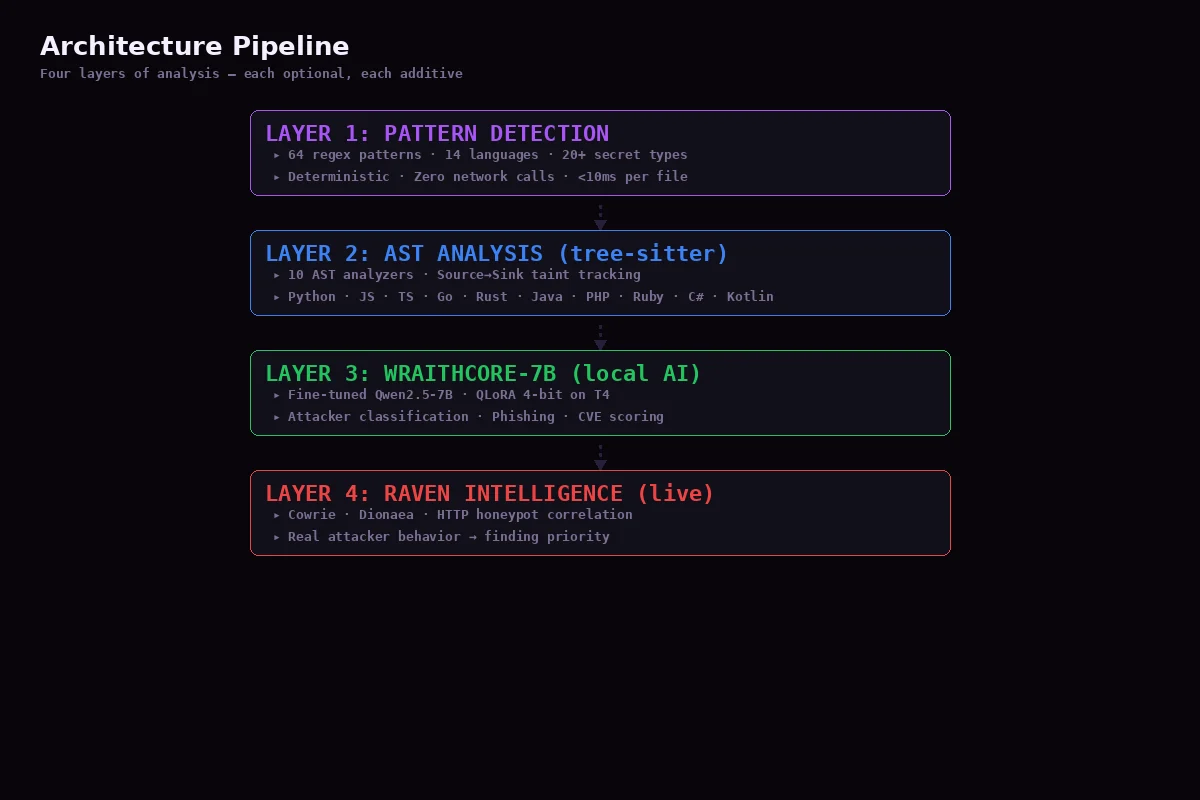
 │ │ │ │
│ │ ┌─────────────┐ ┌────────────────┐ │ │
│ │ │ Knowledge │ │ Raven Bridge │ │ │
│ │ │ Graph │ │ ← attacker data │ │ │
│ │ │ finding→CWE │ │ → threat intel │ │ │
│ │ │ →MITRE→fix │ │ │ │ │
│ │ └─────────────┘ └────────────────┘ │ │
│ └──────────────────┬───────────────────┘ │
│ │ │
│ ▼ │
│ ┌──────────────────────────────────────┐ │
│ │ Developer Feedback │ │
│ │ QuickFix · Explain · Suppress · Fix │ │
│ │ Training · Report · CI/CD │ │
│ └──────────────────────────────────────┘ │
│ │
└──────────────────────────────────────────────┘
│
▼
┌──────────────────────────────────────────────┐
│ WraithWall / Raven │
│ │
│ Cowrie Honeypot → Attacker Telemetry │
│ Campaign Correlation → Behavioral DNA │
│ CISA KEV → OWASP → Composite Scoring │
│ Cross-Repo Systemic Patterns │
│ Dark-Web Breach Monitoring │
└──────────────────────────────────────────────┘
---

## جسر ذكاء Raven

CodeGuard Copilot هو **مستهلك الذكاء الأمامي** لخط أنابيب القياسات الحيوية للمهاجمين في Raven. عندما ترصد honeypots Cowrie مهاجمين حقيقيين يستخدمون تقنيات استغلال، تتدفق الأنماط إلى CodeGuard:
Attacker uses SQL injection on honeypot ↓ Raven detects: CWE-89, credential_access, threat_score=85 ↓ RavenIntelBridge.ingestEvent() receives event ↓ Generates candidate CodeGuard pattern at confidence 0.85 ↓ Proposed pattern: "SQL Injection (attacker-observed)" ↓ Human review → published as CodeGuard rule ↓ Developers protected against the actual exploit
وبالعكس، عندما يكتشف CodeGuard ثغرة، فإنه يولّد تغذية راجعة منظمة لـ Raven:
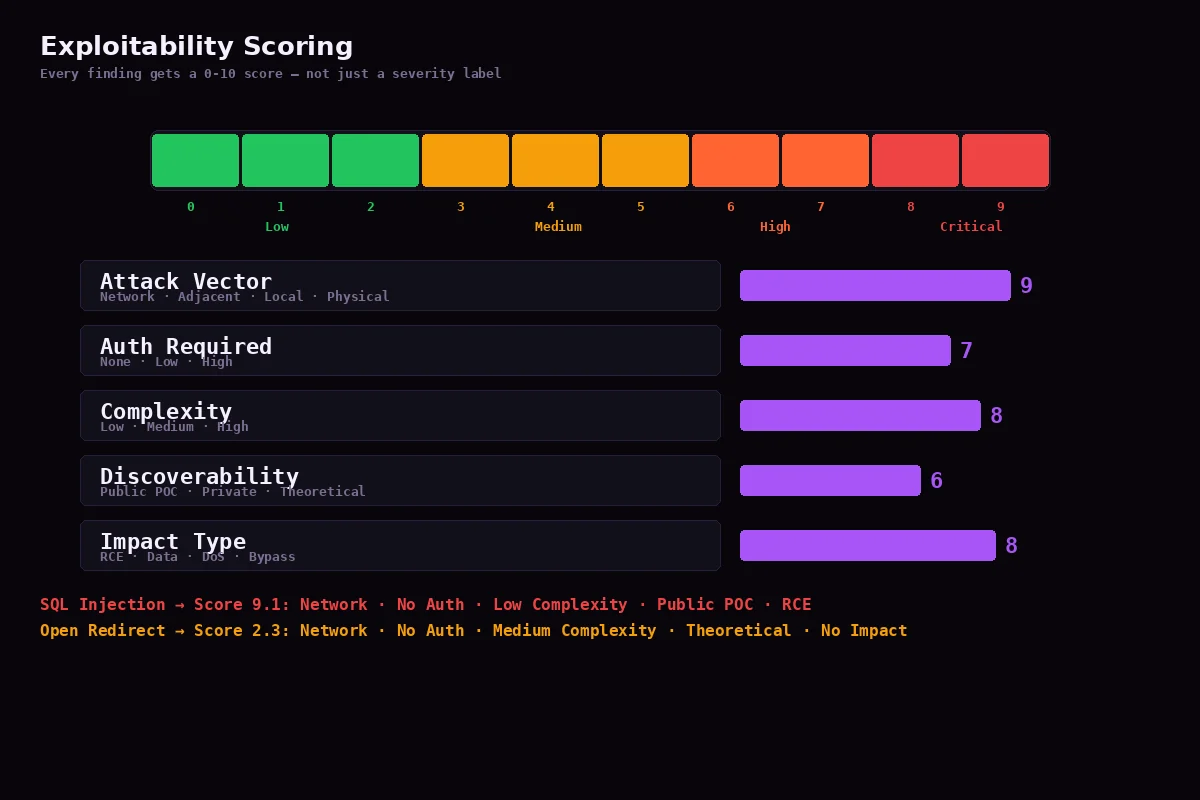
CodeGuard finding: CWE-798 hardcoded secret in auth/login.js ↓ RavenThreatFeedback.generateIntelligence() ↓ MITRE techniques: T1552, T1078 ↓ Raven priority score: 72 (network attack vector, low complexity) ↓ Raven elevates this finding in composite scoring ↓ SOC team sees: "Attacker-aligned credential finding in production repo"
---

## فئات الثغرات المكتشفة

### حرجة
SQL Injection (CWE-89)، Command Injection (CWE-78)، NoSQL Injection (CWE-943)، Hardcoded Secrets (CWE-798)، Insecure Deserialization (CWE-502)

### عالية
XSS (CWE-79)، DOM-based XSS، Path Traversal (CWE-22)، File Upload (CWE-434)، Weak Crypto (CWE-327)، Unsafe Blocks (Rust)، Unescaped HTML (Go)

### متوسطة
CORS Misconfiguration (CWE-942)، Open Redirect (CWE-601)، Insecure Random (CWE-338)، ReDoS (CWE-1333)، Memory Leak (C++)، Mass Assignment (Ruby)

### منخفضة
Weak Password Storage، Express Trust Proxy، Missing Security Headers، أنماط frameworks المضادة

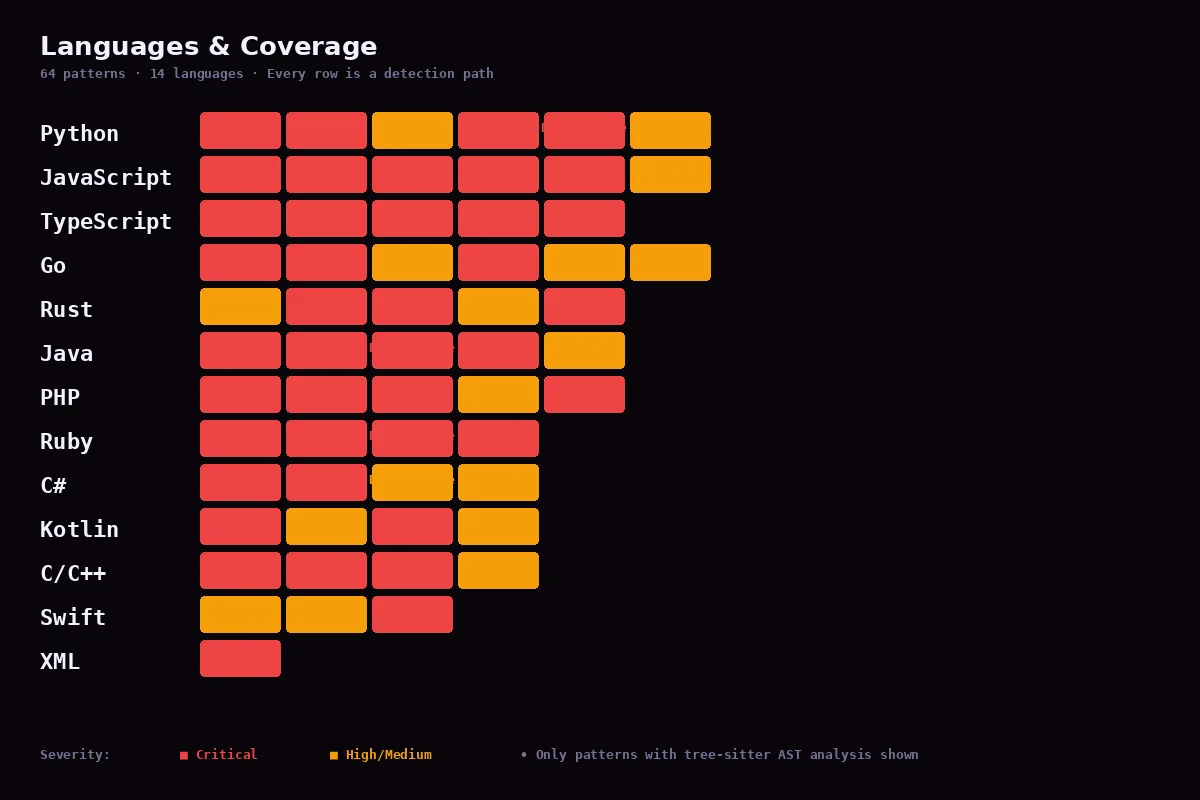
### خاصة باللغات (18 جديدة)
Go: SQLi، Insecure Random، Hardcoded Secret، Unescaped HTML
Rust: Unsafe Block، Hardcoded Secret، Command Injection، Weak Crypto
C++: Buffer Overflow، Memory Leak، SQL Injection
C#: SQL Injection، Connection String، Insecure Deserialization
Ruby: SQL Injection، Command Injection، Mass Assignment، Unsafe YAML

---

## نموذج الأمان المضبوط بدقة (v0.3.1)

النموذج المضبوط بدقة في CodeGuard (`Niffy90/codeguard-security-7b`) هو محول LoRA على **Qwen2.5-7B-Instruct** مدرّب على 32 نمطاً من ثغرات الأمان عبر 8 فئات:
