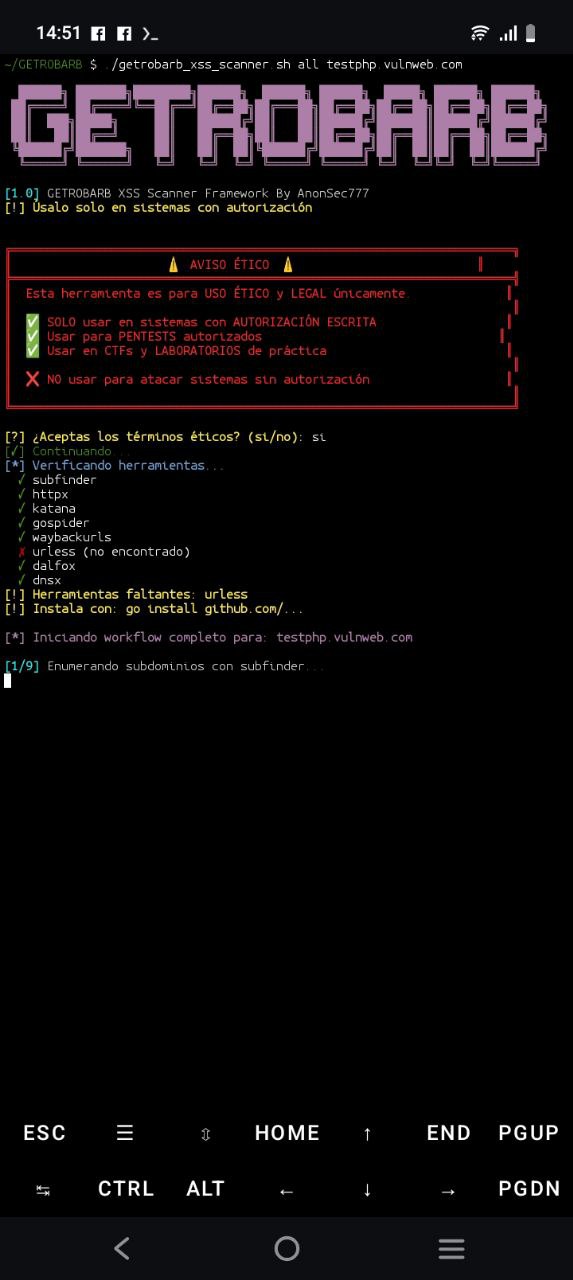
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline for web security auditing and bug bounty hunting.
Automated reconnaissance and XSS vulnerability detection framework written in Bash, designed for authorized web security audits.
Developed by AnonSec777 for the Hacking Team.
GETROBARB XSS Scanner integrates utilities from the bug bounty and pentesting ecosystem to automate the entire discovery flow of endpoints vulnerable to Cross-Site Scripting, from a single interface.
Aimed at: pentesters, security researchers and bug bounty hunters.
All through a structured 9-stage pipeline + payload generation.
| Tool | Function |
|---|---|
subfinder | Subdomain enumeration |
httpx (PD) | Active host verification |
katana | Web application crawling |
gospider | Advanced URL collection |
waybackurls | Historical URLs from Wayback Machine |
urless | Parameter cleaning/normalization (sed fallback) |
paramspider | Hidden parameter discovery (optional) |
arjun | Parameter fuzzing (optional) |
dalfox | Advanced XSS scanner |
dnsx | DNS resolution |
All within the same script getrobarb_xss_scanner.sh (no duplicated code):
do_payloads generates payloads_xss.txt with 68 XSS vectors
(<script>, event handlers onerror/onload, SVG, javascript: URI, polyglots, template injection
{{1*1}}/${1*1}, data-URI/base64 and HTML/hex/null-byte encoded variants to evade WAF).
dalfox uses --payload-file payloads_xss.txt --amount 5.dalfox with --delay 100ms, --timeout 10s and a real Chrome
User-Agent header (--header).do_params integrates paramspider and arjun if they are installed.go/bin PATH to use the ProjectDiscovery httpx
(avoids the Python client at /usr/bin/httpx, which does not accept -list/-silent/-mc).httpx now accepts 500/404/503 (previously only 200/301/302/403).scan_output/ and findings in findings/.gen_report.sh generates a nice report signed by Hacking Team.0) install (or automatically prompted when starting all) that downloads and installs missing tools on its own (go install / git clone / pip) without the user doing anything manually. If the network blocks any of them, it reports it and uses a fallback.GETROBARB/
├── getrobarb_xss_scanner.sh # script principal
├── gen_report.sh # genera reporte PDF del escaneo
├── README.md
├── scan_output/ # ── resultados de recon/escaneo (superficie) ──
│ ├── subs.txt # subdominios
│ ├── alive.txt # hosts vivos
│ ├── katana.txt # URLs de crawling
│ ├── gospider.txt # URLs adicionales
│ ├── wayback.txt # URLs históricas
│ ├── all_urls.txt # todas las URLs
│ ├── params.txt # URLs con parámetros
│ ├── clean_params.txt # parámetros normalizados
│ └── payloads_xss.txt # wordlist de payloads XSS (68 vectores)
└── findings/ # ── hallazgos de vulnerabilidades ──
└── xss_findings.txt # posibles XSS detectados por dalfox
The full scan runs in 9 stages + payload generation:
| # | Stage | Tool | Output |
|---|---|---|---|
| 1️⃣ | Subdomain enumeration | subfinder | scan_output/subs.txt |
| 2️⃣ | Live host verification | httpx | scan_output/alive.txt |
| 3️⃣ | Application crawling | katana | scan_output/katana.txt |
| 4️⃣ | Additional spidering | gospider | scan_output/gospider.txt |
| 5️⃣ | Historical URLs (Wayback) | waybackurls | scan_output/wayback.txt |
| 6️⃣ | URL merging | sort -u | scan_output/all_urls.txt |
| 7️⃣ | Parameter extraction | grep '=' + paramspider/arjun | scan_output/params.txt |
| 8️⃣ | Parameter cleaning | urless (fallback sed) | scan_output/clean_params.txt |
| 9️⃣ | XSS scan | dalfox (68 payloads) | findings/xss_findings.txt |
# Workflow completo (recon + XSS)
bash getrobarb_xss_scanner.sh all ejemplo.com

# Solo un módulo
bash getrobarb_xss_scanner.sh subfinder ejemplo.com

# Generar solo la wordlist de payloads
bash getrobarb_xss_scanner.sh payloads

# Escanear XSS desde una lista de parámetros
bash getrobarb_xss_scanner.sh dalfox scan_output/clean_params.txt

# Generar reporte PDF del último escaneo
REP_TARGET=ejemplo.com bash gen_report.sh
The user does not need to install anything manually. When running the scan, if tools are missing, the script asks and downloads them automatically:
# El script pregunta "¿instalar herramientas faltantes?" → responde si
bash getrobarb_xss_scanner.sh all ejemplo.com

# O instala todo explícitamente antes:
bash getrobarb_xss_scanner.sh install
The install_tools function tries go install (via GOPROXY), then git clone and
pip as a fallback. If the network blocks any tool (e.g., github filtered),
it reports it and the script continues using internal fallbacks when possible.
scan_output/ and findings/The tool includes a prior ethical check. Use it only on:
| Red | Enlace |
|---|---|
| Telegram | https://t.me/HackingTeamGrupoOfficial |
| X | @HackingTeam77 |
| Bluesky | https://bsky.app/profile/hackingteam.bsky.social |
| Discord | https://discord.gg/V4nPFbQX |
| YouTube | https://www.youtube.com/@HackingTeamOfficial |
| TikTok | https://www.tiktok.com/@hacking.kdea |
#hackingteam #cibersecurity #infosec #pentesting #bugbounty #xss #exploit #web #kalilinux #redteam #osint #cve #github #sqlmap #waybackurls #burpsuite #linux #windows #phishing #malware #sandbox #apt #zeroday #ssrf #sqli #cors #python #ai #ia