
tirreno v0.10.1
إطار عمل أمني مفتوح المصدر لتتبع الأحداث في الوقت الفعلي، وكشف التهديدات، وتسجيل المخاطر. يراقب سلوك المستخدم، ويكشف الاحتيال، وهجمات البوتات، والاستيلاء على الحسابات عبر محرك قواعد وسجلات التدقيق.
tirreno
tirreno is a security framework.
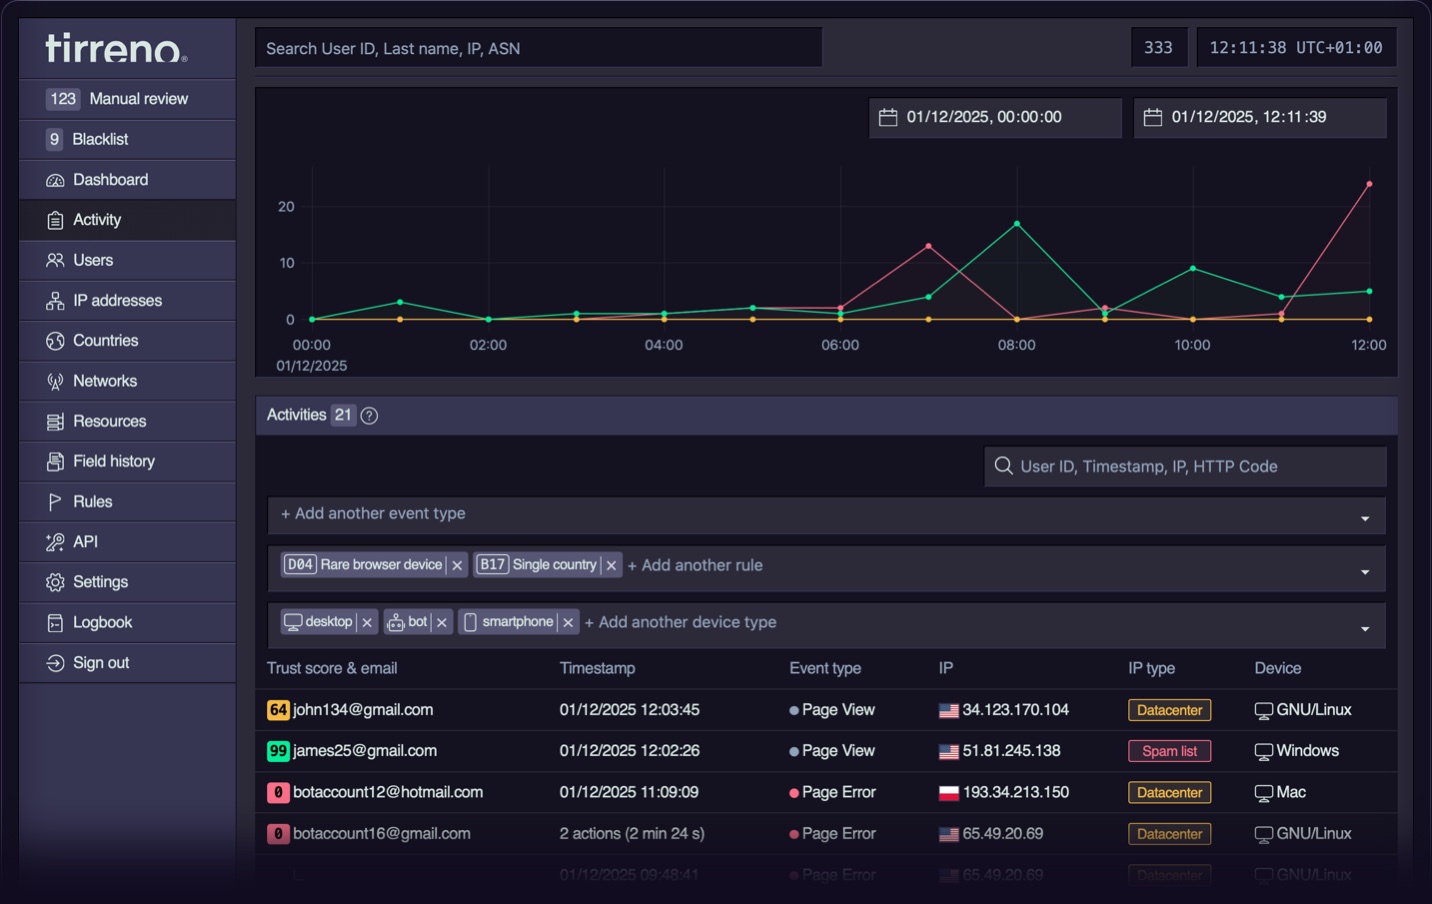
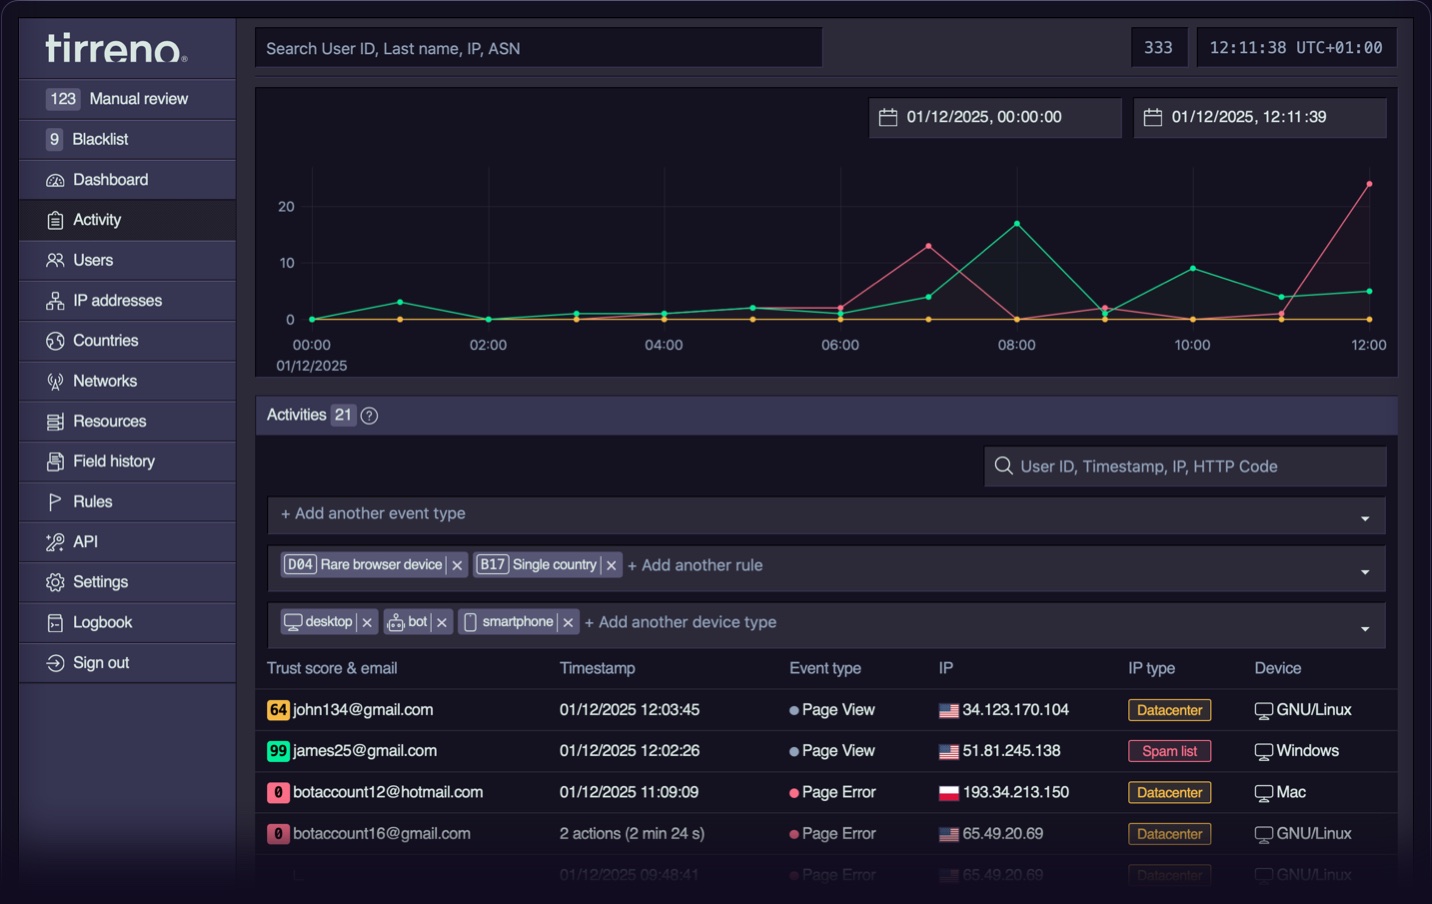
tirreno [tir.ˈrɛ.no] helps understand, monitor, and protect your product from threats, and abuse. While classic cybersecurity focuses on infrastructure and network perimeter, most breaches occur through compromised accounts and application logic abuse that bypasses firewalls, SIEM, WAFs, and other defenses. tirreno detects threats where they actually happen: inside your product.
tirreno is a hand-written, few-dependency, "low-tech" PHP/PostgreSQL application. After a straightforward five-minute installation, you can ingest events through API calls and immediately access a dashboard.
Core components
- SDKs & API Integrate tirreno into any product with SDKs. Send events with full context in a few lines of code.
- Built-in dashboard Monitor and understand your product's security and risk events from a single interface.
- Single user view Analyze behaviour patterns, risk scores, and activity timelines for a specific entity.
- Rule engine Calculate risk scores automatically with preset rules or create your own customized for your product.
- Review queue Automatically suspend entities with risky events or flag them for manual review through threshold settings.
- Field audit trail Track modifications to important fields, including what changed and when to streamline audit and compliance.
Built for
- Self-hosted, internal and legacy apps: Embed security layer to extend your security through audit trails, protect user accounts from takeover, detect cyber threats and monitor insider threats.
- Mission critical applications: Sensitive application protection, even in air-gapped deployments.
- Industrial control systems (ICS) and command & control (C2): Protect, operational technology, command systems, and critical infrastructure platforms from unauthorized access and malicious commands.
- SaaS: Prevent cross-tenant data leakage, privilege escalation, data exfiltration and business logic abuse.
- Non-human identities (NHIs): Monitor service accounts, API keys, bot behaviors, and detect compromised machine identities.
- API-first applications: Protect against abuse, rate limiting bypasses, scraping, and unauthorized access.
Live demo
Check out the live demo at play.tirreno.com (admin/tirreno).
Requirements
- PHP: Version 8.0 to 8.3
- PostgreSQL: Version 12 or greater
- PHP extensions:
PDO_PGSQL,cURL - HTTP web server:
Apachewithmod_rewriteandmod_headersenabled - Operating system: A Unix-like system is recommended
- Minimum hardware requirements:
- PostgreSQL: 512 MB RAM (4 GB recommended)
- Application: 128 MB RAM (1 GB recommended)
- Storage: Approximately 3 GB PostgreSQL storage per 1 million events
Docker-based installation
To run tirreno within a Docker container you may use command below:
curl -sL tirreno.com/t.yml | docker compose -f - up -d
Continue with step 4 of Quickstart.
Quickstart install
- Download the latest version of tirreno (ZIP file).
- Extract the tirreno-master.zip file to the location where you want it installed on your web server.
- Navigate to
http://localhost:8585/install/index.phpin a browser to launch the installation process. - After the successful installation, delete the
install/directory and its contents. - Navigate to
http://localhost:8585/signup/in a browser to create an administrator account. - For cron job setup, insert the following schedule (every 10 minutes) expression with the
crontab -ecommand or by editing the/var/spool/cron/your-web-serverfile:
*/10 * * * * /usr/bin/php /absolute/path/to/tirreno/index.php /cron
Via Composer and Packagist (optional)
tirreno is published at Packagist and could be installed with Composer:
composer create-project tirreno/tirreno
or could be pulled into an existing project:
composer require tirreno/tirreno
SDKs
API reference
tirreno('…') is tirreno's built-in API. It gives your own code the same building blocks the console uses: the current request and page, the ingested data, the rule engine, the tirreno('queries') builder, logging, and utilities. Use it to customize tirreno. The examples below show custom sections built with this API.
LLM bots
Risk users
Documentation
See the User guide for details on how to use tirreno, Developers documentation to customize your integration, Admin documentation for installation, maintenance and updates.
About
tirreno is a free, open-source framework for in-application security.
We solve real people's challenges through love in ascétique code and open technologies. tirreno is not VC-motivated. Our inspiration comes from the daily threats posed by organized cybercriminals, driving us to reimagine the place of security in modern organizations.
Why the name tirreno?
Tyrrhenian people may have lived in Tuscany and eastern Switzerland as far back as 800 BC. The term "Tyrrhenian" became more commonly associated with the Etruscans, and it is from them that the Tyrrhenian Sea derives its name, which is still in use today.
According to historical sources, Tyrrhenian people were the first to use trumpets for signaling about coming threats, which was later adopted by Greek and Roman military forces.
While working on the logo, we conducted our own historical study and traced mentions of 'tirreno' back to the 15th-century printed edition of the Vulgate (the Latin Bible). We kept it lowercase to stay true to the original — quite literally, by the book. The tirreno wordmark stands behind the horizon line, as a metaphor of the endless evolutionary cycle of the threat landscape and our commitment to rise over it.