

pmg v0.26.0
PMG يحمي المطورين ووكلاء الذكاء الاصطناعي من الحزم الضارة مفتوحة المصدر باستخدام proxy و sandbox وتغذية معلومات التهديدات من SafeDep.
Package Manager Guard (PMG)
Block malicious packages before they install.


Why PMG?
Developers and AI coding agents install packages every day. Each npm install or pip install executes thousands of lines of code that nobody reviews.
Recent compromises in popular ecosystems:
- Mini Shai-Hulud - 300+ popular packages compromised
- litellm 1.82.8 - a popular AI proxy library compromised to exfiltrate credentials
- telnyx 4.87.2 - a legitimate telecom SDK hijacked on PyPI
- pino-sdk-v2 - a typosquat package disguised as the popular pino logger
PMG is free, open source (Apache 2.0), and requires no account or API key. It intercepts every package install and checks it against SafeDep's free community API for known malware before code executes. For unknown malware, it uses dependency cooldown and opt-in sandbox for proactive security defense.
How PMG Works
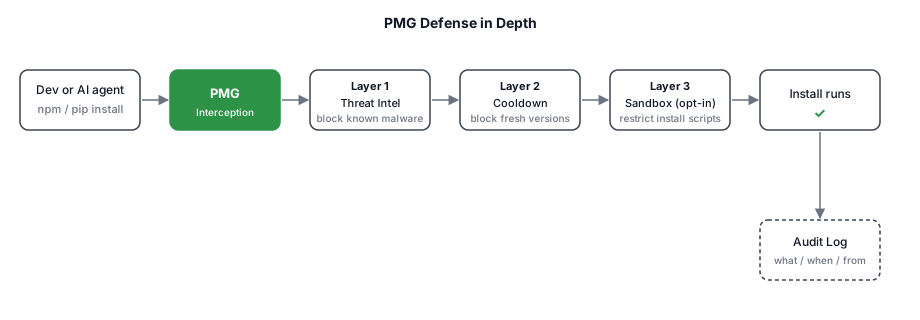
PMG takes a defense in depth approach. Zero config, works across Zsh, Bash, Fish, and PowerShell on Windows. Each intercepted install passes through the protection layers that apply to it before code runs, along with an audit trail.
Layer details
- Transparent Interception - PMG wraps
npm,pip, and other package managers. Developers and AI agents use the same commands. No workflow changes. - Layer 1: Threat Intelligence - PMG checks every package against SafeDep's real-time threat intelligence before install. Known malicious packages are blocked. No key, no login required.
- Layer 2: Policy (Dependency Cooldown) - PMG blocks package versions published inside a configurable cooldown window, so recently compromised versions are skipped during the window.
- Layer 3: Opt-in Sandbox - When sandbox is enabled and configured, PMG runs installs inside OS-native sandboxes (macOS Seatbelt, Linux Landlock by default, or Bubblewrap fallback) so install scripts have restricted system access even if a threat slips past the first two layers.
- Audit Logging - PMG logs every install (what, when, from where) for a verifiable audit trail.
How PMG Compares
PMG combines install-time malware blocking, dependency cooldown, and an OS-native sandbox in one free, open-source tool, for developers and AI coding agents alike.
| Capability | PMG | Socket | safe-chain | Snyk | Dependabot |
|---|---|---|---|---|---|
| OSS / built in public | ✓ | ✗ | ✓ | ✗ | ✗ |
| No account or API key | ✓ | ✓ | ✓ | ✗ | ✗ |
| Install-time malicious package blocking | ✓ | ✓ | ✓ | ✗ | ✗ |
| Dependency cooldown policy | ✓ | ✗ | ✓ | ✗ | ✗ |
| Runtime sandboxing | ✓ | ✗ | ✗ | ✗ | ✗ |
| Protects AI coding agents transparently | ✓ | ✗ | ✗ | ✗ | ✗ |
| Local audit logs | ✓ | ✗ | ✗ | ✗ | ✗ |
| Known-CVE remediation PRs | ✗ | ✗ | ✗ | ✓ | ✓ |
Note: This comparison is accurate as of October 2026.
Quick Start
1. Install
curl -fsSL https://raw.githubusercontent.com/safedep/pmg/main/install.sh | sh
See Installation for Homebrew, npm, and other install methods.
2. Setup
Wire PMG into your shell so it intercepts package managers.
pmg setup install
# Restart your terminal to apply changes
Tip: Re-run
pmg setup installafter upgrading PMG to pick up new configuration options.All-users / golden images:
sudo pmg setup install --systemon Linux, orpmg setup install --systemas administrator on Windows — see docs/system-install.md.
Validate your installation and verify protection is working:
pmg setup doctor
Optional: PMG inspects HTTPS traffic with an on-the-fly CA that it injects into package managers per run. To persist a single CA across runs and trust it in your OS trust store (needed for tools that ignore CA environment variables, such as Go on macOS and Windows), install it once:
pmg setup cert install          # user scope, no sudo
pmg setup cert status           # check trust state and expiry
See Certificate Authority for scopes, rotation, and removal.
3. Use
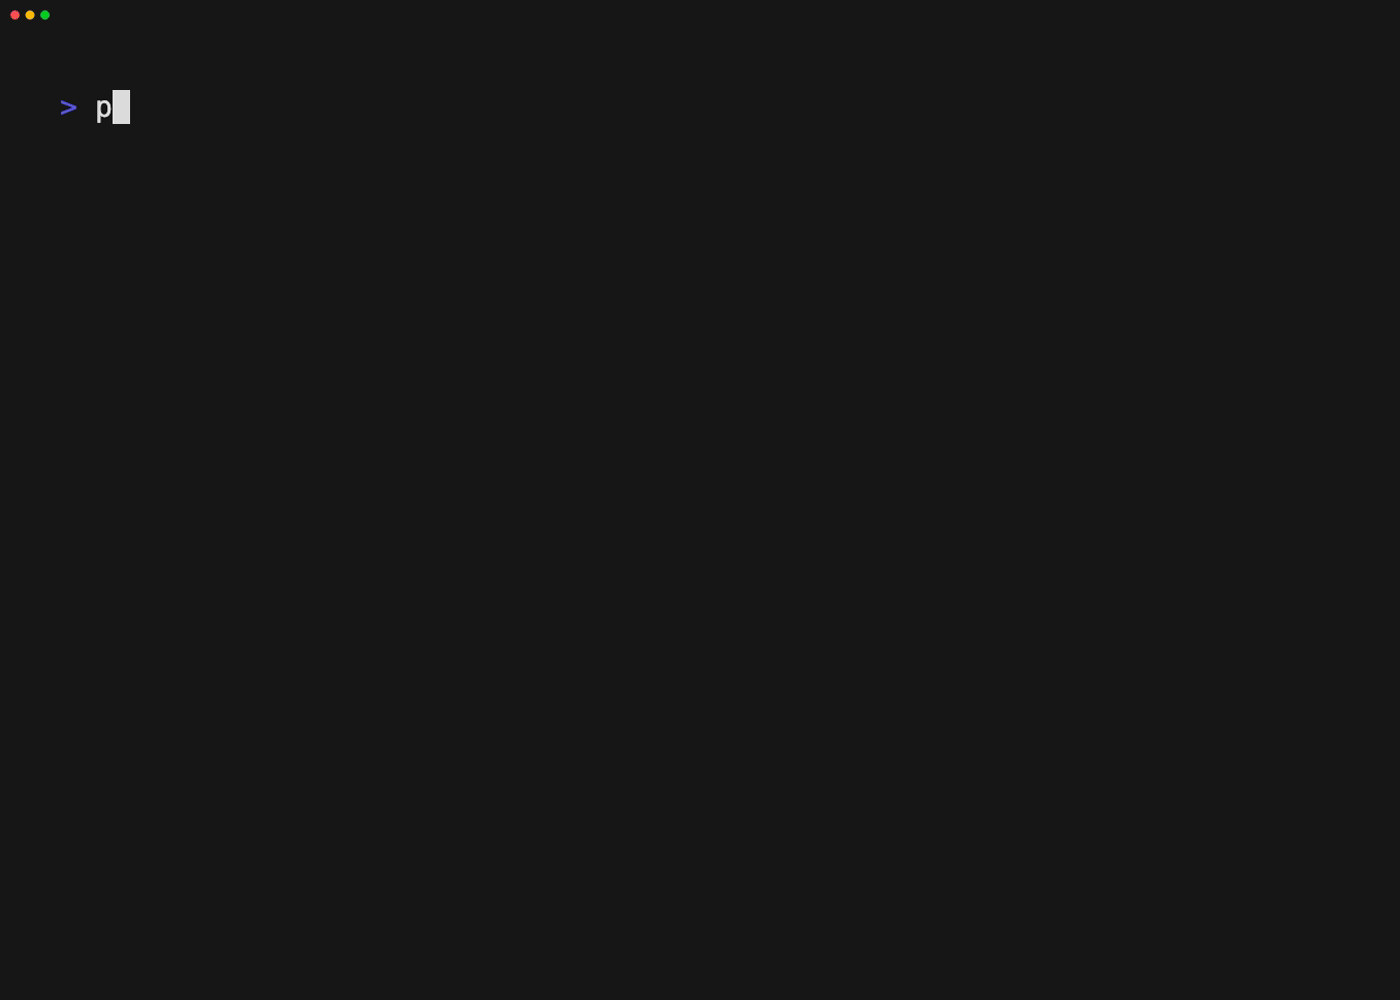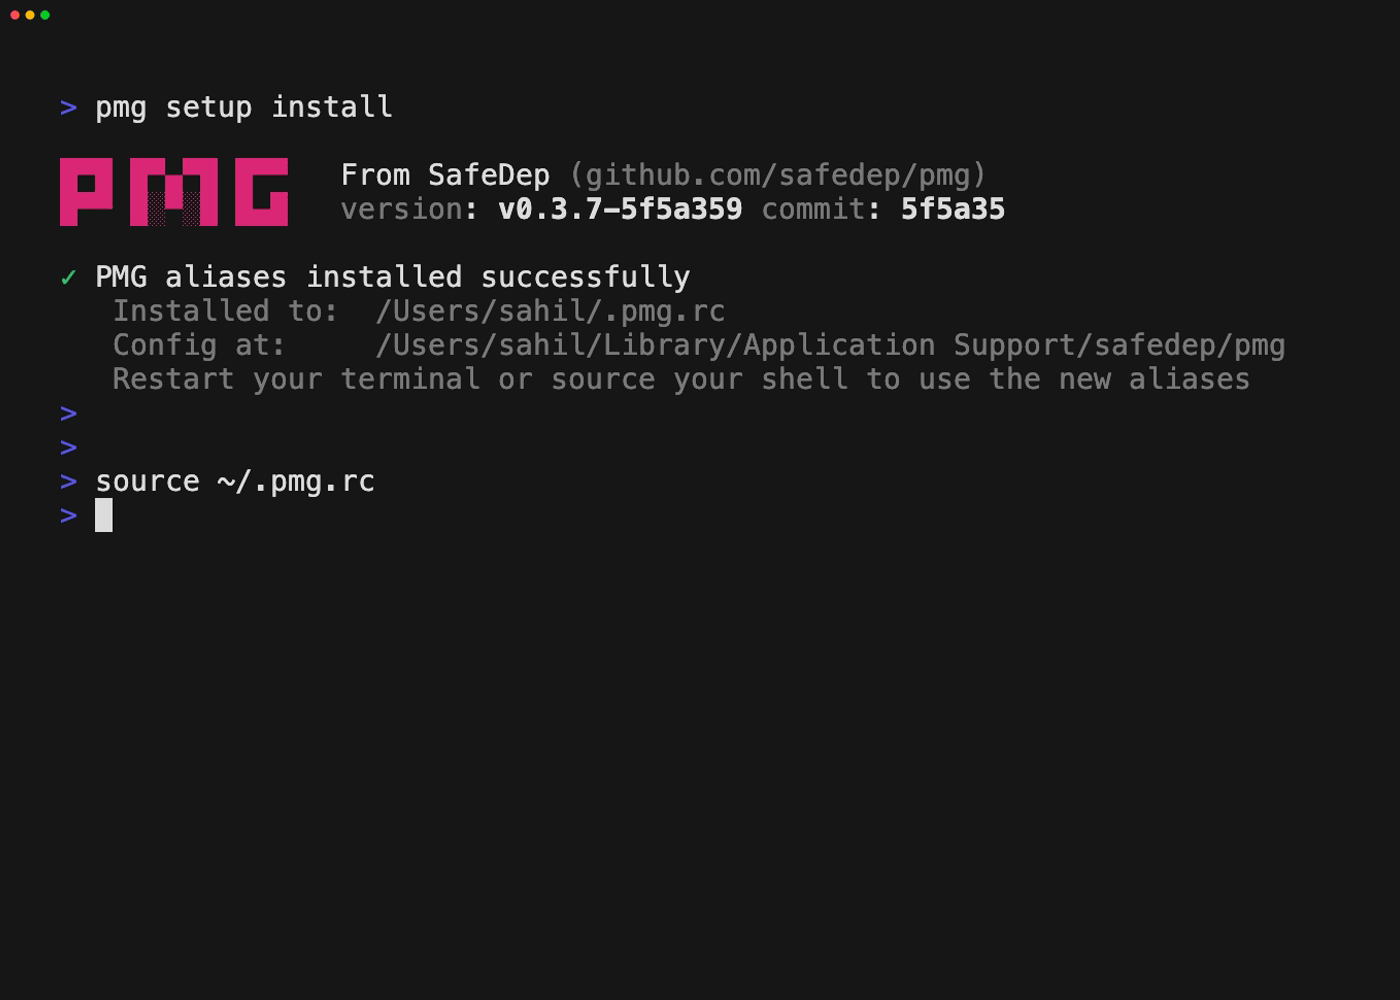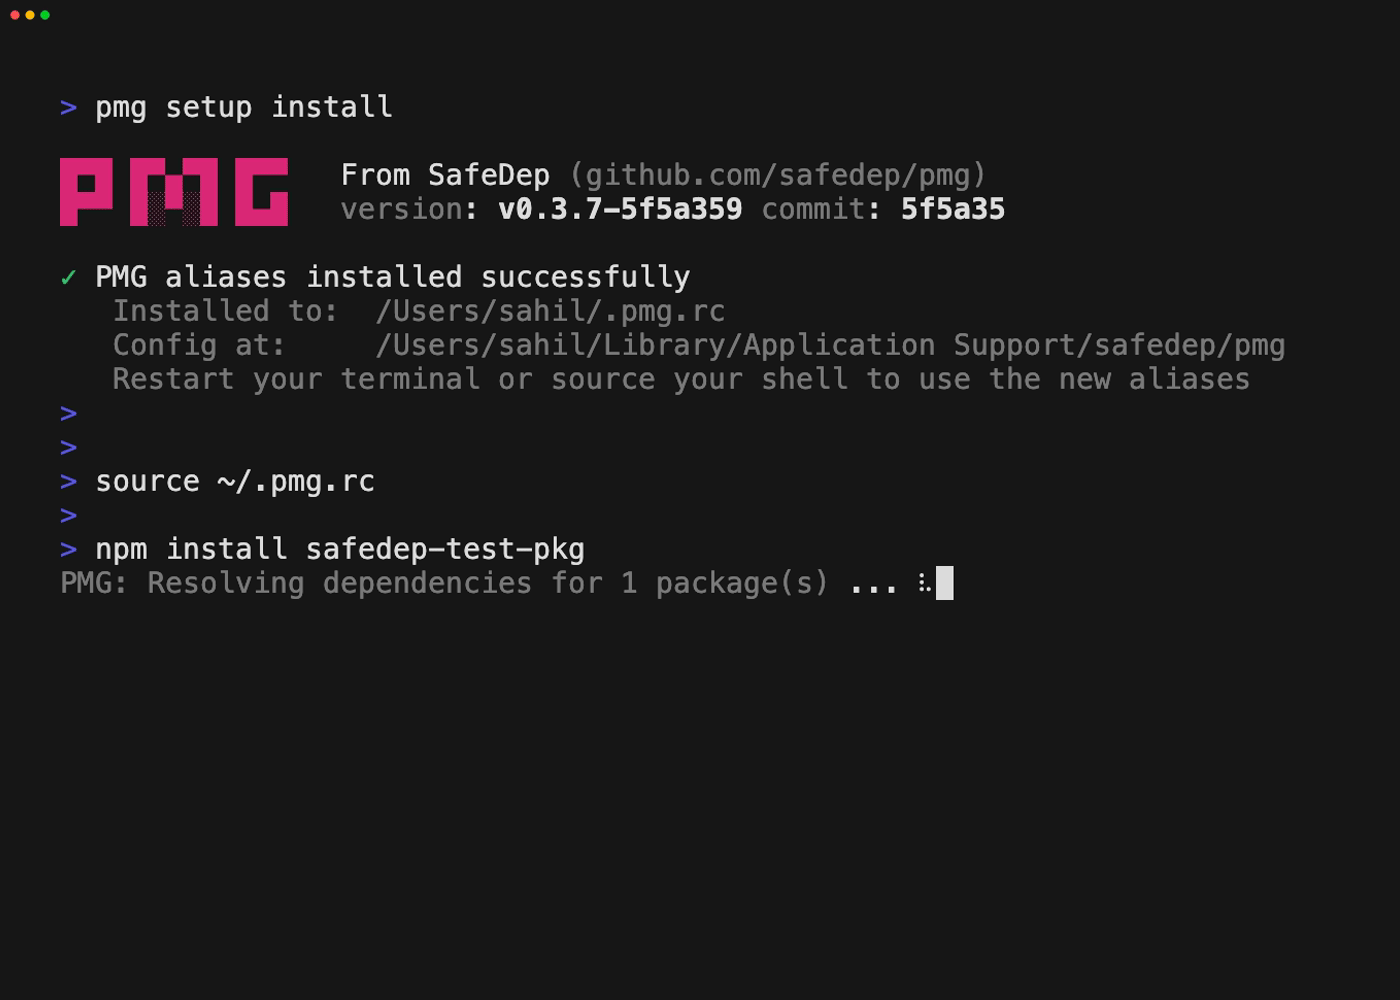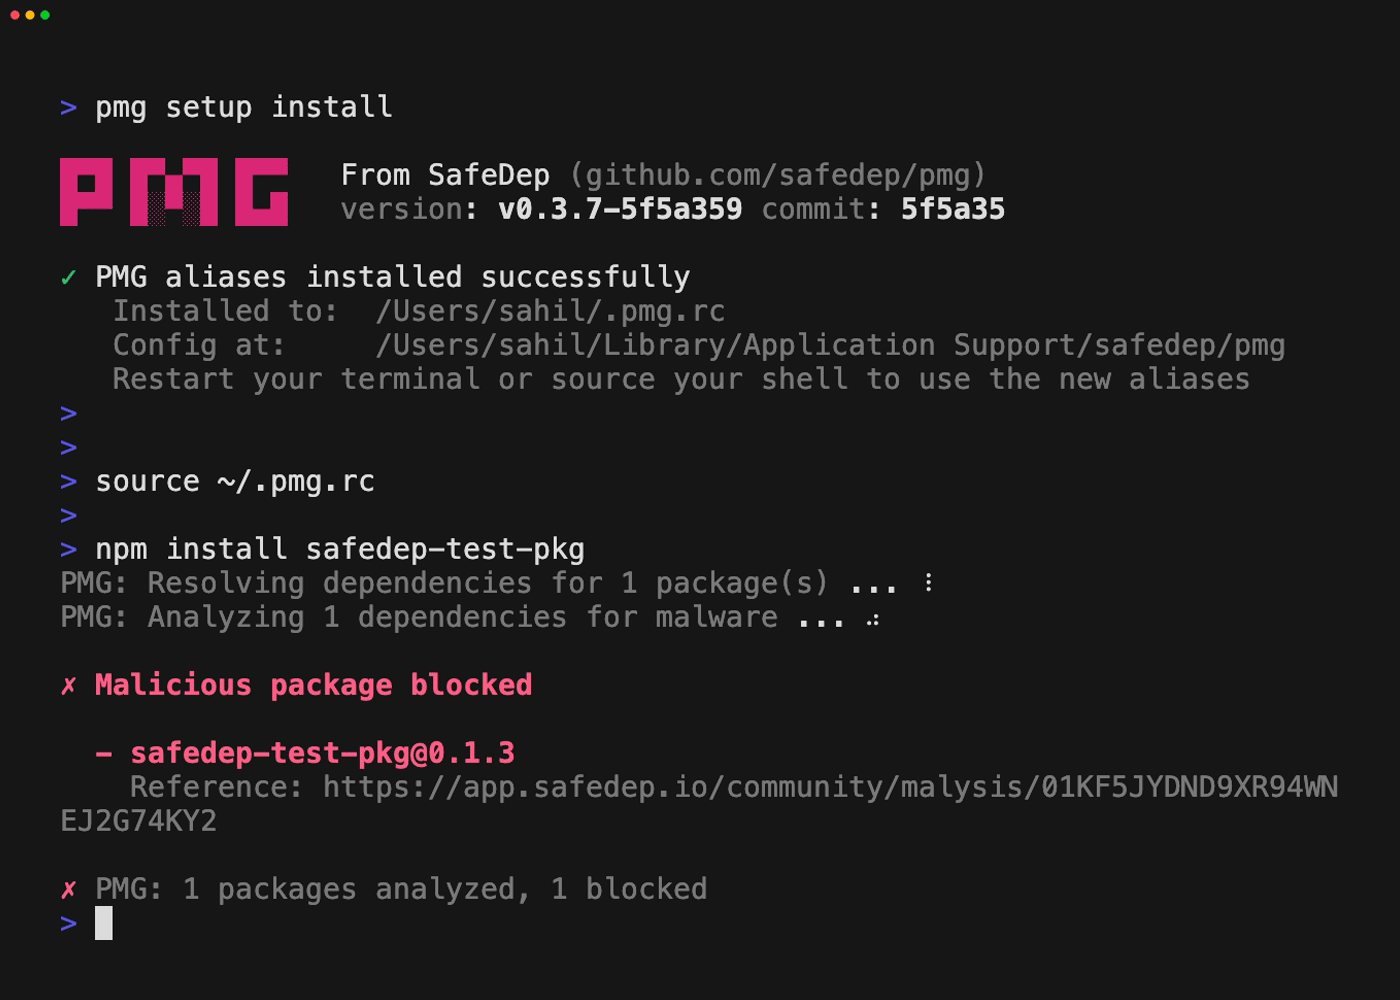
See PMG blocking threats.
npm install --no-cache --prefer-online [email protected]
# or
pip install --no-cache-dir safedep-test-pkg==0.0.4
Note:
safedep-test-pkg(on npm and PyPI) is a benign test package flagged as malicious in SafeDep's database for testing and verification purposes.
Continue using your package managers as usual, or let your AI coding agent run them. PMG sits in the path, blocking malicious packages.
npm install express
# or
pip install requests
Supported Package Managers
PMG supports the tools you already use: