stanfrbd/cyberbro
一个简单的应用程序,可从垃圾输入中提取您的IoC,并使用多种CTI服务检查其信誉。
<h1 align="center">Cyberbro</h1>
<p align="center">
<img src="https://assets.kitploit.com/production/public/readmes/10725/4970c639439a60187e1ba39523b24c3343a5b6946445d8225e23c4060e002ff0.png" width="90" /><br />
<b><i>一个简单的应用程序,可从杂乱输入中提取 IoC,并使用多个服务检查其信誉。</i></b>
<br />
<b>🌐 <a href="https://demo.cyberbro.net/">demo.cyberbro.net</a></b><br />
</p>
---
<p align="center">
<a href="https://github.com/stanfrbd/cyberbro/stargazers">
<img src="https://img.shields.io/github/stars/stanfrbd/cyberbro?style=social" alt="GitHub stars">
</a>
<a href="https://x.com/cyberbro_cti">
<img src="https://img.shields.io/twitter/follow/cyberbro_cti?style=social" alt="Follow on X/Twitter">
</a>
<a href="https://infosec.exchange/@cyberbro">
<img src="https://img.shields.io/badge/Follow_@cyberbro-23-blue?logo=mastodon" alt="Mastodon">
</a>
<a href="https://github.com/stanfrbd/cyberbro/issues">
<img src="https://img.shields.io/github/issues/stanfrbd/cyberbro" alt="GitHub issues">
</a>
<a href="https://github.com/stanfrbd/cyberbro/blob/main/LICENSE">
<img src="https://img.shields.io/github/license/stanfrbd/cyberbro" alt="License">
</a>
<a href="https://github.com/stanfrbd/cyberbro/actions/workflows/jobs.yml">
<img src="https://github.com/stanfrbd/cyberbro/actions/workflows/jobs.yml/badge.svg" alt="build and test badge">
</a>
<a href="https://github.com/stanfrbd/cyberbro/actions/workflows/pre-commit-validation.yml">
<img src="https://github.com/stanfrbd/cyberbro/actions/workflows/pre-commit-validation.yml/badge.svg" alt="pre-commit validation badge">
</a>
<a href="https://www.python.org/">
<img src="https://img.shields.io/badge/Python-3.13-blue?logo=python" alt="Python">
</a>
</p>
---
# 关于
灵感来自 [Cybergordon](https://cybergordon.com/) 和 [IntelOwl](https://github.com/intelowlproject/IntelOwl)。
本项目旨在提供一种简单高效的方式,使用多个服务检查你的可观测对象的信誉,
而无需部署**复杂**的解决方案。请阅读文档 https://docs.cyberbro.net/
> [!TIP]
> 要构建自定义报告,请通过 **MCP**(模型上下文协议)将 Cyberbro 与你最喜欢的 **LLM**(Claude、OpenAI gpt-5...)配合使用 \
> 查看 [Cyberbro MCP](https://github.com/stanfrbd/mcp-cyberbro) 了解更多信息。
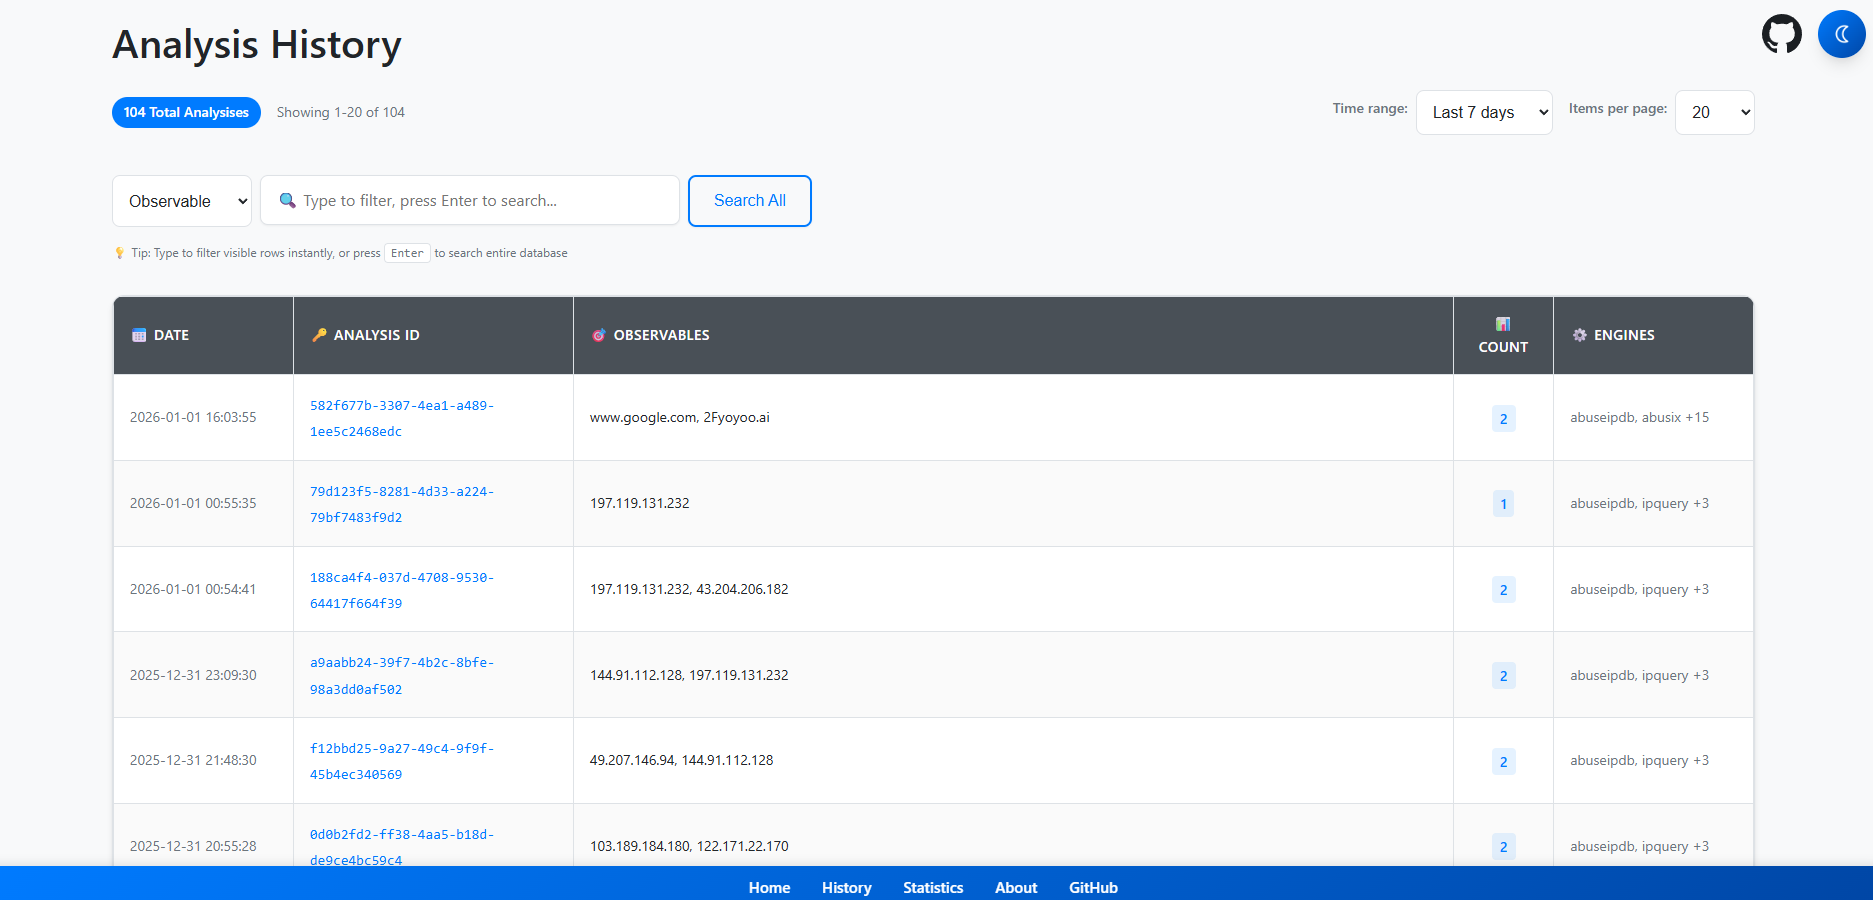
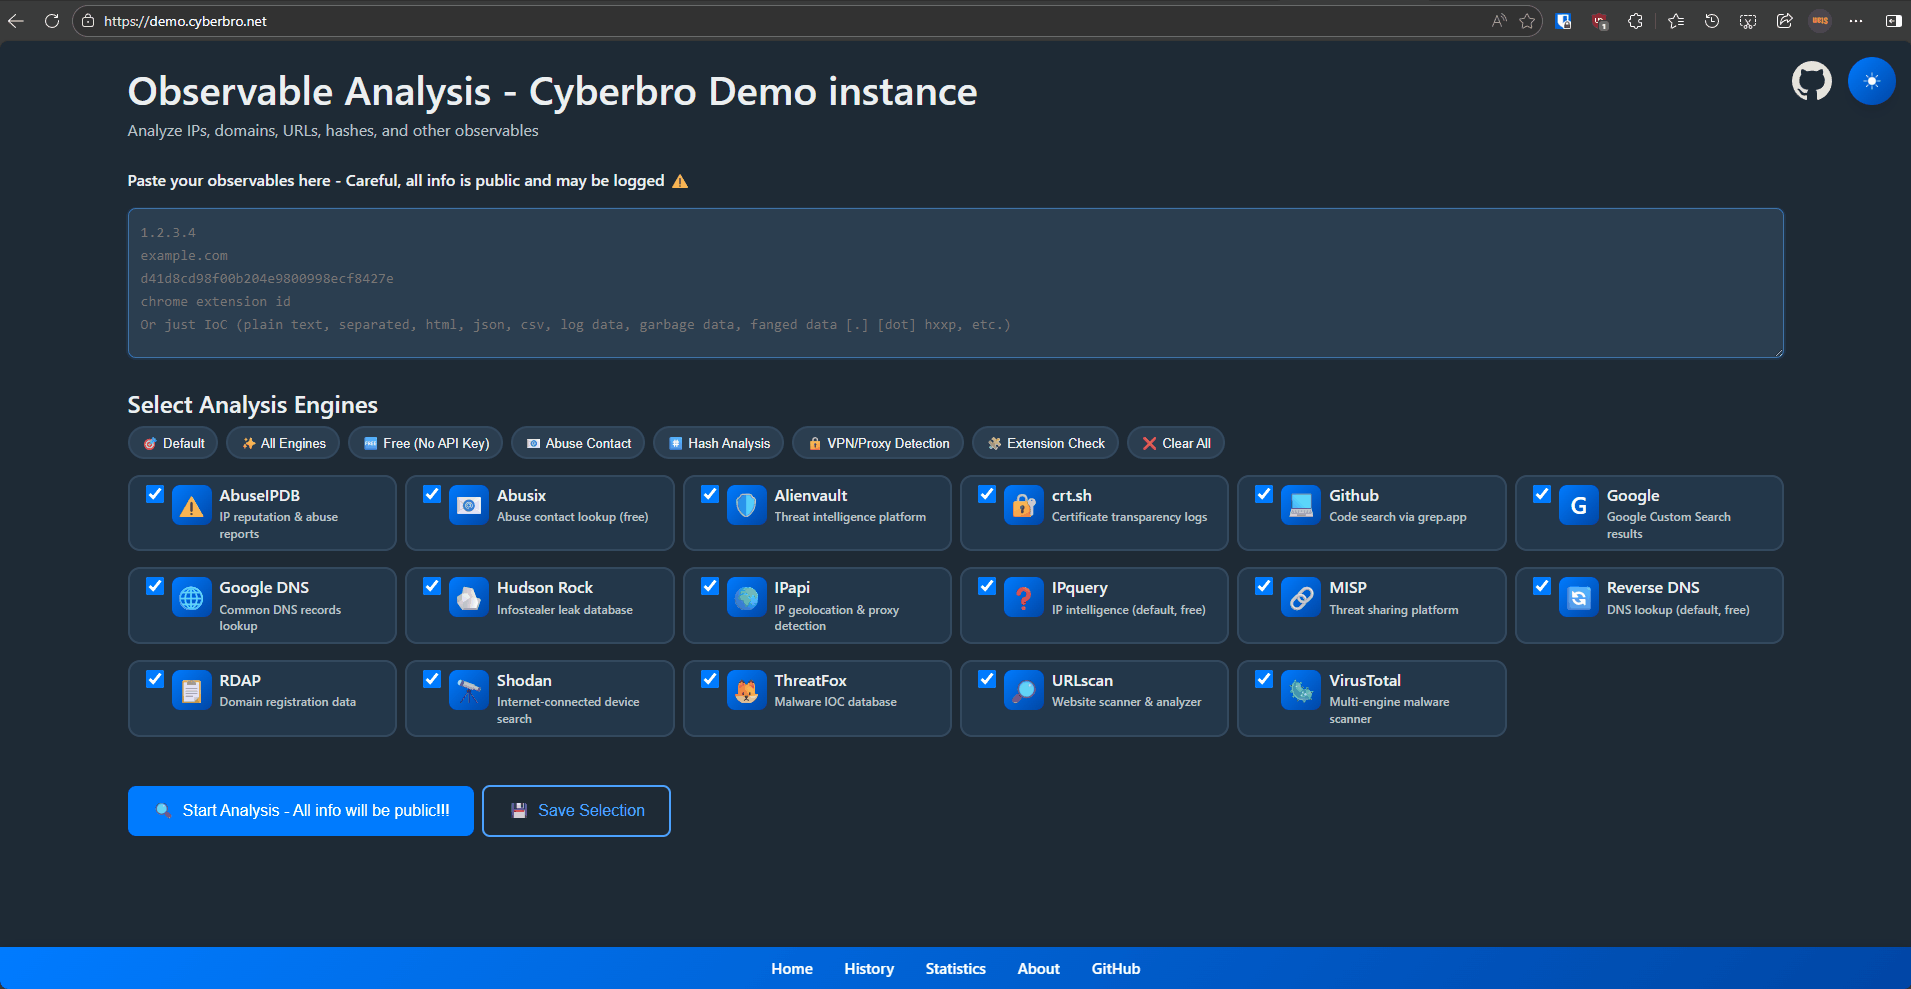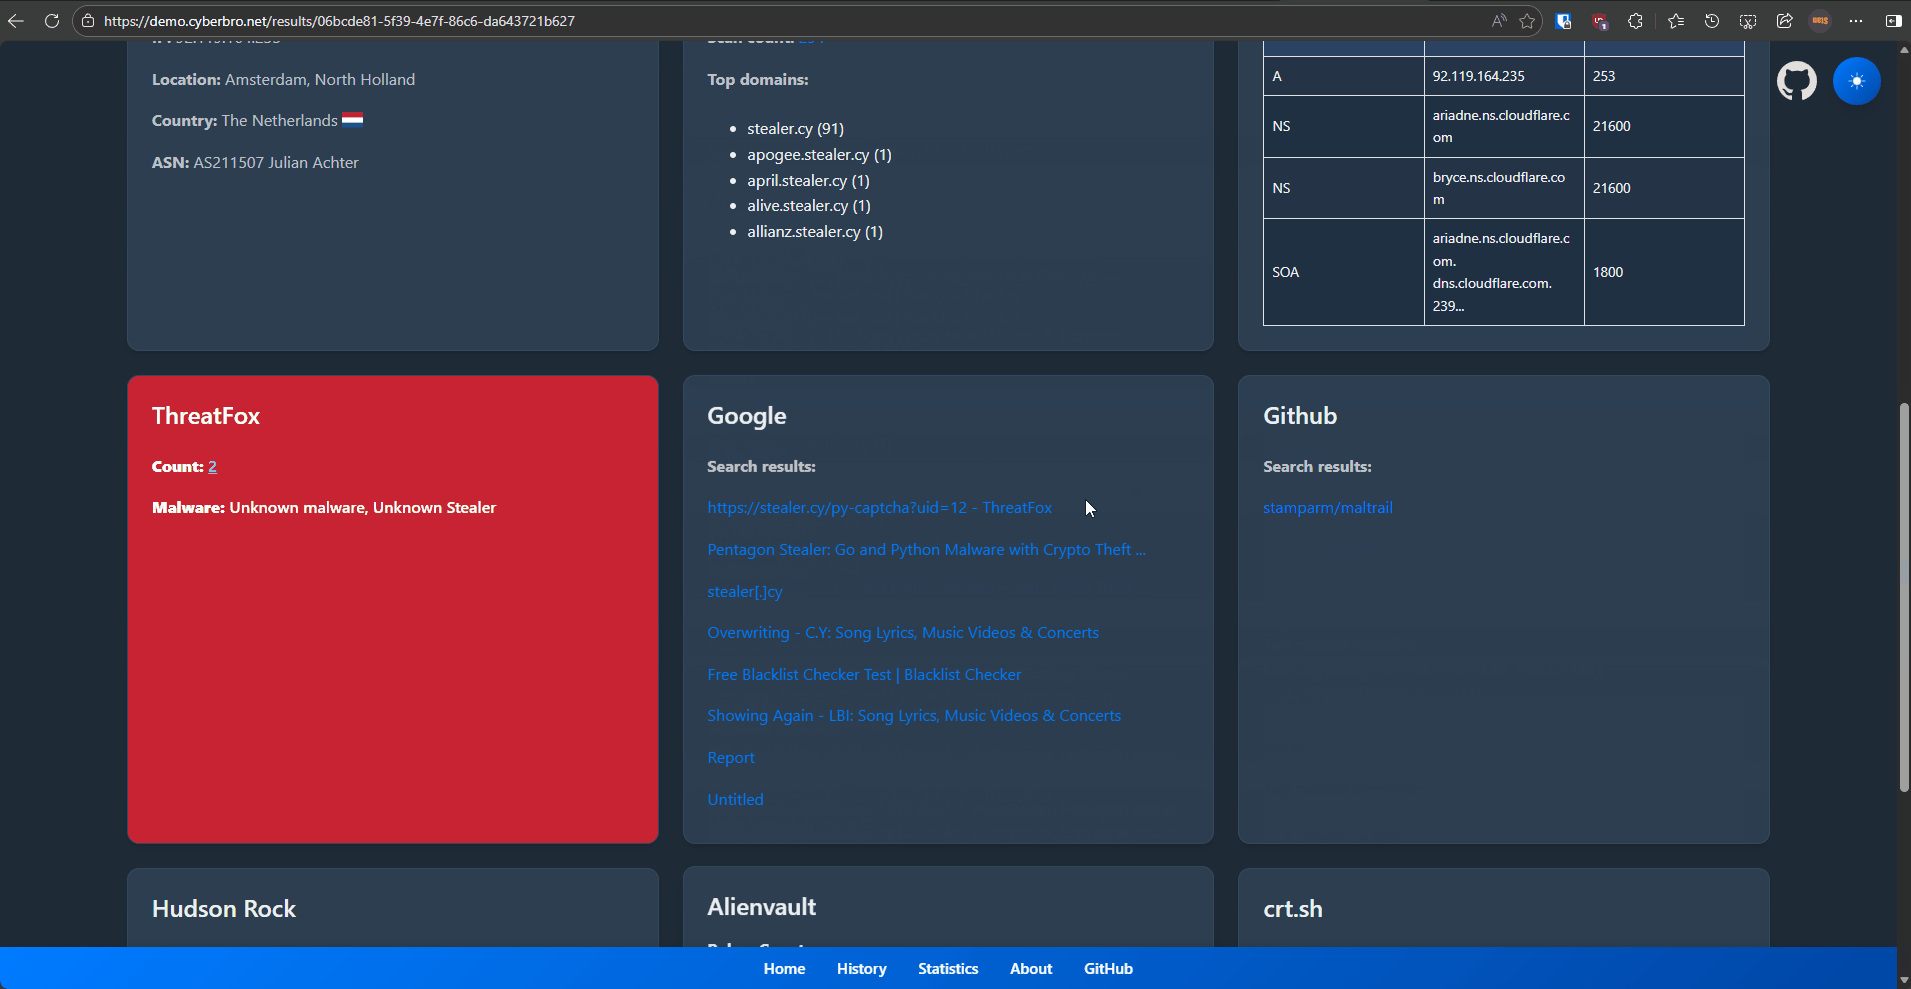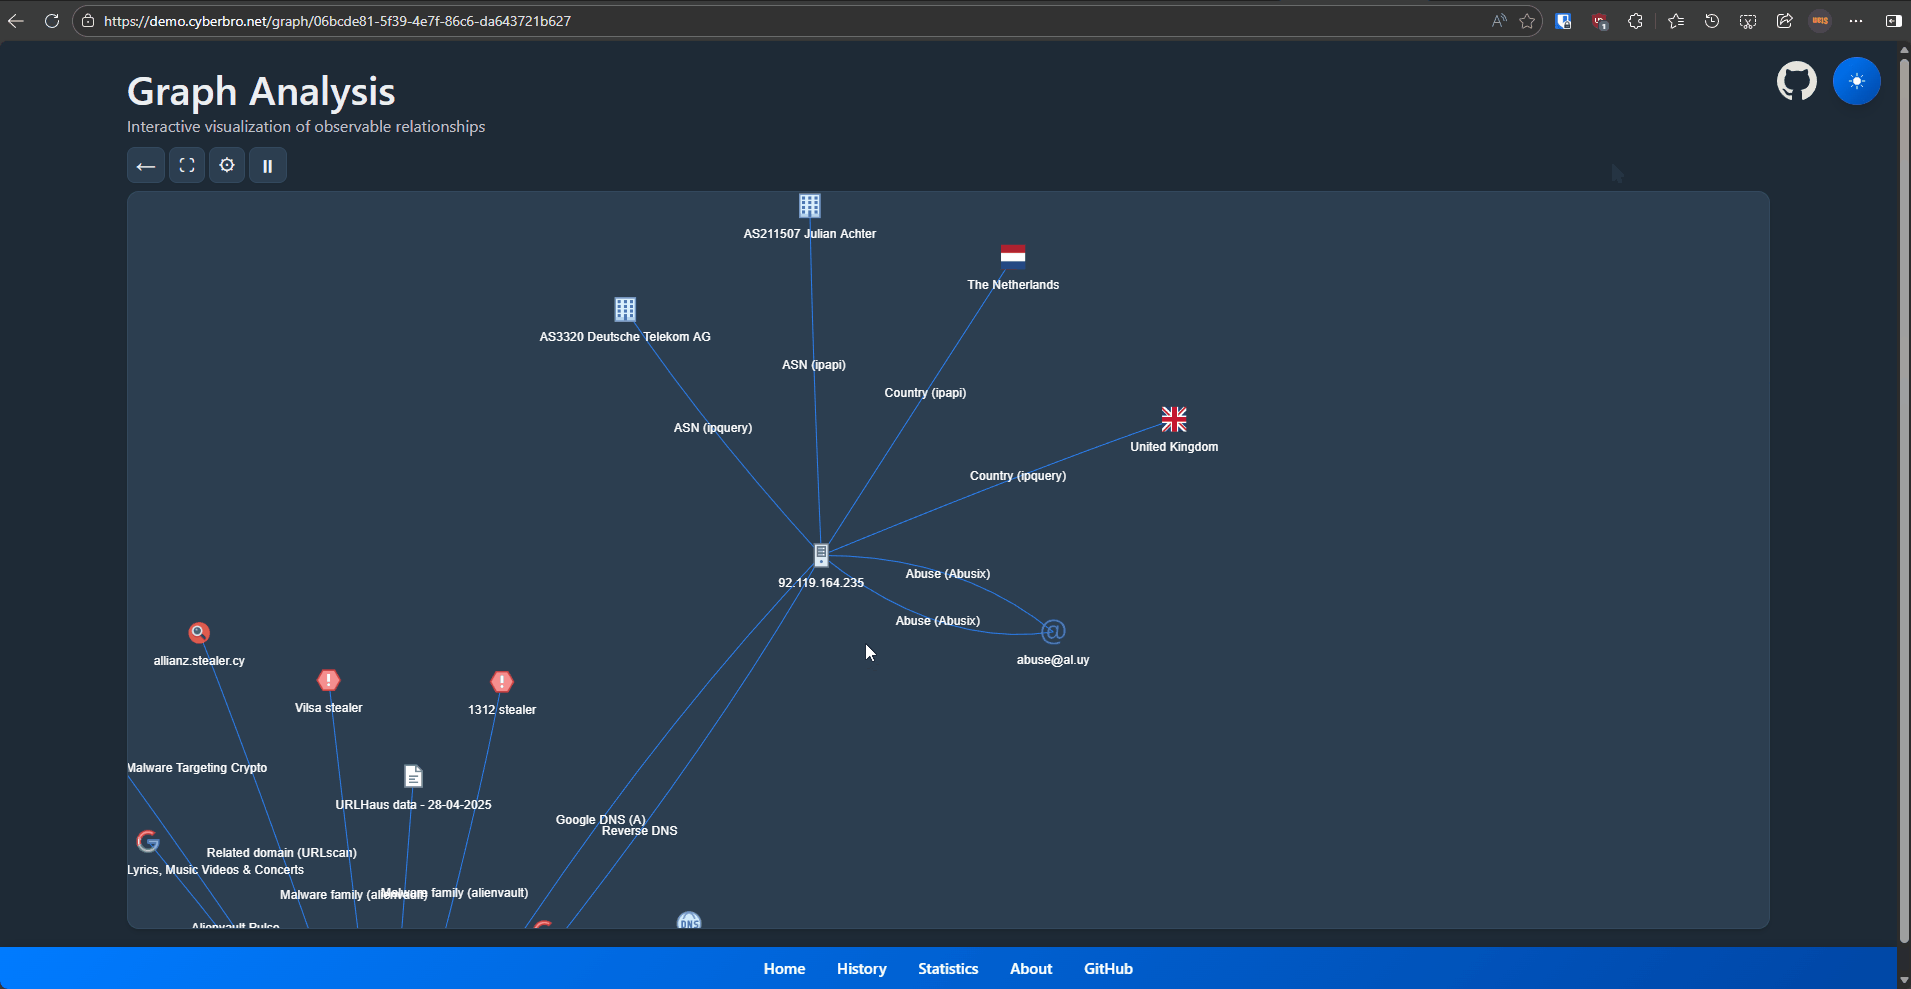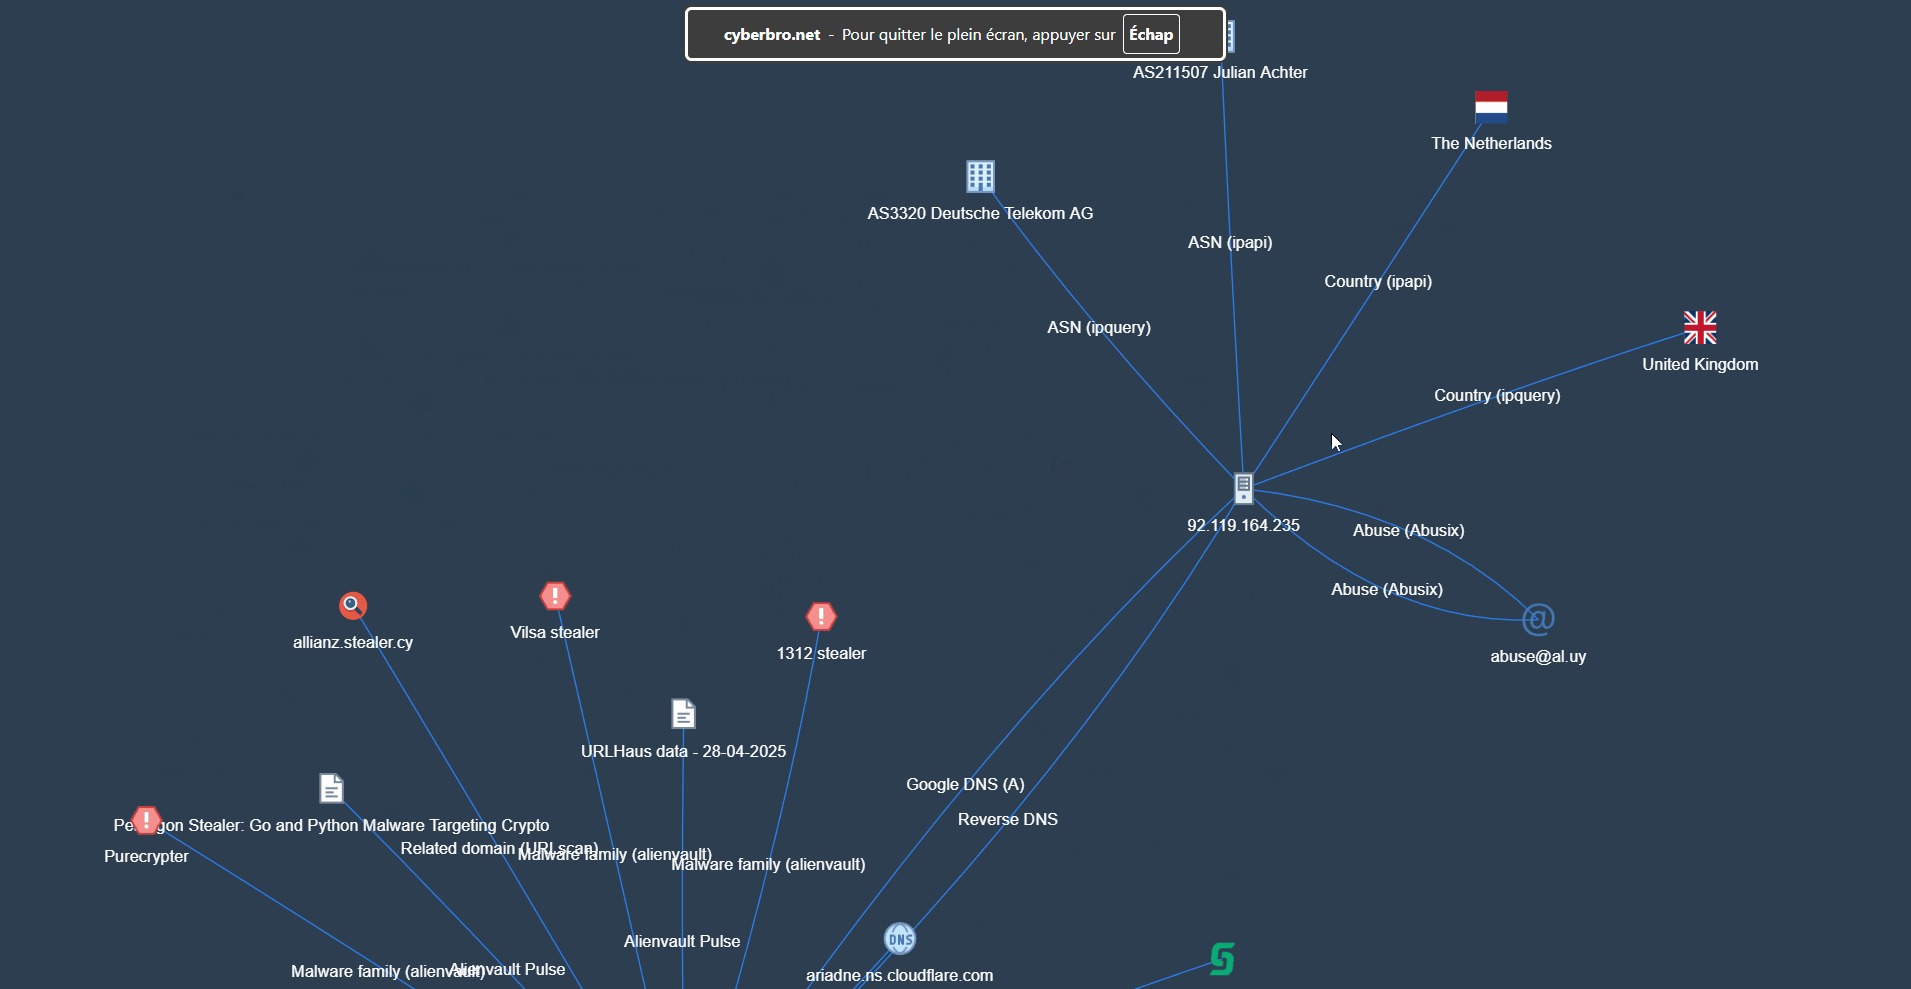
# 演示
# 功能
* **轻松输入**:粘贴原始日志或 IoC——自动解析和提取。
* **多服务检查**:跨众多威胁情报服务对 IP、哈希、域名、URL 和 Chrome 扩展 ID 进行信誉查询。
* **全面报告**:高级搜索、过滤以及导出为 CSV/Excel。
* **快速处理**:多线程以提升速度。
* **自动关联拓展**:通过反向 DNS 和 RDAP / Whois 发现相关域名、URL 和 IP。
* **准确的域名与滥用信息**:RDAP / Whois 和滥用联系人查询。
* **集成**:Microsoft Defender for Endpoint、CrowdStrike、OpenCTI、Grep.App、Hudson Rock 等。
* **代理与存储**:支持代理,结果存储在 SQLite 中。
* **历史与图表**:分析历史和实验性图表视图。
* **缓存**:缓存以加快重复查询(在多引擎级别启用,而非每个引擎)。
# Cyberbro 的独特之处
* **对初学者友好**:适合所有技能水平。
* **Chrome 扩展 ID 查询**:从 ID 获取扩展名称和 CTI 数据。
* **轻量级部署**:设置和使用简单。
* **高级 TLD 提取**:准确的根域名检测,以实现更好的查询。
* **务实的数据收集**:使用 GitHub 和 Google 查找被忽视的 IoC。
* **CTI 报告集成**:从 IoC.One 获取与 IoC 相关的报告。
* **EDR 集成**:根据你自己的安全工具(MDE、CrowdStrike)检查可观测对象。
# 快速开始 - TL;DR
> [!TIP]
> 如果你比较懒,你需要 Docker。 \
> 执行 `git clone`;将 `.env.sample` 复制为 `.env`;`docker compose up` 然后访问 `localhost:5000`。没错,就这么简单!
# 快速开始
* 首先,克隆仓库
```bash
git clone https://github.com/stanfrbd/cyberbro
cd cyberbro
```
## 编辑配置文件(必需)
```
cp .env.sample .env
```
> [!NOTE]
> 没有 API 密钥?没问题,只需将 `.env.sample` 复制为 `.env` 并将可选值留空。如果使用代理请小心。 \
> 你将能够使用**所有免费引擎!**
* 在 `.env` 文件中填写值(包括代理,如需要)。
> [!WARNING]
> `.env` 包含敏感密钥,绝不能提交。
> 对于生产/团队部署,请使用 SOPS、Vault 或等效的密钥管理工作流。
```bash
ABUSEIPDB=token_here
ALIENVAULT=token_here
CRIMINALIP_API_KEY=token_here
CROWDSTRIKE_CLIENT_ID=client_id_here
CROWDSTRIKE_CLIENT_SECRET=client_secret_here
DFIR_IRIS_API_KEY=token_here
DFIR_IRIS_URL=https://dfir-iris.local
DFIR_IRIS_SEARCH_NOTES=false
GOOGLE_CSE_CX=cx_here
GOOGLE_CSE_KEY=key_here
GOOGLE_CSE_URL=https://www.googleapis.com/customsearch/v1
GOOGLE_SAFE_BROWSING=token_here
HISTER_TOKEN=token_here
HISTER_BASE_URL=https://hister.example.com
IPAPI=token_here
IPINFO=token_here
MDE_CLIENT_ID=client_id_here
MDE_CLIENT_SECRET=client_secret_here
MDE_TENANT_ID=tenant_here
MISP_API_KEY=token_here
MISP_URL=https://misp.local
MISP_FEEDBACK_SERVER_URL=https://misp-feedback.local
MISP_FEEDBACK_TOKEN=token_here
OPENCTI_API_KEY=token_here
OPENCTI_URL=https://demo.opencti.io
PROXY_URL=
RANSOMWARE_LIVE_API_KEY=token_here
RL_ANALYZE_API_KEY=token_here
RL_ANALYZE_URL=https://spectra_analyse_url_here
ROSTI_API_KEY=token_here
SHODAN=token_here
SPUR_US=token_here
THREATFOX=token_here
VIRUSTOTAL=token_here
WEBSCOUT=token_here
```
> [!IMPORTANT]
> 从版本 `v0.13.0` 开始,Cyberbro 不再支持 `secrets.json` 和 `/config` 页面。参见[讨论 165](https://github.com/stanfrbd/cyberbro/discussions/165)。\
> 如果你已有旧版 `secrets.json`,请使用以下命令将其转换为 `.env`:
> `python3 scripts/secrets_json_to_env.py`
请参阅文档中的[部署高级选项](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment)。
# 启动应用
## 懒人简易方式 - 使用 docker
> [!WARNING]
> 请确保你安装的是 `compose` 插件,即使用 `docker compose` 而不是 `docker-compose`。
> 在 Docker 中,即使你本地的 `.env` 设置了 `FLASK_HOST=127.0.0.1`,应用也会在容器内绑定到 `0.0.0.0`。
```bash
docker compose up # use -d to run in background and use --build to rebuild the image
```
* 访问 http://127.0.0.1:5000 并尽情享用。
> 别忘了在构建镜像前编辑 `.env`。
请参阅文档中的[部署高级选项](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment)以获取所有 Docker 部署选项。
## 传统方式
* 克隆仓库并安装依赖。
在安装依赖之前,你可能想创建一个 [`venv`](https://docs.python.org/3/library/venv.html)。
```bash
pip install -r requirements.txt
```
* 使用 `gunicorn` 运行应用(干净模式)。
```bash
gunicorn -c prod/gunicorn.conf.py app:app
```
* 以开发模式运行应用。
```bash
python3 app.py
```
# 截图
<details>
<summary>查看所有截图</summary>
<img width="1897" height="909" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/b3a07f1e163ae260b2a5f908a70d571a145f702ad50b524725ce4b3562f7c367.png" />
<img width="1883" height="907" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/3d3404a7e55b688b497db428ecb7fa01b6a23ec8879e2c2c751c68a92545a334.png" />
<img width="1887" height="906" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/cd57a214ae604ed83ca50d119b49391afc0a66c03b3ed93feecfbb59578f5984.png" />
</details>
<img width="1788" height="1536" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/2e6051fe1ad7fadde5ff9074dbb4d96528dd2c8ab8262ea10e1fe49fee031153.png" />
<img width="1873" height="900" alt="image" src="https://assets.kitploit.com/production/public/readmes/10725/5201b888fdaa97465f141379e9f5caedb0bdd847b1e31a08b3e236df8b663ed6.png" />
> [!CAUTION]
> 如果你打算在**生产环境**中使用它,请使用配置良好的**反向代理** + **WAF** 以防止**安全问题**。
# Cyberbro 浏览器扩展
<p>
<a href="https://addons.mozilla.org/addon/cyberbro-analyzer/"><img src="https://assets.kitploit.com/production/public/readmes/10725/7e7e7002c8f357304f16d1d06ff840c40e92c66f6ed072b18da36329502c7a13.png" alt="Get Cyberbro Analyzer for Firefox"></a>
<a href="https://chromewebstore.google.com/detail/cyberbro-analyzer/nfcfigpaollodajabegcdobhmgaclbbm"><img src="https://assets.kitploit.com/production/public/readmes/10725/28dd6378e71c68b4f21b54ad99bb1225f978b8f2bacfa3c46444f988c09ace1c.png" alt="Get Cyberbro Analyzer for Chromium"></a>
<a href="https://microsoftedge.microsoft.com/addons/detail/cyberbro-analyzer/lbponbmcggcepflackehgpbceehagiam"><img src="https://assets.kitploit.com/production/public/readmes/10725/0a301e6c3048478ead36dfbccdba2e5263de7fbeb3de9d22a9f159f64f378273.png" alt="Get Cyberbro Analyzer for Microsoft Edge"></a>
</p>
# Cyberbro API
* API 位于 `/api/`,可通过 GUI 或命令行访问。
**目前有 3 个端点:**
* `/api/analyze` - 分析文本并返回分析 ID(JSON)。
* `/api/is_analysis_complete/<analysis_id>` - 检查分析是否完成(JSON)。
* `/api/results/<analysis_id>` - 检索先前分析的结果(JSON)。
```bash
curl -X POST "http://localhost:5000/api/analyze" -H "Content-Type: application/json" -d '{"text": "cyberbro.net", "engines": ["reverse_dns", "rdap_whois"]}'
```
```json
{
"analysis_id": "e88de647-b153-4904-91e5-8f5c79174854",
"link": "/results/e88de647-b153-4904-91e5-8f5c79174854"
}
```
```bash
curl "http://localhost:5000/api/is_analysis_complete/e88de647-b153-4904-91e5-8f5c79174854"
```
```json
{
"complete": true
}
```
```bash
curl "http://localhost:5000/api/results/e88de647-b153-4904-91e5-8f5c79174854"
```
```json
[
{
"observable": "cyberbro.net",
"rdap_whois": {
"abuse_contact": "[email protected]",
"creation_date": "2024-12-20",
"data_source": "rdap",
"emails": [
"[email protected]"
],
"expiration_date": "2026-12-20",
"link": "https://rdap.verisign.com/net/v1/domain/CYBERBRO.NET",
"name_servers": [
"anderson.ns.cloudflare.com",
"lisa.ns.cloudflare.com"
],
"organization": null,
"registrant": null,
"registrant_country": null,
"registrant_email": null,
"registrar": "Cloudflare, Inc.",
"update_date": "2025-11-20"
},
"reverse_dns": {
"reverse_dns": [
"172.67.197.226",
"104.21.42.7"
]
},
"reversed_success": true,
"type": "FQDN"
}
]
```
> [!NOTE]
> [专用文档页面](https://docs.cyberbro.net/quick-start/API-usage-and-engine-names)提供了所有可用引擎的名称。
# API 和第三方服务
* [AbuseIPDB](https://docs.abuseipdb.com/)
* [Abusix](https://abusix.com/)
* [Alienvault](https://otx.alienvault.com/)
* [CriminalIP](https://www.criminalip.io/)
* [CrowdStrike](https://www.crowdstrike.com/)
* [crt.sh](https://crt.sh/)
* [DFIR Iris](https://www.dfir-iris.org/)
* [Github](https://github.com/)
* [Google Safe Browsing](https://developers.google.com/safe-browsing)
* [Google](https://google.com/)
* [Google DNS](https://dns.google/)
* [Grep.App](https://grep.app/)
* [Hister](https://hister.org/)
* [Hudson Rock](https://hudsonrock.com/)
* [ICANN](https://lookup.icann.org/)
* [IPapi](https://ipapi.is/)
* [IPinfo](https://ipinfo.io/developers)
* [IPquery](https://ipquery.gitbook.io/ipquery-docs)
* [Ioc.One](https://ioc.one/)
* [Microsoft Defender for Endpoint](https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/microsoft-defender-for-endpoint-api)
* [Microsoft Entra ID (OpenID Configuration)](https://login.microsoftonline.com/)
* [MISP](https://www.misp-project.org/)
* [MISP Feedback](https://github.com/MISP/misp-feedback/)
* [OpenCTI](https://www.opencti.io/)
* [OpenRDAP](https://www.openrdap.org/)
* [Phishtank](https://www.phishtank.com/)
* [Ransomware.Live](https://ransomware.live/)
* [ReversingLabs Spectra Analyze](https://www.reversinglabs.com/products/spectra-analyze)
* [Rösti](https://rosti.bin.re/) - 重新打包的开源威胁情报
* [ScanMalware](https://scanmalware.com/)
* [Shodan](https://developer.shodan.io/)
* [Spur.us](https://spur.us/)
* [ThreatFox](https://threatfox.abuse.ch/api/)
* [URLscan](https://urlscan.io/)
* [VirusTotal](https://developers.virustotal.com/v3.0/reference)
* [WebScout](https://webscout.io/)
> [!NOTE]
> 有任何问题?请查看 https://docs.cyberbro.net 或提交 [issue](https://github.com/stanfrbd/cyberbro/issues/new) \
> 对于高级配置(部署前调整 `supervisord.conf`、选择可见引擎、更改 `/api/` 前缀...),请查看[专用文档页面](https://docs.cyberbro.net/quick-start/Advanced-options-for-deployment)。
# 特别感谢
衷心感谢所有提交拉取请求并帮助改进本项目的出色贡献者:
* [Florian PILLOT](https://github.com/Harukunnn),重构了引擎(重构和优化)。
* [Axel](https://github.com/botlabsDev),开发了 [Ioc.One](https://ioc.one/) 并添加了特定的 User-Agent,允许抓取 Ioc[.]One。
* [Jon Mark Allen](https://github.com/ubahmapk/),添加了更好的密钥管理和测试。他进行了大量重构并对代码库做了许多改进,包括 CriminalIP。
* [cirosec GmbH - Felix Friedberger](https://github.com/cirosec),添加了 crt.sh 引擎。
* [Stig Dahl](https://github.com/sdaaish),增强了 crt.sh 引擎,添加了 DFIR IRIS 搜索并修复了 Bandit 问题,修正了 MISP 引擎,添加了 MISP Feedback 引擎。
* [0xffr](https://github.com/0xffr),修复了 issue #98 - Grep.app 引擎损坏,并在 CriminalIP 引擎中正确添加了注释。
* [Maxime Berthault - Maxou56800](https://github.com/Maxou56800),开发了 Cyberbro CLI。
* [Jonas Lejon](https://github.com/jonaslejon),添加了 ScanMalware 引擎。
* [egeoguz04](https://github.com/egeoguz04),允许配置 Google CSE 端点。这将对即将到来的 Google 变更很有用。
非常感谢你们的贡献!
# 许可证
```
MIT License
Copyright (c) 2024-2026 stanfrbd
Permission is hereby granted, free of charge, to any person obtaining a copy
of this software and associated documentation files (the "Software"), to deal
in the Software without restriction, including without limitation the rights
to use, copy, modify, merge, publish, distribute, sublicense, and/or sell
copies of the Software, and to permit persons to whom the Software is
furnished to do so, subject to the following conditions:
The above copyright notice and this permission notice shall be included
in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS
OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY,
FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL
THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER
LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING
FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER
DEALINGS IN THE SOFTWARE.
```
# Logo
本项目使用的 logo 可免费用于个人和商业用途,可在[此处](https://www.veryicon.com/icons/object/material_design_icons/web-39.html)找到。