
 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques

This project does not achieve indistinguishability obfuscation. You should not be using this to product to protect secrets. It exists to deter reverse engineering, not prevent it

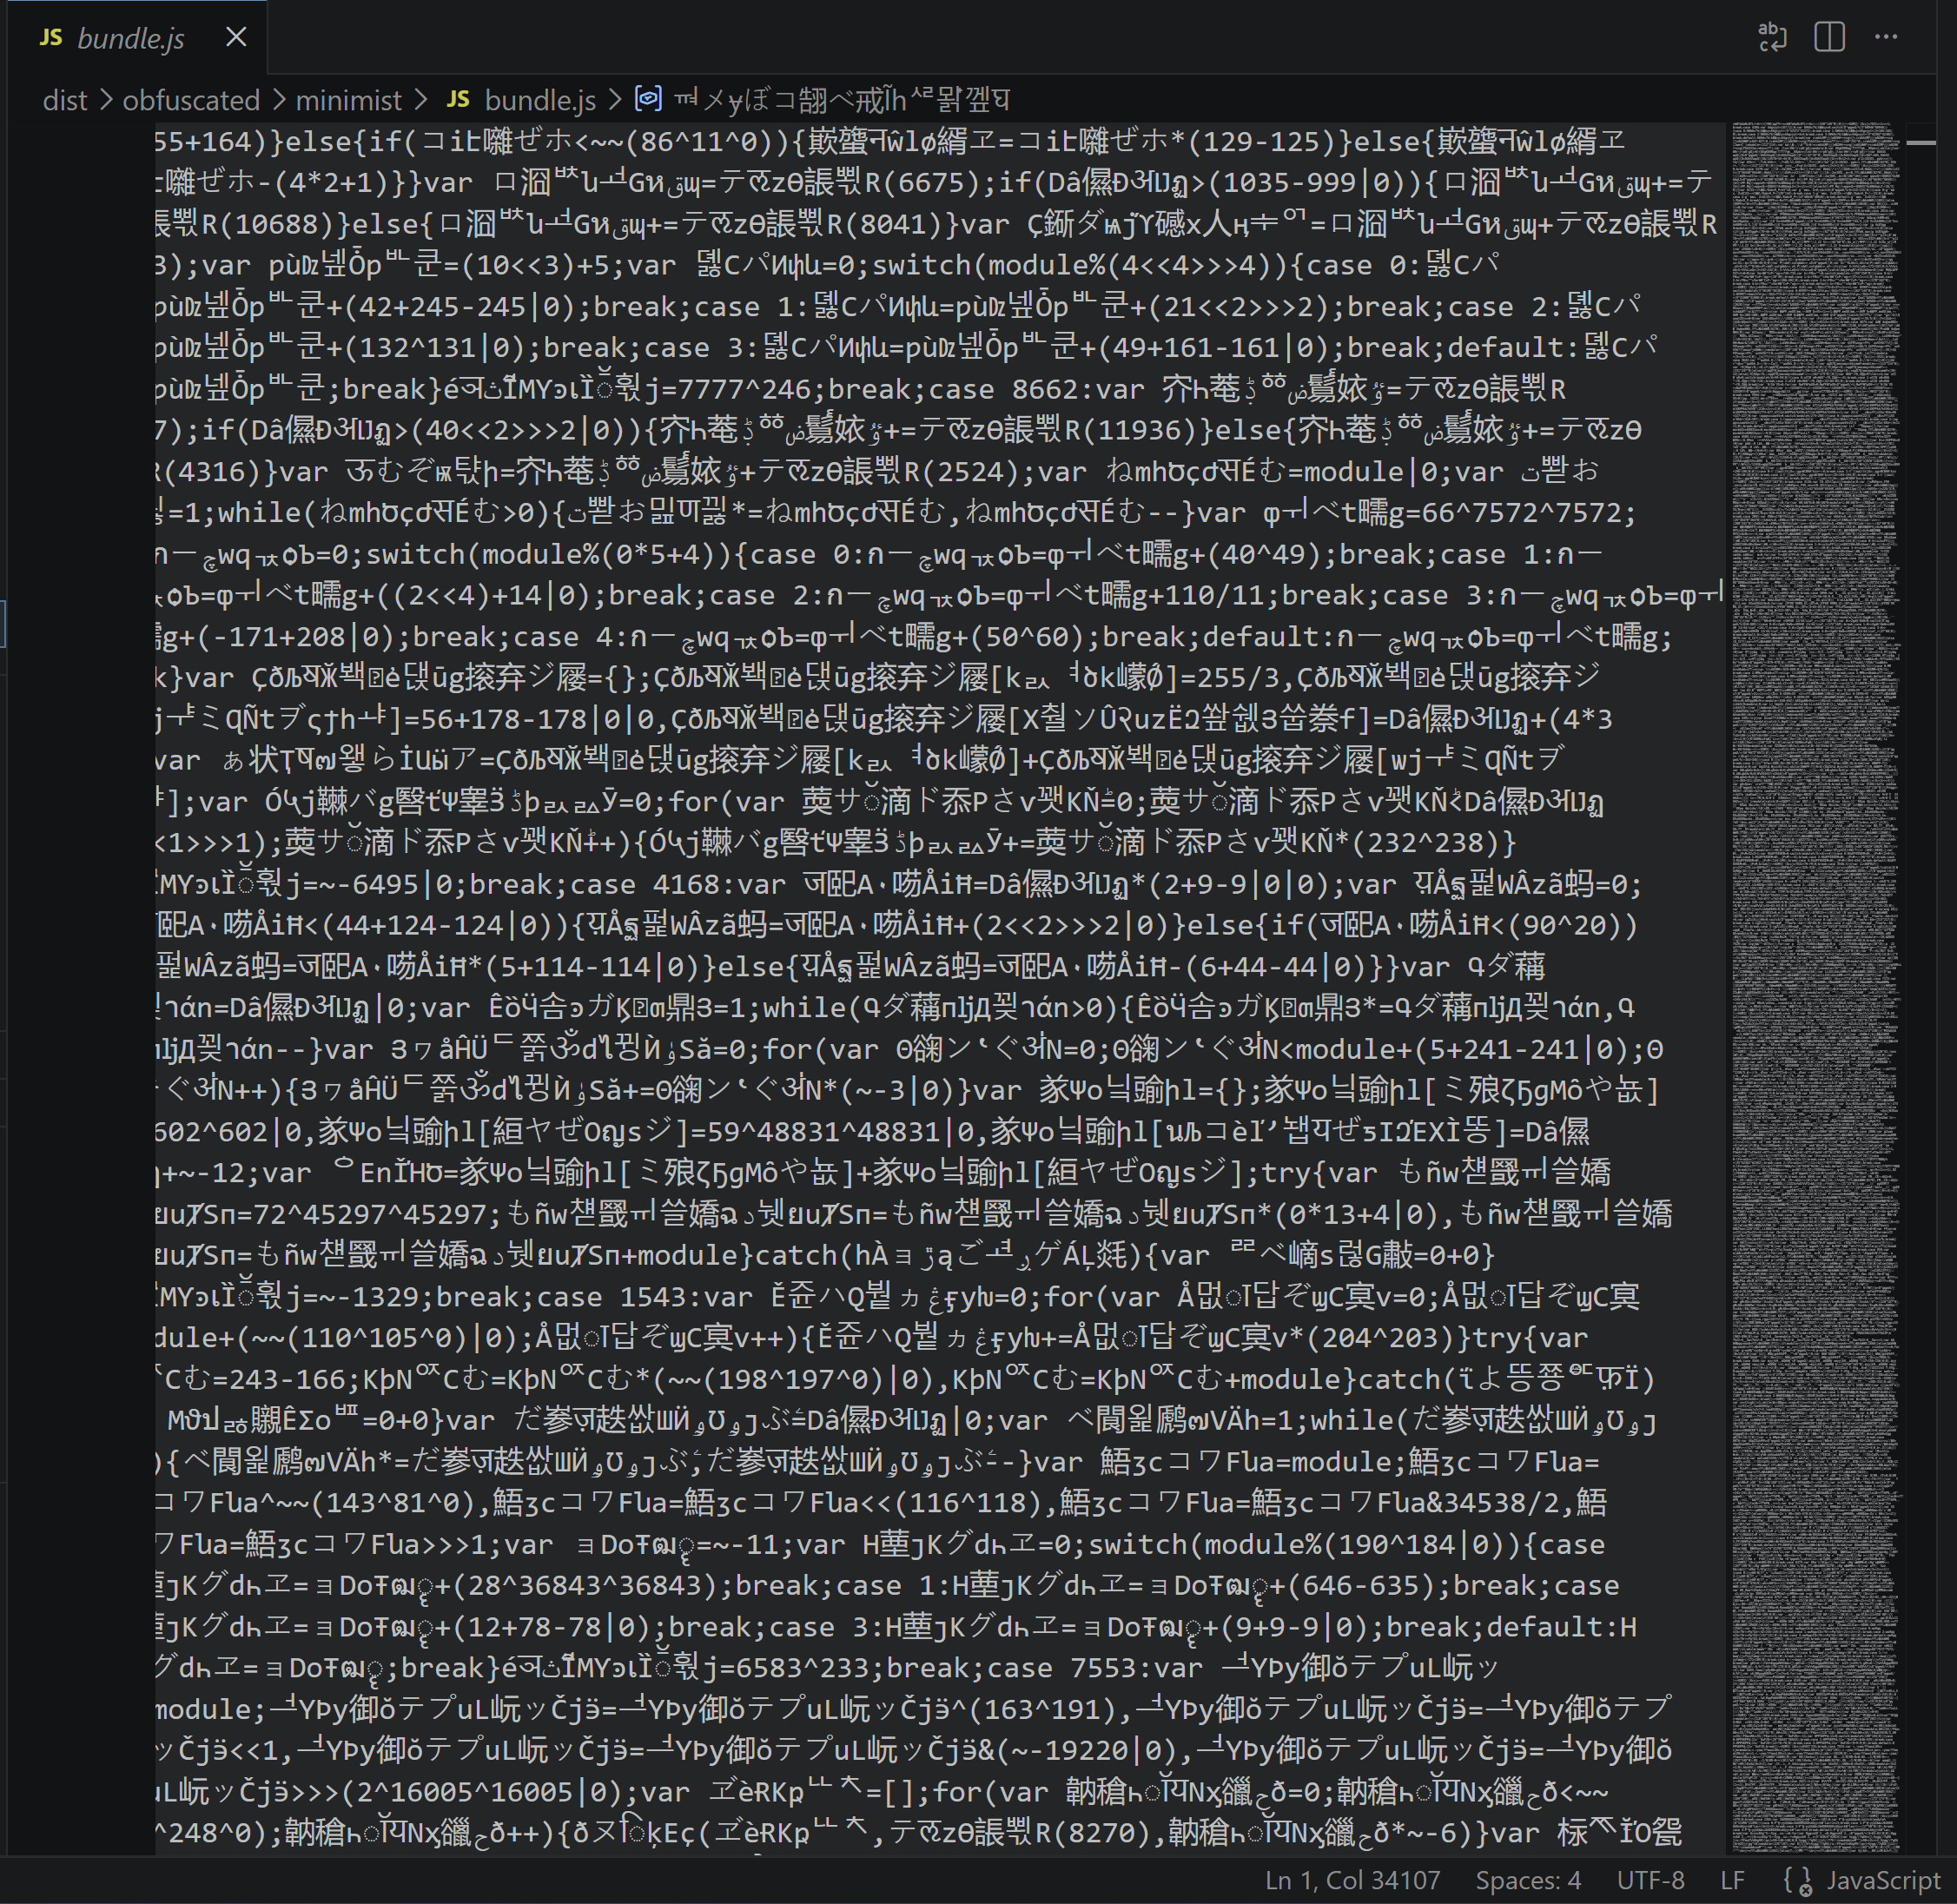 A JavaScript obfuscator designed to make code extremely difficult to read and analyze for both humans and LLMs. Written in TypeScript. Implements techniques from peer-reviewed cryptographic obfuscation research.
Node.js 24 is the default (see .nvmrc); Node.js 26 also works.
The supported range is ^24.15.0 || ^26.0.0. Node.js 22 and earlier are
not supported.
engine-strict=true in .npmrc makes npm install reject an unsupported
version up front rather than failing later with an opaque error.
nvm use # picks up .nvmrc
npm install -g egodeath      # CLI
npm install egodeath         # library
const { obfuscate, obfuscateMultiple } = require('egodeath');

const out = obfuscate(sourceCode, { targetTokens: 10000 });
npm install
npm run build
node dist/cli.js input.js > output.js
# Basic usage
npx egodeath input.js > output.js

# With target token budget (default: 2,000,000)
npx egodeath --target-tokens 500000 input.js > output.js

# Minimal obfuscation (small output)
npx egodeath --target-tokens 10000 input.js > output.js

# Maximum bloat (10M tokens)
npx egodeath --target-tokens 10000000 input.js > output.js

# Using environment variable
INPUT_FILE=input.js npx egodeath > output.js

# Help
npx egodeath --help
| Option | Default | Description |
|---|---|---|
--target-tokens <n> | 2000000 | Target output size in tokens. Small inputs are bloated up to this limit. Large inputs produce less bloat to stay within budget. |
--help, -h | Show help message |
npm run build              # Compile TypeScript to dist/
npm run start              # Run the obfuscator (reads input.js)
npm run test               # Run the test suite
npm run typecheck          # Type check application, tests, and tools
npm run obfuscate-package  # Run compatibility tests against npm packages
const { obfuscate } = require('./dist/obfuscator');

const code = 'function add(a, b) { return a + b; }';
const obfuscated = obfuscate(code);

// With options
const obfuscated = obfuscate(code, { targetTokens: 500000 });
Use the explicit opt-in CSP-safe profile when the output must run without string code generation (for example, a Manifest V3 popup or service worker):
const { obfuscate } = require('egodeath');
const ratio = 30;
const output = obfuscate(sourceCode, {
  targetTokens: Math.ceil(sourceCode.length * ratio / 4),
  cspSafe: true,
  stubConsole: false,
});
npx egodeath --csp-safe --no-console-stub --target-tokens 30000 input.js > output.js
cspSafe is also accepted by obfuscateMultiple. It is false by default, so
existing callers keep the original profile. Ratio 30 is a budget heuristic:
targetTokens * 4 / input.length, not an exact output-size multiplier or security
level. Rounding the token count can make the ratio slightly larger than 30.
The profile keeps the same budget and compatible transforms:
debugger statements instead of
evaluating encoded debugger strings. Debugger traps are consequently easier to
recognize; they can still pause execution when developer tools are attached.toString integrity probes remain. The eval-native probe
is omitted, and the global-variable eval-encoding transform is skipped. Global
identifiers therefore remain visible; their lexical lookup behavior is kept.This mode changes generated helpers, not source semantics. Source-provided
eval, Function constructors, or string timers remain incompatible with strict
CSP. Do not treat this as a sanitizer or a promise that arbitrary inputs run in an
extension. It does not change a manifest, add unsafe-eval, or lower the budget.
Use stubConsole: false / --no-console-stub when sharing a runtime with libraries
whose logging should remain available. Existing integrity/tripwire behavior and
performance tradeoffs still apply.
Validation includes ratio-30 execution with Node VM string code generation
disabled, delayed timer callbacks, lexical shadowing, ESM imports/live exports,
batch and CLI entry points. A manual Chromium Manifest V3 smoke check of the generated
profile also passed without unsafe-eval; applications should test their own final
bundle because source callbacks serialized into another execution context must
remain self-contained.
The obfuscator applies 20 transforms across 4 phases. Each stage builds on the previous one.
| Order | Transform | File | Description |
|---|---|---|---|
| 1 | Anti-Debug Traps | transforms/antiDebug.ts | Injects eval("debugger") statements and 10-20 setInterval loops with prime-number intervals (5s-600s) that repeatedly trigger debugger breakpoints. Each instance uses unique encoded strings. |
| 2 | Punctured Program Tripwires | transforms/tripwires.ts | Embeds hidden checks comparing parameter hashes against secret values. 5 hash patterns (bitwise fingerprint, modular arithmetic, charCodeAt, numeric hash, typeof+length). Triggers silent state corruption, busy loops, or throws on secret inputs. [Paper 4] |
| 3 | LPN Noise Injection | transforms/noiseInjection.ts | Adds and cancels random noise through split paths in arithmetic computations. 6 patterns: add/sub, XOR, mul/div, split dual-variable, computed hash-chain, bit-rotate. Intermediate values are meaningless without tracing full cancellation. [Paper 7] |
| Order | Transform | File | Description |
|---|---|---|---|
| 4 | Control Flow Flattening | transforms/controlFlowFlattening.ts | Converts function bodies into while(true) { switch((_s * P) % M) { ... } } state machines with modular arithmetic dispatch — case values are encoded through (stateId * multiplier) % modulus using random prime parameters. [Paper 3] |
| 5 | Opaque Predicates | transforms/opaquePredicates.ts | Injects if conditions that always evaluate to true or false but are mathematically hard to prove (e.g., (x*x+x)%2===0). 15 predicate formulas across modular arithmetic, bitwise, and type-check categories. |
| 6 | Proxy Functions | transforms/proxyFunctions.ts | Routes all function calls through two dispatchers: _fc(fn, ...args) for simple calls, _mc(obj, prop)(...args) for method calls, preserving method lookup before argument evaluation. Uses Function.prototype.apply captured in a local variable for resilience. |
| 7 | Context Window Exhaustion | transforms/contextExhaustion.ts | Wraps expressions in deeply nested ternaries with opaque conditions, void-expression chains, and conditional void padding. Forces LLMs to waste context window tokens on noise. |
| 8 | Comma Expression Merging | transforms/commaExpressions.ts | Collapses consecutive expression statements into single comma expressions: a(); b(); return c() becomes return a(), b(), c(). |






