AI 驱动的安全副驾驶,在您编码时捕捉漏洞。为开发者提供实时安全扫描、教学式解释和自动修复。
CodeGuard Copilot 在你编写代码时捕获安全漏洞,而不是在你提交之后。它将确定性正则表达式模式检测与 AI 驱动的深度分析以及来自 Raven/WraithWall 生态系统的实时攻击者情报相结合,为你提供其他 VS Code 安全扩展无法提供的上下文。
它的独特之处:
.codeguard.json 自定义规则配置 — 正则表达式、严重性、CWE、按文件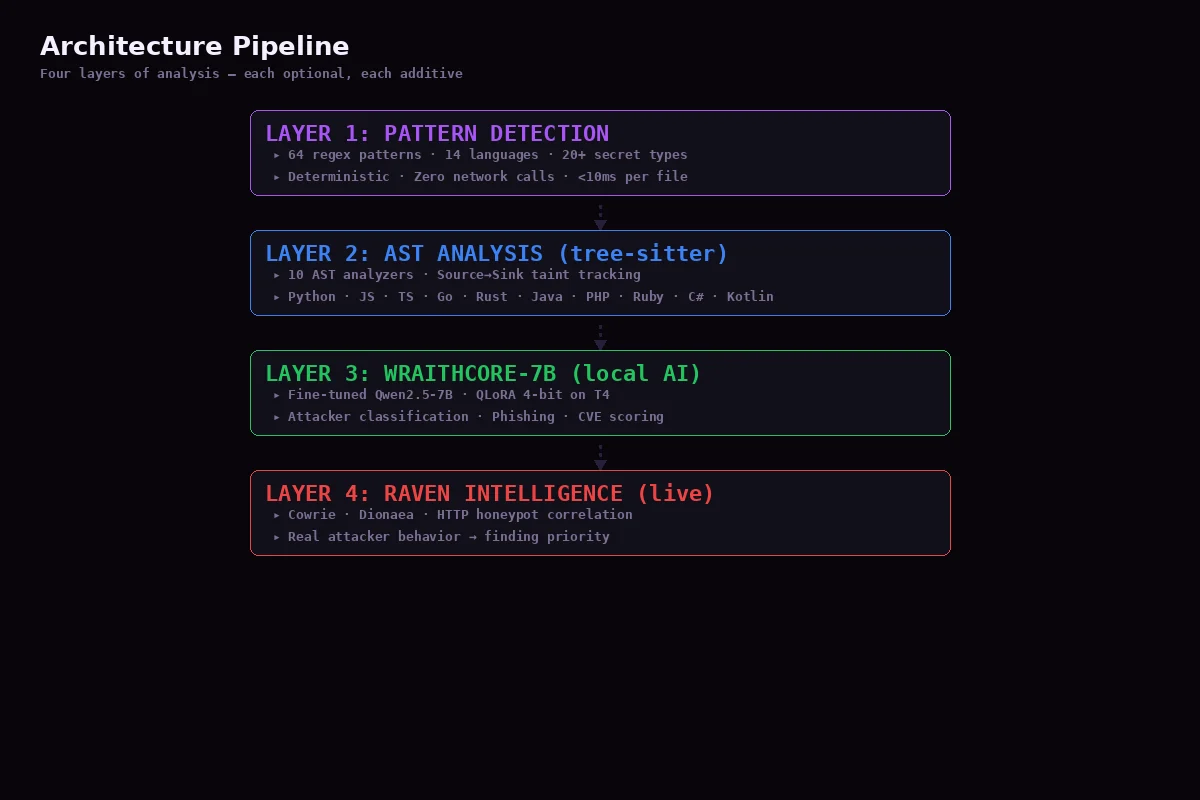
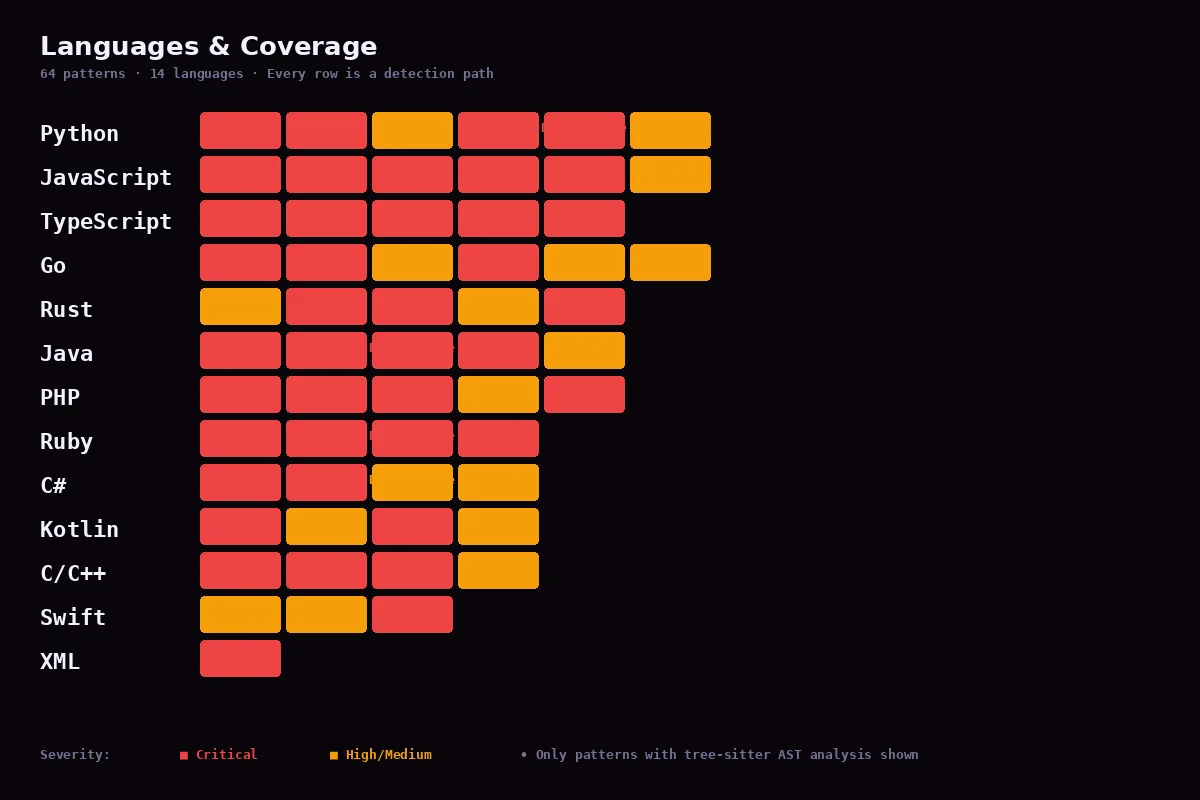
 │ │ │ │
│ │ ┌─────────────┐ ┌────────────────┐ │ │
│ │ │ Knowledge │ │ Raven Bridge │ │ │
│ │ │ Graph │ │ ← attacker data │ │ │
│ │ │ finding→CWE │ │ → threat intel │ │ │
│ │ │ →MITRE→fix │ │ │ │ │
│ │ └─────────────┘ └────────────────┘ │ │
│ └──────────────────┬───────────────────┘ │
│ │ │
│ ▼ │
│ ┌──────────────────────────────────────┐ │
│ │ Developer Feedback │ │
│ │ QuickFix · Explain · Suppress · Fix │ │
│ │ Training · Report · CI/CD │ │
│ └──────────────────────────────────────┘ │
│ │
└──────────────────────────────────────────────┘
│
▼
┌──────────────────────────────────────────────┐
│ WraithWall / Raven │
│ │
│ Cowrie Honeypot → Attacker Telemetry │
│ Campaign Correlation → Behavioral DNA │
│ CISA KEV → OWASP → Composite Scoring │
│ Cross-Repo Systemic Patterns │
│ Dark-Web Breach Monitoring │
└──────────────────────────────────────────────┘
---

## Raven 情报桥

CodeGuard Copilot 是 Raven 攻击者遥测流水线的**前端情报消费者**。当 Cowrie 蜜罐观察到真实攻击者使用漏洞利用技术时,这些模式会流入 CodeGuard:
Attacker uses SQL injection on honeypot ↓ Raven detects: CWE-89, credential_access, threat_score=85 ↓ RavenIntelBridge.ingestEvent() receives event ↓ Generates candidate CodeGuard pattern at confidence 0.85 ↓ Proposed pattern: "SQL Injection (attacker-observed)" ↓ Human review → published as CodeGuard rule ↓ Developers protected against the actual exploit
反之,当 CodeGuard 发现漏洞时,它会生成结构化的 Raven 反馈:
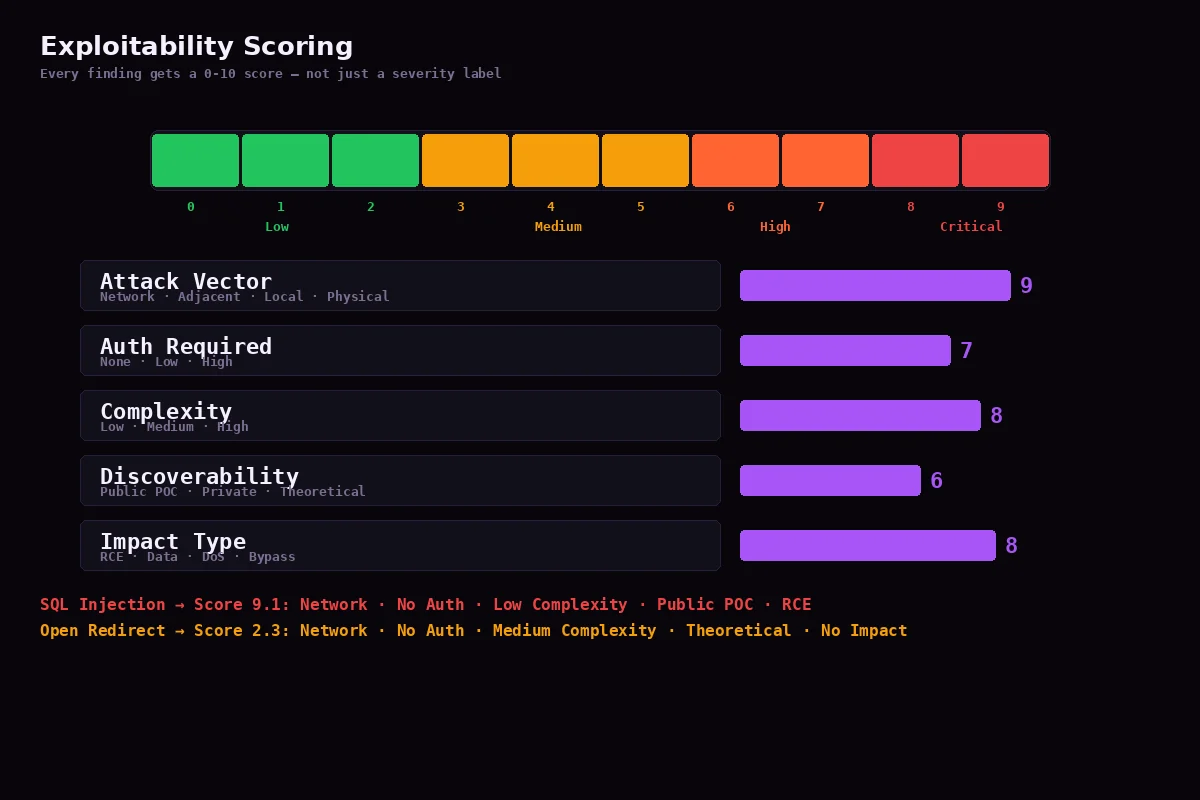
CodeGuard finding: CWE-798 hardcoded secret in auth/login.js ↓ RavenThreatFeedback.generateIntelligence() ↓ MITRE techniques: T1552, T1078 ↓ Raven priority score: 72 (network attack vector, low complexity) ↓ Raven elevates this finding in composite scoring ↓ SOC team sees: "Attacker-aligned credential finding in production repo"
---

## 检测到的漏洞类别

### 严重
SQL 注入(CWE-89)、命令注入(CWE-78)、NoSQL 注入(CWE-943)、硬编码密钥(CWE-798)、不安全反序列化(CWE-502)

### 高危
XSS(CWE-79)、基于 DOM 的 XSS、路径遍历(CWE-22)、文件上传(CWE-434)、弱加密(CWE-327)、不安全块(Rust)、未转义 HTML(Go)

### 中危
CORS 配置错误(CWE-942)、开放重定向(CWE-601)、不安全随机数(CWE-338)、ReDoS(CWE-1333)、内存泄漏(C++)、批量赋值(Ruby)

### 低危
弱密码存储、Express Trust Proxy、缺失安全头、框架反模式

### 语言特定(18 个新增)
Go:SQLi、不安全随机数、硬编码密钥、未转义 HTML
Rust:不安全块、硬编码密钥、命令注入、弱加密
C++:缓冲区溢出、内存泄漏、SQL 注入
C#:SQL 注入、连接字符串、不安全反序列化
Ruby:SQL 注入、命令注入、批量赋值、不安全 YAML

---

## 微调安全模型(v0.3.1)

CodeGuard 的微调模型(`Niffy90/codeguard-security-7b`)是 **Qwen2.5-7B-Instruct** 上的 LoRA 适配器,在 8 个类别的 32 个安全漏洞模式上训练:

- **模式 1(默认 — HF Router API):** 无需 GPU。使用 HuggingFace 最快的推理提供商,配合自定义安全系统提示。
- **模式 2(本地 GPU — `CODEGUARD_LOCAL_MODEL=1`):** 加载微调后的 LoRA 适配器,使用 QLoRA 4 位量化。需要约 5GB GPU 显存。

```bash
# Local GPU inference
CODEGUARD_LOCAL_MODEL=1 codeguard scan app.py

# Or via Python
CODEGUARD_LOCAL_MODEL=1 python3 -c "
from codeguard import CodeGuardEngine
engine = CodeGuardEngine(use_local_model=True)
findings = engine.scan_file('app.py')
print(findings)
"
训练数据集: 来自 WraithWall 蜜罐网络的 1,666 个样本(500 个会话)、OpenPhish + URLhaus(500 个钓鱼 URL)、CISA KEV(500 个 CVE)以及良性样本(166 个)。通过 QLoRA 在 T4 GPU 上训练。
git clone https://github.com/niffyhunt/codeguard-copilot.git
cd codeguard-copilot
npm install
npm run compile
# Press F5 in VS Code to launch Extension Development Host
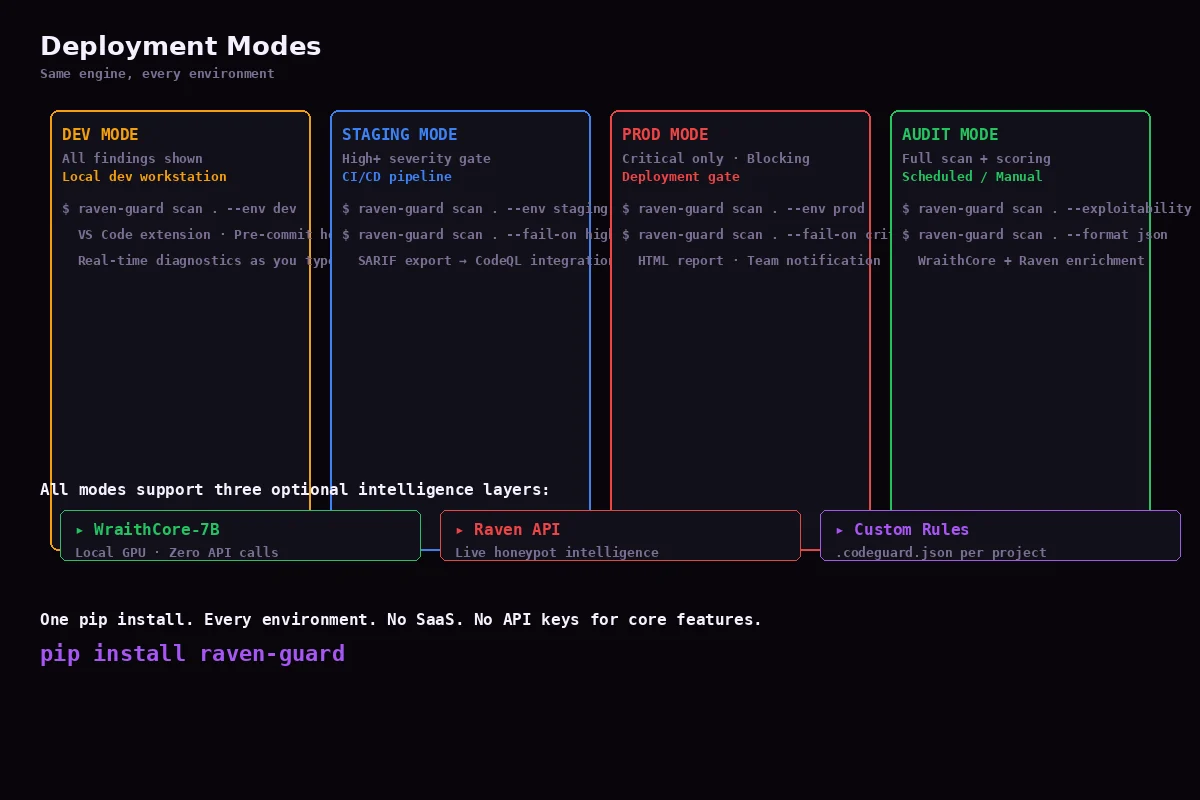
pip install raven-guard
raven-guard scan .
raven-guard scan app.py --severity critical,high
raven-guard scan . --format sarif --output results.sarif
raven-guard doctor
{
  "codeguard.enableRealtime": true,
  "codeguard.scanDelay": 500,
  "codeguard.aiProvider": "groq",
  "codeguard.enableAI": true,
  "codeguard.enablePlugins": true,
  "codeguard.enableTraining": true,
  "codeguard.severityFilter": ["critical", "high", "medium"]
}
{
  "version": "0.1.0",
  "customPatterns": [{
    "id": "my-custom-rule",
    "type": "Custom: Unsafe Function",
    "severity": "high",
    "regex": "eval\\\\(.*userInput",
    "languages": ["javascript"],
    "message": "eval() with user input detected",
    "cwe": "CWE-95"
  }],
  "severityOverrides": { "SQL Injection": "critical" },
  "excludedPaths": ["vendor/", "node_modules/", "*.test.ts"]
}