.______________________________________________________________________________.
|  :: H-AUDITOR :: v1.1.0 :: "DIALING IN... CARRIER DETECTED" ::                |
|------------------------------------------------------------------------------|
|  "warez? nah. headers. we trade banners, not bins."                          |
|  "if it answers any password, it ain't production — it's a lure."            |
|  "respect the sysop. probe only what you own. leave no STOR behind."         |
|______________________________________________________________________________|



这看起来像蜜罐吗?(DTLLAH) — 多协议 CLI,用于指纹识别目标 IP 的行为是否像蜜罐,实现多种策略来识别蜜罐。
站点(BBS / NFO): https://mziqudhd92.github.io/honeypot-auditor/
Agents / AEO: llms.txt · agents.md
  ▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄▄
  █  >>> LIVE DEMO · v1.1.0 · DD-HONEYPOT · 5 SERVICES · -v / --deep <<<   █
  ▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀▀
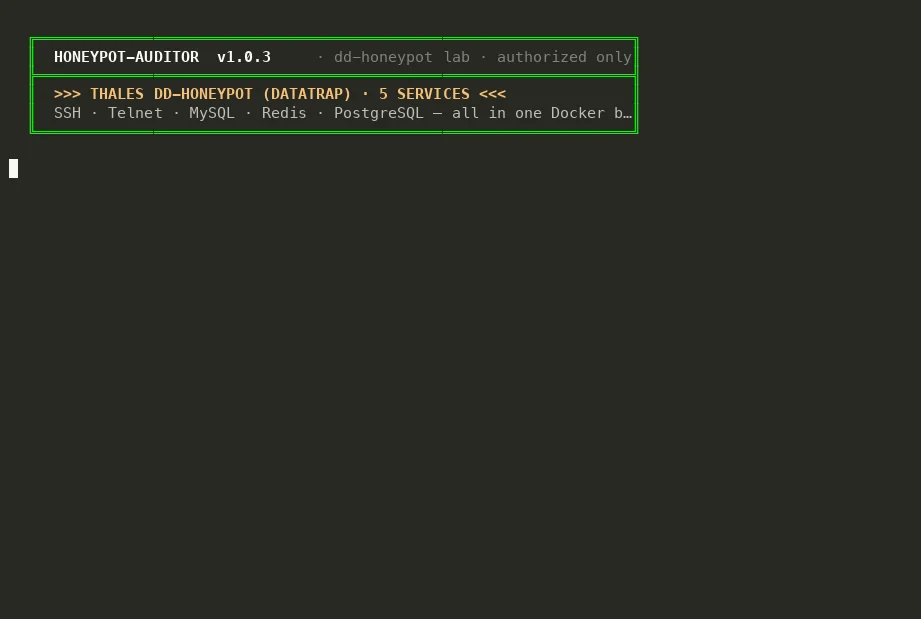
  "five DataTrap faces on loopback: map the ports, run -v, then --deep.
   Honeyscore 100% — Confirmed Honeypot. same fingerprinter, new decoy."
                        — dd-honeypot lab · v1.1.0 · authorized only
.------------------------------------------------------------------------------.
|  NFO · READ BEFORE YOU DIAL                                                  |
|------------------------------------------------------------------------------|
|  Authorized targets ONLY. Lab boxes. Decoys you own. Sensors you run.        |
|  Permission on paper (or in ticket).                                         |
|                                                                              |
|  Scanning random /16 because Shodan said "interesting" = YOU are the bait.   |
|                                                                              |
|  TYPE ...... Multi-Protocol Decoy Fingerprinter / Lab Util                   |
|  PLATFORM .. Linux · macOS · Windows (Python 3.11+)                          |
|  LICENSE ... MIT · spread the sauce · keep the copyright                     |
|  PYPI ...... pypi.org/project/honeypot-auditor                               |
|  REPO ...... github.com/mziqudhd92/honeypot-auditor                          |
'------------------------------------------------------------------------------'
Honeypot Auditor — 一个 CLI,只问一个直白的问题:
这个 IP 的行为像低交互蜜罐,还是像那种真的会因为停机时间向某人收费的东西?
被动情报(Shodan Honeyscore)加上主动的、非破坏性的探测,覆盖常见的诱饵面。输出加权 Honeyscore(0–100%)、Rich 控制台表格、带版本号的 JSON 报告。
快速入门教程:AWS Spot 蜜罐实验环境 · 本地 Web UI(serve,XP.css)
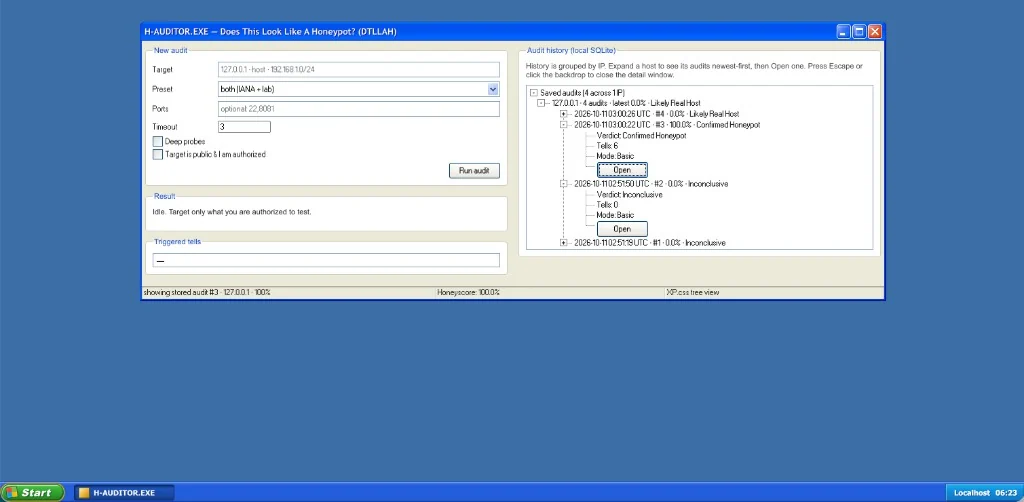
  "localhost UI · IP-grouped history · Open a saved audit for the full tell tree."
                        — honeypot-auditor serve · XP.css · 127.0.0.1 only
  [ BASIC ]  passive intel · Nmap NSE · 34 protocol engines (TCP + UDP) · up to 3 strategies each
  [ DEEP  ]  shell semantics · OS coherence · HASSH · TCP stack · FSM fuzz
             · co-tenancy buffet detect · latency · latency-under-load · egress bait
             (flag: --deep · more intrusive · same authorization rules)
"elite? nah. just consistent timeouts and a honest --confirm-authorized."
  ┌─ USERS · PyPI (public index — no pip config voodoo) ─────────────────────┐
  │  python3 -m venv .venv && source .venv/bin/activate   # recommended      │
  │  pip install honeypot-auditor                                            │
  │  pip install "honeypot-auditor[full]"    # + nmap impacket shodan scapy   │
  │  honeypot-auditor --version                                              │
  └──────────────────────────────────────────────────────────────────────────┘
| 安装 | 解锁功能 |
|---|---|
pip install honeypot-auditor | 核心探测(Paramiko + Requests + Rich + figlet 头部) |
pip install "honeypot-auditor[full]" | + Nmap 集成 · SMB/Impacket · Shodan SDK · Scapy · 深度 telnet |
SHODAN_API_KEY 或 --shodan-key 可启用 Shodan OSINT(需主动选择启用——否则不会查询)。[full] 仅安装客户端库。
Nmap 可执行文件需单独作为受信任的系统安装。
Windows PowerShell 使用 py -m venv .venv,随后执行 .\.venv\Scripts\Activate.ps1。
原始套接字探测可能需要 Npcap 和提权终端;不可用的功能会被报告并跳过。
首次接入:
honeypot-auditor --help          # -h, --help, or /help (BBS figlet header)
honeypot-auditor --target 127.0.0.1
  ┌─ DEVELOPERS · from source ───────────────────────────────────────────────┐
  │  git clone https://github.com/mziqudhd92/honeypot-auditor.git            │
  │  cd honeypot-auditor && python3 -m venv .venv && source .venv/bin/activate│
  │  pip install -e ".[full,dev,security]"                                   │
  │  make test-cov && make lint && make security                             │
  └──────────────────────────────────────────────────────────────────────────┘
无需 pip install(git checkout — 一次性安装最小依赖):
pip install rich paramiko requests    # pyproject.toml is the single source of truth
python3 honeypot-auditor.py --help
python3 honeypot-auditor.py --target 127.0.0.1
pyfiglet / rich-argparse 对于脚本路径是可选的(如果缺失,则使用纯文本标题 + 标准库帮助)。完整探测需要 pip install -e ".[full]"。
发布维护者 → docs/PUBLISHING.md
# local lab · default probes IANA + docker/lab ports (22 and 2222, 80 and 8081, …)
honeypot-auditor --target 127.0.0.1

# go deep · six extra detection axes · still no exploits
honeypot-auditor --target 127.0.0.1 --deep

# internet-facing target · need explicit ack + Shodan key if you want intel
honeypot-auditor --target 203.0.113.10 --confirm-authorized

# SSH 22 only (does not scan the rest of the preset)
honeypot-auditor --target 203.0.113.10 -p 22 --confirm-authorized

# subnet sweep · IPv4 CIDR up to /24 (254 hosts) · parallel by default
honeypot-auditor --target 192.168.1.0/24 --scan-concurrency 16 \
  --confirm-authorized
# subnet JSON → honeypot-audit-subnet-192.168.1.0_24.json (summary + per-host reports)

# interactive wizard · step-by-step target/preset/depth, Rich tables, saves to SQLite
honeypot-auditor wizard




