在JetBrains Ktor 2.3.5之前,ContentNegotiation的默认配置与XML格式存在XXE漏洞。
该漏洞由@marychatte于2023年9月29日修复(https://github.com/ktorio/ktor/pull/3770),漏洞是由于外部库`xmlutil version 0.86.1`中的配置错误导致的供应链攻击。

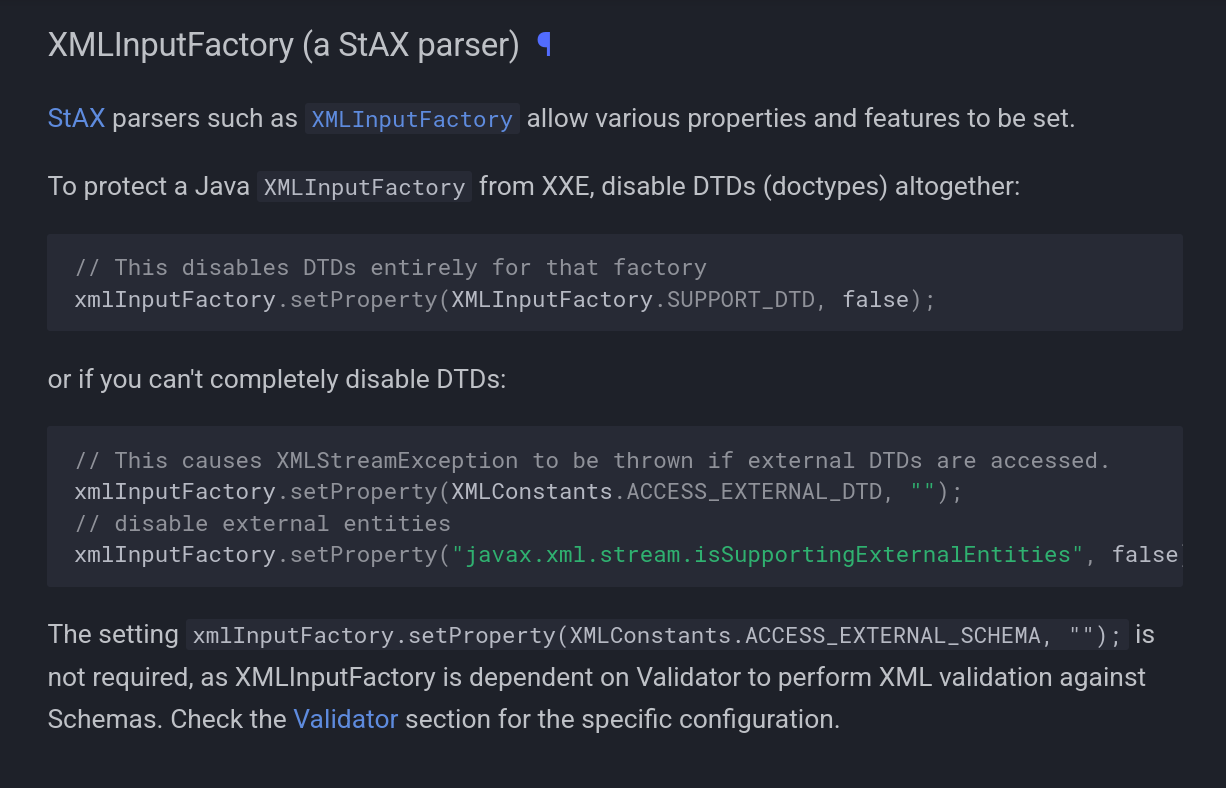
根据OWASP指南(https://cheatsheetseries.owasp.org/cheatsheets/XML_External_Entity_Prevention_Cheat_Sheet.html),修复措施不够全面,我在这里找到了一个有趣的答案(https://security.stackexchange.com/questions/260956/java-xxe-vulnerability):`The main objective is to disable DTDs, it basically consists of the primary defense against this attack.`