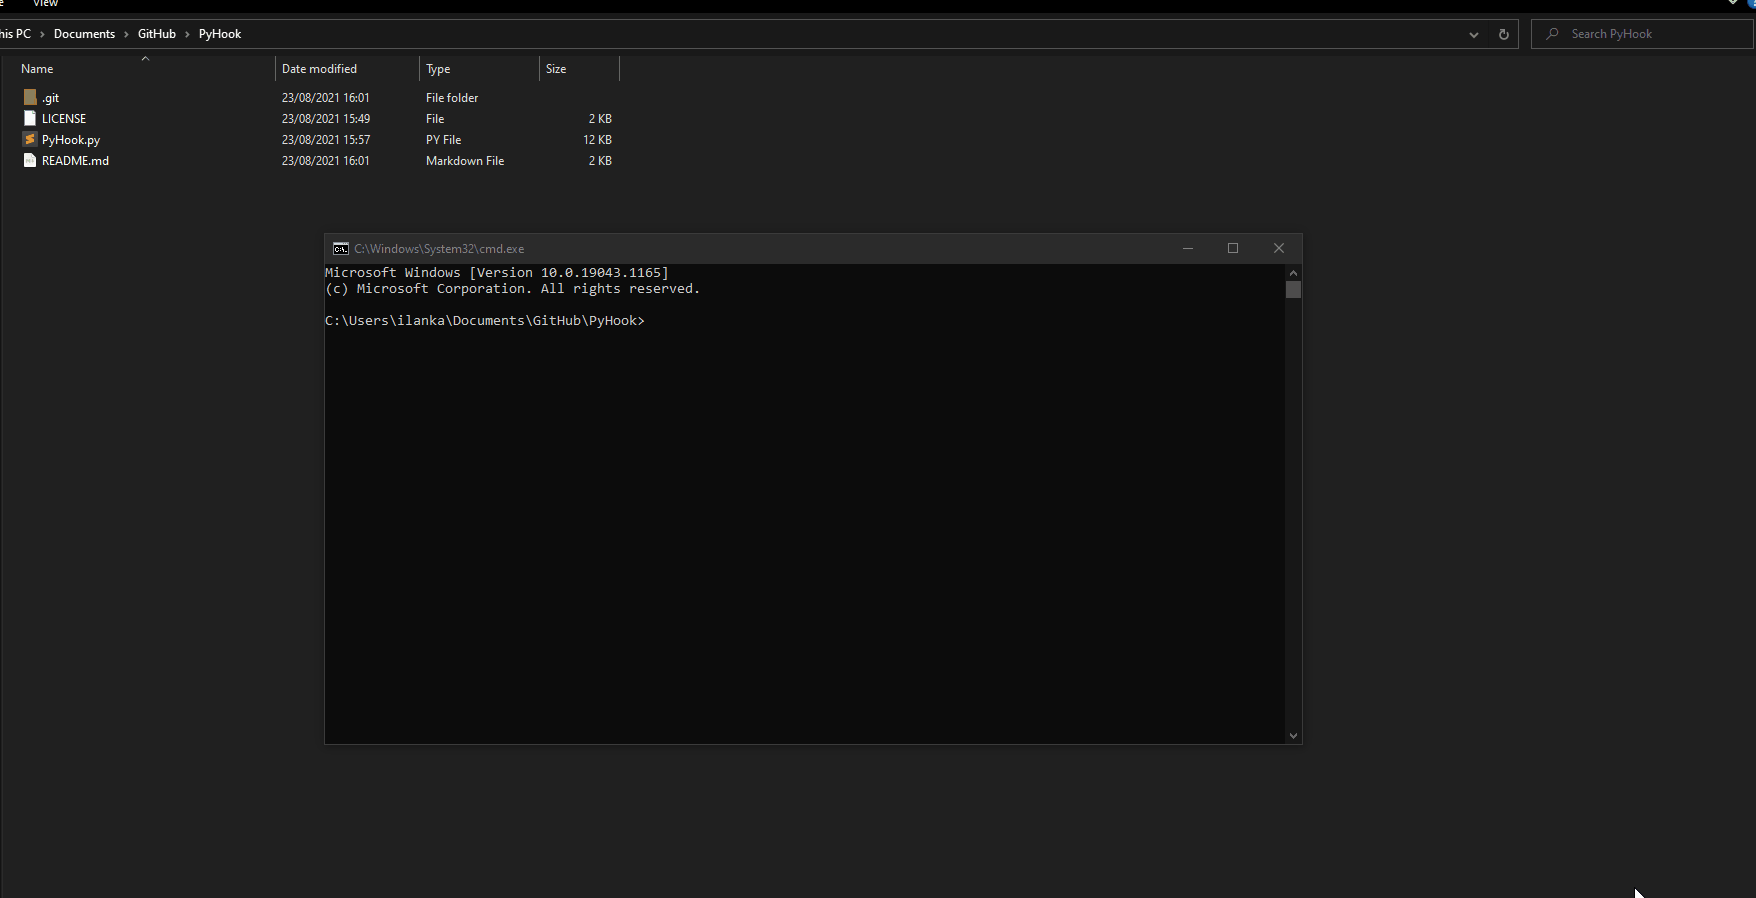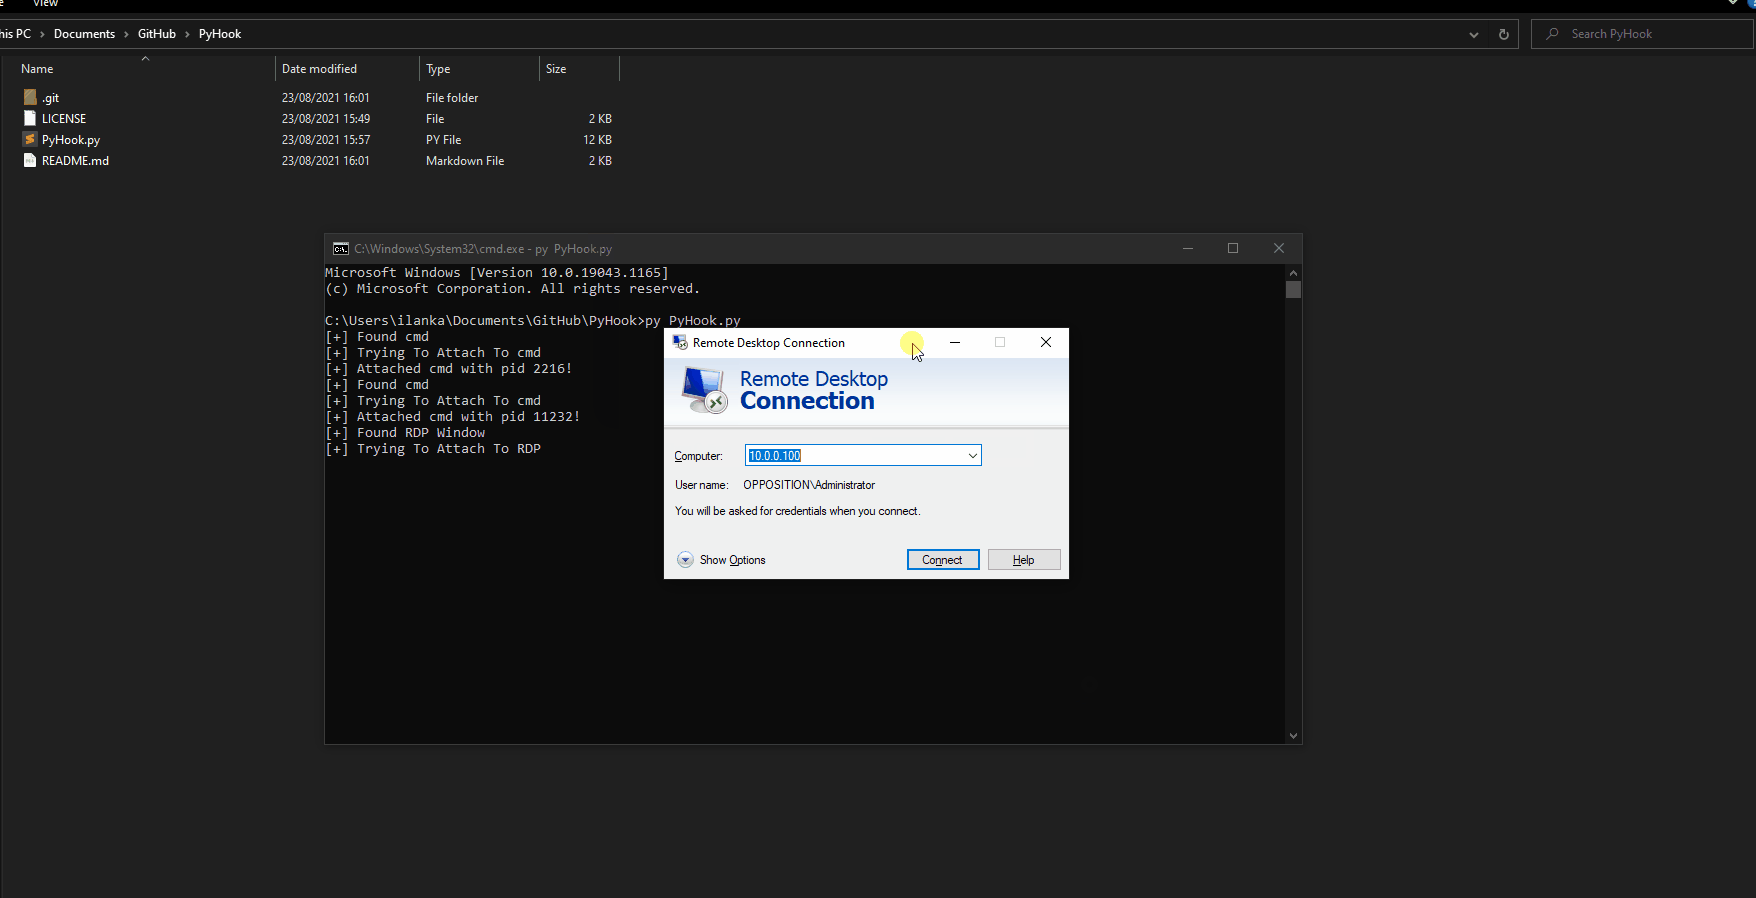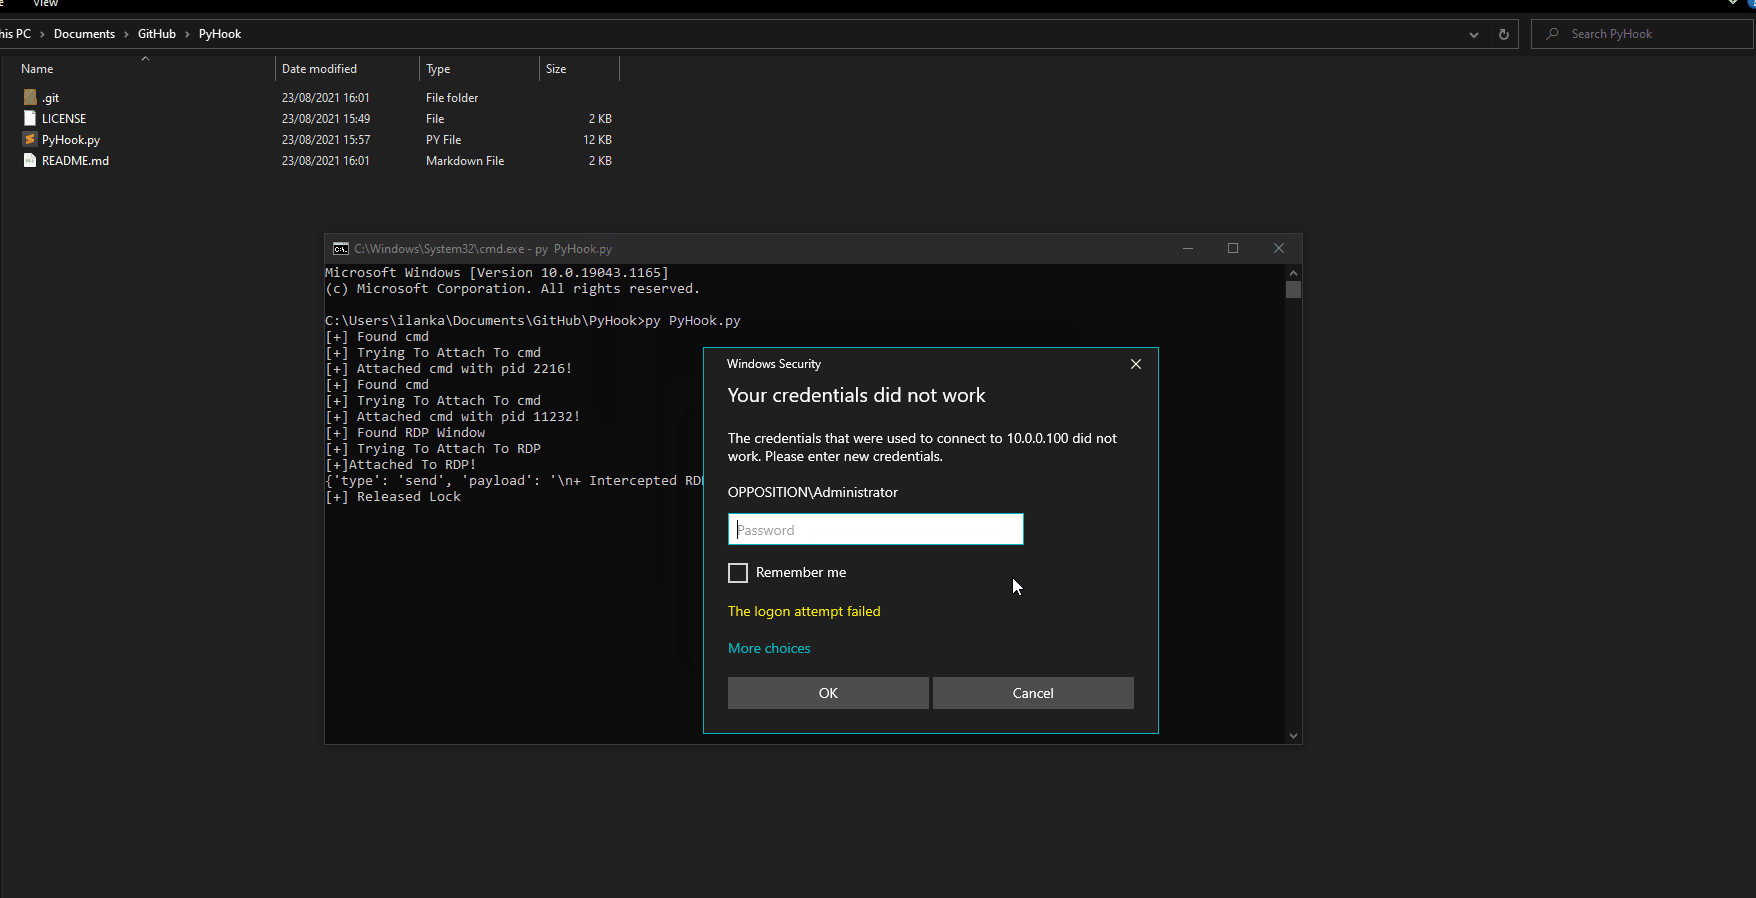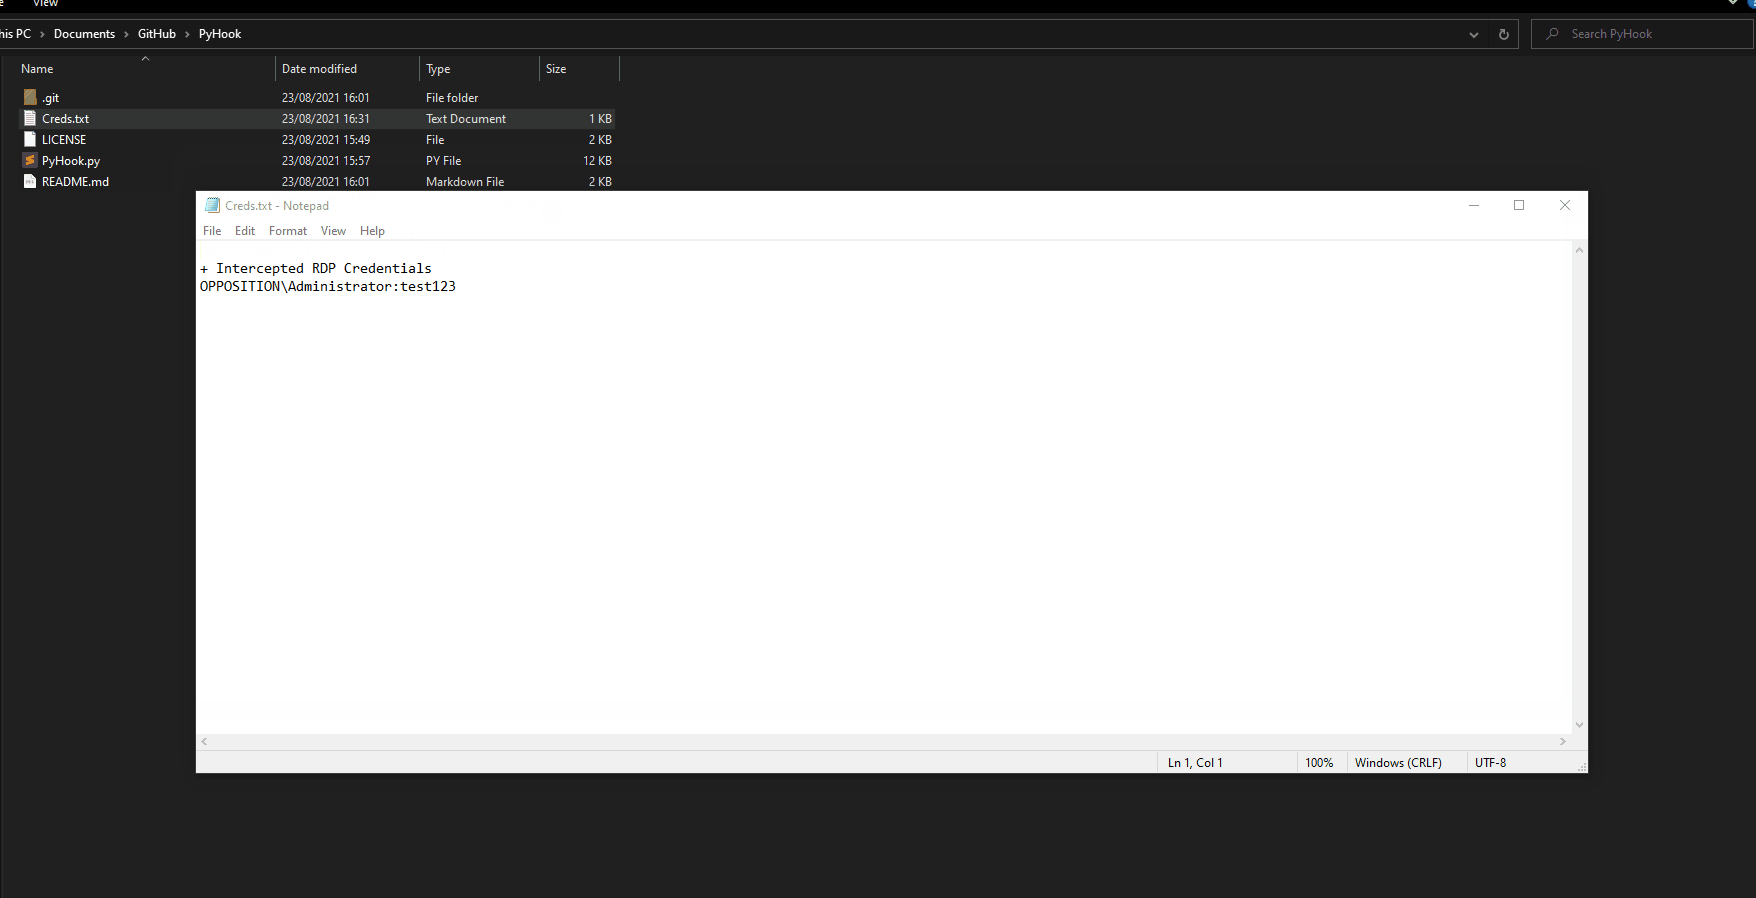
PyHook 是我的 SharpHook 项目的 Python 实现,它使用多种 API 钩子来获取所需的凭据。
PyHook 使用 Frida 将其依赖注入目标进程。
| 进程 | API 调用 | 描述 | 进度 |
|---|---|---|---|
| mstsc | CredUnPackAuthenticationBufferW | 钩取 mstsc 中的 CredUnPackAuthenticationBufferW,输出用户名和密码 | 已完成 |
| runas | CreateProcessWithLogonW | 钩取 runas 中的 CreateProcessWithLogonW,输出用户名、密码和域名称 | 已完成 |
| PowerShell | CreateProcessWithLogonW | 钩取 PowerShell 中的 CreateProcessWithLogonW,输出用户名、密码和域名称(例如 Start-Process cmd -Credential X) | 已完成 |
| cmd | RtlInitUnicodeStringEx | 钩取 cmd 中的 RtlInitUnicodeStringEx,输出特定过滤器(如 "-p"、"password" 等)的数据 | 已完成 |
| MobaXterm | CharUpperBuffA | 钩取 MobaXterm 中的 CharUpperBuffA,输出 RDP 和 SSH 登录的凭据 | 已完成 |
| explorer(UAC 提示) | CredUnPackAuthenticationBufferW | 钩取 explorer 中的 CredUnPackAuthenticationBufferW,输出用户名、密码和域名称 | 已完成 |

关于本主题的博客文章链接:https://ilankalendarov.github.io/posts/offensive-hooking