Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

··订阅源·联系·隐私·© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
CVE-2020-25399 — Stored XSS in InterMind iMind Server through 3.13.65 allows any user to hijack another user's session by sending a malicious file in the chat. 翻译:在 InterMind iMind Server 3.13.65 及之前版本中,存储型 XSS 允许任何用户通过在聊天中发送恶意文件来劫持其他用户的会话。 | Kitploit
工具/GitHubGitHub/h3llraiser/cve-2020-25399
漏洞分析漏洞利用Web应用程序漏洞利用Web安全渗透测试
GitHubh3llraiser/cve-2020-25399

CVE-2020-25399

Stored XSS in InterMind iMind Server through 3.13.65 allows any user to hijack another user's session by sending a malicious file in the chat. 翻译:在 InterMind iMind Server 3.13.65 及之前版本中,存储型 XSS 允许任何用户通过在聊天中发送恶意文件来劫持其他用户的会话。

查看仓库
65年前尚未审核

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享

CVE-2020-25399

InterMind iMind Server 至 3.13.65 版本中存在存储型 XSS 漏洞,允许任何用户通过聊天功能发送恶意文件来劫持其他用户的会话。

信息

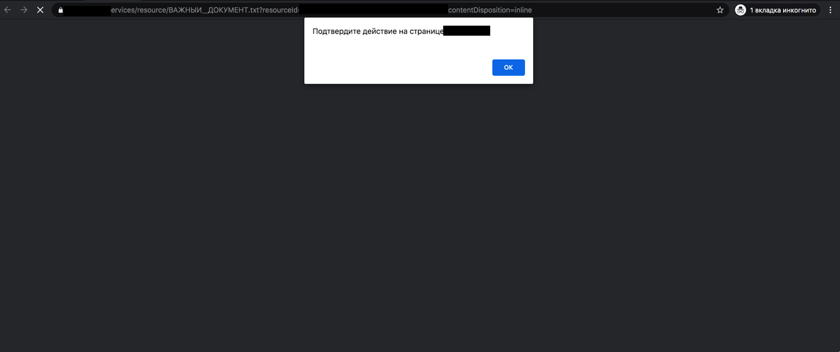
描述:攻击者可利用聊天功能向任何用户发送恶意文件。文件可能包含 JS 负载,在受害者打开文件后于其浏览器中执行。

研究人员:Andrey Skuratov (https://github.com/h3llraiser/)

发现日期:2020-07-06(初始公告)

公开发布:

VEL 链接:即将提供

NIST CVE 链接:即将提供

截图:

下载工具