 gal-nagli/shockwave-oss
精选的漏洞赏金技巧、单行命令和自动化工作流合集,涵盖侦察、模糊测试和 Web 漏洞利用,并包含私有 Nuclei 模板与 HackerOne 报告要点。
分享 Bug Bounty 技巧和诀窍,包括但不限于自动化、单行命令和实用思路
目录
gitsecrets(){
{ find .git/objects/pack/ -name "*.idx"|while read i;do git show-index < "$i"|awk '{print $2}';done;find .git/objects/ -type f|grep -v '/pack/'|awk -F'/' '{print $(NF-1)$NF}'; }|while read o;do git cat-file -p $o;done|grep -E "$1"
}
ffuf -u URL/FUZZ -w allipstoffuf:URL -w ~/.config/wordlists/envpath:FUZZ -maxtime 300 -t 500 -c -v
示例:
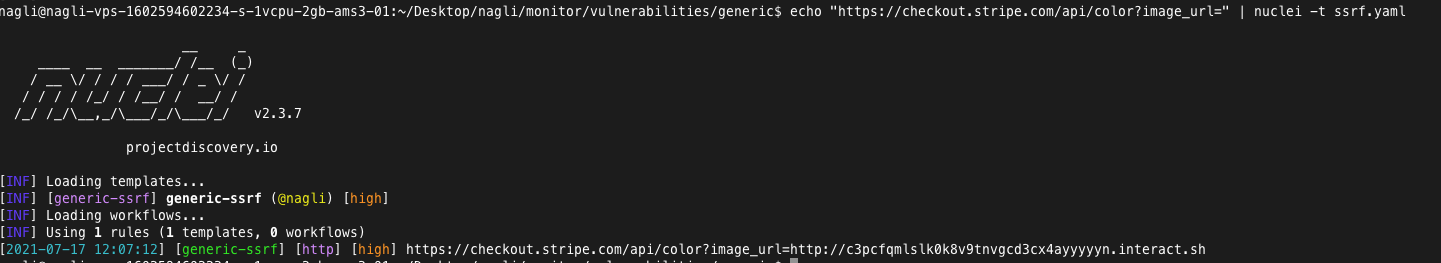
echo "https://checkout.stripe.com/api/color?image_url=" | nuclei -t ssrf.yaml
http://web.com/?XSSendpoint ===> no WAF
https://web.com/?XSSendpoint ===> WAF implemented
Root Domains - "org" subsidiaries
intext: credit company
1. Get company's ASN numbers - amass intel -org DoD
2. Turn ASN numbers into CIDR - whois -h whois.radb.net -- "-i origin $asn" | grep -Eo "([0-9.]+){4}/[0-9]+" | sort -u >> $recondir/cidr
3. Get TLDS from ASN - amass intel -asn $asn
4. Get TLDS from whois data - amass intel -whois -d TLD (facebook.com)
5. Get TLDS from CIDR - amass intel -cidr xxxxxx/23
prips 144.160.32.0/19 | hakrevdns -d | httpx -title -status-code -follow-redirects
Takeaway : FUZZ with certain characters such as \u0000 to try and trigger ReGeX verbose errors
Takeaway: If a company won't require email address verification and will automatically generate support tickets, try and sign up with [email protected]
Takeaway: whenever authenticity_token is presented on requests validate if the value is being processed in the back-end.
Takeaway: try (((((()0))))) when fuzzing post requests.
Takeaway: Swap identifyable cookie values between lateral accounts.
Takeaway: Look through org's public repos for Bitbucket content
Takeaway: When Fuzzing java application to try and insert code injection queries like ${T(java.lang.System).getenv()}
Takeaway: When supplying org name check what is the behaviour with adding " " (space) on it's name
Takeaway: Tampering with the host header with situations who involve caching, can append port to the host to cause DOS
Takeaway: Go through the "main.slug.js" files and look for API Keys, this one looks like the google maps one (AI....)
Takeaway: Look for websites who has bucket like https://s3.amazonaws.com/BUCKETNAME and try to run aws s3 ls BUCKETNAME
Takeaway: Check each step of reset password phase who might not be protected with rate limiting, this could even be a third step after clicking an email, allowing to skip phase 2.
Takeaway: on Admin / custom made login panels check the source code to determine if there are some leaks including password.
Takeaway: %27||/**/(case%20when(/*%c3*/length/*%c3*/(user)=5)then/**/(1)else(1/0)end)||%27
Takeaway: Change the scope parameter to arbitrary file and see if the redirect_url will redirect to external domain
这里展示的部分单行命令或数据可能来自其他仓库,并经过我的修改。我只分享我在过去一年中经常使用或遇到的内容。如果你在这里发现任何最初由你制作的内容,请告诉我,我会注明来源。


