
secator - 渗透测试者的瑞士军刀
<h1 align="center">
<img src="https://assets.kitploit.com/production/public/readmes/6300/dc9ae605fb3dd81cb606836bd853e391122c4acde19b8554c2db00fcaa28a6e5.png" width="400">
</h1>
<h4 align="center">渗透测试者的瑞士军刀。</h4>
<p align="center">
<!-- <a href="https://goreportcard.com/report/github.com/freelabz/secator"><img src="https://goreportcard.com/badge/github.com/freelabz/secator"></a> -->
<img src="https://img.shields.io/badge/python-3.6-blue.svg">
<a href="https://github.com/freelabz/secator/releases"><img src="https://img.shields.io/github/release/freelabz/secator"></a>
<a href="https://github.com/freelabz/secator/blob/main/LICENSE"><img src="https://img.shields.io/badge/License-BSL%201.1-brightgreen.svg"></a>
<a href="https://pypi.org/project/secator/"><img src="https://img.shields.io/pypi/dm/secator"></a>
<a href="https://twitter.com/freelabz"><img src="https://img.shields.io/twitter/follow/freelabz.svg?logo=twitter"></a>
<a href="https://youtube.com/@FreeLabz"><img src="https://img.shields.io/youtube/channel/subscribers/UCu-F6SpU0h2NP18zBBP04cw?style=social&label=Subscribe%20@FreeLabz"></a>
<a href="https://discord.gg/nyHjC2aTrq"><img src="https://img.shields.io/discord/695645237418131507.svg?logo=discord"></a>
</p>
<p align="center">
<a href="#features">功能</a> •
<a href="#supported-commands">支持的命令</a> •
<a href="#install-secator">安装</a> •
<a href="#usage">用法</a> •
<a href="https://docs.freelabz.com">文档</a> •
<a href="https://discord.gg/nyHjC2aTrq">加入我们的 Discord!</a>
</p>
`secator` 是一个用于安全评估的任务和工作流运行器。它支持数十种知名安全工具,旨在提高渗透测试人员和安全研究人员的工作效率。
# 功能
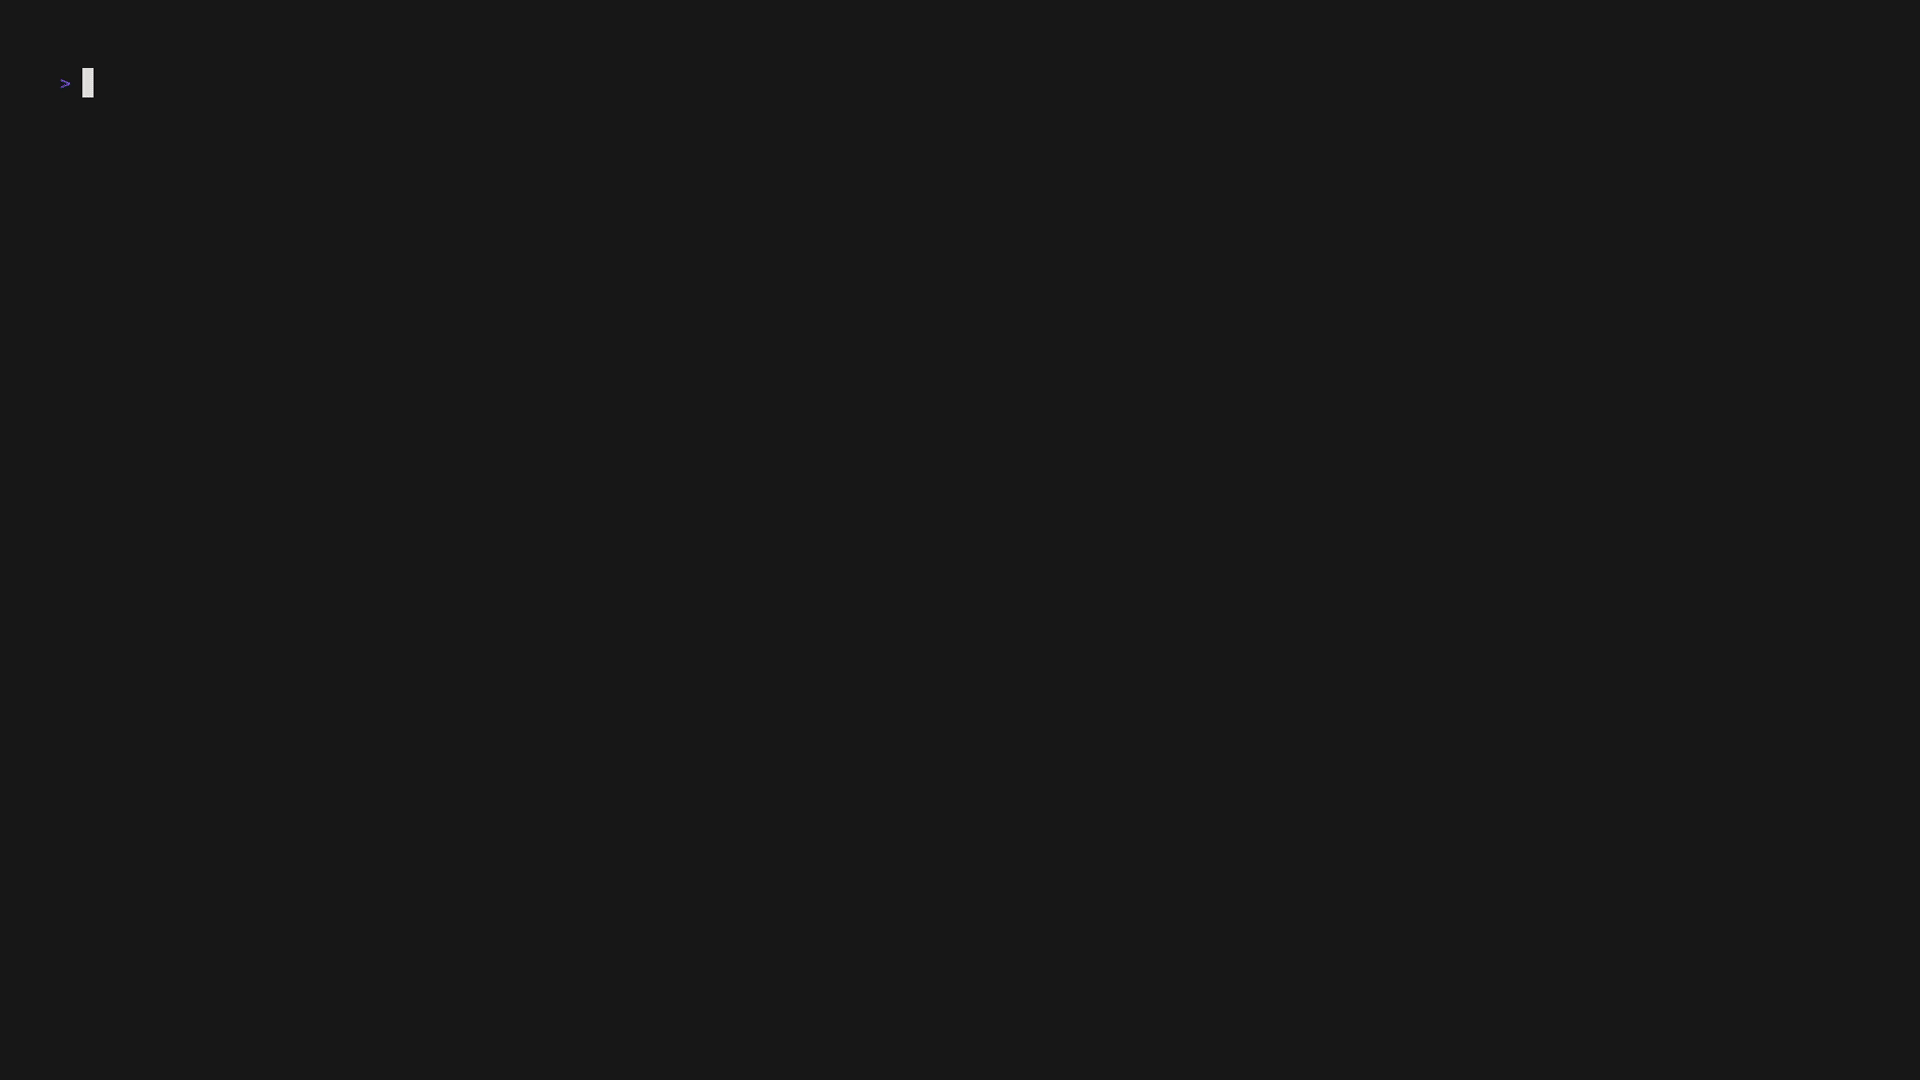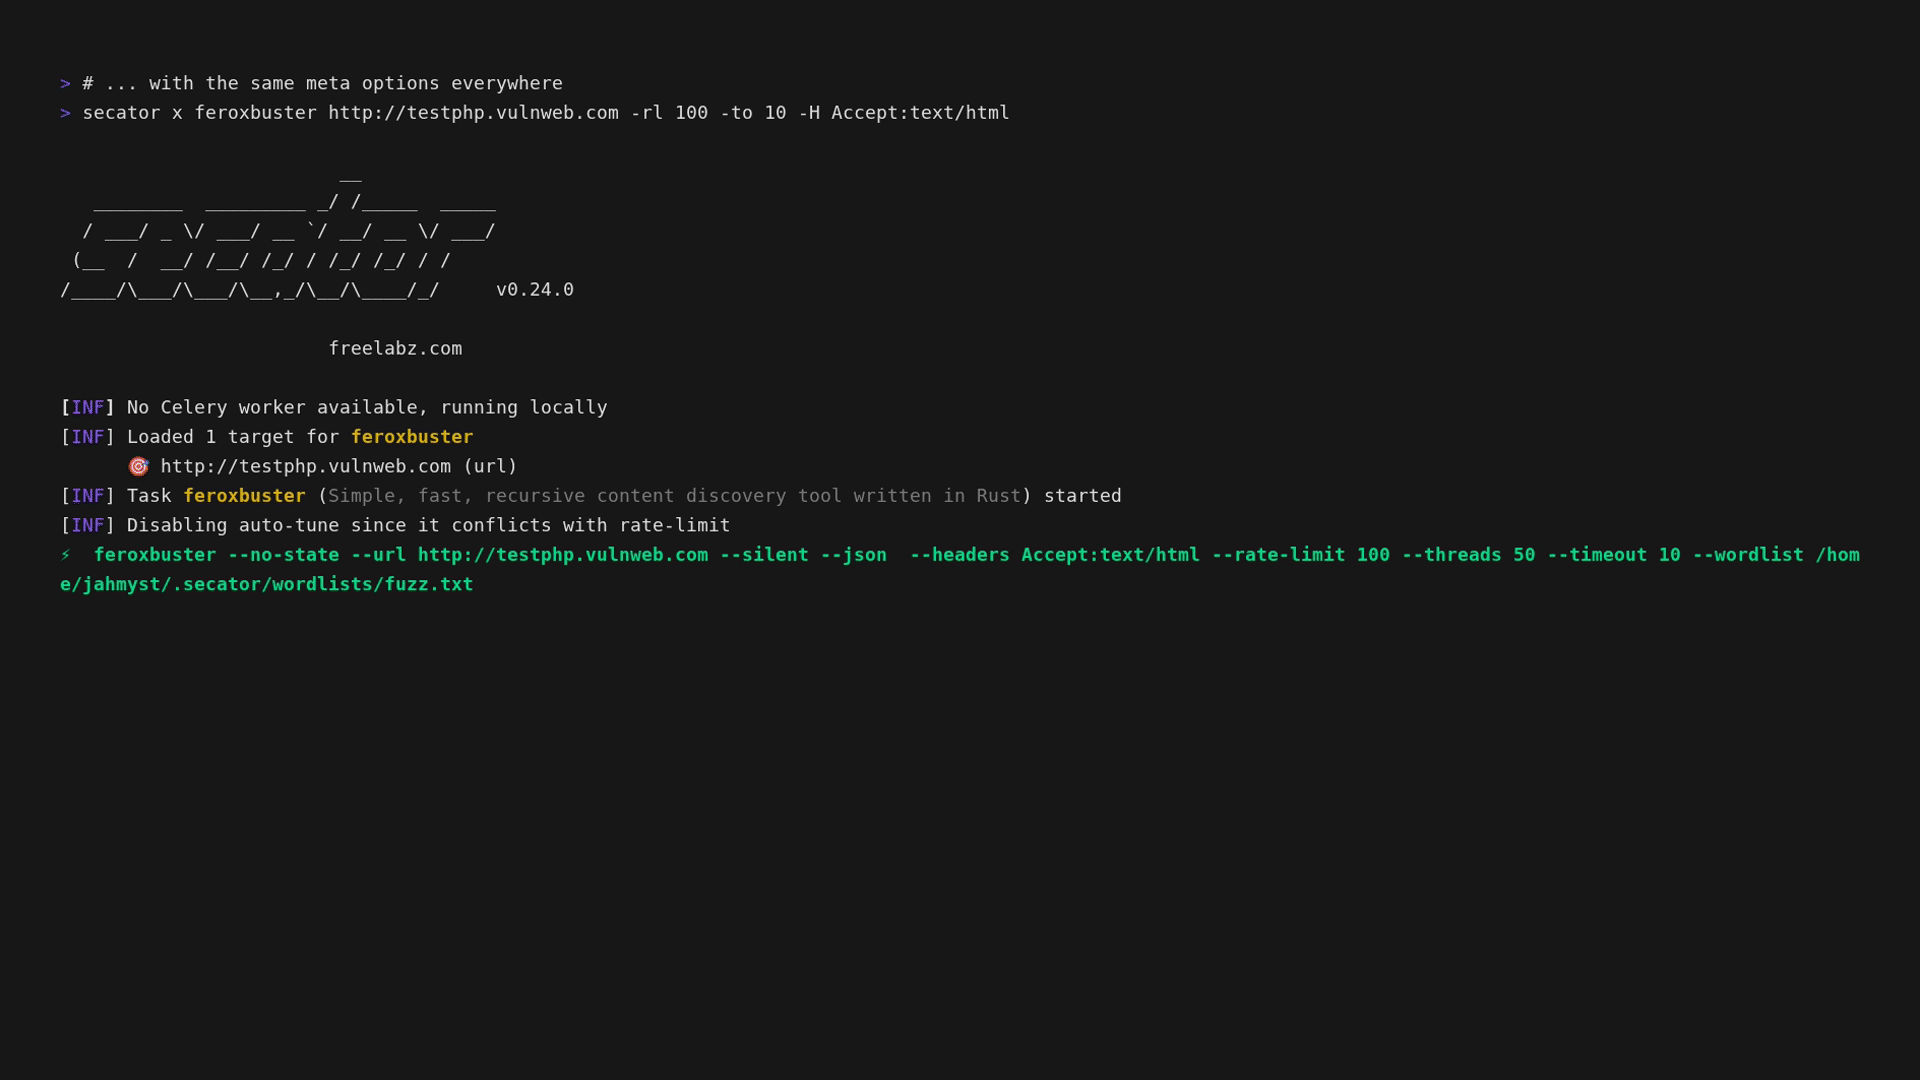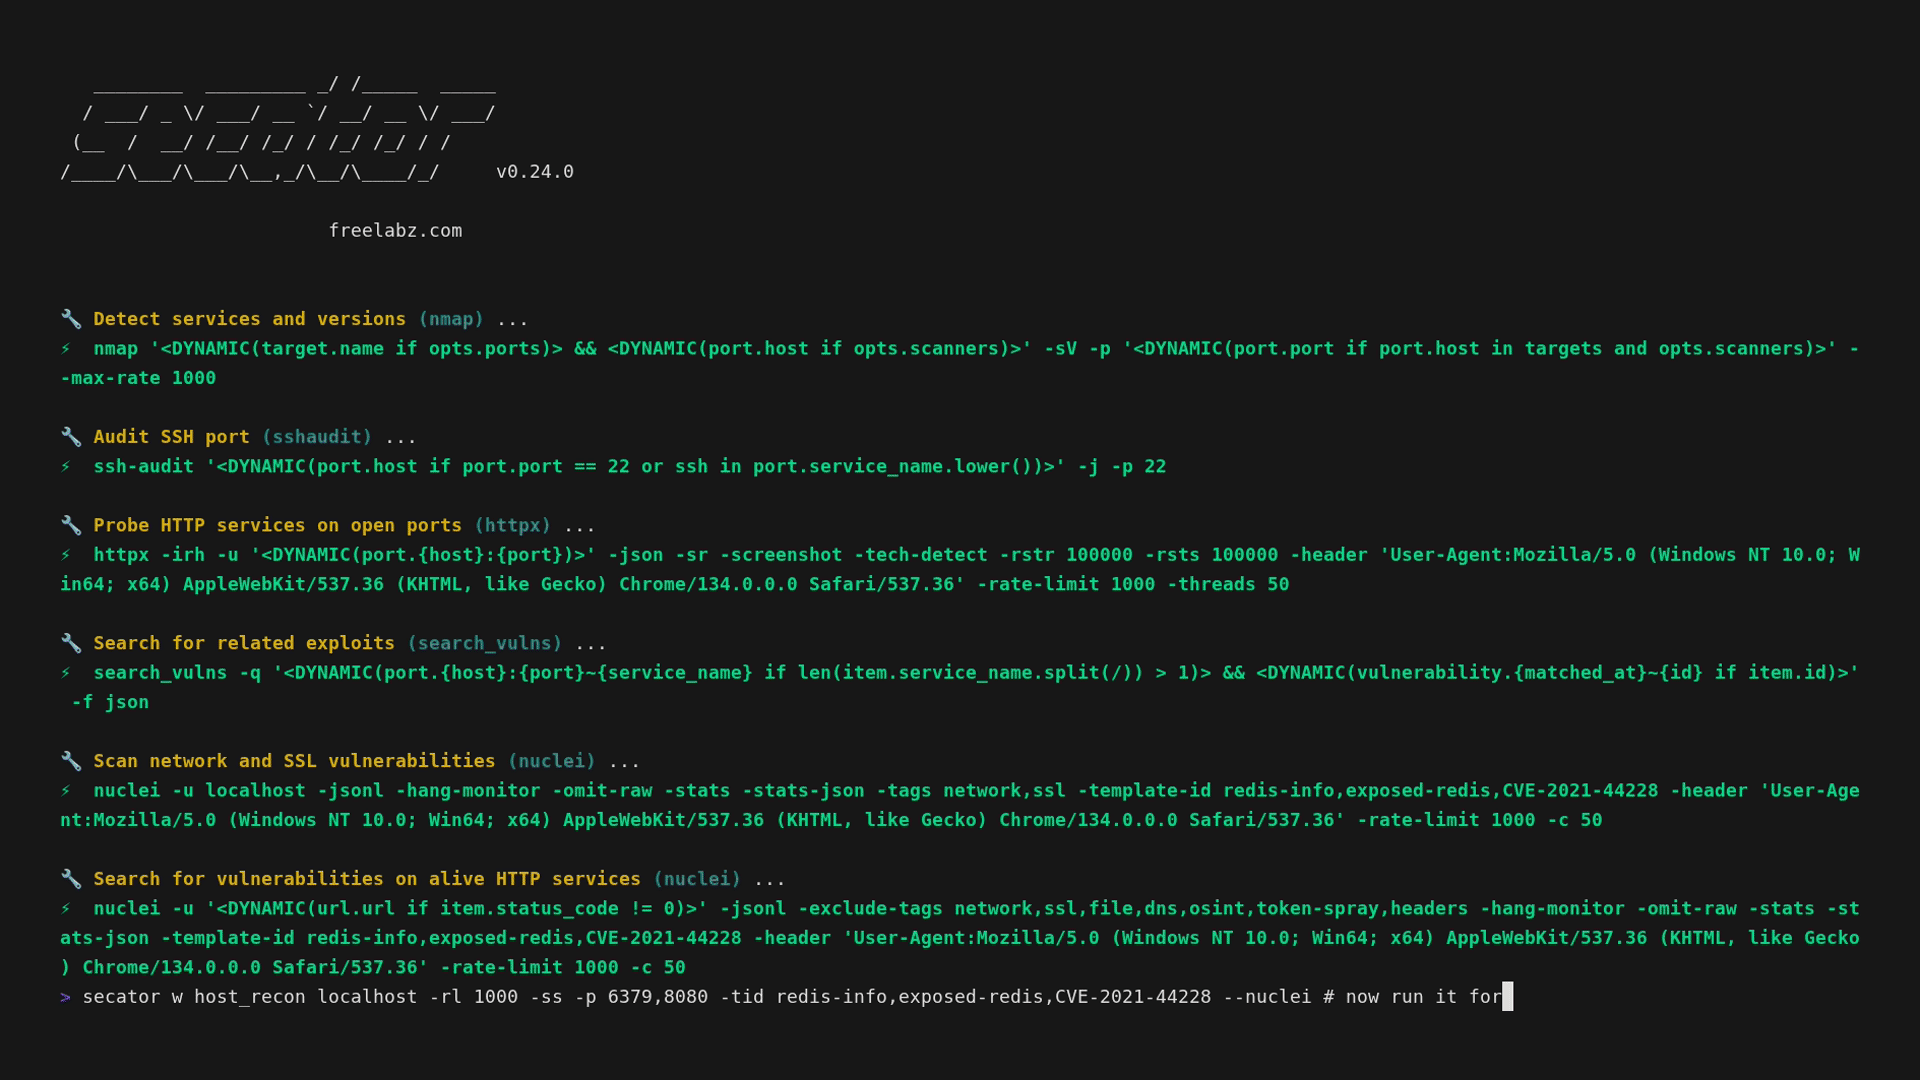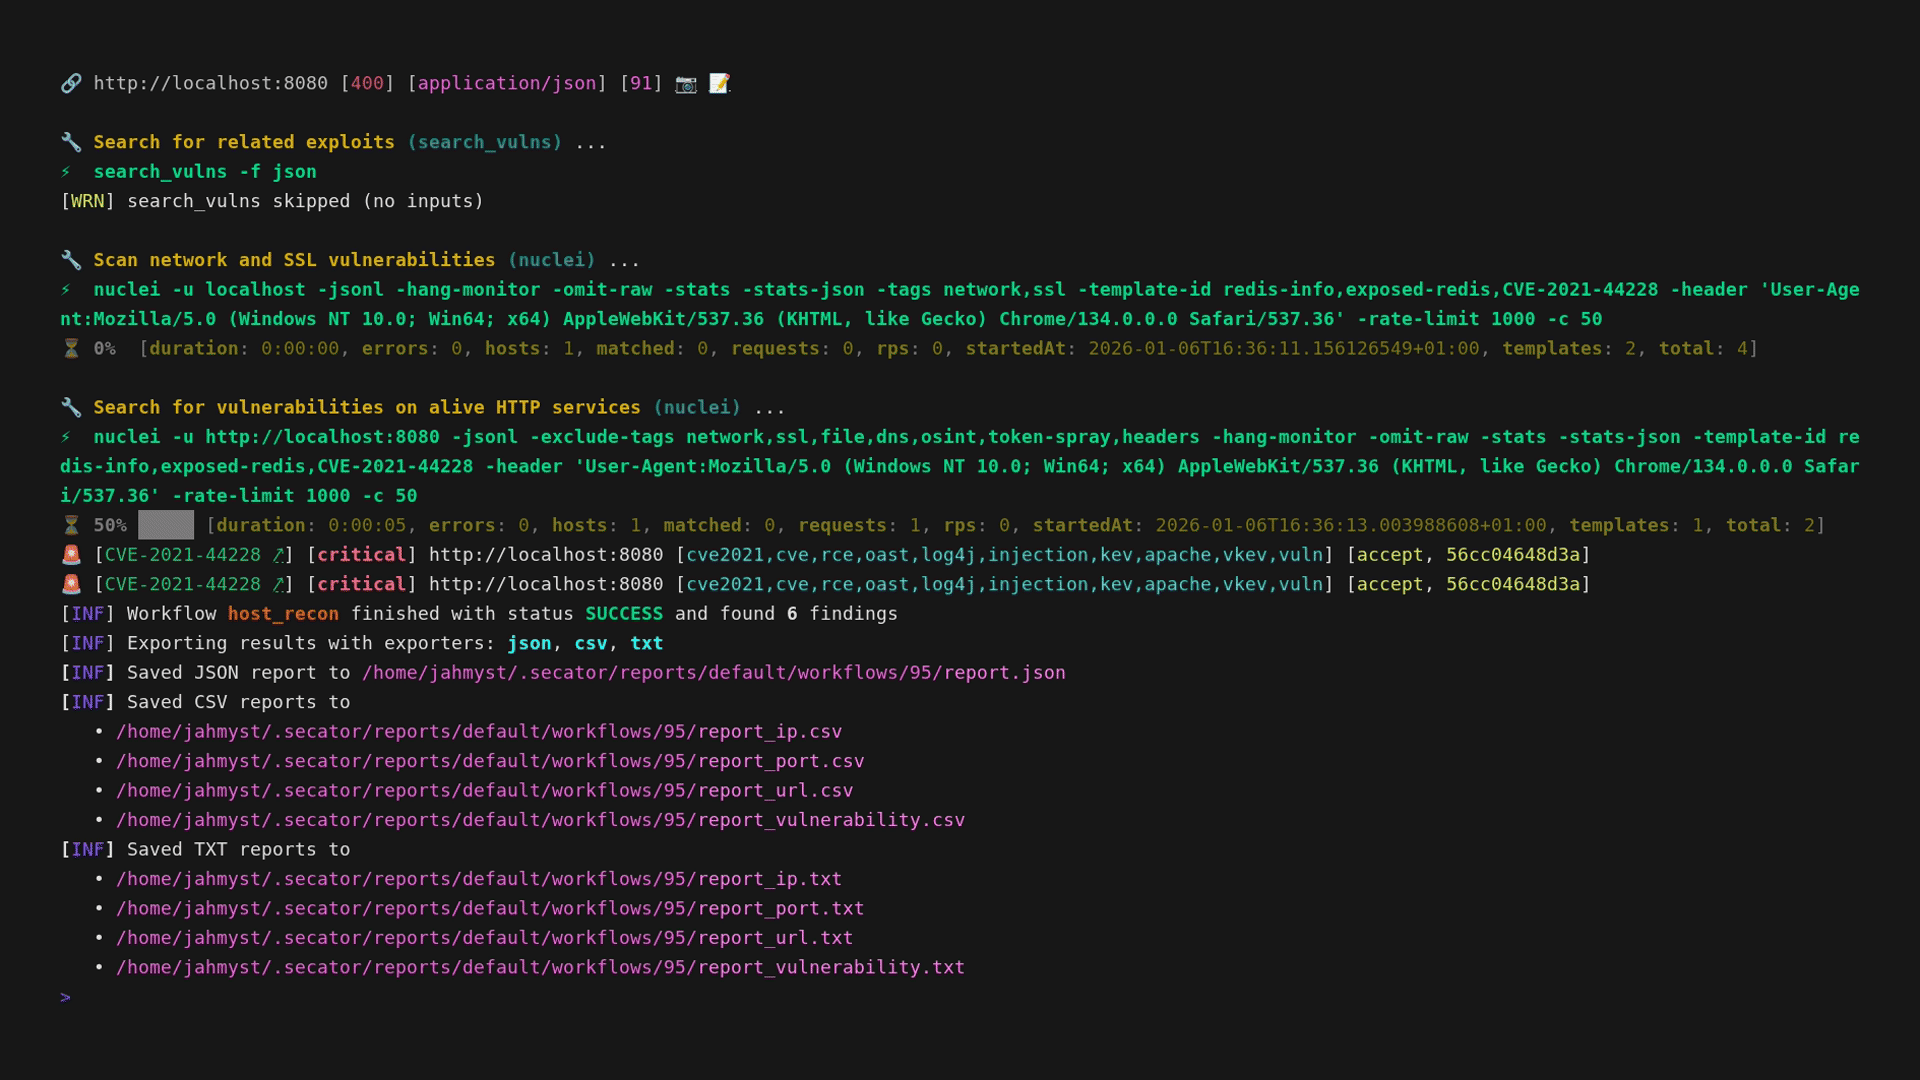
* **精选命令列表**
* **统一输入选项**
* **统一输出模式**
* **CLI 和库使用**
* **基于 Celery 的分布式选项**
* **从简单任务到复杂工作流的灵活性**
* **可定制**
## 支持的工具
`secator` 集成了以下工具:
<!-- START_TOOLS_TABLE -->
| 名称 | 描述 | 类别 |
|-----------------------------------------------------------------|----------------------------------------------------------------------------------|-------------------|
| [arjun](https://github.com/s0md3v/Arjun) | HTTP 参数发现套件。 | `url/fuzz/params` |
| arp | 显示系统 ARP 缓存。 | `ip/recon` |
| [arpscan](https://github.com/royhills/arp-scan) | 使用 ARP 扫描 CIDR 范围以发现存活主机。 | `ip/recon` |
| [bbot](https://github.com/blacklanternsecurity/bbot) | 多用途扫描器。 | `vuln/scan` |
| [bup](https://github.com/laluka/bypass-url-parser) | 40X 绕过器。 | `url/bypass` |
| [cariddi](https://github.com/edoardottt/cariddi) | 爬取端点、密钥、API 密钥、扩展名、令牌等。 | `url/crawl` |
| [dalfox](https://github.com/hahwul/dalfox) | 强大的开源 XSS 扫描工具。 | `url/fuzz` |
| [dirsearch](https://github.com/maurosoria/dirsearch) | 高级 Web 路径暴力破解器。 | `url/fuzz` |
| [dnsx](https://github.com/projectdiscovery/dnsx) | dnsx 是一个快速且多用途的 DNS 工具包,旨在运行各种基于 retryabledns 库的扫描。 | `dns/fuzz` |
| [feroxbuster](https://github.com/epi052/feroxbuster) | 用 Rust 编写的简单快速递归内容发现工具 | `url/fuzz` |
| [ffuf](https://github.com/ffuf/ffuf) | 用 Go 编写的快速 Web 模糊测试器。 | `url/fuzz` |
| [fping](https://github.com/schweikert/fping) | 向网络主机发送 ICMP 回显探测,类似于 ping,但更强大。 | `ip/recon` |
| [gau](https://github.com/lc/gau) | 从 AlienVault 的开放式威胁交换、Wayback Machine、Common Crawl 和 URLScan 获取已知 URL。 | `pattern/scan` |
| [getasn](https://github.com/Vulnpire/getasn) | 从 IP 地址获取 ASN 信息。 | `ip/probe` |
| [gf](https://github.com/tomnomnom/gf) | 对 grep 的封装,帮助你 grep 查找内容。 | `pattern/scan` |
| [gitleaks](https://github.com/gitleaks/gitleaks) | 用于检测 Git 仓库、文件和标准输入中密码、API 密钥和令牌等秘密的工具。 | `secret/scan` |
| [gospider](https://github.com/jaeles-project/gospider) | 用 Go 编写的快速 Web 爬虫。 | `url/crawl` |
| [grype](https://github.com/anchore/grype) | 容器镜像和文件系统的漏洞扫描器。 | `vuln/scan` |
| [h8mail](https://github.com/khast3x/h8mail) | 电子邮件信息和密码查找工具。 | `user/recon/email` |
| [httpx](https://github.com/projectdiscovery/httpx) | 快速且多用途的 HTTP 工具包。 | `url/probe` |
| [jswhois](https://github.com/jschauma/jswhois) | JSON 格式的 WHOIS | `domain/info` |
| [katana](https://github.com/projectdiscovery/katana) | 下一代爬取和蜘蛛框架。 | `url/crawl` |
| [maigret](https://github.com/soxoj/maigret) | 通过用户名收集人员档案。 | `user/recon/username` |
| [mapcidr](https://github.com/projectdiscovery/mapcidr) | 对给定子网/CIDR 范围执行多种操作的实用程序。 | `ip/recon` |
| [msfconsole](https://docs.rapid7.com/metasploit/msf-overview/) | 用于访问和使用 Metasploit 框架的 CLI。 | `exploit/attack` |
| [naabu](https://github.com/projectdiscovery/naabu) | 用 Go 编写的端口扫描工具。 | `port/scan` |
| [nmap](https://github.com/nmap/nmap) | 网络映射器是一个免费开源的网络发现和安全审计工具。 | `port/scan` |
| [nuclei](https://github.com/projectdiscovery/nuclei) | 基于简单 YAML DSL 的快速可定制漏洞扫描器。 | `vuln/scan` |
| [search_vulns](https://github.com/ra1nb0rn/search_vulns) | 按产品名称或 CPE 搜索已知漏洞。 | `vuln/recon` |
| [searchsploit](https://gitlab.com/exploit-database/exploitdb) | 基于 ExploitDB 的漏洞利用搜索器。 | `exploit/recon` |
| [sshaudit](https://github.com/jtesta/ssh-audit) | SSH 服务器和客户端安全审计(横幅、密钥交换、加密、MAC、压缩等)。 | `ssh/audit/security` |
| [subfinder](https://github.com/projectdiscovery/subfinder) | 快速被动的子域名枚举工具。 | `dns/recon` |
| [testssl](https://github.com/testssl/testssl.sh) | SSL/TLS 安全扫描器,包括密码、协议和加密缺陷。 | `dns/recon/tls` |
| [trivy](https://github.com/aquasecurity/trivy) | 全面且多功能的漏洞扫描器。 | `vuln/scan` |
| [trufflehog](https://github.com/trufflesecurity/trufflehog) | 使用 TruffleHog 在 Git 仓库和文件系统中查找秘密的工具。 | `secret/scan` |
| [urlfinder](https://github.com/projectdiscovery/urlfinder) | 在文本中查找 URL。 | `pattern/scan` |
| [wafw00f](https://github.com/EnableSecurity/wafw00f) | Web 应用防火墙指纹识别工具。 | `waf/scan` |
| [whois](https://github.com/mboot-github/WhoisDomain) | whois 工具检索域名和 IP 地址的注册信息。 | |
| [wpprobe](https://github.com/Chocapikk/wpprobe) | 快速 WordPress 插件枚举工具。 | `vuln/scan/wordpress` |
| [wpscan](https://github.com/wpscanteam/wpscan) | WordPress 安全扫描器。 | `vuln/scan/wordpress` |
| [x8](https://github.com/Sh1Yo/x8) | 用 Rust 编写的隐藏参数发现套件。 | `url/fuzz/params` |
| [xurlfind3r](https://github.com/hueristiq/xurlfind3r) | 以简单、被动且高效的方式发现给定域名的 URL | `url/recon` |
<!-- END_TOOLS_TABLE -->
欢迎通过提交 Issue 请求添加新工具,但请先确认该工具符合我们的选择标准。如果不符而您仍希望将其集成到 `secator` 中,您可以自行接入(请参阅[开发指南](https://docs.freelabz.com/for-developers/writing-custom-tasks))。
## 安装 secator
<details>
<summary>Bash</summary>
```sh
bash -c "$(curl -fsSL https://raw.githubusercontent.com/freelabz/secator/main/scripts/install_universal.sh)"
```
***注意:** 支持可选标志 `--version`、`--templates`、`--addons` 和 `--tools` — 使用 `--help` 运行脚本以查看详情。*
</details>
<details>
<summary>Pipx</summary>
```sh
pipx install secator
```
***注意:** 确保已安装 [pipx](https://pipx.pypa.io/stable/installation/)。*
</details>
<details>
<summary>Pip</summary>
```sh
pip install secator
```
</details>
<details>
<summary>Docker</summary>
```sh
docker run -it --rm --net=host -v ~/.secator:/root/.secator freelabz/secator --help
```
挂载卷 -v 是必要的,以便将所有 secator 报告保存到宿主机,推荐使用 --net=host 以赋予宿主机网络的完全访问权限。
您可以为此命令设置别名以便于运行:
```sh
alias secator="docker run -it --rm --net=host -v ~/.secator:/root/.secator freelabz/secator"
```
现在您可以像在裸金属上安装一样运行 secator:
```
secator --help
```
</details>
<details>
<summary>Docker Compose</summary>
```sh
git clone https://github.com/freelabz/secator
cd secator
docker-compose up -d
docker-compose exec secator-client secator --help
```
</details>
***注意:** 如果您选择了 Docker 或 Docker Compose 安装方式,可以跳过后续部分直接前往[用法](#usage)。*
## 用法
```sh
secator --help
```
### 使用示例
要获取 `secator` 完整功能的速查表,请阅读以下命令的输出:
```sh
secator cheatsheet
```
运行一个模糊测试任务(`ffuf`):
```sh
secator x ffuf http://testphp.vulnweb.com/FUZZ
```
运行一个 URL 爬取工作流:
```sh
secator w url_crawl http://testphp.vulnweb.com
```
运行一个主机扫描:
```sh
secator s host mydomain.com
```
要列出所有可用任务/工作流/扫描:
```sh
secator x --help
secator w --help
secator s --help
```
要查看系统上安装了哪些语言或工具(及其版本):
```sh
secator health
```
### 查询
`secator` 允许你使用 `secator query`(或 `secator q`)命令查询所有之前的报告,并重复使用查询。
`secator q <arg>` 通过三个步骤解析其参数:
1. **保存的查询名称** — 如果 `<arg>` 匹配已保存的查询,则使用其表达式。
2. **过滤表达式** — 如果 `<arg>` 看起来像过滤器(包含 `==`、`<`、`~=`、`&&` 等),则直接传递。
3. **自然语言** — 否则发送到 AI 聊天(`secator x ai --mode chat`)。
```sh
# 直接运行原始表达式
secator q "vulnerability.tags ~= 'kev' && vulnerability.confidence == 'high'" # 漏洞 KEV(已知可利用漏洞)+ 高置信度
secator q "vulnerability.severity == 'critical' && vulnerability.tags ~= 'exploitable' && vulnerability.confidence == 'high'" # 漏洞 严重 + 可利用 + 高置信度
secator q "vulnerability.severity_nb < 2 && vulnerability.confidence == 'high'" # 漏洞 严重程度 > 高 + 高置信度
secator q "exploit.cves ~= 'CVE-2021-44521'" # 为漏洞 CVE-2021-44521 找到的利用
secator q "port" -f "{host} {port} {service_name}" | cut -d " " -f2 | sort | uniq -c | sort -nr | head -n 15 # 前15个端口
secator q "port" -f "{host} {port} {service_name}" | cut -d " " -f3,4,5,6 | awk 'NF > 0' | sort | uniq -c | sort -nr | head -n 15 # 前15个服务
secator q "technology" -f "{product}/{version}" | sort | uniq -c | sort -nr | head -n 15 # 前15个技术
secator q "port.state == 'open'" -rf scans/23,tasks/10 # 仅来自扫描23和任务10的结果
# 保存查询并运行
secator c set queries.critical_vulns "vulnerability.severity_nb < 2" # 保存查询
secator c get queries # 列出保存的查询
secator q critical_vulns -f "{vulnerability.matched_at}" -ws secator.cloud # 在工作区上运行保存的查询 + 提取目标
# 提出自然语言问题(运行 AI 聊天任务)
secator q "分析我的工作区数据"
```
`secator q` 接受与 `secator r show` 相同的选项(`-o/--output`、`-d/--time-delta`、`-f/--format`、`-w/-ws/--workspace`、`--driver`、`--dedupe`),外加 `-rf/--report-filter` 用于将查询范围限定到特定的运行器路径(相当于 `r show` 的 `REPORT_QUERY` 参数)。在 AI 聊天路径中,仅使用工作区和提示。
### Shell 自动补全
`secator` 支持 bash、zsh 和 fish 的 Shell 自动补全。这提供以下内容的自动补全:
- 任务名称(如 `nmap`、`httpx`、`nuclei`)
- 工作流名称(如 `url_crawl`、`subdomain_recon`)
- 扫描名称(如 `host`、`domain`、`network`)
- CLI 选项如 `--profiles`、`--workspace`、`--driver`、`--output`
要安装 Shell 自动补全:
**Bash:**
```sh
secator util completion --shell bash --install
source ~/.bashrc
```
**Zsh:**
```sh
secator util completion --shell zsh --install
source ~/.zshrc
```
**Fish:**
```sh
secator util completion --shell fish --install
```
安装后,您可以使用 Tab 键自动补全:
```sh
secator x n<TAB> # 补全为 nmap、naabu、nuclei 等
secator w url_<TAB> # 补全为 url_crawl、url_fuzz、url_dirsearch 等
secator x nmap --profiles ag<TAB> # 补全为 aggressive
```
## 安装工具
`secator` 在您首次使用工具时会自动安装。您可以通过 `secator config set security.autoinstall_commands false` 或 `SECATOR_SECURITY_AUTOINSTALL_COMMANDS=0` 将 `security.autoinstall_commands` 设置为 `false` 来阻止此行为。
要安装所有工具,您仍可以运行:
```sh
secator install tools
```
## 安装附加组件
`secator` 提供附加组件,详情请查阅[我们的文档](https://docs.freelabz.com/getting-started/installation#installing-addons-optional)。
例如,使用 `mongodb` 附加组件可以将运行器结果发送到 MongoDB。
## 了解更多
要深入了解 `secator`,请查看:
* 我们的完整[文档](https://docs.freelabz.com)
* 我们的入门[教程视频](https://youtu.be/-JmUTNWQDTQ?si=qpAClDWMXo2zwUK7)
* 我们的 [Medium 文章](https://medium.com/p/09333f3d3682)
* 在社交媒体上关注我们:Twitter [@freelabz](https://twitter.com/freelabz) 和 YouTube [@FreeLabz](https://youtube.com/@FreeLabz)
## 统计
<a href="https://star-history.com/#freelabz/secator&Date">
<picture>
<source media="(prefers-color-scheme: dark)" srcset="https://api.star-history.com/svg?repos=freelabz/secator&type=Date&theme=dark" />
<source media="(prefers-color-scheme: light)" srcset="https://api.star-history.com/svg?repos=freelabz/secator&type=Date" />
<img alt="Star History Chart" src="https://api.star-history.com/svg?repos=freelabz/secator&type=Date" />
</picture>
</a>

