
通过搜索 JavaScript 中的端点生成针对特定目标的单词列表,并附加参数以便与其他工具进行模糊测试
版本 1.0
$ go get -u github.com/ethicalhackingplayground/wordlistgen
$ go get github.com/003random/getJS

$ echo "https://www.twitter.com" | getJS -complete | ./wordlistgen -p params.txt -d "https://www.twitter.com"
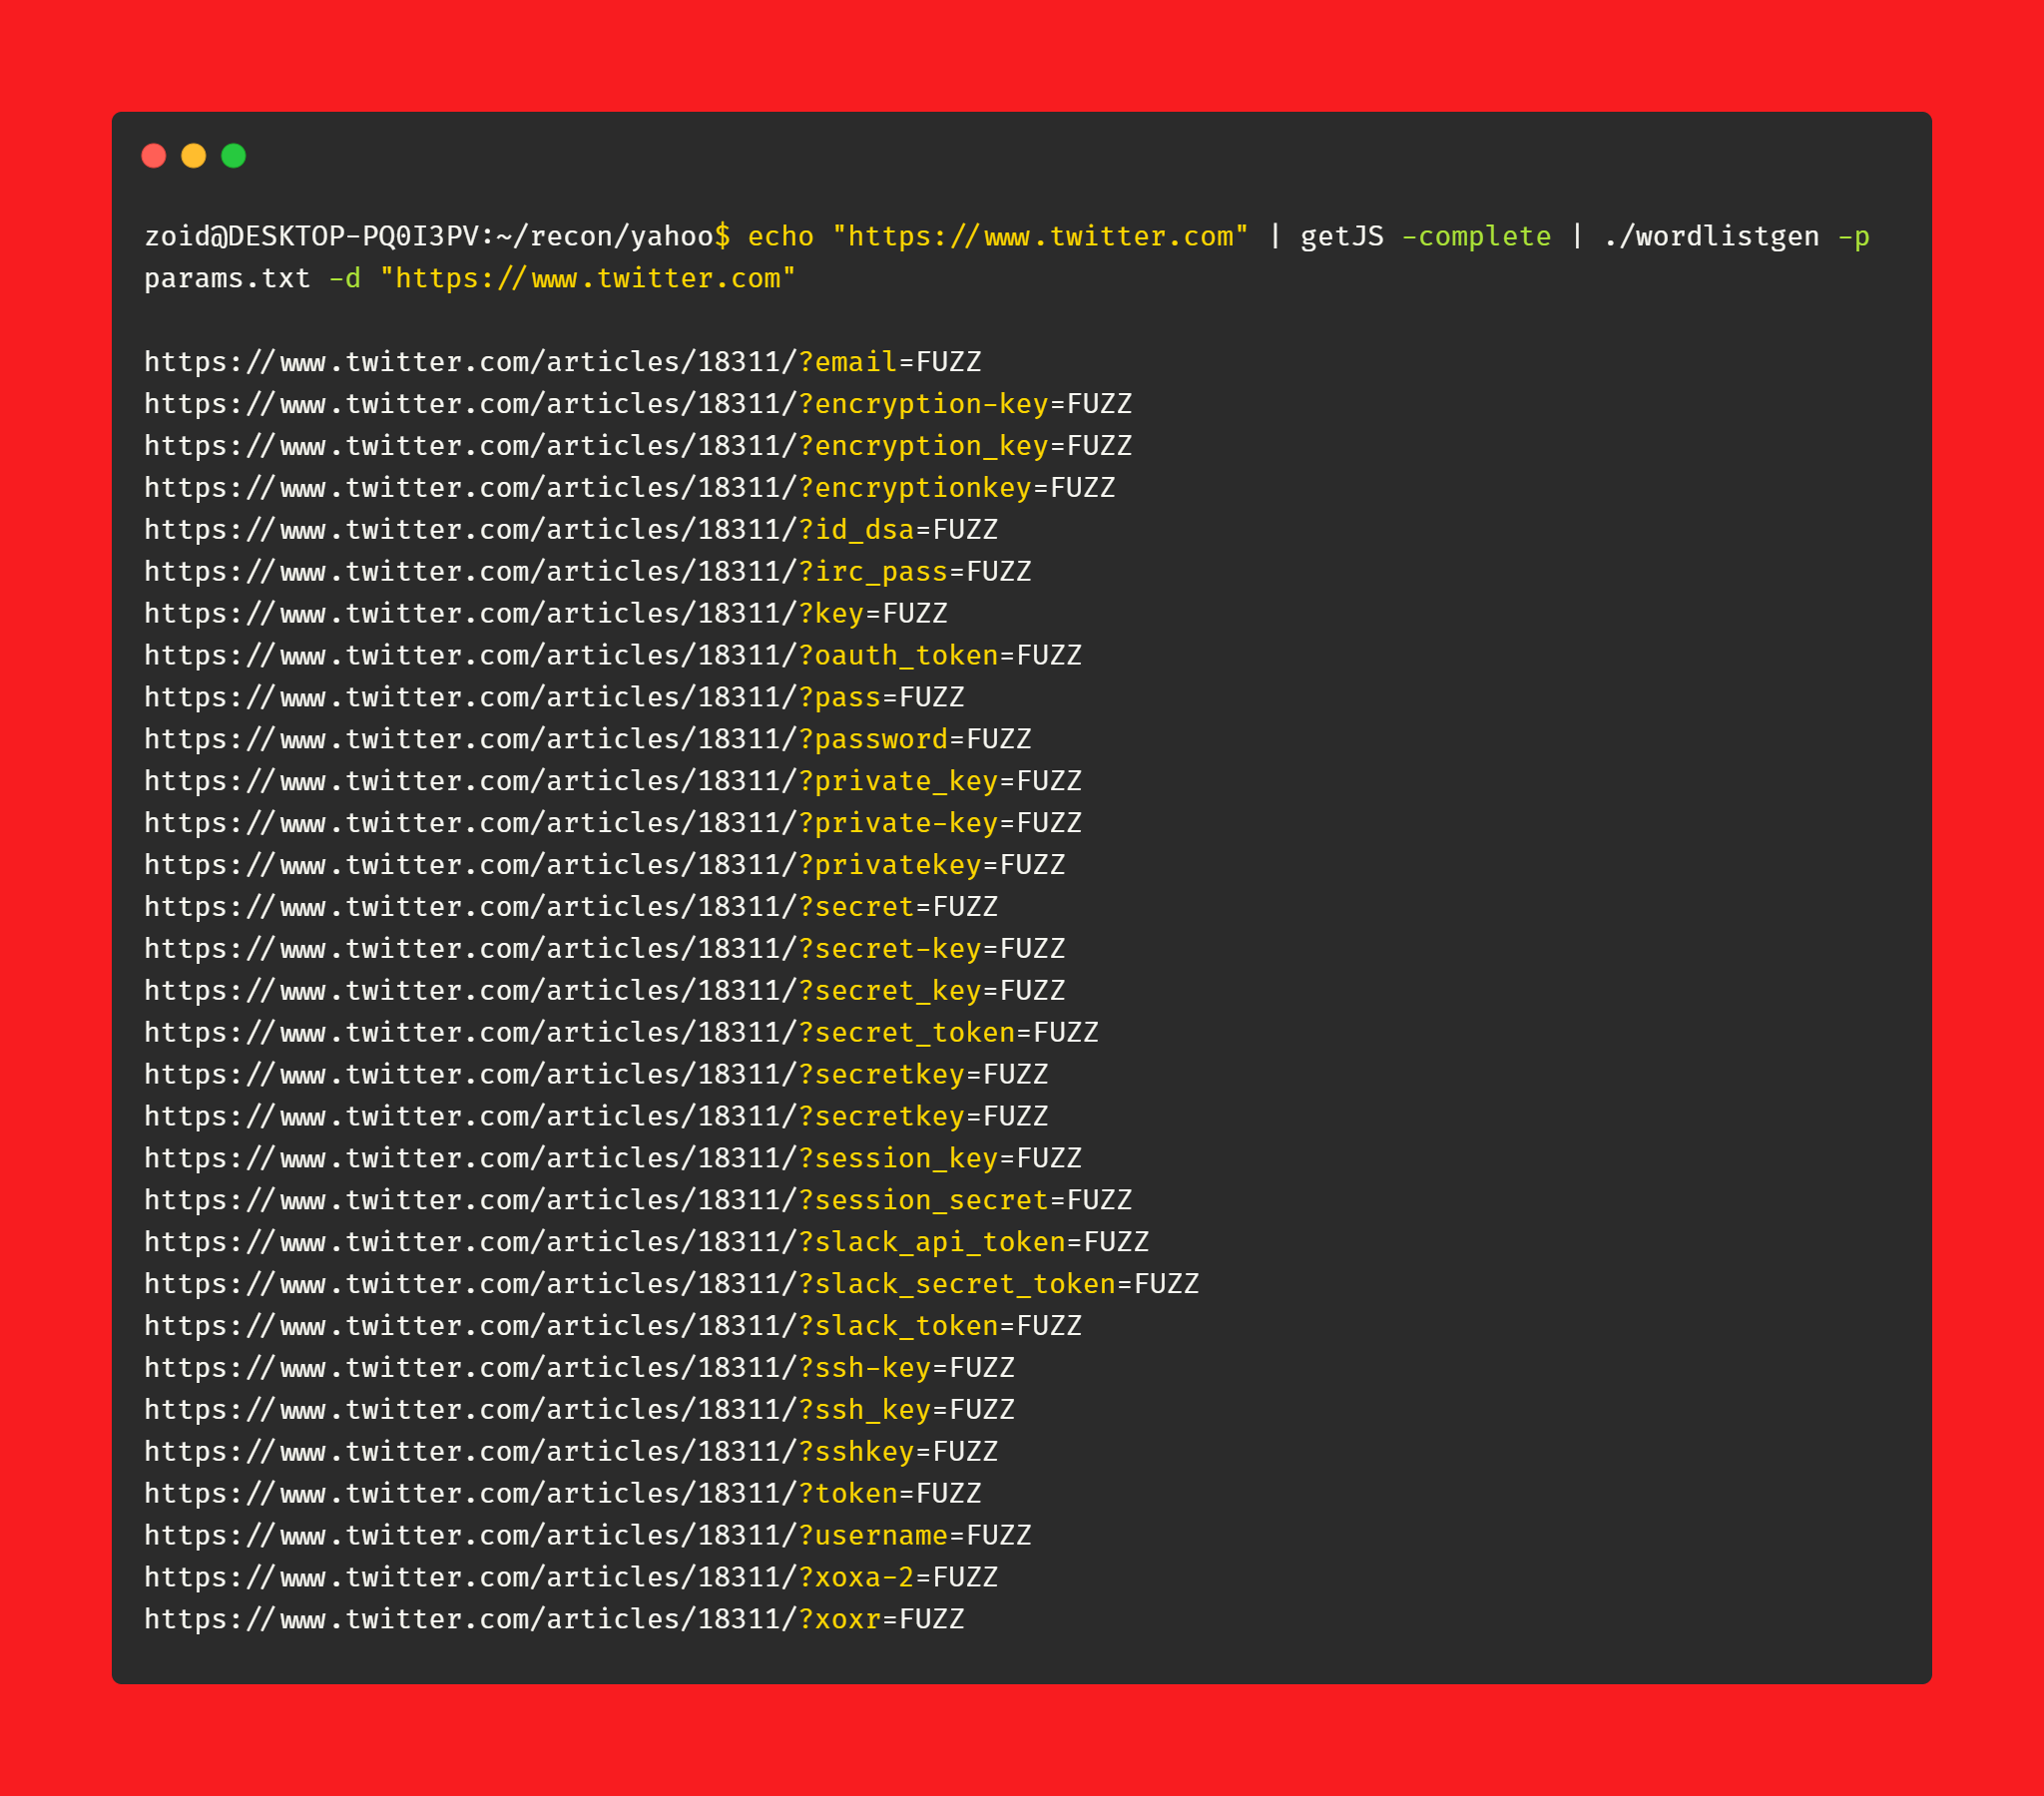
使用 ffuf
然后发挥创意,搭配 FFuF 或 https://github.com/tomnomnom/qsreplace 使用
$ cat <Resolved-Domains> | getJS -complete | ./wordlistgen -p params.txt -d <Un-Resolved> | tee wordlist
$ cat "https://www.twitter.com" | getJS -complete | ./wordlistgen -p params.txt -d "www.twitter.com" | tee wordlist
输出:

www.twitter.com/responsive-web-internal/sourcemaps/client-web-legacy/polyfills.525f28f5.js.map/?url=FUZZ
www.twitter.com/v/latest/72x72//?url=FUZZ
www.twitter.com/responsive-web-internal/sourcemaps/client-web-legacy/en.363b7e25.js.map/?url=FUZZ
www.twitter.com/articles/18311/?url=FUZZ
-dL 来加载一个子域名列表,例如:$ cat <Resolved-Domains> | getJS -complete | ./wordlistgen -p params.txt -dL <Un-Resolved> | tee wordlist
$ cat wordlist | qsreplace http://127.0.0.1/admin | tee -a hosts
输出:

www.twitter.com/responsive-web-internal/sourcemaps/client-web-legacy/polyfills.525f28f5.js.map/?url=http%3A%2F%2F127.0.0.1%2Fadmin
www.twitter.com/v/latest/72x72//?url=http%3A%2F%2F127.0.0.1%2Fadmin
www.twitter.com/responsive-web-internal/sourcemaps/client-web-legacy/en.363b7e25.js.map/?url=http%3A%2F%2F127.0.0.1%2Fadmin
www.twitter.com/articles/18311/?url=http%3A%2F%2F127.0.0.1%2Fadmin
$ cat hosts | httpx -title -status-code
如果你获得了赏金,请支持我,给我买杯咖啡









